#websecurity
A web application reflects user input without proper output encoding.
Which OWASP vulnerability is most likely?
A) SQL Injection
B) Reflected XSS
C) SSRF
D) IDOR
Comment your answer 👇
#IndiaMatters with @VishnuNDTV | Meta Versus Government
"Transparency has to come from social media service provider itself": @mukesh_one, Founder & CEO, Cyberops
BJP's @shaziailmi responds to @ranjanakumari, says the CSAM ads were being prompted by algos.
Which attack abuses #Kerberos service tickets to crack service account passwords offline?
A) Golden Ticket
B) Pass-the-Hash
C) Kerberoasting
D) Silver Ticket
Comment Your Answer 👇
During a VAPT assessment, security experts frequently uncover critical vulnerabilities that attackers actively exploit—from SQL Injection and Broken Access Control to ….
How many of these vulnerabilities could exist in your environment today?
#VAPT#PenetrationTesting#OWASP
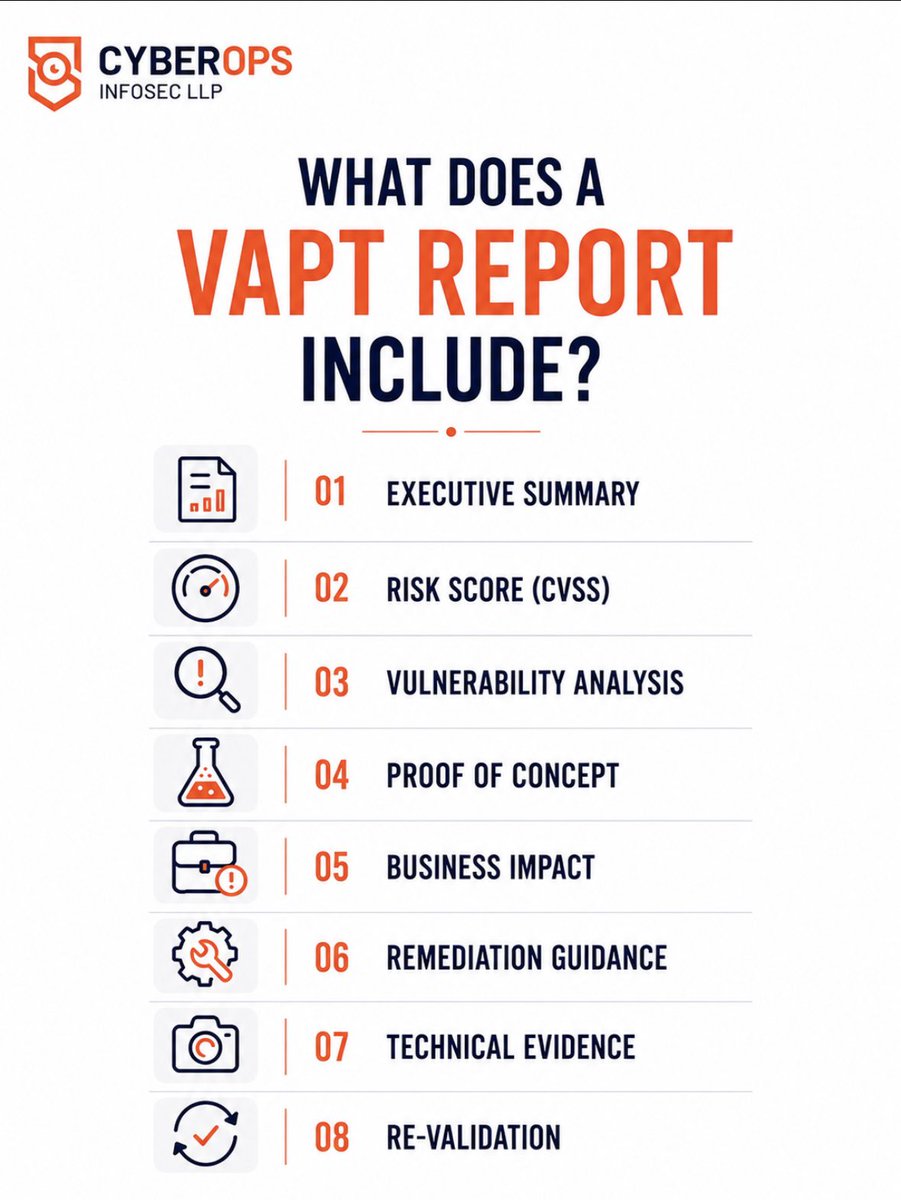
An effective report should include:
Executive Summary
Risk Score (CVSS)
Vulnerability Analysis
Proof of Concept
Business Impact
Remediation Guidance
Technical Evidence
Re-Validation
Does your current VAPT report provide actionable insights or just a list of findings?
#VAPT
WhatsApp pe fake message aaya, boss ki photo lagi thi, aur 7.8 crore transfer kr diye!
Here’s how Naresh Gujral was targeted by the cyber fraudsters and what should we learn for this case.
#cyberfraud#WhatsAppScam#awareness#nareshgujral
A web application allows users to fetch remote resources from a URL provided by the user. An attacker uses this feature to access internal cloud metadata services.
What #vulnerability is being exploited?
A) IDOR
B) XXE
C) SSRF
D) CSRF
Comment your answer👇
#Medicine isn't just about machines; it's about humanity. 🏥
#London’s King’s College #Hospital just launched the UK’s first dedicated outdoor ICU rooftop garden for patients to experience natural sunlight and fresh air to help combat ICU delirium and accelerate healing. 🌿☀
Which #AWS service helps identify security #vulnerabilities and unintended network exposure?
A) EC2
B) CloudWatch
C) Inspector
D) Route 53
Comment Your Answer👇
What does #XSS stand for?
A) XML Secure Service
B) Cross Site Scripting
C) Cross Server Security
D) Extended Security Session
Comment Your Answer👇
#Cyberops#CyberSecurity#Pentesting
#CyberAttack
What attack technique is commonly used to extract password hashes from Windows memory?
A) DNS Tunneling
B) Mimikatz
C) Burp Suite
D) Hydra
Comment Your Answer👇
#authentication#cybersecurity
Which authentication factor does a fingerprint belong to?
A) Something You Know
B) Something You Have
C) Something You Are
D) Something You Access
#OWASP
Which OWASP vulnerability allows attackers to manipulate database queries through unsanitized input?
A) Broken Access Control
B) SQL Injection
C) SSRF
D) Security Misconfiguration
👇 Drop your answer
A stranger calls claiming to be from your bank and asks for your OTP.
What should you do?
A) Share OTP immediately
B) Share only the first 3 digits
C) Never share OTP with anyone
D) Ask them to call later
👇 Comment your answer
#cybercrimeawareness
Social engineering attacks primarily exploit:
A) Software bugs
B) Network cables
C) Human psychology
D) Hardware failures
Drop your answer below.
#SocialEngineering#CyberAwareness#CyberVeer