🚨 #CyBlack2026 Tickets Are Now Live!
Join cybersecurity professionals, industry leaders, innovators, and the next generation of talent as we come together to explore solutions to tomorrow’s cyber challenges.
Expect thought-provoking discussions, practical insights,
1/2
Thursdays are for throwbacks!
Taking a trip down memory lane with some memorable moments from the #CyBlack2022 Conference.
A look back at the connections, conversations, and experiences that made it one to remember.
#CyBlack#ThrowbackThursday
Human Factors in Cybersecurity sprint at @Cyblackorg wrapped up!
My biggest takeaway? Security is only as strong as the people, processes & controls behind it. Human risk matters a lot.
I've shared more about this project on: https://t.co/HlBMsDvwwl
@ireteeh@TemitopeSobulo
Day 84 - Build Log
Today marked another productive step in my cybersecurity journey.
DG Interns Hub - Week 3
I completed the Incident Management 101 course on LetsDefend, wrapping up my Week 3 internship learning task.
I also submitted my Week 3 internship deliverables. I've documented the practical work from this week on GitHub, and you can check it out here: https://t.co/sbA5xNwp7f
@Cyblackorg Internship - Sprint 4: Governance, Risk and Compliance (GRC)
We resumed today after a six-day break with our Sprint 4 task call. I'm looking forward to exploring the governance, risk, and compliance side of cybersecurity and understanding how organisations establish controls, manage risks, and maintain security standards.
Lessons learned: Technical security skills are important, but understanding how security is governed, assessed, and maintained is equally essential.
A new sprint, new challenges, and another opportunity to grow. Ready for the work ahead!
We resumed today after a six-day break with our Sprint 4 task call. I'm looking forward to exploring the governance, risk, and compliance side of cybersecurity and understanding how organizations establish controls, manage risks, and maintain security standards.
Day 85 - Build Log
I combined hands-on security learning with team collaboration.
TryHackMe: Vulnerability 101
Completed the Vulnerability 101 room, strengthening my understanding of security vulnerabilities, how they are identified, assessed, and prioritised, and why vulnerability management is an important part of an organisation's security programme.
@Cyblackorg Internship - Sprint 4: GRC
Attended my team's first meeting as we kicked off the second phase of the internship following the break.
We discussed our approach to the Governance, Risk and Compliance (GRC) sprint, shared responsibilities, and agreed on how to tackle the assigned tasks as a team.
Lesson: Identifying vulnerabilities is only part of the process. Organisations also need structured approaches to assess risks, prioritise remediation, and maintain effective security controls.
A new sprint, shared responsibilities, and more opportunities to grow. On to the work ahead!
#Cybersecurity #VulnerabilityManagement #GRC #RiskManagement #Compliance #TryHackMe #CyBlack #LearningInPublic
Day 87 - Build Log
I combined Blue Team learning with GRC project collaboration.
TryHackMe - Two Rooms Completed
1. Linux Incident Response
Practised investigating a compromised Linux server by examining user accounts, authentication logs, shell history, scheduled tasks, and persistence locations.
One important lesson was how correlating traces across different system files helps reconstruct an attacker's activities and build an incident timeline.
2. Lab 3: Forensics
Explored practical digital forensic investigation, evidence examination, and the tools used to analyse digital artifacts.
The exercise reinforced the importance of methodical analysis, evidence integrity, and proper documentation so findings can be independently verified.
@Cyblackorg Internship - Sprint 4: GRC
Met with my team to review our sprint progress. We've made progress developing organisational policies and are now working towards completing the remaining drafts.
We also discussed the policy review process, with emphasis on maintaining proper separation of responsibilities between authors, policy owners, reviewers, and approvers.
Lesson: Effective incident response depends on correlating evidence, while effective security governance depends on clearly defined responsibilities, accountability, and review processes.
Two labs completed, team progress made, and more lessons added to my journey.
#Cybersecurity #LinuxSecurity #DigitalForensics #IncidentResponse #GRC #TryHackMe #CyBlack #LearningInPublic #BuildInPublic
I’m finally done with the human factor sprint at @Cyblackorg At first, it sounded like a straightforward sprint, but getting into the actual tasks made me realise how challenging and interesting it could be.
Third sprint done ✅️ @Cyblackorg
From researching human factor threats to developing awareness stories, exploring accessibility and creating content on Vivida.
One of my biggest lesson is that a good research is about evidence, not assumptions
@ireteeh@NnajiDaniel_C
A friendly voice, a little urgency, and the desire to help. Sometimes, that’s all social engineering needs.
And if our security measures aren't accessible to people with disabilities, who are we truly protecting?
Human Factors gave me a lot to think about.
@Cyblackorg@ireteeh
A few moments with some of the amazing people who made #CyBlack2026 special.💙
From meaningful conversations to new connections, it was great bringing the cybersecurity community together to solve tomorrow’s challenges.
Thank you for being a part of it!
#CyBlack#CyberSecurity
Day 58 - Build Log
Today was about documenting progress and moving projects closer to completion.
Portfolio Updates: I updated my cybersecurity portfolio to reflect recently completed projects, their documentation, and credentials I’ve earned. I want it to accurately represent my growth and the practical work behind it.
You can check it out through the link on my bio. Feedback and suggestions are very much appreciated!
CyBlack Internship - Sprint 2: I spent the evening with my team wrapping up our Cloud Security task. With the technical work coming together, we’re using the coming week to prepare our deliverables and presentation.
Building technical skills is important, but documenting your work, keeping your portfolio current, and communicating results are equally valuable parts of professional growth.
Still building, documenting, and learning along the way.
@Cyblackorg
#Cybersecurity #CloudSecurity #Portfolio #BuildInPublic #LearningInPublic #CyBlack
Cloud Security Sprint 2 is still in progress @Cyblackorg
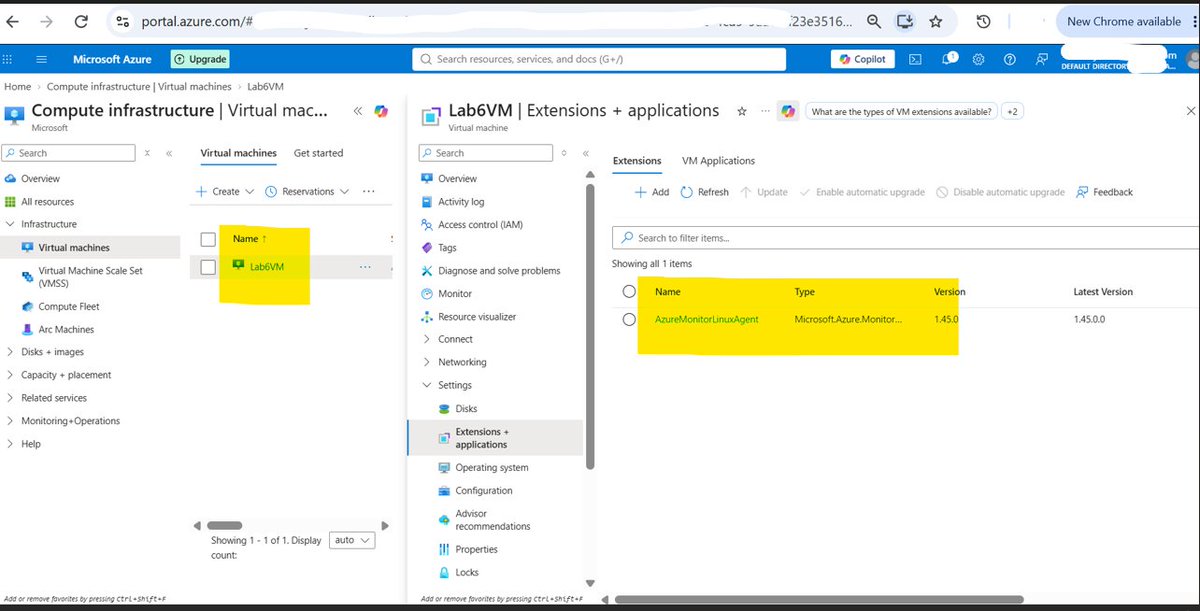
This time, I got hands-on with Azure Monitor Agent & Data Collection Rules.
From configuring VM monitoring to collecting Syslog and performance data, then validating everything in Log Analytics.
@ireteeh@TemitopeSobulo
On the Sprint 2 (Cloud Security)
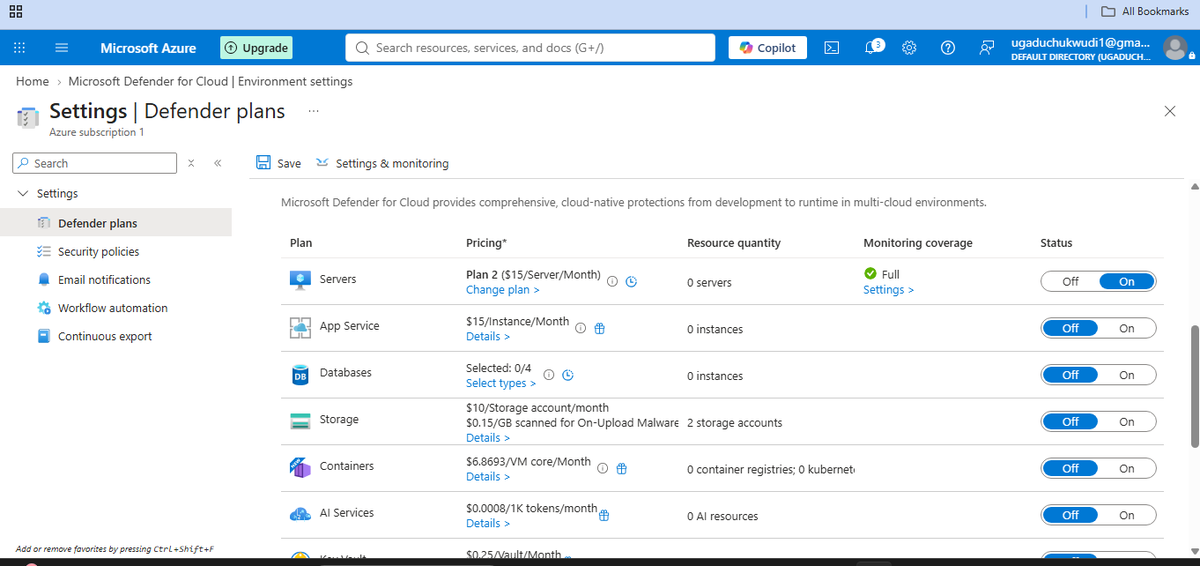
I enabled Microsoft Defender for Servers Plan 2 in Azure Defender for Cloud. Extended advanced EDR, threat monitoring, and vulnerability assessments across our hybrid & Azure VM infrastructure. Securing workloads one step at a time
@Cyblackorg
Day 61 - Build Log
CyBlack Internship Update: Sprint 2 - Cloud Security
As the Project Manager of my team, I worked on consolidating our individual contributions into a comprehensive Cloud Security Team Report.
Our sprint covered several key areas of Microsoft Azure security:
Identity and Access Management (IAM): Managing identities, permissions, and access controls.
Cloud Network Security: Securing network traffic and access using firewalls, subnets, route tables, and gateways.
Container Security: Exploring security considerations around Azure Container Registry (ACR) and Azure Kubernetes Service (AKS).
Storage Security: Addressing access control and the protection of cloud-stored data.
Monitoring and Logging: Using Microsoft Sentinel to support security monitoring, event analysis, and threat detection.
Since we are done working on the tasks, my responsibility was to bring the team's individual work together, ensuring the report was structured, detailed, and useful to both executive stakeholders and technical teams. This included our findings alongside practical security recommendations.
This responsibility has been sharpening my skill in how to consolidate findings, communicate risks clearly, and recommend actionable improvements which is necessary to turn technical effort into meaningful security insights.
This sprint continues to strengthen both my cloud security knowledge and my experience in project coordination, technical documentation, and team collaboration.
@Cyblackorg
#Cybersecurity #CloudSecurity #MicrosoftAzure #MicrosoftSentinel #ProjectManagement #LearningInPublic #CyBlack
Nine Azure security labs later.🙂↔️This cloud Security Sprint taught me something important, Implementing a security control isn't enough. You need to test and verify that it actually works.
I faced challenges and learnt along the way.
Thank you @Cyblackorg@ireteeh
Sprint 2 (Cloud security) ✅
9 security controls. All 9 tested & validated.
From restricting access to detecting our own simulated attack, we put our Azure security setup to the test.
Biggest lesson?
Untested protection is just decoration.
@Cyblackorg@ireteeh@segoslavia
Second sprint done! @Cyblackorg
Glory be to God, yesterday I presented our Azure Cloud Security Assessment!
From access control to network security and incident response, this was a great learning experience for me.
@ireteeh@NnajiDaniel_C