Can you spot the AI trap or attack?
Knowing scams exist and spotting one in real time are two different skills.
that’s the standard I hold exchanges to, and why @MEXC earns my trust
practice here: https://t.co/Chf3lTxqOC
AI scams are getting harder to spot than the real thing
We built the AI Safety Score with @MEXC to test how safe you really are
Try it now: https://t.co/4Ga4lEx39i
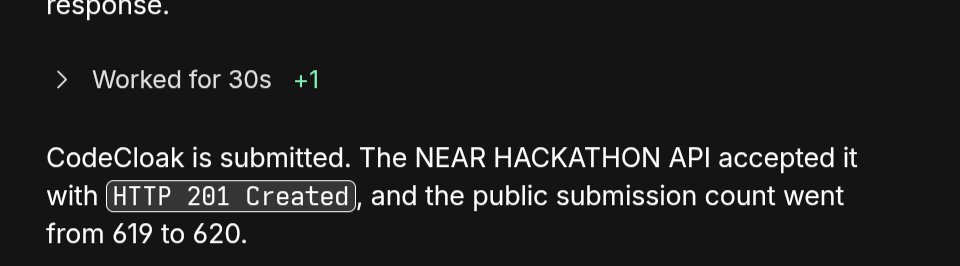
CodeCloak was built and submitted forNEAR HACKATHON
A private multi-agent code review inside @near_ai TEEs.
The hardware has to prove itself before any code leaves.
Full story below, try it:
https://t.co/Gg0peOQL0P
@NEARProtocol#NEARHackathon@NearLegion@NearBuilders
Treat your life like a dataset:
- Track where your time actually goes
- Delete the habits that drain your focus
- Double down on the skills that compound
You cannot fix a life you refuse to measure.
I built the code review Illia asked for.
On October 3rd, @ilblackdragon posted a list of things he wished someone would build.
One of them was:
Code review that is fully private: an agent that verifiably runs code review on private PRs using @near_ai
So I built it. Meet CodeCloak.
The problem
When you send private code to an AI reviewer today, it goes to someone else's server.
It might be logged, cached, kept for 30 days, maybe even used for training. You just have to trust them.
The fix: the room proves itself before your code goes in
Before a single line leaves my server, CodeCloak asks NEAR AI Cloud for a hardware attestation tied to a fresh 32-byte nonce.
Then it checks everything:
→ Intel TDX quotes, verified with dcap-qvl
→ NVIDIA GPU evidence
→ Pinned enclave measurements
The nonce inside every quote, so an old report can't be reused
The enclave's own signing key
If any of those checks fails, it returns a 403 and your code is never sent.
Then the auditors go in
Three agents review your code in parallel inside the enclave.
One looks at security, one at breaking changes, one at quality.
Then they challenge each other's findings, and a moderator makes the final call.
The server counts the votes, not the model. No model can rewrite the verdict.
Receipts for everything
Every answer comes back signed by the enclave's key, and CodeCloak checks each signature against the key it attested earlier.
A full review takes 15 NEAR AI Cloud calls: 1 attestation, 7 completions, and 7 signatures.
Every one is attested or signed, and you get a receipt showing them.
Then your code is gone
Your code is held in memory only. There's no database, no disk, and no logs.
The response keeps a SHA-256 hash of what was reviewed, not the code itself.
In the demo, it caught two high-severity SQL injections in a sample orders API in about 35 seconds.
Fully private code review, verifiably private, on NEAR AI.
Wish granted. 🔒
Video: below 👇
Try it: https://t.co/0JsqqGULaR
Code : https://t.co/m7nwIaWKgg
Nigeria is tightening its stable-coin rules, Bitcoin is facing market pressure, and MEXC is under scrutiny. What's happening in the blockchain space? 👀
In this week's Analytic Sages Weekly Research Brief, we break down three important developments shaping the crypto and Web3 ecosystem.
📌 Nigeria's evolving stable-coin regulations
📉 Bitcoin's recent market decline
⚖️ MEXC's $16 billion AML case
What do these developments mean for the future of digital assets, crypto adoption and the wider blockchain industry?
Get the insights, understand the implications, and stay informed.
🔗 Read the full research brief: https://t.co/Zpr0jaj80D
#AnalyticSages #WeeklyResearch #Blockchain #Bitcoin #Stablecoins #Web3 #CryptoRegulation #CryptoNews