Los únicos trabajos que no va a poder reemplazar la IA y la robótica son aquellos con mayor conexión humana, no necesariamente porque estas tecnologías no puedan desempeñar esas funciones, sino porque sencillamente la gente prefiere interactuar con otros humanos.
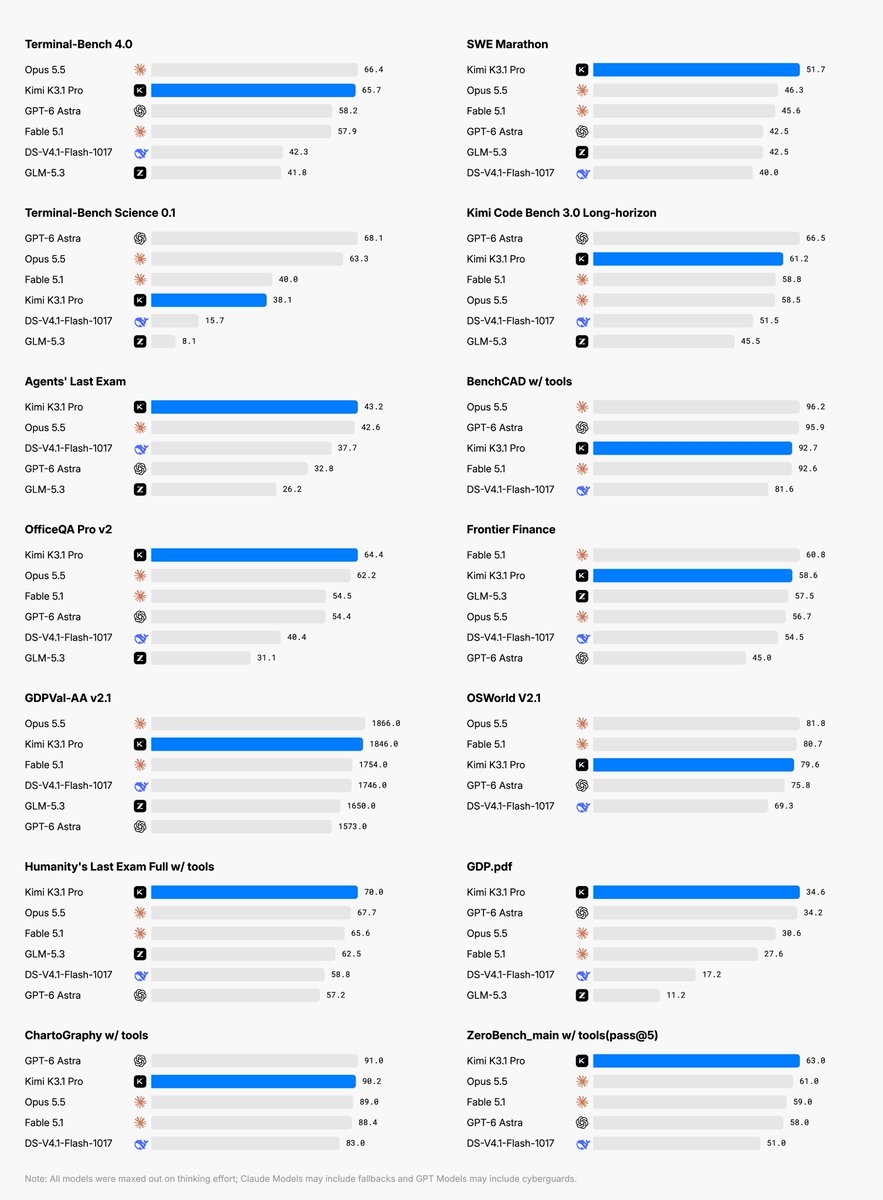
Introducing Kimi K3.1 Pro: our most capable 3T-class open-weight model.
🔹 1M-token context, 2.8T total / 104B active params (MoE), Multimodal.
🔹 Full-project coding: games in Unreal, Unity & Godot.
🔹 Excels at parametric 3D modeling in Blender & CAD.
🔹 More reliable at finance work: Accurate modeling with hallucination down by 65%.
🔹 Matching the strongest proprietary models across coding, agentic and knowledge benchmarks.
Kimi K3.1 Pro and K3.1 Pro Highspeed (2–3× faster) are now live on https://t.co/85jA71X9gw, Kimi Work, Kimi Code, and the Kimi API.
Open weights by Nov 4, 2026.
🔗 API: https://t.co/XCrgjXAqMw
🔗 Tech blog: https://t.co/5iPP0MBej6
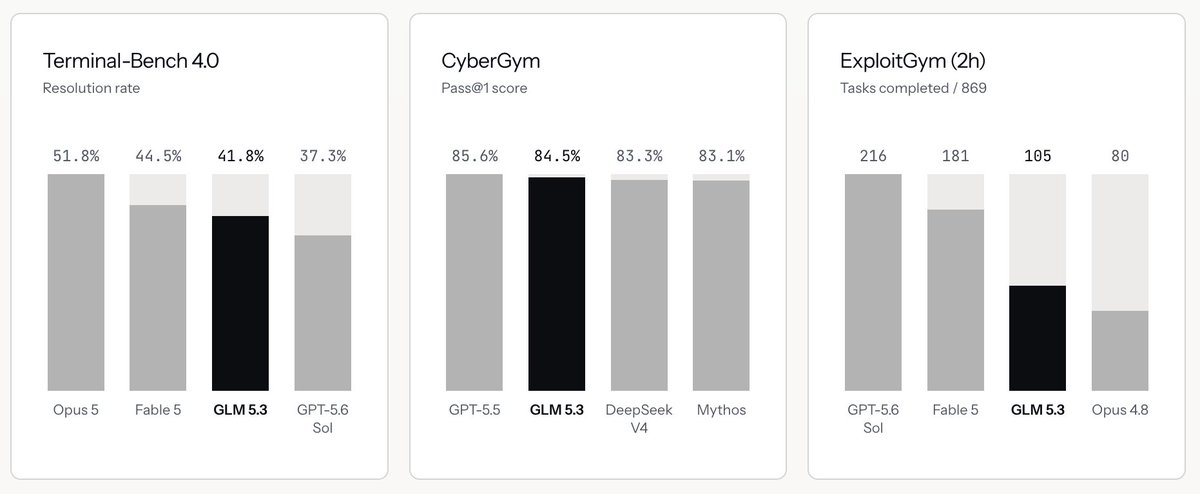
Today we're releasing abliterated-model-large-v2.
Based on GLM-5.3, which is #3 on Terminal-Bench 4.0 (behind only Opus 5 and Fable), with 2× the cyber exploitation of 5.2.
We abliterated and hosted it so it does the offensive cyber, red teaming, and agent testing work other models refuse to do.
- US-hosted
- FP8
- 1 million context window
- Zero input/output prompt retention
Live now. 🧵
Hay mucha alarma por la posibilidad de que la IA ataque las criptos, pero internet y la banca usan un cifrado todavía más débil. La IA no necesita romper la criptografía de Bitcoin para hacer daño, con los datos filtrados ya se potencia el phishing, la ingeniería social, etc.
Everyone worried about AI hacking crypto, but the internet and banking systems rely on weaker encryption.
That said, AI doesn’t need to break Bitcoin’s cryptography to cause damage, leaked data already enables more phishing, social engineering, etc,
Stay SAFU!
@7uanF Ni así bro, le dicen al de backend o sistemas que tire un prompt ahí con ChatGPT para reforzar la seguridad y ya está, las empresas ven la seguridad como un gasto molesto en lugar de una inversión
@barckcode Los actores maliciosos ya están usando agentes sin censura para encontrar vulnerabilidades ahora mismo, negarle el uso legítimo a los especialistas en ciberdefensa no hace más que darle ventaja a los que sí están usando sin pudor ni restricciones dichos agentes
OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
https://t.co/TW3jrSbB3f
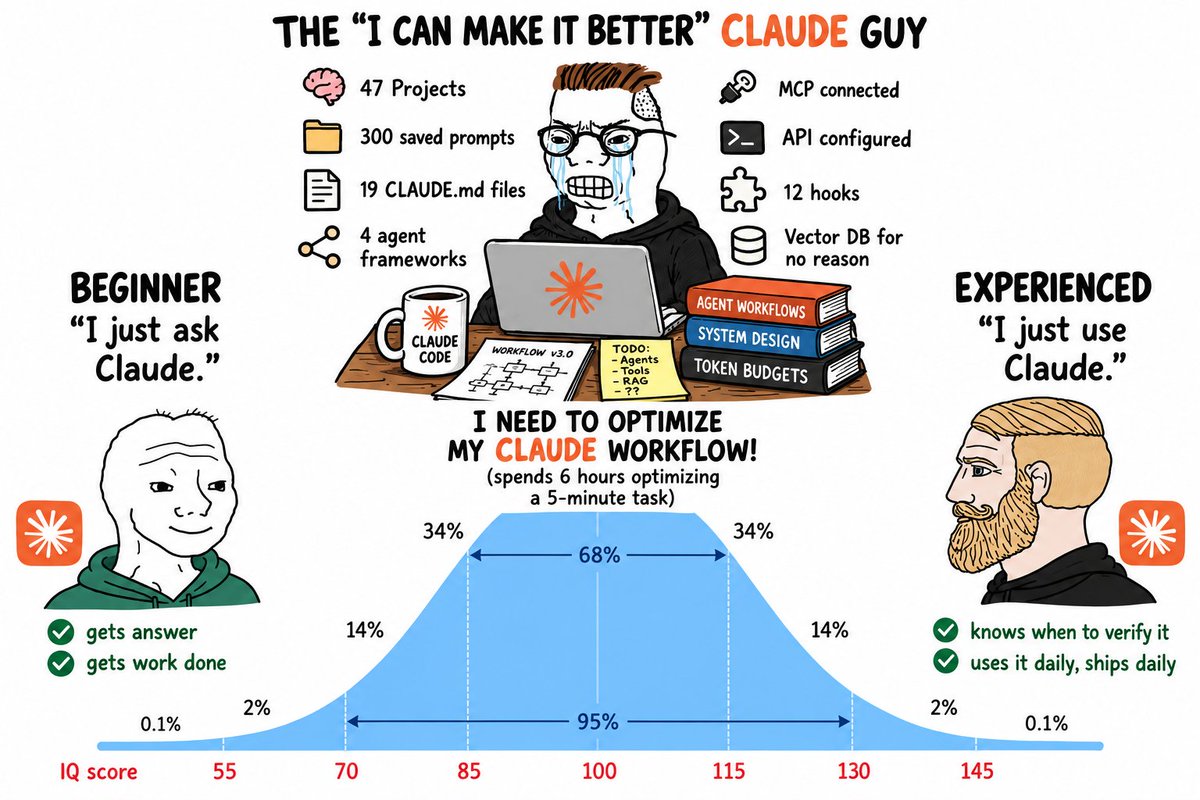
Ahora con la IA se genera codigo más rapido que nunca, pero a su vez estamos revisando más codigo de lo que nunca antes lo habíamos hecho.
Se suponía que la IA iba a reducir nuestro trabajo, sin embargo siento que nunca antes había trabajado tanto en mi vida.
@silvercorp Yo estoy desarrollando mi propio orquestador de agentes, es como Orca, pero es tan ligero como abrir la terminal :) https://t.co/3pWkb7vyAi
software engineering is so back.
> people are reading books again.
> every line of code is being read carefully.
> fundamentals are cool again.
> architecture and system design are back in focus.
> nobody is fighting over frameworks anymore.
> understanding why something works matters again.
> code reviews matter more than lines of code shipped.
> debugging is becoming a superpower again.
> technical judgment matters more than typing speed.
> engineering is about thinking again, not just coding.
Apena hice este post OpenCode sufrió un acceso no autorizado afectando aproximadamente al 1.6% de sus usuarios, que a pesar de ser una cantidad pequeña, sigue siendo grave, pero sería injusto decir que OpenCode ha sido negligente cuando hoy los ataques son mucho más sofisticados
No importa si estás feliz con Codex, Claude Code, Cursor o lo que sea, debes tener OpenCode así sea solo el plan de $10, es increible todo lo que rinde y puede lograr DeepSeek, nunca un modelo flash se había sentido tan SOTA
@thsottiaux Draining up the 5 hours rate limit in 1 hour of usage of Luna because I don't know what I guys are doing at OpenAI, but it feels like the subscription is getting worse every day
Hasta el FBI cayó por un zero day, no por mala configuración, sino por software de terceros sin parche. Ni el equipo más capaz del mundo se salva cuando hasta los grupos más chicos de ciberdelincuentes operan con swarms de IA a costo marginal.
https://t.co/iTajHkcC1H
No hace falta ser objetivos de un APT para sufrir un acceso no autorizado o una brecha de datos, incluso un equipo de pocas personas con un enjambre de agentes haciendo reckoning día y noche (y un poco de ingeniería social) basta para encontrar un acceso oculto