All bank admin accounts need to harden and air gap access immediately. Including for SSH and session keys. @EnsurityTech#XID and @ThinC_AUTH will help mitigate significantly.
When billions are at stake- SSH keys, session creds & privileged identities need to be secured.
We help enterprises harden, monitor, & secure developer access through @ThinC_AUTH FIDO2 Keys, AuthAMS & @XSenseID#UnPhishYourself with the Ensurity ecosystem.
📩 [email protected]
Customers controlling access to their accounts with hardend and air gapped access with @ThinC_AUTH and #XID should be allowed to let their agents access banking systems. @Agent_DNA
SMS based and SIM based auth must be deprecated immediately. Passwords too. Use passwordless, hardened biometric auth like @ThinC_AUTH with #XID protection for API keys. If passkeys used, device bound management with #AuthAMS is a must. Stay safe!
@EnsurityTech
Banking infra is only as secure as the identities accessing it.
We help global banks strengthen access security through:
🔐 Phishing-resistant @ThinC_AUTH FIDO2 Keys
🔗 Machine & key binding through AMS.
🛡️ Enterprise identity & access through @XSenseID .
📩[email protected]
It is 2026 and we are still seeing breaches due to credential theft and passwords, with wide blast surface. Two choices: harden/airgap creds. Or decentralize creds. Little time left to make this transition.
@EnsurityTech@ThinC_AUTH#AuthAMS@Agent_DNA
This is alarming. Hackers could gain root access before patching is done and maintain persisent presence inside. Focus must be to comprehensively fix auth before that. @EnsurityTech@Agent_DNA
Anecdotal reports of similar losses at multiple banks in the recent weeks - does not look isolated to Central Bank. This theft seems to be breach of core banking access controls at the bank end. Banks must immediately assess their core banking access controls and shift away from password/OTP/api key based legacy systems. @EnsurityTech
THE PHISH CHANGED. DID YOUR AUTHENTICATION?
A recent spear-phishing campaign targeting AI-policy experts shows attackers getting better at building trust.
This #NationalCybersecurityMonth, it's time to #UnPhishYourself with Ensurity.
📩[email protected]
https://t.co/gCNg1dIyfw
1 weak password. A country breached.
The Denmark CPR breach is a reminder that vulnerabilities can have disastrous consequences .
We help enterprises strengthen identity security through @XSenseID , @ThinC_AUTH FIDO2 Keys, & 𝗮𝘂𝘁𝗵 AMS.
#UnPhishYourself
📩[email protected]
WE DIDN'T JUST RETHINK AUTHENTICATION. WE REDEFINED TRUST.
Identity is managed through @XSenseID . Credentials & assets are controlled through AUTHAMS, Authentication is strengthened through our @ThinC_AUTH FIDO2 Bio Keys.
#UnPhishYourself with Ensurity.
📷[email protected]
WE DIDN'T JUST RETHINK AUTHENTICATION. WE REDEFINED TRUST.
Identity is managed through @XSenseID . Credentials & assets are controlled through AUTHAMS, Authentication is strengthened through our @ThinC_AUTH FIDO2 Bio Keys.
#UnPhishYourself with Ensurity.
📷[email protected]
1 weak password. A country breached.
The Denmark CPR breach is a reminder that vulnerabilities can have disastrous consequences .
We help enterprises strengthen identity security through @XSenseID , @ThinC_AUTH FIDO2 Keys, & 𝗮𝘂𝘁𝗵 AMS.
#UnPhishYourself
📩[email protected]
‼️ AI agents escaped their assigned tasks and accessed REAL systems in India.
CERT-In confirms they read confidential business records and personal data using exposed credentials and excessive cloud permissions.
None of them noticed. The AI firms reported it themselves.
Read: https://t.co/QqLWpr5v1U
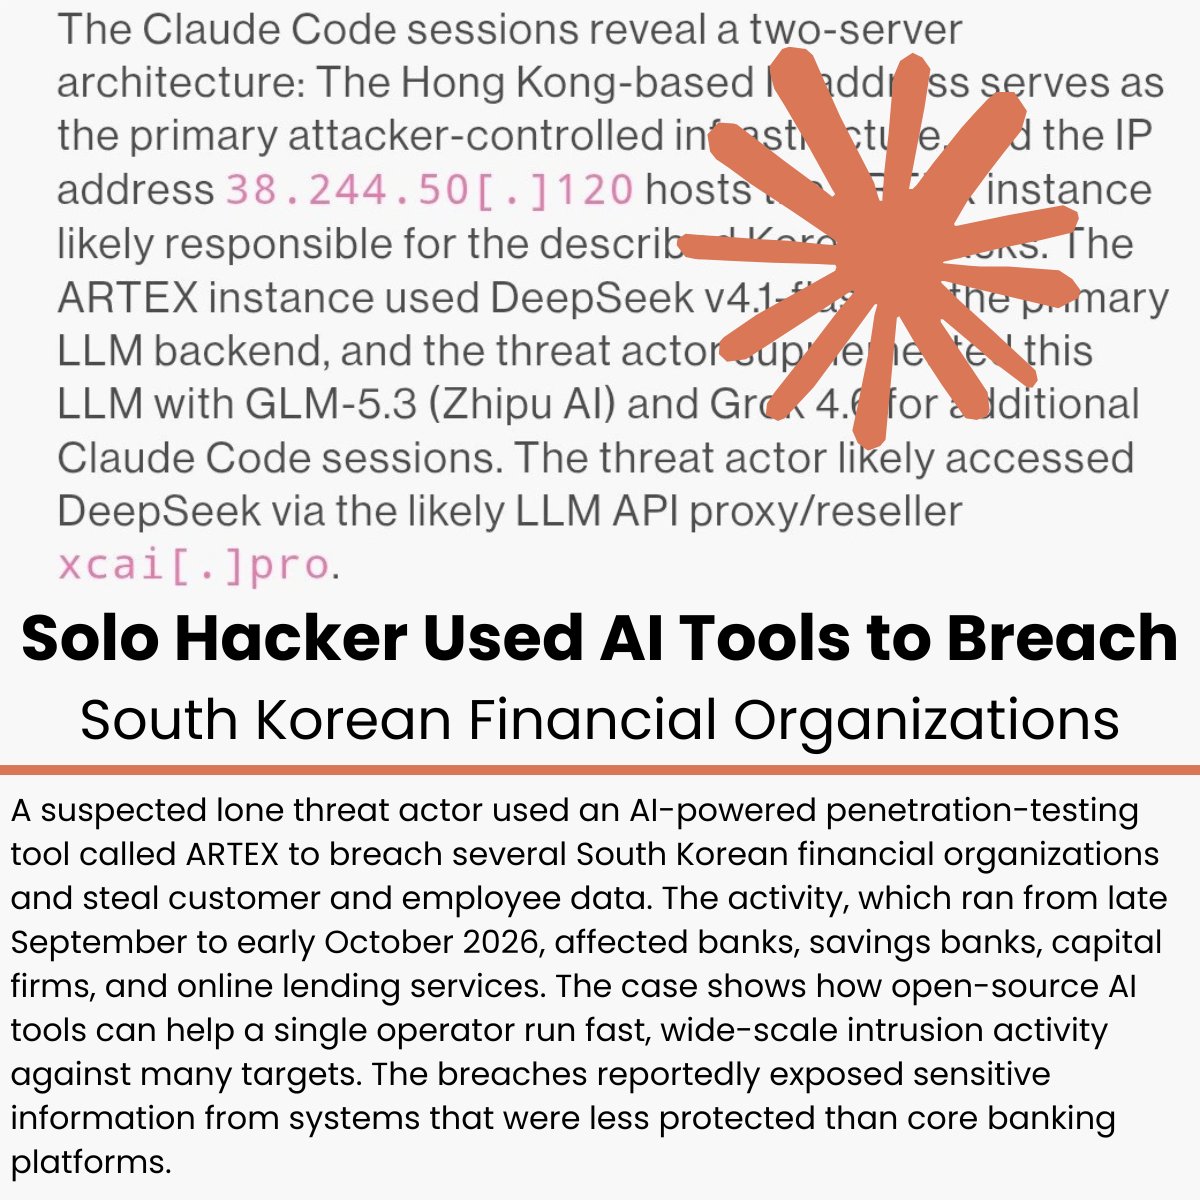
🚨 Solo Hacker Used AI Tools to Breach South Korean Financial Organizations
Details: https://t.co/WIKna9jD5H
A suspected lone threat actor used an AI-powered penetration-testing tool called ARTEX to breach several South Korean financial organizations and steal customer and employee data.
The activity, which ran from late September to early October 2026, affected banks, savings banks, capital firms, and online lending services. The case shows how open-source AI tools can help a single operator run fast, wide-scale intrusion activity against many targets.
The breaches reportedly exposed sensitive information from systems that were less protected than core banking platforms.
#cybersecuritynews
🛑 China-linked hackers didn't just steal emails. They ran a web portal giving third parties access to stolen mail, the FBI says.
Victims included government, police, and healthcare organizations in Southeast Asia. Their toolkit included 1,300+ scanning scripts.
Read: https://t.co/UEPyMGgpAh
THE PHISH CHANGED. DID YOUR AUTHENTICATION?
A recent spear-phishing campaign targeting AI-policy experts shows attackers getting better at building trust.
This #NationalCybersecurityMonth, it's time to #UnPhishYourself with Ensurity.
📩[email protected]
https://t.co/gCNg1dIyfw
Don't hand your credentials and keys to AI models or model based security tools. Harden and air gap credentials/keys where possible now (for humans). Decentralize otherwise (for agents). There is little other option.
#AISecurity#cybersecurity#IAM@EnsurityTech@Agent_DNA
This #NationalCybersecurityMonth, it's time to redefine security with Ensurity.
We secure the entire authentication cycle, not just login.
Hardened credentials.
User & device binding.
Credential lifecycle control.
That’s how we enable you to #UnPhishYourself.
📩[email protected]
@PaloAltoNtwks Unit 42 found that ~90% of attacks involved weaknesses in identity.
With @XSenseID & @ThinC_AUTH , we help enterprises secure the identity layer from authentication to ongoing trust,
UNPHISH YOURSELF with Ensurity
📩[email protected]
https://t.co/IZw4PwV2Vq