1/
📢 Your Conditional Access policies aren't protected by Conditional Access. Unless you turn this on.
There's a feature called protected actions that's worth knowing about. By default, an admin can edit or delete your CA policies using whatever auth they used at their last sign-in - which, under Entra's 90-day default sign-in frequency, could be weeks old.
Protected actions fixes this: Attach a CA policy directly to specific permissions (like creating, updating, or deleting CA policies themselves) so the action is challenged in real time, no matter which role granted the permission.
We now know the Iran war price tag is more like $50 billion - hundreds of dollars per household - and counting.
It's enough to cover all the health insurance premium credits that the Republicans got rid of for this year, and next. It could save rural hospitals, pay teachers, fix roads.
Don't let this White House insult your intelligence by blowing your money on war, then saying America can't afford nice things.
DocuSign Personal: $10 to $15 per month.
DocuSign Standard: $25 to $45 per user per month.
DocuSign Business Pro: $40 to $65 per user per month.
A 10-person team on Business Pro pays $4,800 to $7,800 a year. To put signatures on PDFs.
A team of 50 pays $24,000 to $39,000 a year.
And there is a 100-envelopes-per-year cap on most plans. Send more contracts and you pay extra.
Need SMS delivery? $0.40 per send.
Need ID verification? $2.50 per attempt.
Need premium support? $5,000 to $50,000 per year add-on.
You are rationing digital signatures in 2026.
DocuSign is a $10 billion company built entirely on this pricing model.
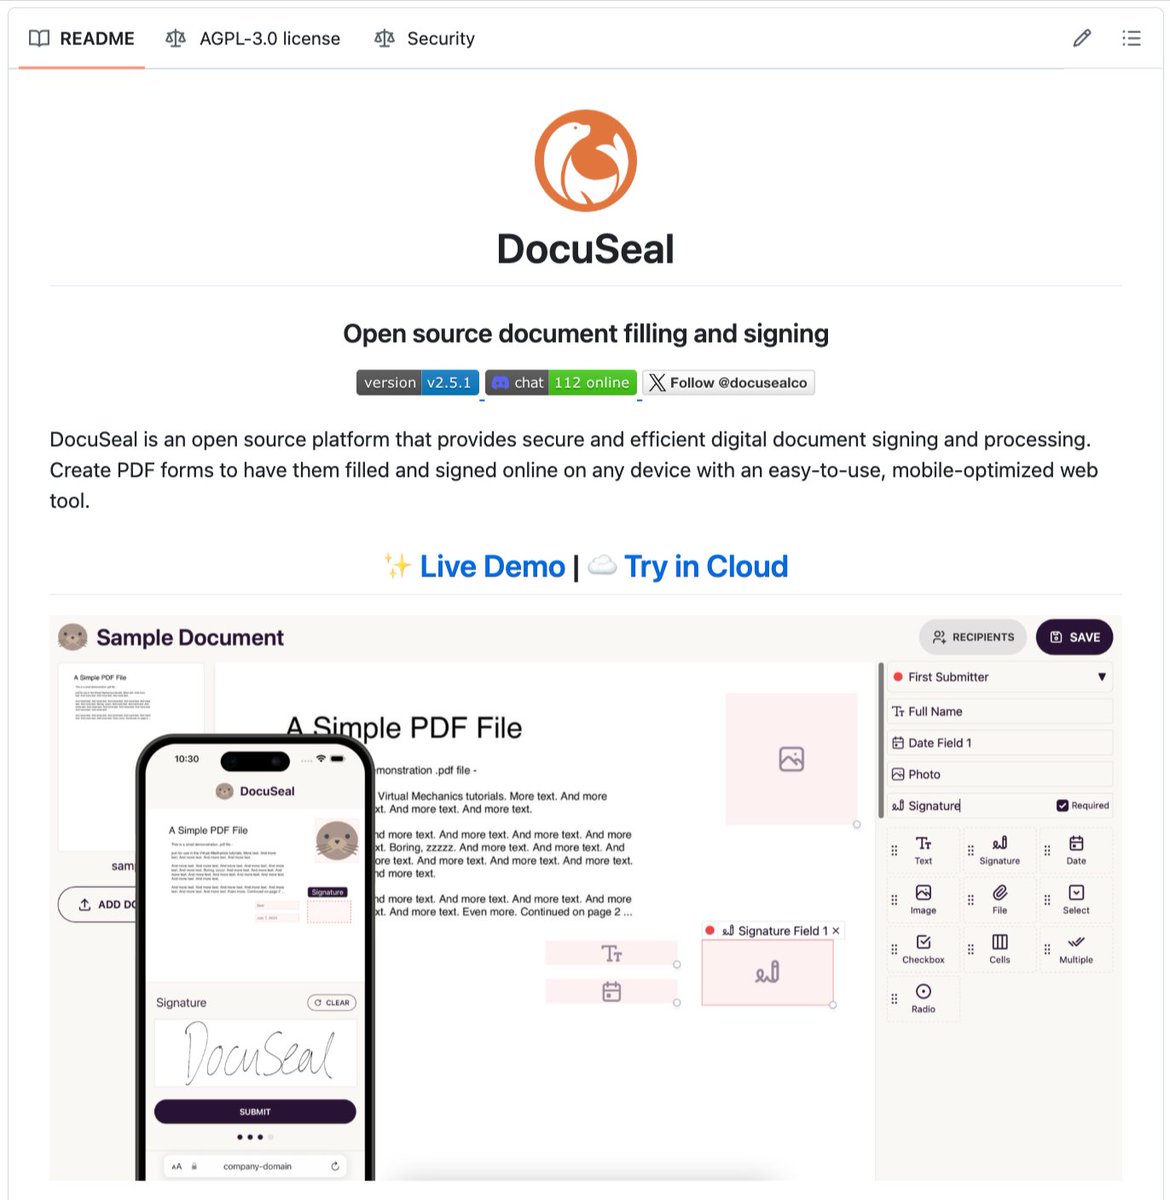
Now meet DocuSeal.
A free and open source alternative to DocuSign.
Created in 2023 by a Ruby developer named Alex who was simply trying to sign one document and realised every solution online was overpriced or required a subscription.
Three weeks later he had a working alternative. He pushed it to GitHub under the AGPL-3.0 license.
Today it has 11,800+ stars and over 1,000 forks. Bootstrapped. No VCs. No paywalls.
Here is what DocuSeal does:
- Upload any PDF and turn it into a fillable, signable form
- Drag and drop signature fields, dates, checkboxes, file uploads, and 13 field types
- Send to multiple signers with custom signing order
- Automated email reminders
- Mobile signing on any device
- PDF signature verification built in
- Audit trail for every document
- Bulk send and templates
- Full API access
- Self-host with one Docker command
Here is what DocuSeal costs:
Zero. Forever. Unlimited documents. Unlimited signers. Unlimited storage.
DocuSign limits envelopes. DocuSeal doesn't.
DocuSign charges per SMS. DocuSeal doesn't.
DocuSign charges for ID checks. DocuSeal doesn't.
DocuSign sees your contracts on their servers. DocuSeal doesn't.
Here is the wildest part:
The median DocuSign contract per Vendr is $17,250 per year. One Reddit thread has people saying "they want me to pay $4.80 per e-signature."
Self-host DocuSeal on a $5 cloud server and a 50-person team can sign as many contracts as they want without paying a single dollar.
Your contracts never leave your server. Your client lists. Your NDAs. Your employment agreements. None of it touches a third-party company.
For individuals who only sign a few contracts a year, you save $180.
For small teams of 10, you save up to $7,800 a year.
For a 50-person company, you save up to $39,000 a year.
Your documents. Your signatures. Your server.
100% Open Source. (Link in the comments)
Age verification sounds reasonable until you realize it means every adult hands over their ID just to go online.
We wrote about why this is a terrible idea and what should happen instead.
https://t.co/vj0bjwHn1J
It’s absurd that American authorities can purchase personal data – that they’re not allowed to gather themselves without a warrant – directly from data brokers. This violates the Fourth Amendment, and it’s time to close the data broker loophole.
Today, @RepThomasMassie, @RepBoebert and @naomibrockwell at the @LudlowInstitute introduced the Surveillance Accountability Act. It requires warrants based on probable cause for all government surveillance and data access. You can read more about it at https://t.co/iFX17ELSLA
Tools the internet doesn't want you to find 🔍
1. Shodan
A search engine for internet-connected devices. You can find cameras, servers, and routers exposed online.
2. Archive. ph
Saves a permanent snapshot of any webpage. Useful when articles go behind paywalls.
3. Similarsites
Enter any website and instantly find dozens of similar ones. Great for discovering alternatives.
4. Mailtrack
Shows you when someone opens your email. You see the exact time it was read.
5. Hunter. io
Type in a company name and it finds employee email addresses linked to that domain.
6. Photopea
A free Photoshop that runs entirely in your browser. No download needed.
7. 12ft .io
Removes paywalls from most news articles. Just paste the link and read for free.
8. Carbon
Turns your code into beautiful shareable images. Popular among developers.
9. Explainshell
Paste any Linux command and it explains exactly what every part does.
10. Tineye
Reverse image search that shows where a photo has appeared on the internet.
11. Namecheckr
Check if a username is available across all social media platforms at once.
12. Untools
A collection of thinking frameworks and mental models to help you make better decisions.
13. BuiltWith
Shows the exact technologies, tools, and software any website is built with.
14. GeoGuessr
Drops you anywhere in the world on Google Street View. You guess the location.
15. Virustotal
Upload any file or paste any link and it scans it with over 70 antivirus engines instantly.
🔒 Secure Bits 💡
𝗬𝗼𝘂𝗿 𝘁𝗲𝗻𝗮𝗻𝘁 𝗵𝗮𝘀 𝗖𝗔 𝗺𝗶𝘀𝗰𝗼𝗻𝗳𝗶𝗴𝘂𝗿𝗮𝘁𝗶𝗼𝗻. 𝗘𝘃𝗲𝗿𝘆 𝗮𝗱𝗺𝗶𝗻 𝗶𝘀 𝗹𝗼𝗰𝗸𝗲𝗱 𝗼𝘂𝘁. 𝗗𝗼 𝘆𝗼𝘂 𝗵𝗮𝘃𝗲 𝗮 𝘄𝗮𝘆 𝗯𝗮𝗰𝗸 𝗶𝗻?
Most organizations don’t — or think they do, until they discover their break-glass accounts are untested, unmonitored, or built on outdated guidance. You don’t want to find that out the hard way, and you definitely don’t want to go through Microsoft’s Tenant Recovery process.
🤔 𝗪𝗵𝘆 𝗰𝗮𝗿𝗲?
A lockout from a bad CA policy, a compromised admin, or a personnel emergency means opening a support ticket with Microsoft and waiting. In urgent situations, you don’t have 14 days for that process.
🧠 𝗪𝗵𝗮𝘁 𝘄𝗲 𝘀𝗲𝗲 𝗶𝗻 𝘁𝗵𝗲 𝗳𝗶𝗲𝗹𝗱
•𝗕𝗿𝗲𝗮𝗸-𝗴𝗹𝗮𝘀𝘀 𝗮𝗰𝗰𝗼𝘂𝗻𝘁𝘀 𝗮𝗿𝗲 𝗺𝗶𝘀𝘀𝗶𝗻𝗴 — Two geographically separated accounts is the baseline.
•𝗚𝗲𝗻𝗲𝗿𝗶𝗰 𝗻𝗮𝗺𝗲𝘀 — admin@…, info@… are not break-glass accounts.
•𝗙𝘂𝗹𝗹 𝗖𝗔 𝗲𝘅𝗰𝗹𝘂𝘀𝗶𝗼𝗻 𝗶𝘀 𝗱𝗲𝗮𝗱 — MFA is now enforced by Microsoft regardless.
•𝗪𝗲𝗮𝗸 𝗮𝘂𝘁𝗵 𝗺𝗲𝘁𝗵𝗼𝗱𝘀 — Phone or certificate-based auth will fail exactly when you need it.
•𝗨𝗻𝗽𝗿𝗼𝘁𝗲𝗰𝘁𝗲𝗱 𝗮𝗰𝗰𝗼𝘂𝗻𝘁𝘀 — Any admin can edit or delete them.
•𝗡𝗼 𝗺𝗼𝗻𝗶𝘁𝗼𝗿𝗶𝗻𝗴 — If someone touches these accounts, you should know immediately.
🛠️ 𝗖𝗿𝗲𝗮𝘁𝗲 𝘁𝘄𝗼 𝗮𝗰𝗰𝗼𝘂𝗻𝘁𝘀
Use descriptive names on onmicrosoft[.]com with a random string — e.g. [email protected]. Assign 𝗚𝗹𝗼𝗯𝗮𝗹 𝗔𝗱𝗺𝗶𝗻𝗶𝘀𝘁𝗿𝗮𝘁𝗼𝗿 as a direct, permanent, active role. No eligibility.
🛠️ 𝗟𝗼𝗰𝗸 𝘁𝗵𝗲𝗺 𝗱𝗼𝘄𝗻
Place both accounts and their group inside an 𝗥𝗠𝗔𝗨 (requires Entra P1). Manage access via a custom PIM role — max 1-hour activation, approval required, auth context enforced (requires Entra P2).
🛠️ 𝗖𝗼𝗻𝗳𝗶𝗴𝘂𝗿𝗲 𝗮𝘂𝘁𝗵𝗲𝗻𝘁𝗶𝗰𝗮𝘁𝗶𝗼𝗻
Scope a passkey profile to the break-glass group with specific AAGUIDs for your hardware keys (YubiKey, Token2). Enforce via a custom authentication strength in a dedicated CA policy. Exclude the group from all other CA policies — run a What If to verify only your two break-glass policies apply.
🛠️ 𝗦𝗲𝘁 𝘂𝗽 𝗮𝗹𝗲𝗿𝘁𝗶𝗻𝗴
Stream AuditLogs and SignInLogs to a Log Analytics Workspace (requires Azure subscription). KQL alert rule on the break-glass Object IDs — any event fires immediately.
🛡️ 𝗦𝘁𝗼𝗿𝗲, 𝘁𝗲𝘀𝘁, 𝗱𝗼𝗰𝘂𝗺𝗲𝗻𝘁
Each passkey + PIN in a separate physical location. Define who can trigger the procedure and under what circumstances. Test end-to-end at minimum every 180 days — Microsoft recommends 90. Pick your cadence, but validate.
💬 When was the last time you tested these accounts?
𝘈𝘶𝘁𝘩𝘰𝘳: Martin Strnad
PS: We will soon 𝗽𝘂𝗯𝗹𝗶𝘀𝗵 𝗳𝘂𝗹𝗹 𝗴𝘂𝗶𝗱𝗲 on this topic!
#EntraID #IdentitySecurity #ConditionalAccess #SecureBits #HorizonSecured
We are very happy that today Apple issued a patch and a security advisory. This comes following @404mediaco reporting that the FBI accessed Signal message notification content via iOS despite the app being deleted.
Apple’s advisory confirmed that the bugs that allowed this to happen have been fixed in the latest iOS release. You can read more here: https://t.co/yE8ufSTQHk
Note that no action is needed for this fix to protect Signal users on iOS. Once you install the patch, all inadvertently-preserved notifications will be deleted and no forthcoming notifications will be preserved for deleted applications.
We’re grateful to Apple for the quick action here, and for understanding and acting on the stakes of this kind of issue. It takes an ecosystem to preserve the fundamental human right to private communication.
Age verification is moving off websites and into your operating system (yes, even you, Linux).
California just passed a law requiring it. The UK already has it. More states are following.
Here's why that's a much bigger deal than it sounds. 🧵
1/6
What I learned from 1,000 hours of internal pentesting in 2025.
- LAPS is not as common as you’d think
- The built-in domain Administrator account is often misused as a service account
- Flat, non-segmented networks are the norm
- Too much stock is put into EDR alone
- File shares are never checked for credentials
- Many IT admins don’t know they have ADCS
I could go on.
On the bright side, I truly believe these are some of the most solvable IT security issues.
If we can’t eliminate credentials from shares how do we expect to defend against more serious issues…
Curious what else I see during internal pentest? I wrote more about this on my blog.
Read more: https://t.co/Qc49zMhil9
🚨 Top 5 Live Intelligence Dashboards You Should Be Watching
If you're tracking cyber threats, geopolitical tensions, or OSINT signals in real time, these platforms provide a powerful “single pane of glass” into what’s happening globally:
🌍 LiveUAmap – Real-time conflict and geopolitical event tracking
🔗 https://t.co/HV7wR0jxD4
📊 GDELT Project – Global event monitoring powered by AI across dozens of languages
🔗 https://t.co/Y3468LUhoI
🌐 WorldMonitor – Live global incidents, disasters, and security alerts
🔗 https://t.co/1qMzK0Dtaq
🛡️ SOCRadar Cyber Conflict Dashboard – Focused cyber threat intelligence (Iran–Israel context)
🔗 https://t.co/d4MNtnQ1OM
🧠 Pizzint – OSINT-driven monitoring of leaks, dark web activity, and threat signals
🔗 https://t.co/GutduD8Bif
These dashboards highlight how OSINT + real-time data + visualization are reshaping situational awareness for both cyber and physical threats.
👉 If you know other high-quality live intelligence dashboards, drop them in the comments — always looking to expand the list.
#OSINT #CyberThreatIntelligence #ThreatIntel #Geopolitics #DarkWeb #CyberSecurity #DDW #InfoSec #OpenSourceIntelligence
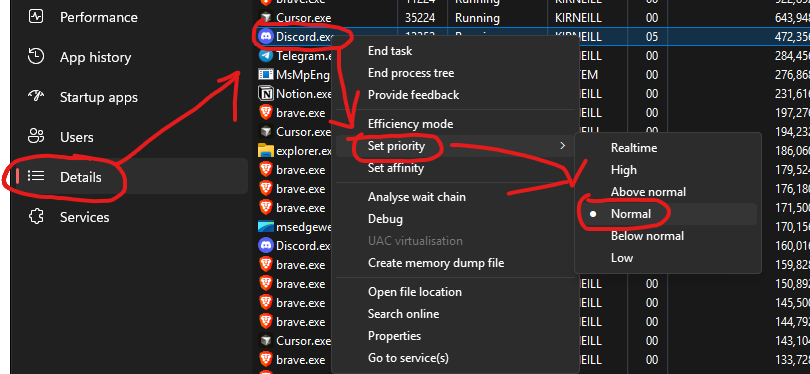
Discord is secretly running at Real Time priority on your PC.
This causes frametime spikes in CS2, Valorant, and basically every competitive game.
Fix: Task Manager → Details → Discord.exe → Set Priority → Normal
One change. Instant smoother gameplay.
Scientists just cracked the multiple sclerosis code after decades of searching.
Two specific gut bacteria are triggering the disease, and they've proven it using identical twins and mice.
This changes everything we know about MS:
THE WHEELS ARE FULLY TURNED AWAY FROM THE OFFICER.
Watch in SLOW MO.
No intention IMO to hit anyone.
Sole intention based on wheel/steering wheel to LEAVE the scene
NOT A THREAT.
Look at the wheel.
🚨WARNING: GRAPHIC VIDEO
This is video showing the ICE agent shooting a woman in the face as she attempted to leave.
This is disgraceful, horrific, and must be denounced by ALL.
In a few days, you may be notified that your health insurance premiums will double, because of Republican cuts to health care. Democrats are fighting to change that before it's too late.
So far, Republicans would rather shut down the government. So Americans face flight delays, reduced services, and mounting economic damage.
It's time for Trump and Republicans to change course on health care and reopen the government.
I feel like this photo of masked, armed men pepper spraying a pastor protecting his community is going to be a defining picture of this moment in America for a long, long time.
A message from a Kindergarten teacher:
After forty years in the classroom, my career ended with one small sentence from a six-year-old:
“My dad says people like you don’t matter anymore.”
No sneer. No malice. Just quiet honesty — the kind that cuts deeper because it’s innocent. He blinked, then added, “You don’t even have a TikTok.”
My name is Mrs. Clara Holt, and for four decades, I taught kindergarten in a small Denver suburb. Today, I stacked the last box on my desk and locked the door behind me.
When I started teaching in the early 1980s, it felt like a promise — a shared belief that what we did mattered. We weren’t rich, but we were valued. Parents brought warm cookies to parent nights. Kids gave you handmade cards with hearts that didn’t quite line up. Watching a child sound out their first sentence felt like magic.
But that world slowly slipped away. The job I once knew has been replaced by exhaustion, red tape, and a kind of loneliness I can’t quite describe.
My evenings used to be filled with construction paper, glitter, and glue sticks. Now they’re spent filling out digital reports to protect myself from angry emails or lawsuits. I’ve been yelled at by parents in front of twenty-five children — one filming me with his phone while I tried to calm another child mid-meltdown.
And the kids… they’ve changed too. Not by choice.
They arrive tired, anxious, overstimulated. Their tiny fingers know how to swipe a screen before they can hold a crayon. Some can’t make eye contact or wait in line. We’re expected to fix all of it — to patch the gaps, heal the trauma, teach the curriculum, and document every move — in six hours a day, with resources that barely fill a drawer.
The little reading corner I once built, full of soft beanbags and paper stars, was replaced by data charts and “learning metrics.” A young principal once told me, “Clara, maybe you’re too nurturing. The district wants measurable results.”
As if kindness were a weakness.
Still, I stayed. Because of the small, holy moments that no spreadsheet could measure —
a whisper of, “You remind me of my grandma.”
a shaky note that read, “I feel safe here.”
a quiet boy finally meeting my eyes and saying, “I read the whole page.”
Those tiny sparks were my reason to keep showing up.
But this last year broke something in me.
The aggression grew sharper. The laughter in the staff room turned to silence. The light went out of so many eyes. I watched brilliant teachers — my friends — vanish under the weight of burnout, their joy replaced by survival.
I felt myself fading too, like chalk on a board that’s been wiped one too many times.
So today, I began my goodbye. I pulled faded art off the walls and tucked thirty years of handmade cards into a single box. In the back of a drawer, I found a letter from a student from 1998:
“Thank you for loving me when I was hard to love.”
I sat on the floor and cried.
No party. No applause. Just a handshake from a young principal who called me “Ma’am” while checking his notifications.
I left my rocking chair behind, and my sticker box too. What I carried with me were the memories — the faces of hundreds of children who once trusted me enough to reach out their hands and learn. That can’t be uploaded. It can’t be measured. It can’t be replaced.
I miss when teachers were partners, not targets. When parents and educators worked side by side, not in opposition. When schools cared more about wonder than numbers.
So if you know a teacher — any teacher — thank them. Not with a mug or a gift card, but with your words. With your respect. With your understanding that behind every test score is a heart that cared enough to try.
Because in a world that often overlooks them, teachers are the ones who never forget our children.