New research from @MSFTResearch found that editing fewer than ten neurons could turn a capable agent model into a sleeper agent that passes all evaluations but runs an attacker’s command with the agent’s environment access when a trigger string appears in its context. https://t.co/PZRb8ulov5
On Nov 17 at 2:20 PM ET, FEMA and @FCC will conduct a nationwide test of the Emergency Alert System on TV and radio. This legally required, regularly scheduled test ensures critical, life-saving messages can reach Americans when it matters most during major emergencies.
PHP2Shell, a Brotli decoder vulnerability, and the eMudhra certificate authority key issue each require attention. Microsoft is updating the services it operates and releasing fixes for affected products.
Customers should review the issue-by-issue guidance for updates and actions in environments they manage: https://t.co/TeJSVIOZWK
[Watching the news while traveling and the local traffic report starts]
"Traffic is backed up on FeebaWumble all the way to Skipabid. If you're working in The Grampa, you should definitely take Route 88÷6Alpha to NeffaStwp Boulevard. Now to Jimmy with the weather"
Microsoft Threat Intelligence is tracking an active supply chain attack in which a threat actor compromised the trusted OAuth App of the backup application ConnectWise Cloud Backup (AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae), formerly SkyKick Backup, to obtain access tokens across customer tenants.
ConnectWise Cloud Backup is a multitenant vendor application; customers grant consent for the application to operate in their tenants. We assess that the threat actor likely abused permissions previously granted by customers to the application, including highly elevated permissions like Directory.ReadWrite.All.
On October 15, 2026, we observed broad successful service principal authentication originating from the IP address 144.172.64[.]128. Follow-on activity included Microsoft Graph API reconnaissance and attempts to add additional credentials on the related service principal in target tenants to maintain direct access as a backdoor.
Microsoft Defender detects post-exploitation activity with the following alerts:
- Any alert related to "Suspicious sign-in"
- Graph API activity from a Microsoft threat intelligence IP address
- Verified Threat Actor IP
Defenders should review service principal sign-ins from unrecognized IP addresses, app credential changes, and OAuth grant activity associated with this specific OAuth AppId. In addition, we recommend looking for Threat Intelligence alerts on matching of IP against the Graph API activity and service principal activities.
We will continue to monitor this incident and will share updates as they become available. We encourage customers to check ConnectWise advisory for more information and additional guidance: https://t.co/zwFyMAzaEV.
Indicators of compromise (IOCs):
- App name: ConnectWise Cloud Backup
- AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae
- Publisher name: SkyKick
- Source IP: 144.172.64[.]128
- User agents: Python-urllib/3.12, python-requests/2.31, python-requests/2.34.2
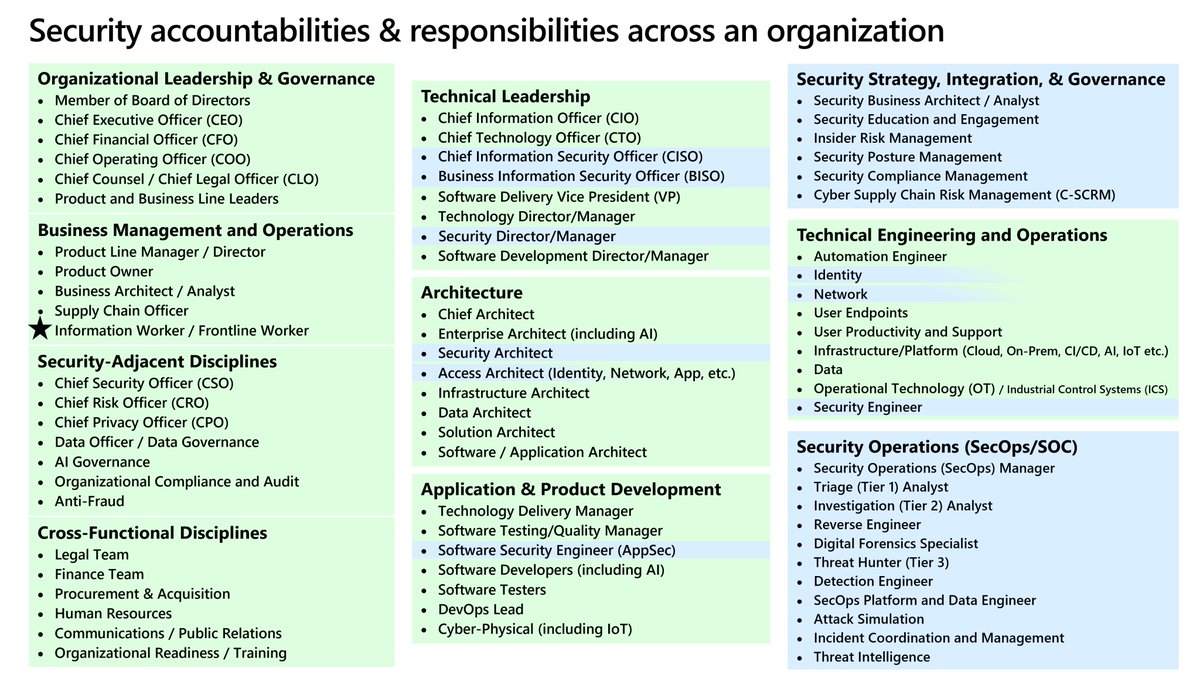
Security is a Team Sport
…but if you have no idea who the players and positions are, you are probably going to lose most of your games.
All roles in an organization have a critical part to play in avoiding the next cybersecurity crisis, including YOU! 🙂
👇