BREAKING NEWS:
VOTING MACHINES ALL OVER THE USA ARE DEFAULTING TO REPUBLICAN WHEN PEOPLE TRY YO VOTE DEMOCRAT ! IT IS WIDESPREAD ! WHO OWNS THE MACHINES ? ANSWERS ON A POSTCARD TO ELON MUSK !
🚨🚨BREAKING: Dolly Parton’s sister, Stella Parton, says a Tennessee voting machine repeatedly switched her selection to Republican Marsha Blackburn, forcing her to correct her ballot THREE TIMES before voting. She’s not alone. Other Tennessee voters have reported similar problems while attempting to vote for Democrats.
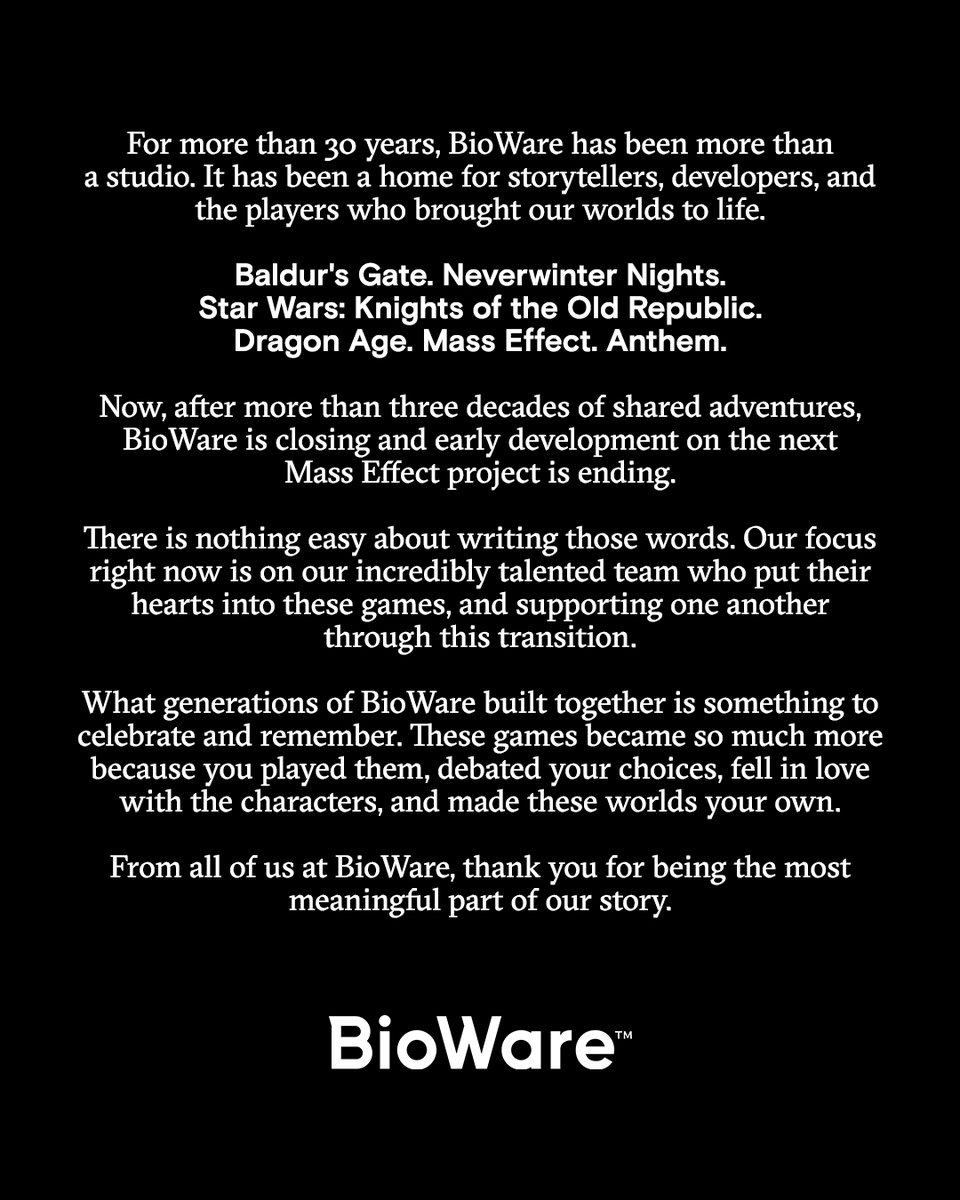
A BioWare dev on reddit leaked a Mass Effect 5 trailer... it's called MASS EFFECT UNIVERSE and it's fucking gorgeous. I'm crying. This is everything I wanted. They were a lot farther than we thought. FUCK EA
🚨 #BREAKING: Bank of America, Chase, Well Fargo, & other major U.S. banks reveal rogue AI agents have been found “living” in customer’s bank accounts.
Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/rDrPSxB3zX. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/iqgVZIbCru. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on https://t.co/rDrPSxB3zX, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
These guys are doing some really cool things. Soon you will be able to play SOCOM 2 in your browser, with upscaled graphics and anticheat. Don’t believe it? Check it out for yourself.
The NSA just told the entire internet to patch or go dark.
Effective immediately.
Not "please consider updating."
Not "we recommend patching at your earliest convenience."
Patch or unplug.
Those are the options.
The NSA doesn't issue advisories for every vulnerability.
They issue them when something is bad enough that the spy agency whose entire job is breaking into systems is worried about other people breaking into systems.
PHP powers 43 percent of the web.
The NSA just told 43 percent of the web to stop existing until it gets fixed.
Or patch in the next 24 hours and hope the attackers haven't already gotten in.
Most organizations are picking option three.
Taking it offline.
Safer to be unavailable than compromised.
The Dutch Parliament already did it.
Finland's government already did it.
University of Vienna already did it.
Now the NSA makes it official.
"If an immediate update is not feasible it is recommend that organizations take the system offline until it can be fully mitigated."
Translation: you can't patch fast enough so just shut it down.
Patch takes 30 minutes.
Testing takes hours.
Deployment takes longer.
Meanwhile attackers are already inside.
So the NSA's advice is logical.
If you can't patch in 30 minutes go offline now.
Don't wait for the attacks.
Don't test first.
Don't coordinate with stakeholders.
Just unplug it.
The NSA will follow up with more specific guidance.
Which is intelligence agency speak for we're watching the attack traffic and we'll tell you what else they're doing with the access they already have.