Seems that folks successfully achieved working RCE w/ a previous RTF/Win exploit! This is expected as #MonikerLink is a powerful attack vector (delivering exp) on Outlook - it bypasses Protected View too!
Now u have more reasons to PATCH & GET PROTECTED!
https://t.co/esPv5KUJpd
AD CS: New Ways to Abuse ManageCA Permissions.
Any standard user with a ManageCA ACL can publish CRL Distribution Points and move arbitrary files to a restricted directory (C:\Windows\System32, etc).
https://t.co/6yH6MwbNEw
#infosec#redteam#cybersecurity#Pentesting
Mythic just got an update! ✨
Check out @its_a_feature_'s latest blog post for a rundown of the updates made in Mythic v3.2, including:
✅ Push C2
✅ Interactive Async Tasking
✅ Dynamic File Browser
Read more! https://t.co/ncumn1ajnA
New blog: Obtaining Domain Admin from Azure AD by abusing Cloud Kerberos Trust
I teased this a bit during my Windows Hello talks, now found some time to write about this interesting technique. Also contains defenses and detection opportunities.
https://t.co/KSPVRm5iGo
Want to know what fsutil devdrv actually does? Here you have it:
1. devdrv enable -> FsEnableDevDrive=1 in CCS\Control\FileSystem
2. disallowAv -> FltmgrDevDriveAllowAntivirusFilter=0 in CCS\Control\FilterManager
3. clearFiltersAllowed -> FsFlags + FsGuid in CCS\Control\FileSystemVolumes\{VOLUME_GUID}
4. trust -> DeviceIoControl(FSCTL_SET_PERSISTENT_VOLUME_STATE, PERSISTENT_VOLUME_STATE_TRUSTED_VOLUME)
Now you can enjoy the bypass without touching fsutil.exe 😎
New blog post: Deception in Depth - Hiding AD Users & Groups Part 1
https://t.co/qg8KWJnhfI
In this post, we explore the ability to deny read privs on privileged accounts & set the framework for future blog posts involving creation of deceptive OUs, Users & Groups in AD!
I've approved a new version of https://t.co/nLVZJFKO5m. Thanks to all contributors especially @chudyPB for so many new gadgets!
📃See @chudyPB🤯"130 page" research: https://t.co/afHjboqPlX
📽️Video here: https://t.co/RtiQQjbaLF at @hexacon_fr#AppSec#DotNet#Deserialization
Miss @chudyPB's talk on .NET deserialization bugs during @hexacon_fr? You can check out his full white paper at:
https://t.co/MNNuqkZC49
And be sure to catch his exploit videos for #Exchange (https://t.co/rViksCihNf) and #SolarWinds (https://t.co/8Ituruzlaw)
People were saying I'm not on smoke.
After sitting on this for 2 years, I've decided to refute this claims by releasing yet another SaaS data exposure piece, but this time for ServiceNow. Enjoy!
https://t.co/P7fDLRkVsb
#servicenow#SaaS#CyberSecurity
Wrote a blog post for my company on how we implement obfuscation for our C# post-exploitation arsenal. Discussing some detection opportunities and our ways around them. Special thx to @Flangvik for his video on SharpCollection, which is our pipelines base
https://t.co/px6kyIS7jL
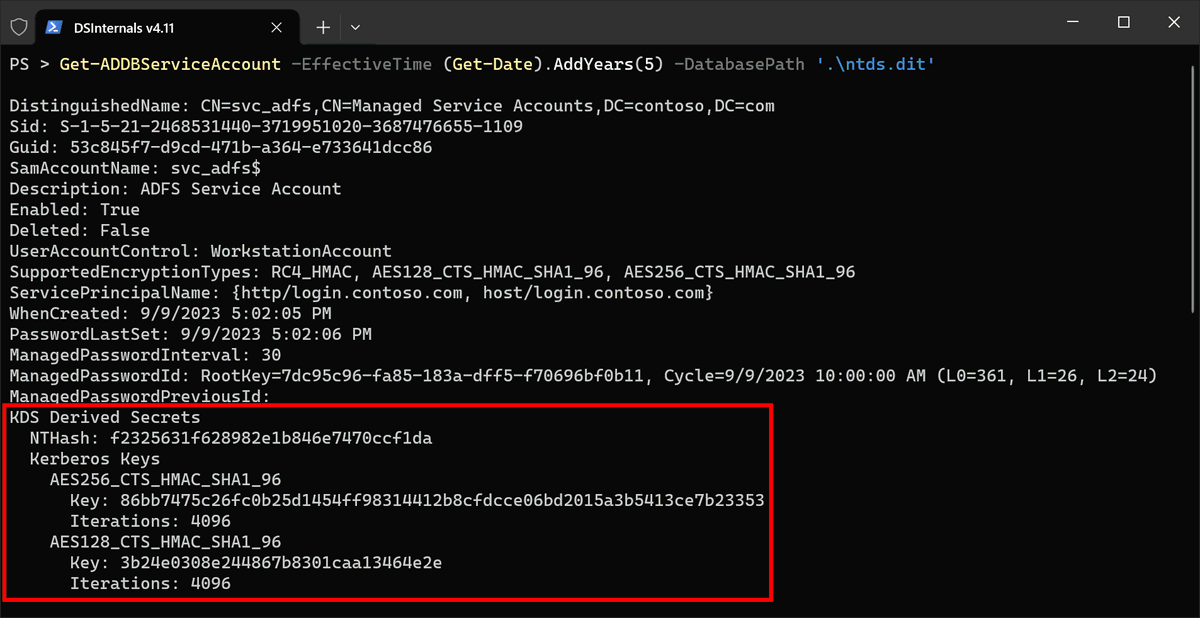
Introducing a new offline variant of the Golden gMSA attack against AD with time shifting. Enables Pass-the-Hash and Silver Ticket attacks. Requires access to ntds.dit backup and works until a new KDS Root Key is generated. #DSInternals CC: @YuG0rd
https://t.co/poMhPmDdPn
Exploiting ASP .NET TemplateParser to get RCE in Sitecore (CVE-2023-35813) and SharePoint (CVE-2023-33160) by @mwulftange in two parts: part 1 at https://t.co/viBnUPO9kU is live now and part 2 will follow in a few days...stay tuned!
Have you ever wanted to extract, decode and decrypt all NTDS.dit data? We are glad to share with you a new tool: ntdissector by @kalimer0x00 and @Julien_Legras, powered by the awesome lib dissect.esedb from @foxit! More info in the blogpost: https://t.co/HJJKFjd5YD
My Okta for Red Teamers post is up! We look at how Kerberos SSO works, how to intercept credentials via a fake AD Agent, decrypting AD Agent tokens, adding skeleton key's, and even how to deploy a janky SAML IdP server to auth as any user for good measure. https://t.co/Hs0wN5397s
We would like to express our condolences to Blue Teamers.
Microsoft has announced Microsoft Excel will now support Python.
More information: https://t.co/LutCzlYc0x