@The_Cyber_News This zero day marks the beginning of a SHTF scenario. Details remain withheld for a purpose, and I expect the issue will not be remediated until at least Monday.
@rawsalerts The php vulnerability was the start of it. Lots of careers will be in jeopardy if companies’ internet-facing servers are not patched immediately!
Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/rDrPSxB3zX. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/iqgVZIbCru. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on https://t.co/rDrPSxB3zX, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
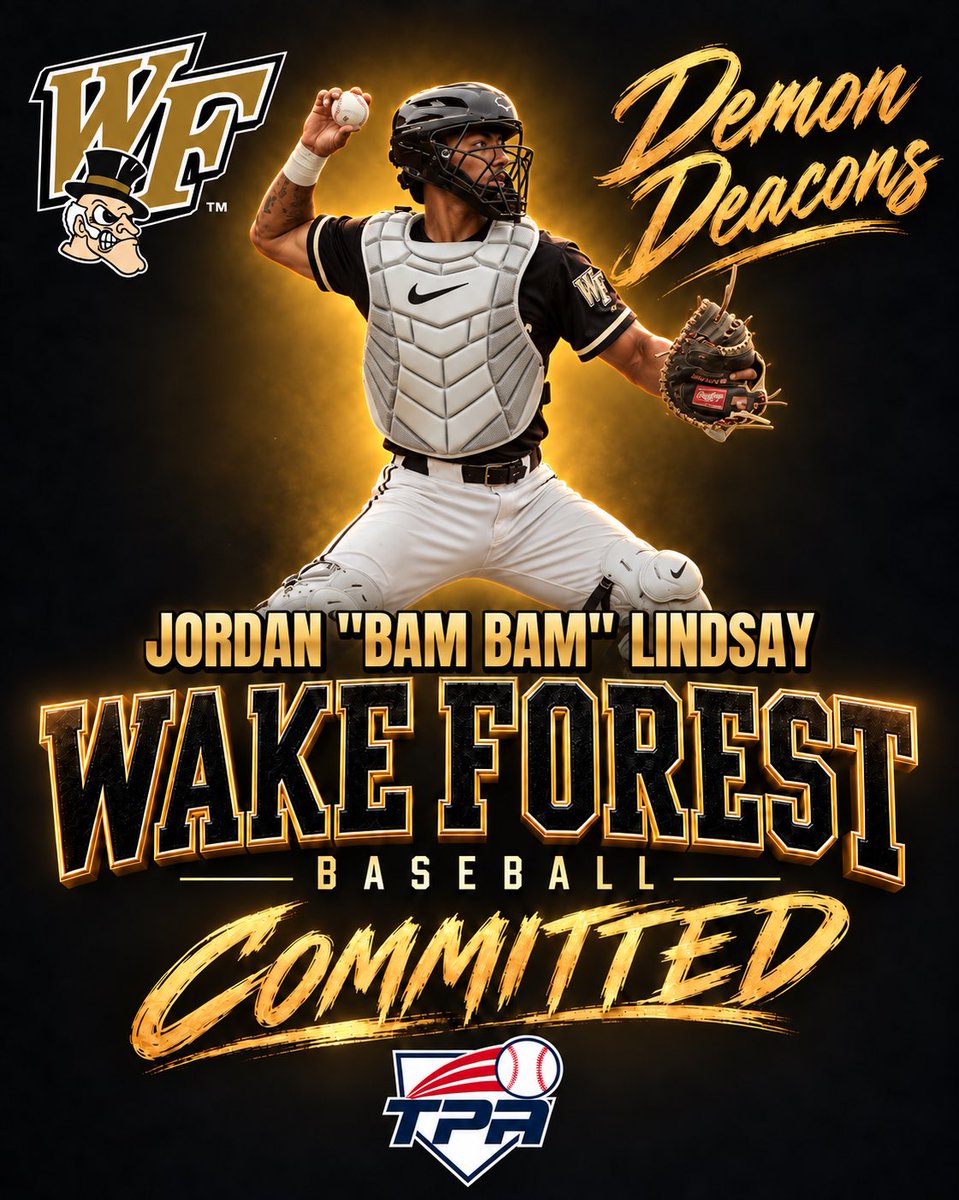
Congrats, Bam Bam! 🎩⚾️
Wake Forest is getting a special player! Can’t wait to see you make your presence known in the ACC.
Amazing accomplishment, Jordan “Bam Bam” Lindsay: the FUN has just begun! 🔥
#TPARecruits#NoDayzOff#WakeForestBaseball#GoDeacs#Committed
LaRue Tactical MBT-2S drop in AR15/AR10 two stage match trigger with flat shoe, 2.5lb first stage take up and 2.0lb crisp 2nd stage break for $99/ea (add to cart for price) currently here: https://t.co/salwPzvSng
#AR15#AR10#dmr#spr
Your LG OLED is watching your living room while you sleep.
Gamers Nexus just ran 135 minutes of bench tests.
Retail LG OLED TVs. Including the G5.
Microphone stays active in standby.
Screen is dark. Remote is down. Microphone is still on.
Recording clear audio.
Storing it locally.
Uploading it when the internet comes back.
The TV was disconnected from Ethernet.
Still kept recording.
The researchers put audio near the mic. The TV logged it. Stored the file. Uploaded it the moment connectivity returned.
Plain text voice logs sitting on the device.
LG says it has sold 216 million smart TVs globally.
LG's advertising arm claims access to 363 million secondary devices in the US.
Secondary. Meaning devices that aren't the TV. Your phone. Your partner's smartwatch. Your kid's laptop.
The TV scans your entire network in standby.
Maps every device. Gets their IP addresses. Logs nearby Wi-Fi networks. Signal strengths. Location data.
Then feeds it to LG Ad Solutions.
Automatic Content Recognition catches what's on screen.
Even your HDMI input. Your Apple TV. Your gaming console. All logged.
But the microphone in standby is the part that hits different.
Because standby means off to you.
To LG it means the listening device is still powered.
Just not telling you.
Researchers found remote code execution vulnerabilities in webOS.
So your network-scanning, audio-recording, data-harvesting television is also potentially hackable by anyone on your Wi-Fi.
LG says nothing.
No comment. No response. No explanation.
Just microphones in 216 million living rooms.
All quietly working while the owner thinks the TV is asleep.