The @FBI and @TheJusticeDept have announced the disruption of Virtualine, a so-called “bulletproof hosting” service designed to help cybercriminals evade detection and law enforcement action.
Before the FBI and its partners shut it down, the Virtualine[.]net domain was used to facilitate the distribution of child sexual abuse material (CSAM), international money laundering, and numerous other cybercrimes.
The case was investigated by @FBIWFO, with significant assistance from Germany’s Polizei Hessen, the Netherlands’ Politie Midden-Nederland, the UK’s National Crime Agency, and private sector partners OverRIPE and Lumen. The Justice Department’s Office of International Affairs provided additional support.
https://t.co/AqE9SfAW0O
Earlier today, Artem Aleksandrovych Stryzhak, 35, of Barcelona, Spain, was sentenced to nearly six years in prison. Stryzhak conspired with others to deploy the Nefilim ransomware against victim computer networks in the United States and other countries, causing significant damage to victim computer systems.
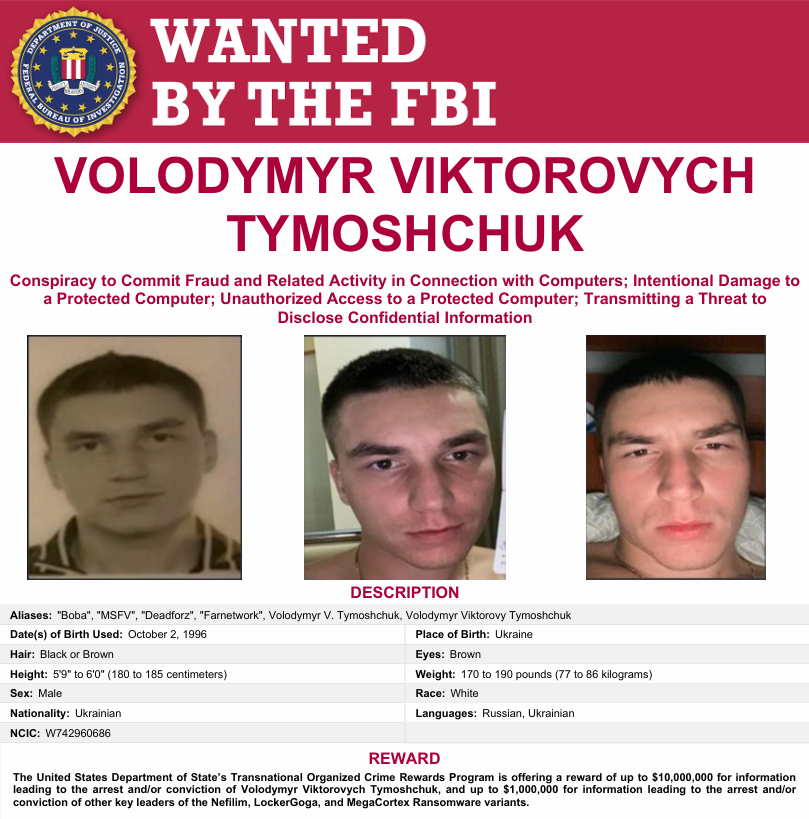
The @FBI is seeking further information on co-conspirator Volodymyr Viktorovych Tymoshchuk. Currently, there is an award of up to $10,000,000 for information leading to the arrest and/or conviction of Volodymyr Viktorovych Tymoshchuk, and up to $1,000,000 for information leading to the arrest and/or conviction of other key leaders of the Nefilim, LockerGoga, and MegaCortex ransomware variants.
If you have any information concerning this person, please contact the FBI via WhatsApp or Signal (neither government-operated nor government-controlled platforms) at (917) 242-1407. You may also email [email protected], or contact your local FBI office or the nearest American embassy or consulate.
https://t.co/mNZbFnhJy4
Last week, #FBI Louisville participated in the 2026 Cyber Bluegrass Blue Team Summit, Kentucky's premier cybersecurity training and exercise event. It brings together government, military, and private sector professionals to strengthen our collective cyber resilience.
The FBI continues to warn about two critical security flaws in PHP, a programming language used to build many websites and online services. Attackers could exploit these vulnerabilities to break into systems, putting sensitive information and business operations at risk. Security updates are available and should be applied immediately.
If you are a business owner or website operator, check whether your systems are affected. Contact your IT support team, website developer, or hosting provider for help identifying vulnerable systems and applying the necessary updates.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/JFOW6jG9Ws. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/ZWC7Se2YdU. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information on these vulnerabilities (CVE-2026-109618 and CVE-2026-109619), follow PHP’s announcements on https://t.co/JFOW6jG9Ws, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
In an interview with John Riggi of the American Hospital Association, Brett Leatherman, Assistant Director of FBI's Cyber Division, discussed Operation Riptide, which brought more than 200 arrests, six extraditions, and numerous takedowns of malicious infrastructure during a 60-day push against cybercrime and cyber-enabled fraud. AD Leatherman explained how those actions advance the FBI’s cyber strategy and help protect healthcare organizations and other critical infrastructure.
@FBI cyber teams have become “exceptionally good at attribution,” AD Leatherman said, identifying people behind attacks and pursuing them aggressively. Even when actors are beyond the immediate reach of US law enforcement, the FBI is finding ways to seize their funds, dismantle their tools, and disrupt operations. Each of those actions reduces harm and makes it costlier to target US victims.
That work couldn’t be done without private sector partners. In the #cyber domain, the FBI needs industry as an equal partner in the fight, with trust built before a crisis. The FBI wants to use its partnership with the AHA as a model for equally effective cooperation across critical infrastructure sectors.
https://t.co/X5dnmzwhCD
Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/rDrPSxB3zX. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/iqgVZIbCru. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on https://t.co/rDrPSxB3zX, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
The @FBI and our partners are releasing detailed, actionable guidance to help network defenders protect their organizations from SafePay, one of 2026’s most active ransomware groups.
SafePay actors have already targeted more than 600 victims worldwide across multiple critical infrastructure sectors. Today’s Joint Cybersecurity Advisory, developed with @CISAgov, @SecretService, and international partners, outlines steps organizations can take to reduce their risk and limit the impact of a SafePay ransomware attack.
https://t.co/wGWO3F4hNp
A Nigerian man has been sentenced to eight years in prison for a series of fraud, hacking, and identity theft offenses.
Beginning in 2019, Chukwuemeka Amachukwu and his co conspirators carried out a scheme targeting U.S.-based tax preparation businesses. They used spearphishing emails to break into these firms’ systems, stealing sensitive customer information. With this compromised PII, the conspirators filed fraudulent tax returns with the IRS and state tax authorities, obtaining at least $2.5 million in illicit refunds.
Learn more about @NewYorkFBI's investigation: https://t.co/o3ixYOcMdb
North Korea thought American companies were its personal ATM — to bankroll its nuclear weapons program. NOT ON OUR WATCH.
Operation Lonestar Roundup: 14 charged. 2 arrested. 187 devices seized. 40+ suspected Texas laptop farms. 70+ U.S. companies affected. ~$3M allegedly funneled to the DPRK.
-DKP🇺🇸
Strengthening International Cybercrime Partnerships!
Last week in Skopje, #FBI Jacksonville joined U.S. and North Macedonia partners for a specialized cybercrime investigative workshop. Coordinated by the U.S. Department of Justice’s International Criminal Investigative Training Assistance Program (ICITAP), the workshop brought together approximately 30 investigators, including representatives from North Macedonia’s Ministry of Interior, Bureau for Public Security, Sector for Cybercrime and Digital Forensics.
The workshop opened with remarks from the Director of the Bureau of Public Security for the Ministry of Interior in North Macedonia and provided an opportunity to exchange investigative expertise and share best practices.
The engagement reflects continued collaboration among ICITAP, the U.S. Department of State’s Bureau of International Narcotics and Law Enforcement Affairs (INL), the U.S. Embassy in Skopje, the FBI Law Enforcement Attaché Office in Sofia and North Macedonia law enforcement partners on cybercrime investigations and emerging digital threats.
#FBI #FBIJacksonville #Cybercrime #NorthMacedonia
#ICYMI: We sat down with Spectrum News to talk about how cyber criminals are utilizing SI to exploit our systems and what you can do to keep yourself safe.
Watch here, and don't forget to report any online crime to the Internet Crime Complaint Center (IC3): https://t.co/wljdpwinhp
This week, the @FBI and DOJ announced coordinated actions in Ohio and Texas to counter the North Korean IT worker threat. The effort included raids on suspected “laptop farms” and resulted in charges, arrests, and the seizure of nearly 190 devices.
Brett Leatherman, Assistant Director of the FBI’s Cyber Division, sat down with CrowdStrike’s Adam Meyers to examine the broader threat behind these actions. They discussed North Korea’s ongoing efforts to infiltrate American companies through remote IT workers and how the FBI and industry are working together to combat the threat.
These recent actions, like many of the FBI’s most significant cyber operations, were made possible by intelligence and technical expertise from industry partners. The FBI is strengthening these partnerships to “move upstream” against cyber threat actors. That means going beyond responding to individual incidents to proactively target the command-and-control infrastructure, tools, and criminal ecosystems that enable their activity.
https://t.co/CcExE8kpeD
Cyber threats cross borders, so the @FBI must maintain global reach. Our Cyber ALATs work alongside partners around the world to turn shared intelligence into coordinated action against threat actors.
This week, FBI Cyber Assistant Law Enforcement Attaché (Cyber ALAT) Kathryn Sherman spoke with BNY employees at the U.S. embassy in London about the threat landscape. In banking, trust is everything. ALAT Sherman discussed how criminals exploit that trust through increasingly sophisticated manipulation of human behavior.
The FBI will continue to deploy Cyber ALATs in strategic locations to assist our partners and combat the evolving cyber threat.
Today at the 10th annual Boston College Cyber Security Conference, @FBI Operations Director Joe Perez, who oversees the Criminal and Cyber Branch, discussed the evolving threat landscape and how the FBI is putting the National Cyber Strategy into action.
OD Perez congratulated @FBIBoston on this year’s Operation Masquerade, a worldwide effort to disrupt a Russian military intelligence campaign that hijacked internet traffic and stole sensitive data.
He also highlighted the FBI’s efforts to combat “cyber-enabled crime,” from overseas scam centers that systematically target Americans to criminal organizations stealing millions through healthcare and investment schemes. He emphasized that we are disrupting these networks, seizing illicit proceeds, dismantling call-center infrastructure, rescuing victims when possible, and working with international partners to bring perpetrators to justice.
#FBI Boston's Special Agent in Charge Ted Docks kicked off our 10th annual Boston Conference on Cybersecurity @BCLAW today bringing together leaders in law enforcement, academia, & the private sector to discuss best practices in creating a more secure cyber-space amidst the growing threats posed by nation-states and cybercriminals.
Last year, Americans reported losing more than $20 BILLION to cybercriminals. New Englanders lost almost $600 MILLION - which is only a fraction of the true cost - highlighting the magnitude of this threat. Among the hardest hit: healthcare, information technology, and government services.
Special thanks to #FBI Operations Director Jose Perez who delivered the keynote address outlining the #FBI's new cyber strategy, which is Actor Focused, Victim Centered, and Partner Driven as we work to make cybercrime harder, riskier, and far less profitable for those behind it. Learn more about the ways in which you can partner with us: https://t.co/Nwl5tHrHC6
At a press conference yesterday, @FBIDallas Special Agent in Charge R. Joseph Rothrock announced that FBI Dallas and other field offices conducted operations at more than 40 Texas residences and seized approximately 187 laptops and KVM devices used in fraudulent remote IT employment schemes.
North Korean IT workers allegedly used stolen identities and U.S.-based facilitators to gain access to American corporate systems and generate revenue for the regime’s weapons programs.
The FBI will continue working with law enforcement and private-sector partners to disrupt these networks and protect U.S. businesses and national security. Companies with information about suspected schemes should report it at https://t.co/WJUOFLirqy.
🔗 https://t.co/DnmqnwaKuG
The @FBI congratulates our partners at the North Macedonia Bureau of Public Security's Cybercrime Unit from the Ministry of Interior on the successful arrest of the OLVX criminal marketplace administrator.
Active between 2023 and 2025, OLVX is alleged to have unlawfully sold victims’ personally identifiable information (“PII”) and login credentials via over 1,500 seller accounts. The existence of this marketplace directly endangered the digital security of thousands of American citizens who rely on the integrity of accounts they use.
This disruption marks the first-ever cyber operation coordinated between the FBI and North Macedonia and reflects the FBI’s commitment to working with partners around the world to protect the American people in cyberspace.
https://t.co/yoP6VmrpVQ
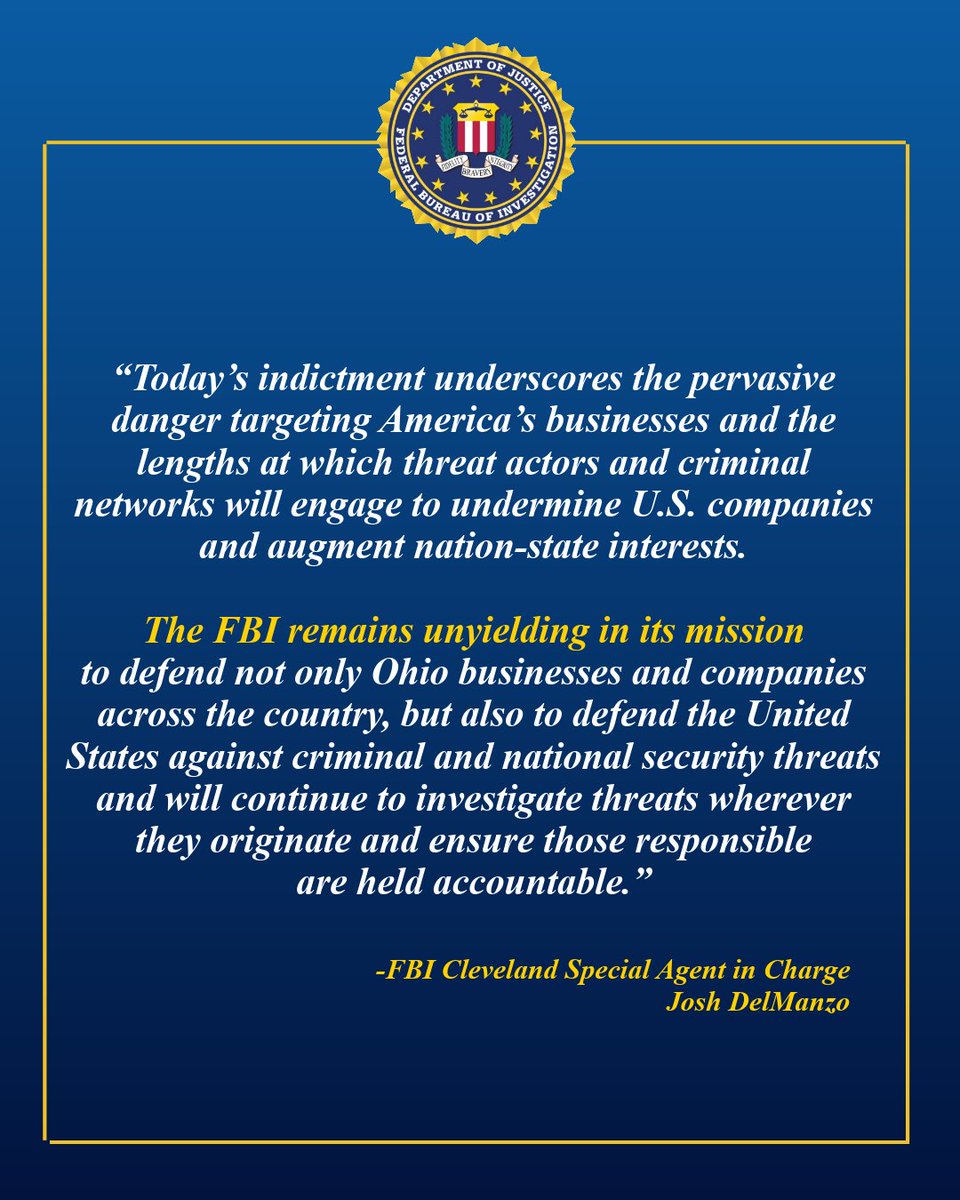
Thanks to an FBI Cleveland investigation, the US Attorney's Office of Northern Ohio indicted 14 individuals who targeted and subsequently victimized 70 businesses as part of a remote IT worker conspiracy. Read more: https://t.co/gw1Asmga2c
SAC Rothrock spoke at a press conference announcing the results of Operation Lonestar Roundup, an enforcement action conducted across the state of Texas that resulted in the seizure of approximately 187 laptops and devices. More than 100 of those devices were seized in the North Texas area.
These devices are tied to a hosting network that enabled Democratic People's Republic of Korea IT workers to unlawfully access U.S. corporate systems using stolen or falsified American identities.
Learn more at: https://t.co/51YZTxDaKh
Thousands of North Korean IT workers are infiltrating companies across the world, generating millions of dollars for the North Korean regime and gaining access to sensitive corporate networks.
Posing as legitimate remote employees, they use stolen identities, earn salaries from unwitting companies, exploit their access to steal data, and funnel their earnings back to North Korea.
The scheme relies on a network of facilitators – including Americans – who are paid to appear on camera, participate in job interviews, verify fraudulent identities, and keep employment-related devices connected to the internet at personal residences.
U.S. companies should recognize the scale and persistence of the threat and review our updated @FBI PSA for mitigation guidance: https://t.co/CcExE8kpeD