I've reverse engineered the infamous NSO Group's Pegasus spyware for Android. Check out the article if you want to know how it implements its functionalities. https://t.co/Tj4tLV5IUU #pegasus#spyware#dfir
#Malware_analysis
1⃣. Hugging Face Malware Campaign
Returns to Hijack GPUs for Crypto Mining
https://t.co/ayqMefME5D
2⃣. DeepSeek Kong RAT
https://t.co/NvXzbbOPyB
3⃣. Trojanized Claude Code Extension Plants an SSH Backdoor
https://t.co/f2ar5mYKwA
4. https://t.co/zbzWsKbPt8
🔎 That top DeepSeek search result might not be what it seems.
🧨 Fake installer → signed binary → DLL side-loading → Kong RAT
New on the Hybrid Analysis blog: Vlad Pasca unpacks the whole campaign 🧵
https://t.co/46eF6S15XB
#ThreatIntel#SEOPoisoning#CyberSecurity#Deepseek
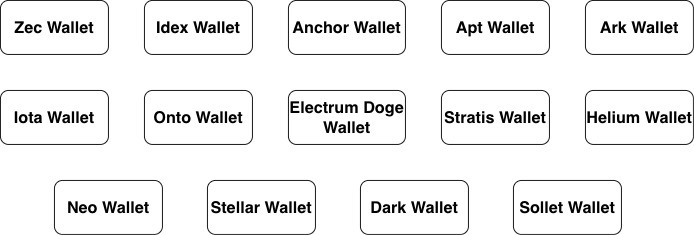
I've recently analyzed a suspected russian threat actor that created fake crypto wallets and deployed a Russian RMM tool. Targets include Anchor, Zec, Iota, Onto, Dark, and Stellar wallets as oversized Advanced Installers. Full analysis at https://t.co/BixbL1LM21. #crypto#dfir
I've recently analyzed a suspected russian threat actor that created fake crypto wallets and deployed a Russian RMM tool. Targets include Anchor, Zec, Iota, Onto, Dark, and Stellar wallets as oversized Advanced Installers. Full analysis at https://t.co/BixbL1LM21. #crypto#dfir
#Malware_analysis
1. Bandook RAT - C2 Traffic Analysis
https://t.co/tXXvPrbE1o
// IOC extraction, protocol analysis, and detection notes
2⃣. VELVET CHOLLIMA Infostealer Campaign
https://t.co/JRv7nggcCW
// Final payload is MoonPeak, a custom variant of the open-source XenoRAT malware
3⃣. Gentlemen RaaS
https://t.co/uPHFH9vzzY
// The group actively evaluates CVE-2024-55591-https://t.co/nQJG3gBkqI, CVE-2025-32433- https://t.co/tSxk6Rc6he, CVE-2025-33073- https://t.co/2T97IwM5wr and combines them with technique‑driven paths like backup and management‑controller abuse and NTLM relay workflows