@Volatility Core Dev | Art of Memory Forensics co-author | Sr. Director of Adversary Tactics @HuntressLabs | #DFIR enthusiast/trainer | [email protected]
PSA: Don’t forget to give a fuck. Give a fuck about what you do. Be intentional. Continue to better yourself. Remove things and people in your life who don’t add value.
And have a good day!
These two live to cast themselves as the main characters in a little soap opera of their own making.
It’s not the rise of skynet to find a fucking php vuln and your warnings mean jack when they don’t come with an effective mechanism for replacing technical debt at scale so go ahead and climb up off that cross.
Storm-0940, a China-state aligned actor, used the agentic AI penetration testing framework ARTEX to automate attacks targeting hundreds of organizations globally across a broad range of industries. Several of these Storm-0940 ARTEX-driven attacks have resulted in the actor obtaining privileged access to an organization’s cloud infrastructure – including multiple instances where the time from initial targeting to privileged access was less than 3 hours. Microsoft assesses that Storm-0940 was responsible for the recently disclosed ConnectWise supply chain compromise of a multi-tenant application.
https://t.co/aKrkgXLeFk
Heading to @BSidesAugusta this Saturday, October 24? Catch @Volexity's Director of Research, Andrew Case (@attrc), at 10:00 AM (Track 1 - Plug N Play) for his talk, “Finding Evil Fast: Windows Memory Triage with Volatility 3”.
See the full conference schedule here: https://t.co/oykJZyPHAL
#memoryforensics #dfir #volatility
Periodic reminder that for every serious, exploitable vulnerability that you find out about and patch, there was some level of exploitation of it *before* then.
Someone told me last week to look for “signposts” that might indicate attacks were getting significantly faster and worse than the historical norm. Do you think we’re seeing any of those?
@mgreen27@fr0gger_ That’s fair. Maybe just DFIR blue teamy type things in general would be good, but was curious what type of offerings there might be out there
What's a good class to take for someone who wants to learn more about using AI in threat hunting? I know @fr0gger_ 's class is really good, are there some others that people would recommend?
🤓 Our training Practical AI for CTI (renamed AI Threat Intelligence Bootcamp) is getting an update! You will learn methodologies for hunting adversarial AI agents, AI attackers infrastructure, prompt hunting and more!
The training will be available at @BlackHatEvents Europe (almost sold out) and Black Hat Asia.
I’ll share more updates in the next few weeks!
You can already book for Black Hat Asia! 👇
Cc: @SecurityBreakAI
https://t.co/VjOSkMRSbJ
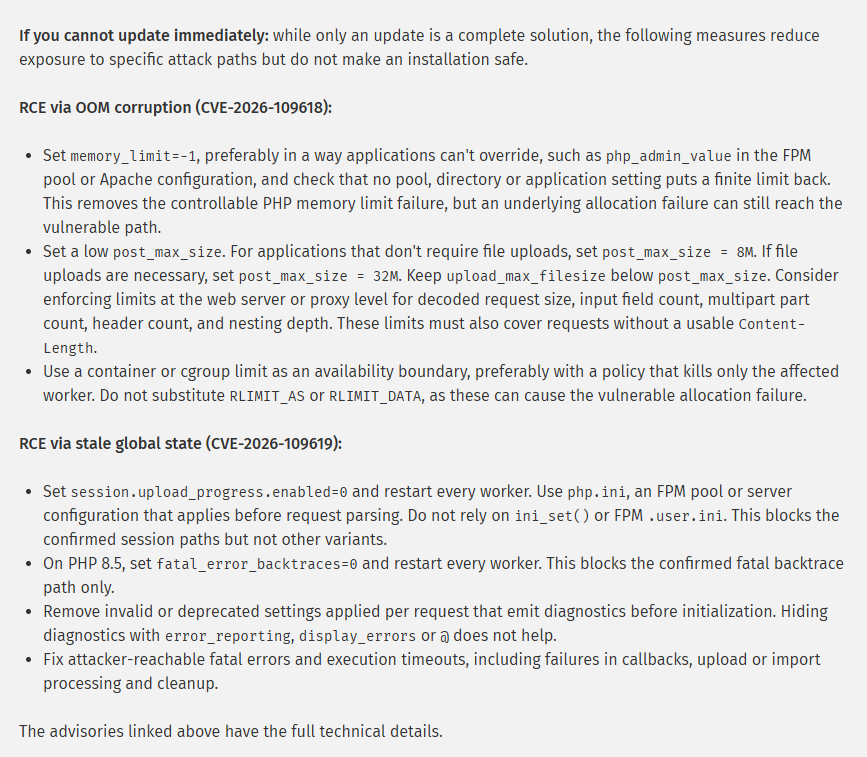
The PHP team released 8.5.12, 8.4.27, 8.3.36, and 8.2.35 to address two remote code execution CVEs. All PHP installations serving web requests are at risk, making patching urgent.
Read our updated blog for the latest: https://t.co/3MTEUlPE5W
We’re officially at capacity! Thank you to everyone who registered for the upcoming @Volexity Cyber Sessions in Amsterdam. Registration is now closed.
If you’d still like to attend, join the waitlist and we’ll notify you if a spot opens up: https://t.co/jVirRurpjo
We look forward to seeing registered attendees on October 29 for an afternoon of DFIR talks, followed by an evening of dinner, drinks & networking!
#dfir
Transition from vulpocalypse to breachpocalypse is here. IR firms are saturated & turning away work. Now one hacker unleashed AI agents on 1,200+ websites, compromising 100+ for ~$5,000 in tokens. $50 per hack. Agents won and compromised targets. https://t.co/30wJxs7iIY
New: The FBI believes an exec at a prestigious U.S. consulting firm (1,000+ associates) helped run Shinywire, the ShinyHunters site used to extort nearly 100 victims.
The people victims hire to negotiate with hackers may have been on the other side of the table.
- Dutch police raided ShinyHunters suspect Pepijn van der Stap with flash-bangs while he was logged into Signal
- His chats showed frequent contact with ransom negotiators in the U.S. and Canada
- Those negotiators often knew about new victims before the victims knew they'd been breached
- Per sources, Edward Dubrovsky, a Canadian negotiation exec charged earlier this month, knew ShinyHunters had the FBI's personnel files and never told the FBI
- Dubrovsky's other firm, CyberSteward, helped PowerSchool pay its ~$2.85M ransom
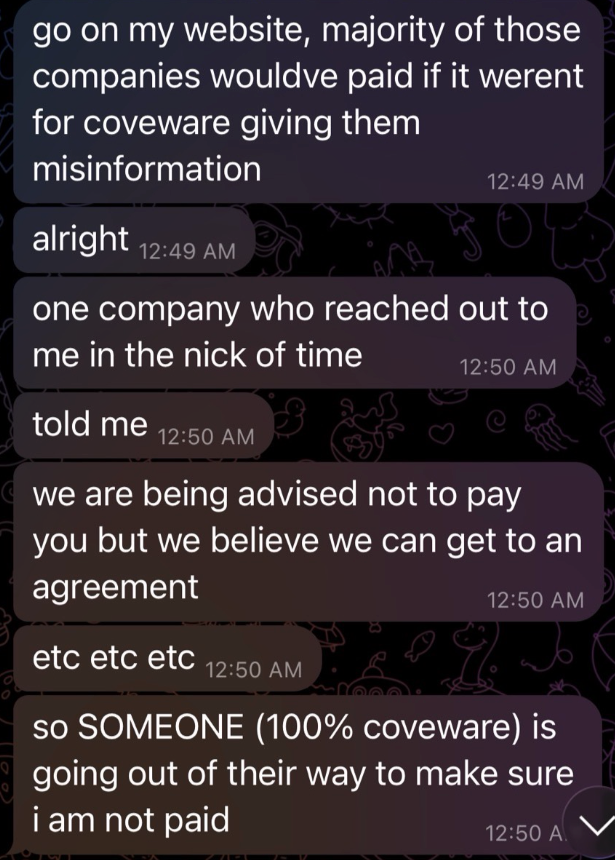
Meanwhile ShinyHunters was griping on Telegram that Coveware kept telling victims not to pay and it was wrecking their conversion rate.