JWT testing gets tedious fast.
Decode → edit → re-sign → repeat.
Hakluke’s ( @hakluke ) toolkit makes it much faster.
Paste a token and you can quickly test:
- alg:none + case variants
- Algorithm confusion
- kid injection
- Weak JWT secrets
- Claim injection
- Tampered tokens without re-signing
The last one is my favorite.
Disable auto re-sign → modify the token → send it.
If the server accepts the tampered JWT without verifying the signature, you’ve got a finding.
https://t.co/yRB7x5qr3T
Bug Bounty Methodology with OpenCode CLI
1/10
Turn your terminal into an AI-powered bug bounty machine.
Recon → Hunt → Validate → Report — all inside OpenCode.
No more context-switching. Just pure hunting flow.
#BugBounty#OpenCode#CyberSecurity#WebAppSec
Recently came across a pretty interesting XSS payload that managed to slip past some generic WAF rules and basic mitigations.
Could be useful in situations where you already have HTML injection on the target and traditional payloads keep getting blocked.
Payload: <svg><animate onbegin="alert(1)" attributeName=x></svg>
If you want to learn more on cyber security, bug bounty and penetration testing then feel free to check out my youtube channel where i have uploaded 180+ videos on various topics like xss, sql injections, unique/underrated vulns, chaining bugs together etc...all practical!
Link: https://t.co/gavWFZXUqx
🔥 Great read on breaking 2FA the real way (logic flaws, not brute force myths)
Covers practical bypass techniques like:
• Flow manipulation
• OTP leakage
• Weak rate limiting
• Session handling issues
If you're into bug bounty / web security, this is gold 👇
🔗https://t.co/J9eQjFLfVz
#BugBounty #WebSecurity #AppSec #CyberSecurity #Infosec
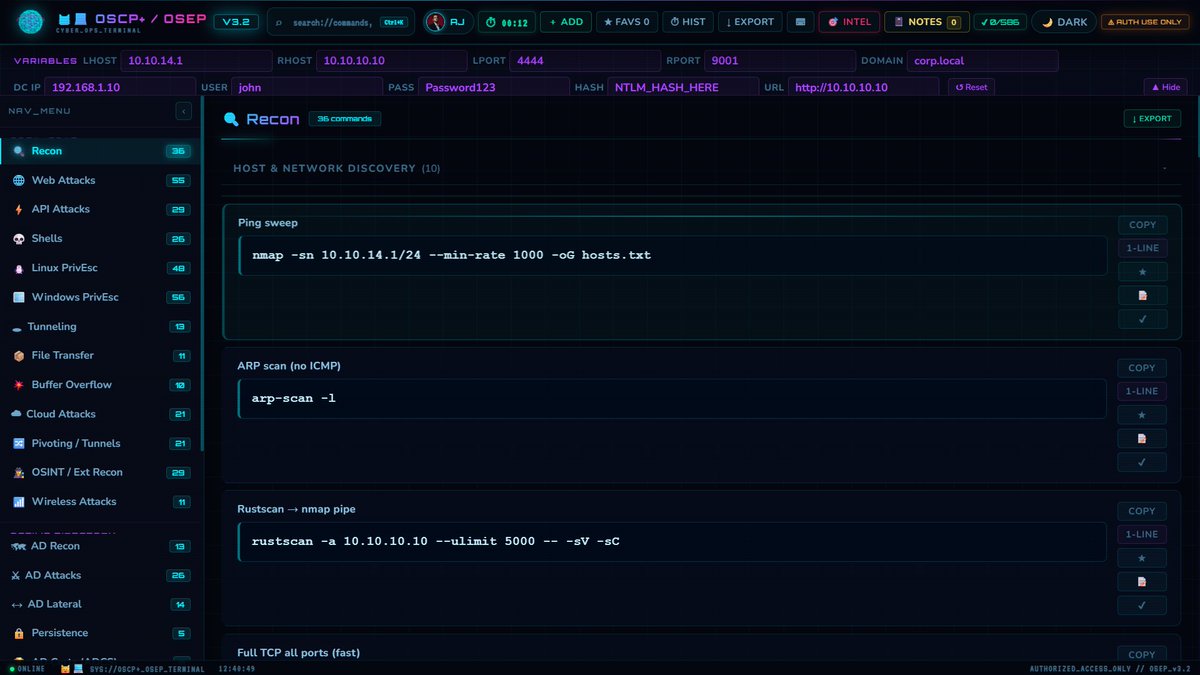
Just came across this insanely clean browser-based pentest cheatsheet 👀
Source: https://t.co/YNOvOjulMW
580+ pentesting commands organized for recon, privesc, AD, web testing, pivoting & more, all inside a fast terminal-style UI.
No setup. No clutter. Just practical workflows ⚡
Perfect for OSCP/OSEP prep, labs, CTFs, and real-world engagements.
#cybersecurity #bugbounty #pentesting #redteam #oscp
Bug Bounty Tip 🎯 - WordPress /wp-json/wp/v2/users/ Still Works in 2026
WordPress user enumeration via REST API is old. It still works everywhere.
curl https://t.co/G8IQSQ8Zwm
Got: name, slug (= login username), user ID, profile URL
Then the chain: Username known → /wp-login.php?action=lostpassword → host header injection in reset email → ATO
Add it to your checklist. It takes 2 seconds and the slug is usually the WP login.
#bugbountytips #cybersecurity #wordpress #recon
PHP Null Byte on Parameter Trick
Use to fool WAFs that decode before parsing.
It might consider the anchor with dangling (but harmless) markup instead of the real vector.
param%00p%3D<A/Href="<Svg/OnLoad=alert(1)//
More on https://t.co/7OQf9q3gJ3
PoC https://t.co/FXIFrgjemu
🧠 AI-Powered Red Team — 28 Specialized Agents for Offensive Security 🤖🔥
Turn Claude into a full pentesting team.
• 28 agents (Recon, AD, Web, Cloud, Mobile)
• Auto task routing → correct agent
• Real tools support (nmap, sqlmap, nuclei, BloodHound)
• Recon → Exploit → Report
Link: https://t.co/O7OBGldz9q
#AI #RedTeam #Pentesting #CyberSecurity #Infosec
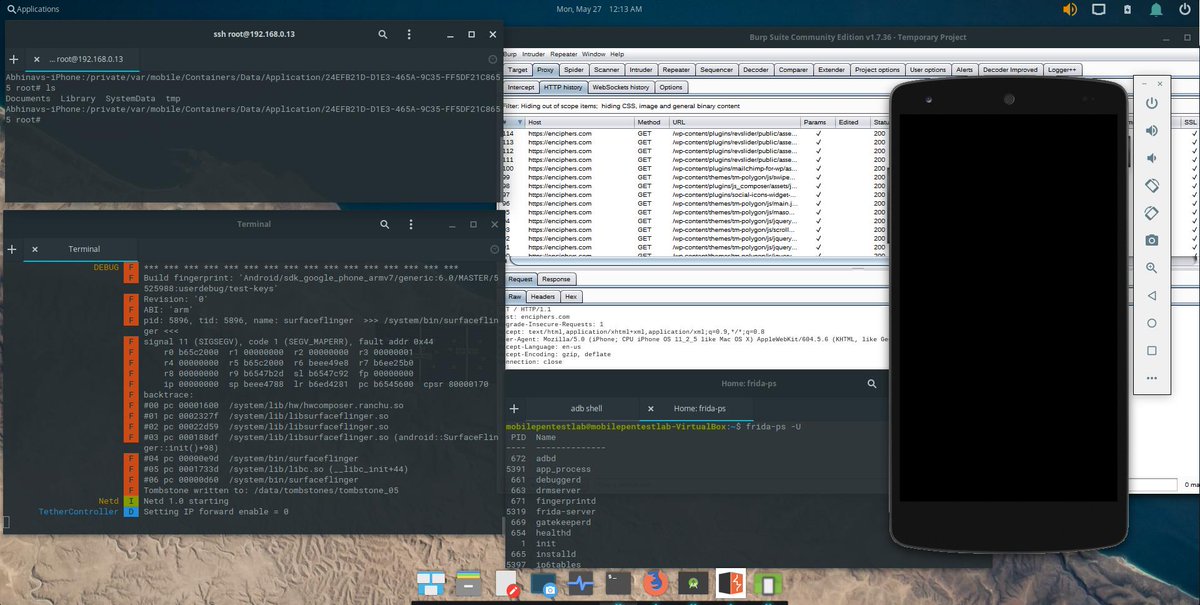
iOS Pentesting Series
Learn how to work with useful tools and apps such as Frida, Objection, 3uTools, Cydia, Burp, fsmon, fridump, SSL bypass, reFlutter etc.
Part 1: https://t.co/nSPl5yZa18
Part 2: https://t.co/t6UFBy1wm9
Part 3: https://t.co/zud0PguDCS via @KishorSec
👉Practice and get certified in Mobile application pentesting
🌟Frida Labs by DERE-ad200 Thank you Joas A Santos for this gem!
https://t.co/QYgdOkXC2s
🌟Damn Vulnerable iOS App
https://t.co/0ssOhrDsvl
🌟Oversecured Vulnerable IOS App by oversecured
https://t.co/wlVKCkebzW
WHAT THE HACK HAPPENS IN THIS YEAR!
cPanel & WHM - Auth bypass (CVE-2026-41940)
here is the exploit POC: https://t.co/uLFJ5XqTc0
Join my bugbounty telegram chennal: https://t.co/J6uPf8H57o
#bugbounty#cpanel#cve