We analyzed the 100 largest digital asset security incidents from 2014 to H1 2026. 🔐
The attack surface moved. 96% of H1 2026 losses now come from compromised keys, signing workflows, and vendor infrastructure.
🔗 Get your copy: https://t.co/g9LB6pguEi
The custody trilemma: agility, cost of the solution, security. ⚖️
Where you land depends on the asset class you want to custody. Fast start? A regulated custodian.
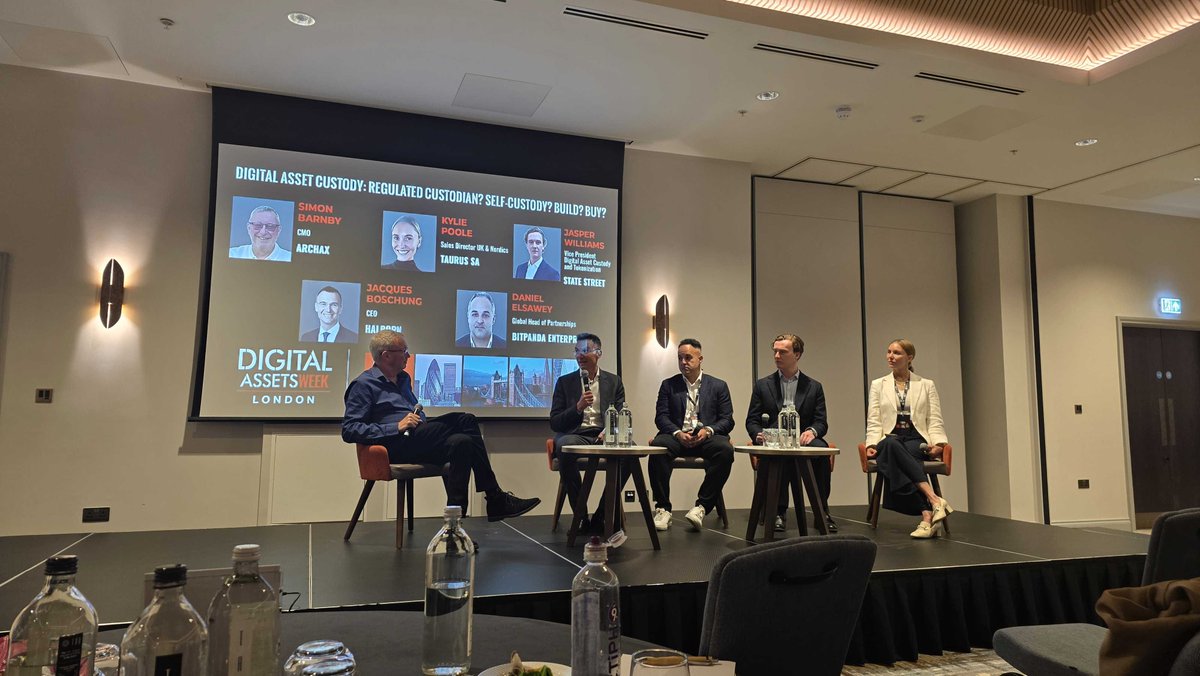
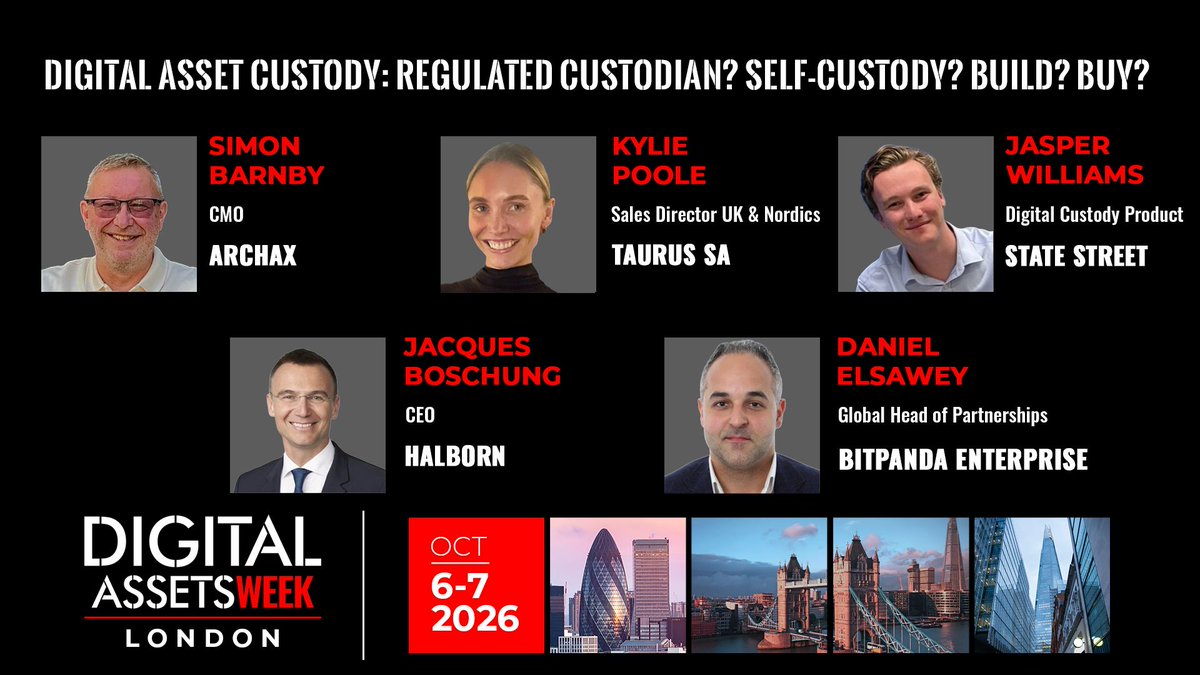
Our CEO Jacques Boschung, Digital Assets Week London.
Hybrid incidents are now a recurring pattern in digital asset hacks. 🔓
One infrastructure or social step. One technical exploitation step.
🔗 Learn more in our report: https://t.co/VJvOBbfHXS
HSMs, multisig wallets, and MPC each move the attack surface somewhere different and trade availability against isolation differently. 🔏
We evaluate them on security, availability, and operational complexity.
📰 Read: https://t.co/Oyumqm4zq6
An estimated $93M was stolen from accounts protected by a Ledger hardware wallet. 🔒
The hack is linked to an implant in hardware from a reseller. It monitored the screen during setup and captured the recovery phrase.
🔗 Learn more: https://t.co/dM6zbnPWke
Recovery rate in the top 100 digital asset hacks: 40% in 2021, 11% in H1 2026. 💸
Forensics got better. Laundering got faster.
DPRK-linked losses recover at 9.0%.
🔗 Get the report: https://t.co/X47yXGEPyB
We're pleased to announce the formation of CMTA's new Product Committee, chaired by Gabi Urrutia, (SVP Security & Field CISO @HalbornSecurity), to drive international tokenization standards and cross-border interoperability.
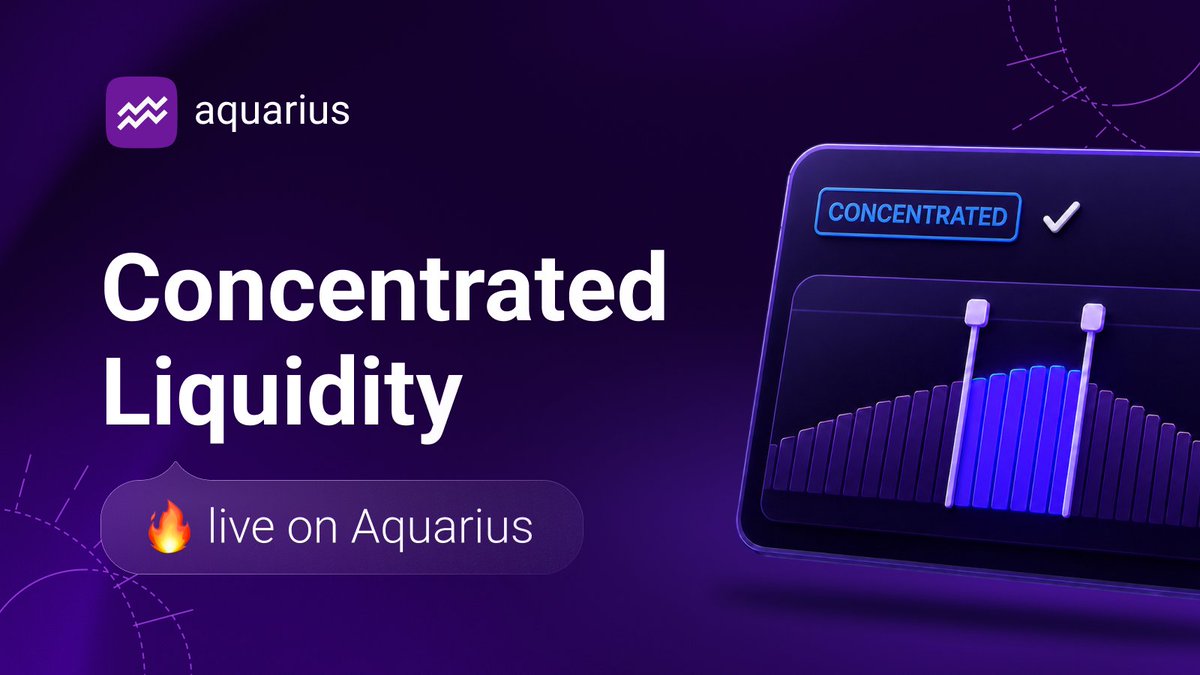
1/ @HalbornSecurity has finished the security audit of our concentrated liquidity pools. Every finding is closed.
The pools have been live and working for a while. Now an independent auditor has signed off on them too. ♒
RCM is moving closer to launch.
@HalbornSecurity has completed the smart contract audit of the RCM Protocol, covering the contracts supporting RCM Asset issuance and lifecycle functions.
The audit summary is available below ↓
Raising the signer count doesn't address where attackers actually operate. ❌
All 12 multisig breaches in our Top 100 Digital Asset Hacks report were defeated through the human or workflow layer. Not the cryptography.
📰 Full report: https://t.co/4GOmXNbzgU
$387.5M out of Bitget's hot and warm wallets on Sept 24. The biggest hack of the year so far. 🚨
On current evidence, no private key was stolen. Bitget's own signing service signed the transfers.
📰 Read @urruts' analysis: https://t.co/GQQtsj8jBd
Third-party custodian, self-custody, in-house build, or acquisition. Every route to institutional digital asset custody carries a different risk profile. ⚖️🔐
Today at Digital Assets Week London, our CEO Jacques Boschung discussed these trade-offs with fellow experts on a panel.
French fintech @finaryhq needed to run a custody key ceremony, with no internal experience and a regulatory need for independent attestation. 🔑
Halborn reviewed the runbook, identified two gaps, then attested the ceremony live.
🔗 Full case study: https://t.co/KW89E2H3yv
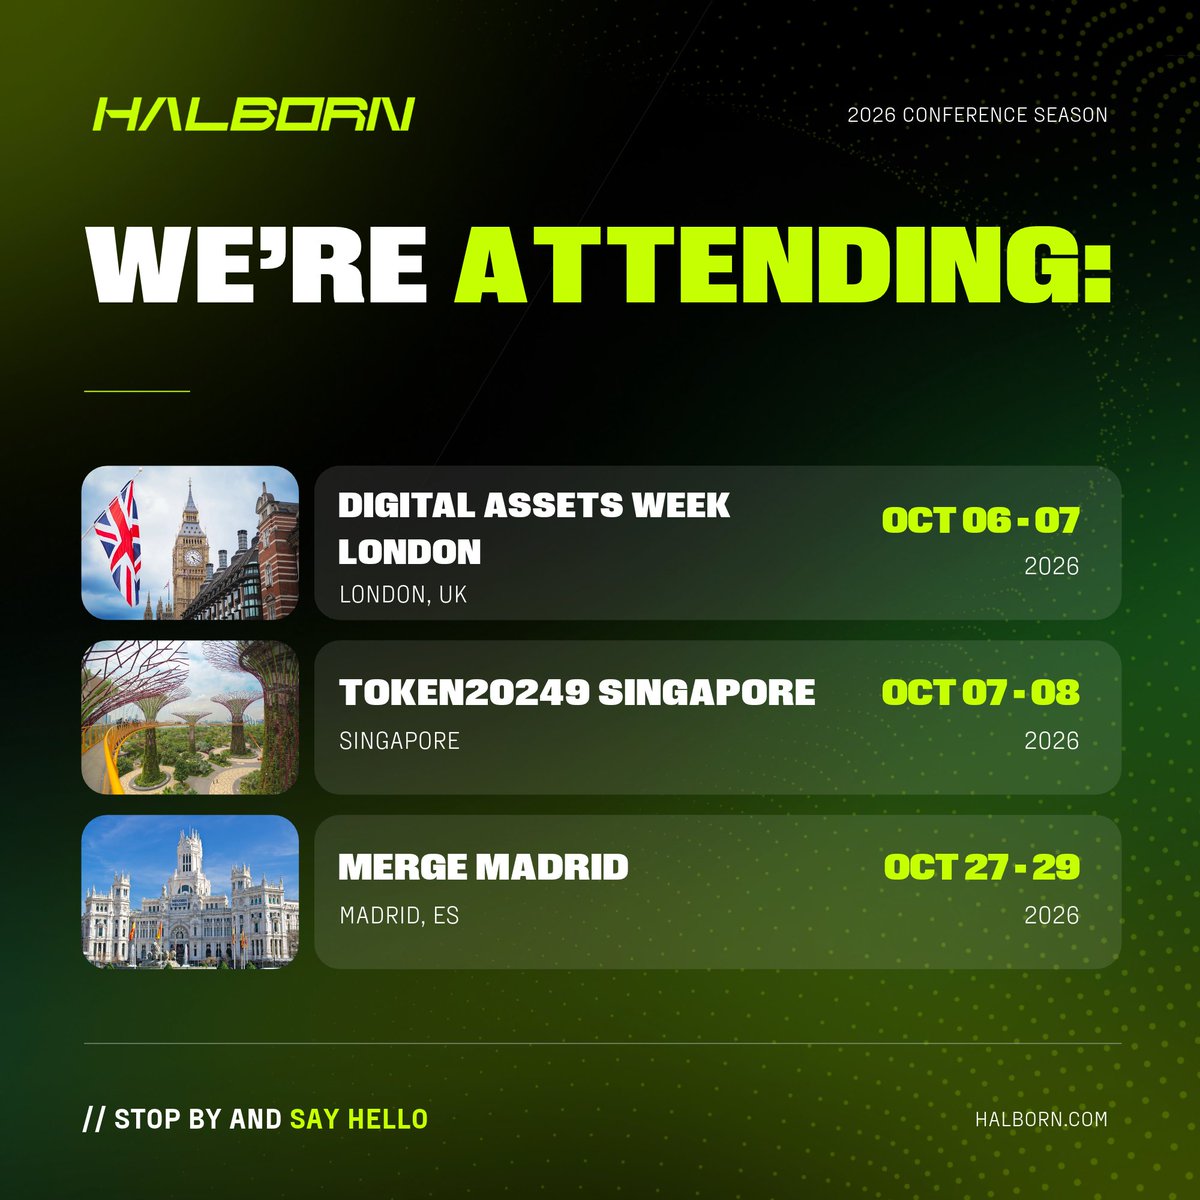
It is a major week on the digital asset conference calendar, and Halborn is on the ground at every stop. 📌
The biggest hacks have cost this industry $12B+ so far. Come find us and talk through the security measures that keep institutions off that list.
Custody decisions carry more than operational weight. They define an institution's compliance posture and risk exposure for years. ⚖️
Our CEO Jacques Boschung joins experts from @ArchaxEx, @taurus_hq, @Bitpanda, and @StateStreet at DAW London to break down each option.
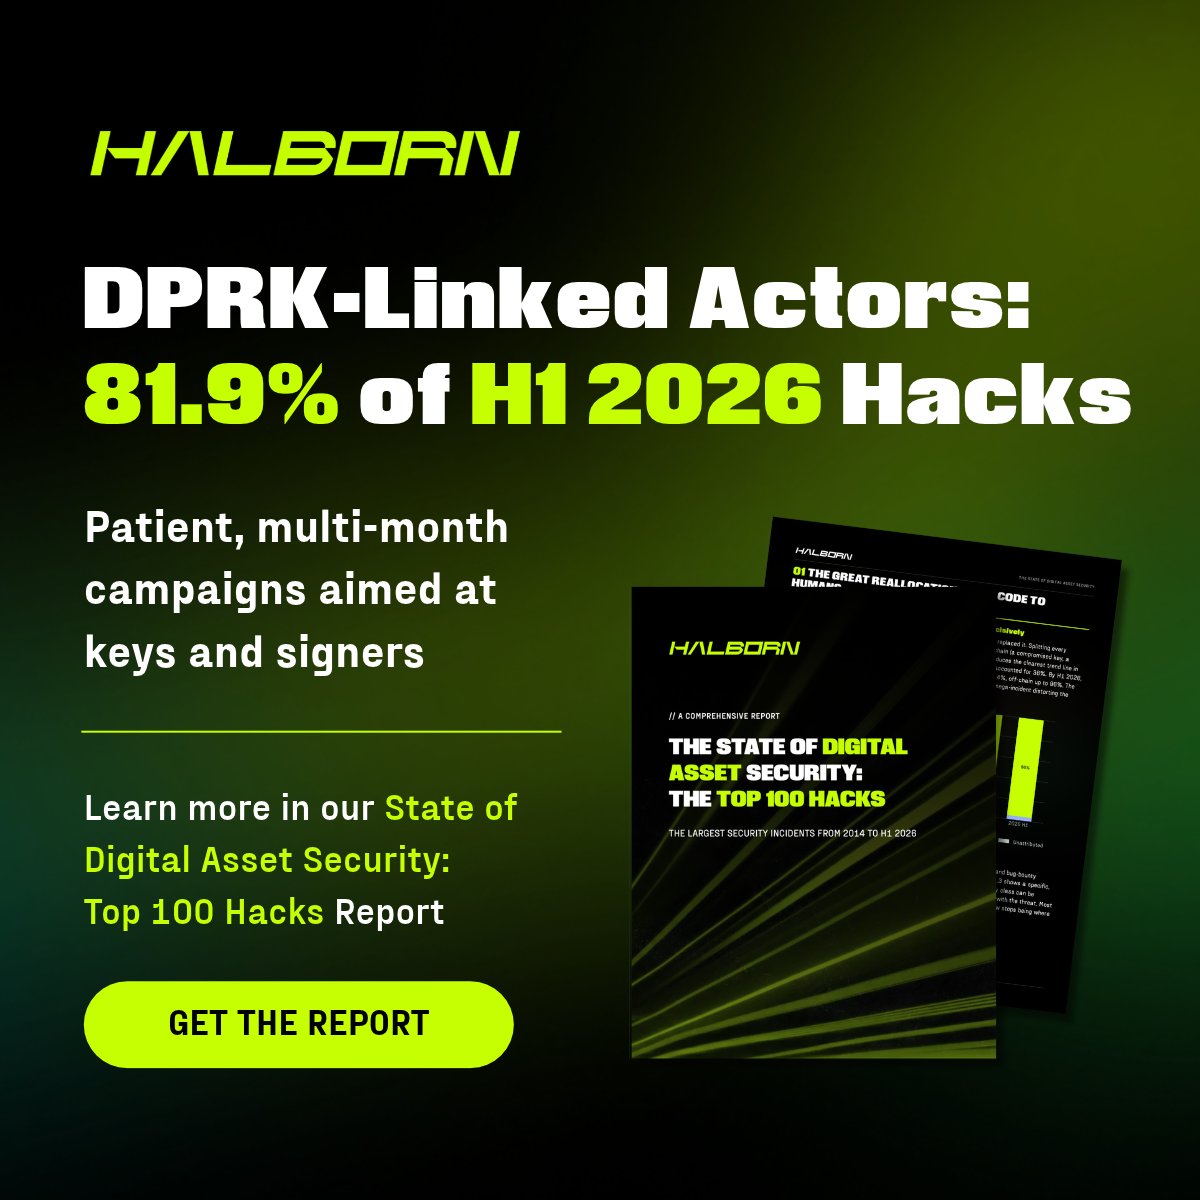
DPRK-linked incidents were 0% of annual crypto losses in 2021. By H1 2026, they hit 81.9%. 🚨
Fake recruiters, deepfake approval calls, compromised signing vendors. This is patient APT tradecraft, not smash-and-grab crime.
📰 More in our report: https://t.co/Uy9QbtEEps