BREAKING: Introducing our latest "HashDit Pro" Chrome Extension🎉🥳
The latest Extension will offer :
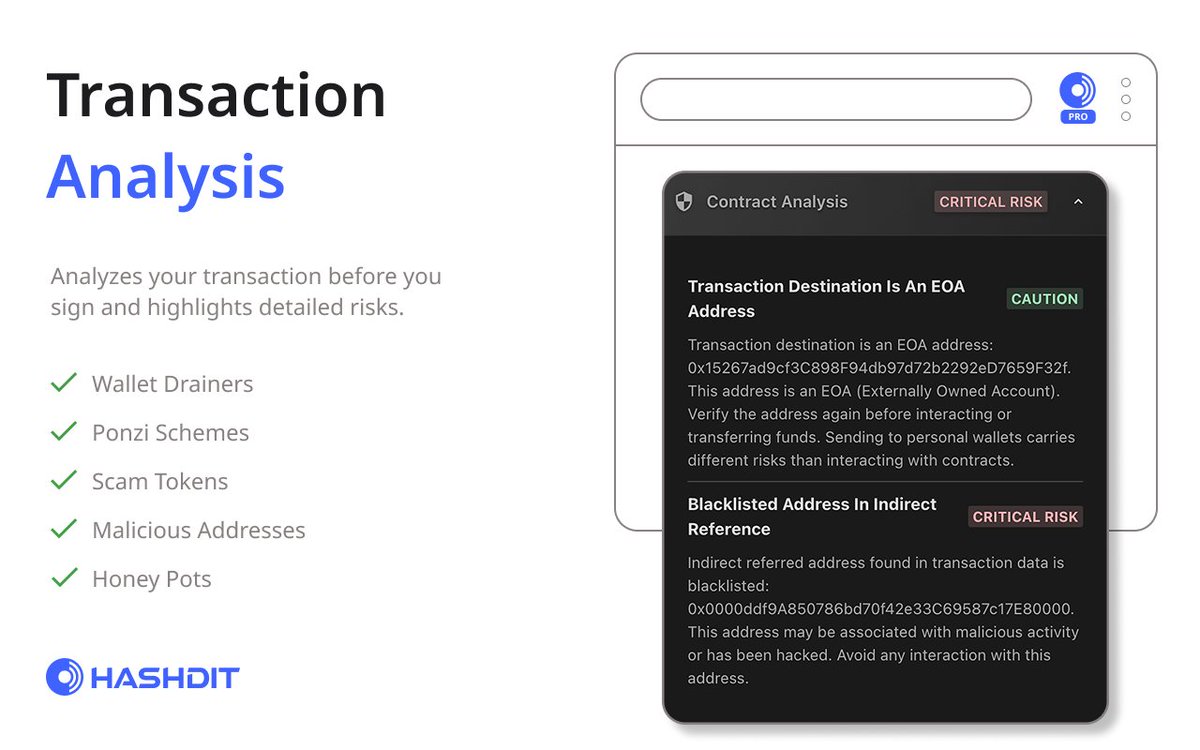
🔹 Powered up Threat Protection (stay SECURED against address poisoning / drainer + any other phishing attacks)
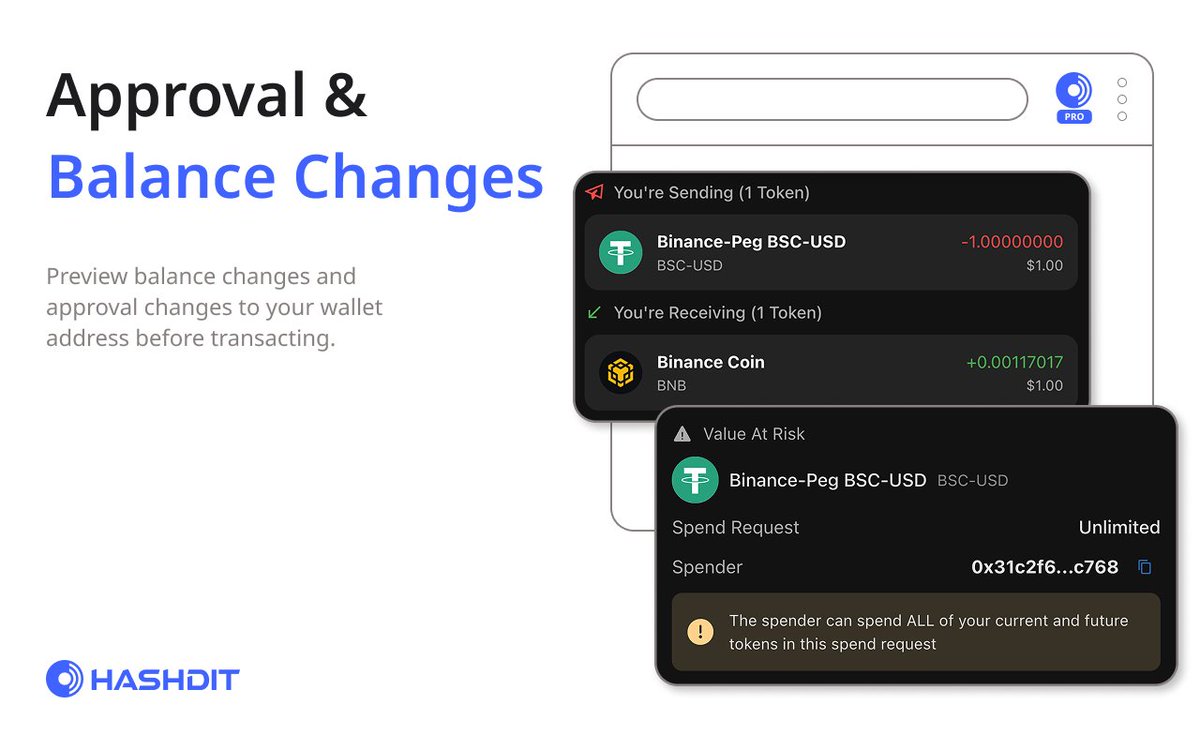
🔹 Smart Contract Simulation (preview balance changes and approval changes)
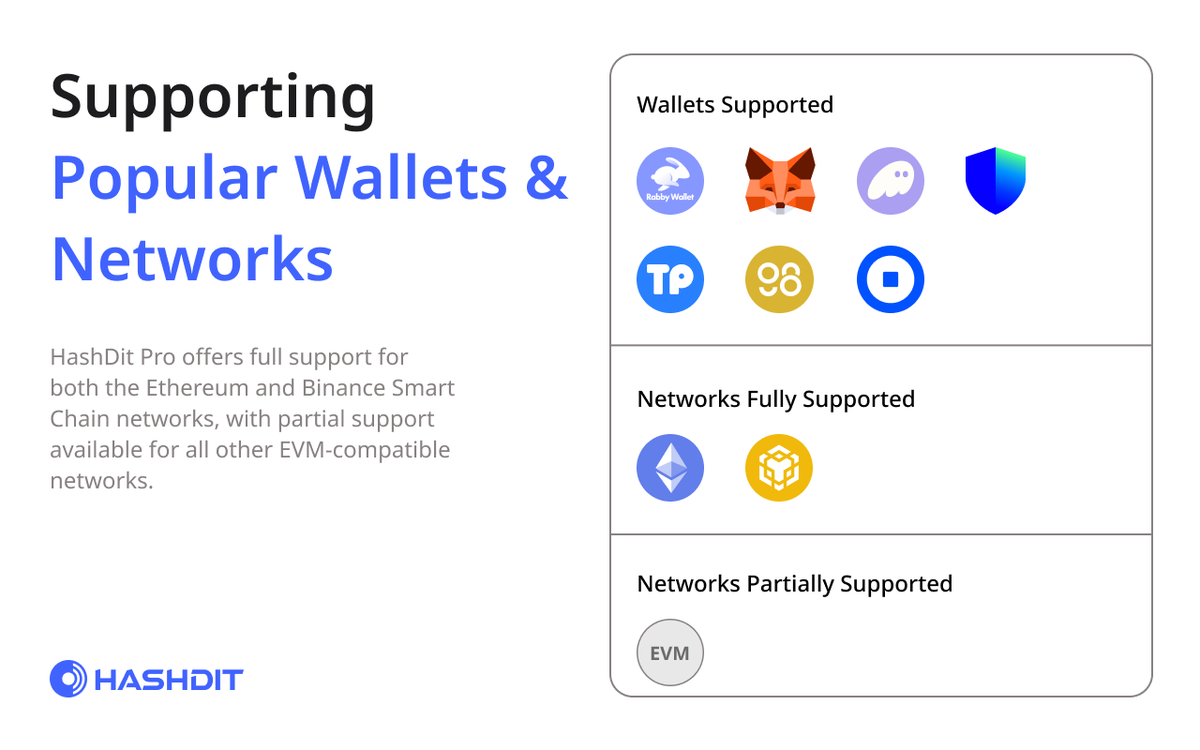
🔹 Supporting 7 popular wallets + all EVM chains
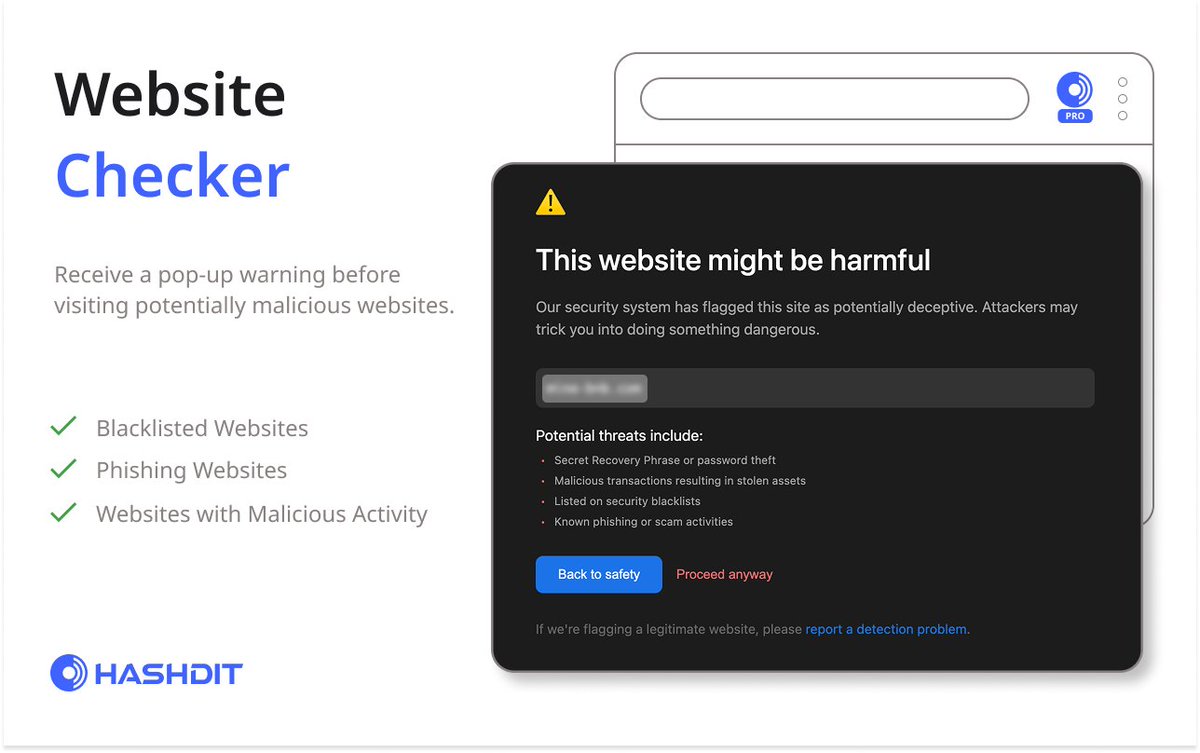
🔹 Website checker (Clear pop-up warning when visiting malicious websites)
🤔 What you should do if you are using the old Extension? Remove the old Extension and install our latest Extension for continuous improved protection!
Download here NOW for FREE: https://t.co/gaGayreOLI
Stay safe with HashDit Pro! 🛡️
🔐 Node.js security updates are now available!
New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues.
Review the details and update your systems to stay secure.
🔗 https://t.co/W4kfzx5lxz
#NodeJS#Security
🚨 HashDit Alert! 🚨
Fearless Wallet extension versions 3.0.1, 3.0.3, 3.0.4, and 3.0.5 contained malicious code that could exfiltrate private keys when users unlocked the wallet.
Confirmed on Chrome; Firefox users during the same period should also treat keys as compromised. So far, 8 users have reported unauthorized transactions totaling 17,286 DOT.
If affected, assume compromise and move funds to a new wallet immediately.
Stay safe!
Security Alert for Fearless Wallet
Fearless Wallet is a third-party application, built and maintained by an independent team.
Following an investigation by the Polkadot Technical Fellowship on behalf of the @PCF_org, it was found that the Fearless Wallet browser extension had been compromised and had been leaking users’ private keys since February 2025.
If you have used the Fearless Wallet browser extension, please create a new keypair with a different wallet and move your funds as soon as possible.
Remember to never share your private keys.
According to @spreekaway , @swellnetworkio has been breached and could potentially be linked to the Railway incident.
Stay safe!
https://t.co/nJaYReN3Sw
🚨 HashDit Alert! 🚨
@Railway detected unauthorized access to systems storing customer environment variables. An attacker may have obtained some encrypted env vars and their decrypted contents (API keys, DB credentials, private registry credentials, private keys, etc.).
Immediate actions recommended for all users (especially crypto teams):
1. Rotate/roll all environment variables and secrets stored in Railway right away.
2. For crypto: treat any private key that was in Railway as compromised! Migrate funds/roles to new keys rather than just rotating in place.
3. Rotate any related private registry credentials.
4. Review service logs for unusual activity.
This appears to be part of a broader series of attacks on platform companies (primarily aimed at compromising AI inference providers). Crypto projects are also heavily affected/at risk, especially any that stored private keys, wallet keys, or signer credentials in Railway env vars.
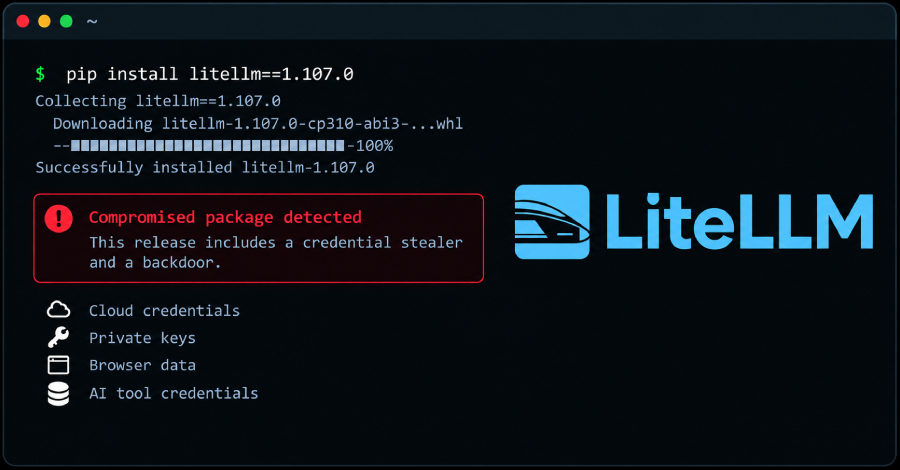
🚨 LiteLLM 1.107.0 compromised in a supply chain attack.
Malicious PyPI packages and Docker images delivered a credential stealer and backdoor.
⚠️ The malware runs at Python startup, targeting cloud credentials, private keys, and AI tool credentials.
🔗 Full story: https://t.co/ElNT6Wpe8p
‼️ BREAKING - PHP releases emergency patches for two critical #PHP2Shell RCE flaws (CVSS 9.2) as early exploit attempts emerge.
The flaws can enable unauthenticated code execution and expose server memory.
👉 PATCH NOW (CVE-2026-109618, CVE-2026-109619)
Details ➜ https://t.co/jJT7p6lala
🚨 HashDit Alert! 🚨
We have monitored that $NEM 0x9Cf0E3aD4efa7ab602D7b5a38c55795CFA777777 has been compromised and drained for roughly $725k worth of funds on $BSC.
This is a typical Price Manipulation attack. The attacker first flashloaned USDT and swapped for NEM.
Next, he aimed to manipulate the AMM pool price, the attacker was able to repeatedly follow this sequence 42 times
1) transfer NEM directly to the pool contract,
2) used skim() to pull the excess tokens back to the attack contract
3) call the exposed flushLpSellRecycle method to burn some NEM from the pool
4) call the sync() method
After sufficiently distorting the pool state, the attacker swapped back through the pool at the manipulated price and realized a profit.
The issue lies in the flushLpSellRecycle() method, which burns tokens directly from the LP pair based on balanceOf[pair], which is attacker-influenceable.
Calling sync() afterward updates reserves to the manipulated balance, enabling pool price distortion and profit extraction.
Funds have been bridged to ETH.
Detected by our Internal HashDit AI Triage Monitor.
Stay safe!
⚠️ DApps with OFTs on @GravityChain, @campnetworkxyz, @GOATNetwork, @MetisL2 or if you deposited into Stargate pool positions on these 4 chains take note!
Stargate support ends Oct 23 (in 3 days); LayerZero Labs’ DVN/Executor services end Oct 30 (in 10 days).
Your OFT isn’t automatically deprecated, but affected routes need alternative infrastructure. Check configs and coordinate migration with chain teams.
Reminder: For a number of chains with minimal activity, LayerZero is winding down offchain support. This means that LayerZero DVN and Executor services will no longer be available for these chains.
We will be deprecating support for the following chains via Stargate v2, effective October 23rd, 2026:
Gravity, Camp, GOAT, Metis
Stargate Pool liquidity providers and ETH liquidity providers should withdraw their funds from the respective pools to redeem their assets before the effective deprecation date.
Stargate hydra (USDC.e, USDT) holders should bridge their funds to Stargate Pools to redeem their assets before the effective deprecation date.
For the full list of impacted chains and effective dates, read here: https://t.co/AhVenA9Zr7
🚨 HashDit Alert! 🚨
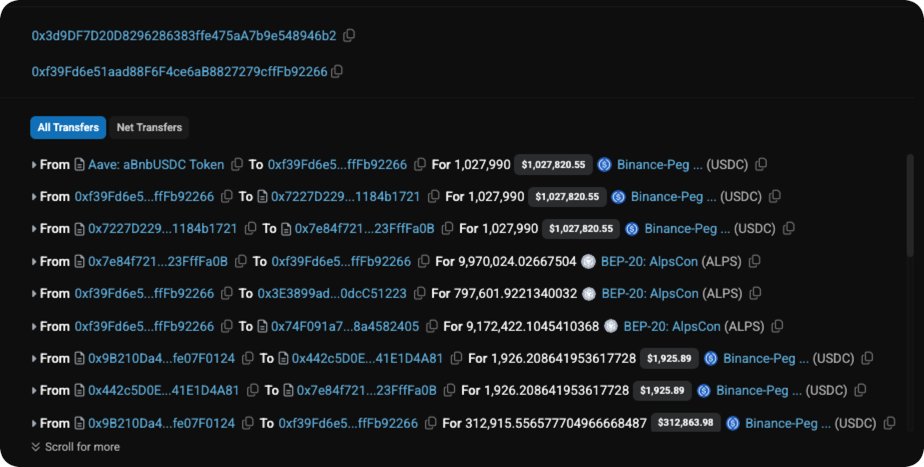
Over the weekend, HashDit have monitored 3 notable hacks on #BSC, involving #TIP, #SIEVE, #ALPS, resulting in approximate losses of $69k, $11k, $152k respectively.
We have blacklisted the hackers on our system.
Detected by our Internal HashDit AI Triage Monitor.
Feel free to reach out if your project needs early warning detection! 🛡️ Stay safe!
🚨 HashDit Alert! 🚨
We have monitored that @cysic_xyz has been compromised and drained for roughly $1.1m worth of funds.
🔍 According to preliminary root cause, the attacker gained unauthorized access to a database supporting its bridge services and exploited a processing-logic vulnerability to submit a fraudulent mint message.
⛓️ Our on-chain shows that its deposit nonce (1792239993405, a millisecond timestamp) falls outside the normal sequential range (20978–20980). This indicates a forged record that the signers accepted without verifying it on the Cysic chain.
Malicious bridge: https://t.co/kMmNp7f5uh
Most of the funds are held here at the moment https://t.co/03o80AI0oA , while 2.8m base:0x19e8d59ff3d7a31289e0dc04db48d43b02c7ffa6 are still held in the hacker wallet. We have blacklisted the wallets and are monitoring closely.
Stay safe!
On Oct 17, a security incident involving the unauthorized minting of 10M CYS occurred through the Cysic bridge.
Our team responded swiftly. User wallets and mainnet operations remain unaffected.
The bridge remains suspended pending security review.
Full update below. 👇
🚨 HashDit Alert! 🚨
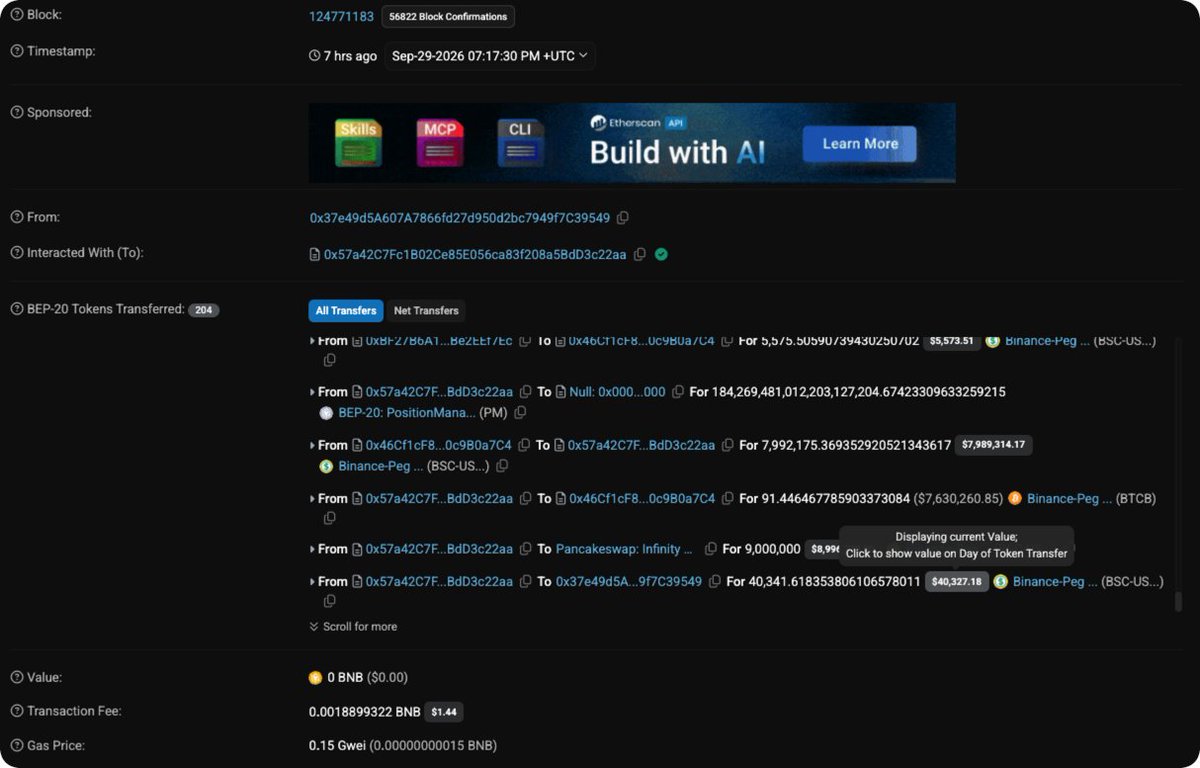
We have monitored that PositionManager has been compromised and drained for roughly $40k worth of funds.
The issue lies in the deposit() function. Internally, newly minted shares are calculated by valuing the vault’s existing pooled assets using a manipulable AMM spot price, while the incoming deposit is valued using a trusted Chainlink oracle price. As a result, withdraw() returns an incorrectly priced amount.
By manipulating the AMM pool price, the attacker was able to repeatedly call deposit() and withdraw() in a loop 24 times, compounding a small profit on each cycle. The attacker ultimately forwarded the remaining profit of approximately 40,341.62 USDT to the sender’s EOA.
Funds have been deposited into Tornado Cash.
Detected by our Internal HashDit AI Triage Monitor.
Stay safe!
🚨 HashDit Alert! 🚨
As if Mid-Autumn Festival wasn’t eventful enough, following Bitget, payy_link, and Duelbits, another exploit has surfaced...
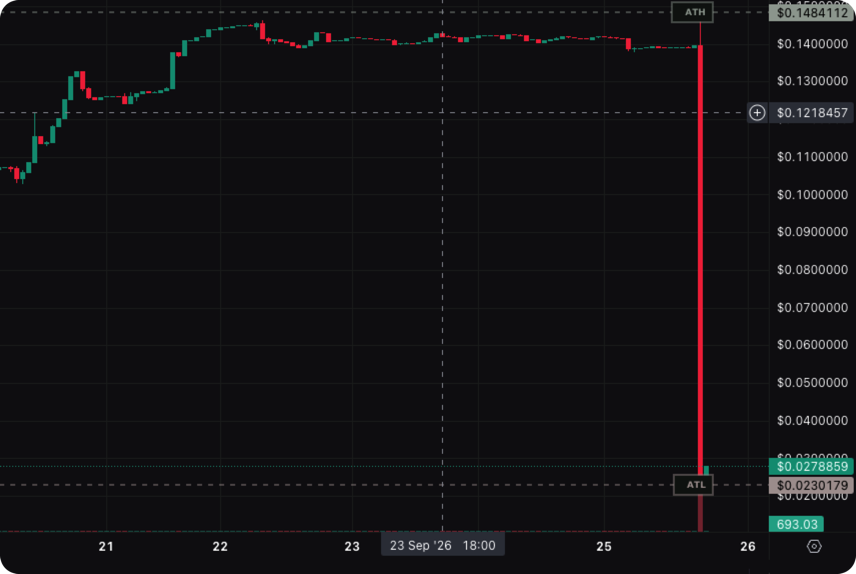
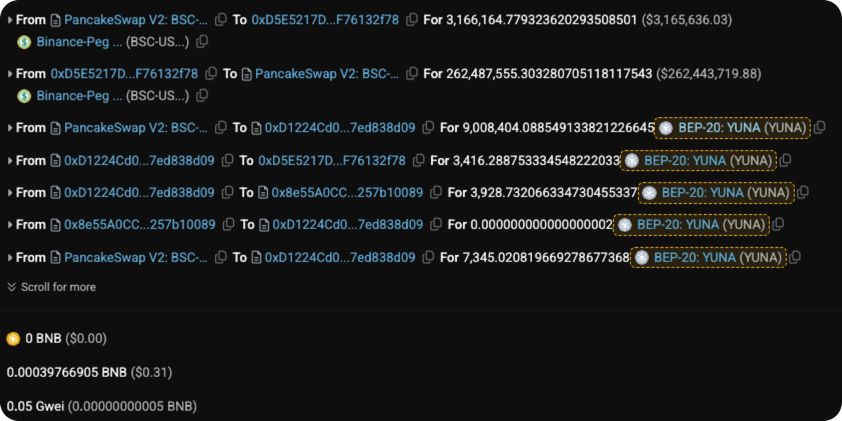
We detected an exploit involving $YUNA on #BNBChain, resulting in an estimated $1.2M drain.
The issue stemmed from the Pool contract’s claim() function, where staking rewards were priced using the YUNA/USDT pool. By manipulating the pool price, the attacker was able to claim significantly more YUNA than intended, then unwind the position for a large USDT profit.
The stolen funds have since been bridged to Ethereum and remain in the attacker’s wallet.
Detected by our Internal HashDit AI Triage Monitor.
Stay safe!
🚨 HashDit Alert! 🚨
@bitget has been reported to be hacked for ~$351.6M!
Withdrawals are temporarily paused and the platform has stated that users will be covered by their User Protection Fund.
HashDit is following the incident closely.
Stay Safe!
[SECURITY NOTICE] Bitget Hot Wallet Incident — September 24, 2026
At 18:31 UTC on September 24, 2026, Bitget's security systems detected unauthorized transfers from some of our hot wallets. Our security team activated emergency response protocols immediately.
What we have confirmed:
-Estimated funds affected: approximately $351.6 million
-Cold wallets remain fully secure. Bitget operates a three-tier wallet architecture — the breach contained only a portion of the hot wallet and warm wallet layers.
-User funds are safe. The full amount of this loss falls within the coverage of Bitget's User Protection Fund, which currently holds over $464 million
Actions we have taken:
-Emergency response team activated within minutes of detection
-Abnormal transfer addresses identified, flagged, and reported
-Withdrawals temporarily suspended as a precautionary measure, pending security review
-Law enforcement and on-chain security firms have been formally notified and are engaged
What this means for you:
-Your account balances are accurate and your assets are protected
-Deposits and trading remain fully operational
Withdrawals are temporarily paused and will be restored as soon as the security review is complete
-What comes next: We will provide updates on an hourly basis across this channel and all official platforms. A full incident report — including root cause analysis and corrective actions — will be published within 24 hours. We will not speculate on the attack vector until the investigation is complete.
Bitget has navigated multiple market cycles. We will not run from this. Every dollar and every decision will be accounted for, transparently and in full.
Updates will be posted here and across all official Bitget channels as they become available.
— Gracy Chen, CEO, Bitget
🚨 HashDit Alert! 🚨
Trezor's third-party e-mail provider has been compromised!
Please be extra wary for any phishing emails even coming from the official trezor[.]io domain.
Stay Safe!
Our third-party e-mail provider has been breached. Please be aware that the email named ‘Critical Security Alert: STM32 Entropy Vulnerability’ is not coming from us, and it’s a phishing attempt. Do not click on any link.
We have taken down the domain, and we are investigating the situation, including how the hackers got access to our legit domain.
Builders on @BNBCHAIN can now book HashDit's security services through the AvengerDAO marketplace.
HashDit provides Security APIs, Web2/Web3 audits, monitoring, and incident handling to help teams catch vulnerabilities before launch, scan risky addresses/tokens/websites in real time, and respond faster when threats appear.
Find us on the AvengerDAO marketplace 👇
https://t.co/UGOACLHpi4
Defimon detected a malicious governance proposal that attempts to drain @autonolas Treasury - $100K at risk
Tornado-funded attacker registered ENS name "autonolas-deployer.eth" and submitted a proposal titled "Owner migration: transfer treasury ownership from old timelock to Safe updater".
In fact proposal execution would move Treasury ownership away from the legit Autonolas Timelock to the attacker contract, who could then rebalance and withdraw all 40.196 ETH.
There is 3 days to defeat the proposal. We have shared the alert in the community chat of the @autonolas project.
TX: https://t.co/kkZBV6TRDG
Attacker: https://t.co/B6poDkMXGz
Victim: https://t.co/h4XVftxmjD
An ongoing security incident has impacted users of the Cosmos EVM module. Cosmos Labs’ security and engineering teams have been proactively responding to this incident. We have advised the Cosmos EVM chains that are in contact with us to request that validators halt their chains.
We thank the teams using Cosmos EVM for their rapid response. An incident report will be shared once the situation is resolved.
If you are a team using Cosmos EVM and have questions, please contact [email protected].