Hekatomb connects to LDAP directory to retrieve all computers and users informations.
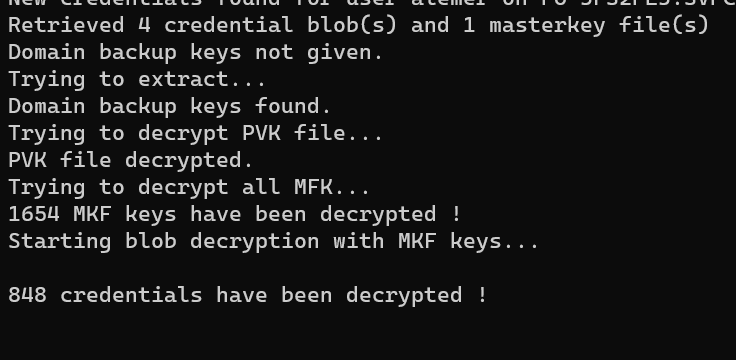
Then it will download all DPAPI blob of all users from all computers and uses Domain backup keys to decrypt them.
Because Domain Admin rights are not enough.
Hack them all.
Thanks to @kalu_69 HEKATOMB is now available in version 1.4 !! 😱🤯
SMB multi-threading is now supported to speed up the MKF and blobs collect and a progress bar is displayed
https://t.co/OKYr9GuqPP
J'ai eu la chance de présenter l'outil @HekatombProject dans le podcast de @nolimitsecu 😊
C'est à retrouver ici :
https://t.co/F7OlHqMrU9
Un complément d'infos est également dispo dans cet article : https://t.co/RvqtffbVzT
Avec @Herve_Schauer, @newsoft et @julloa
Thanks to @kalu_69 HEKATOMB is now gathering credentials faster by comparing users folders instead of trying to get into each user folder 😉
Version 1.3.1 is available on Pypi !!
J'ai fais un petit article sur le fonctionnement technique de l'API de chiffrement de #Microsoft (aka #DPAPI) suite à la publication de Hekatomb :
https://t.co/Agj5Yf3sgq
ça permet de bien comprendre le fonctionnement du système 🙂
HEKATOMB is now in version 1.2.2 thanks to @kevin_racca !! 💀
Impacket has been replaced by ldap3 for Active Directory requests, SMB connection can be forced to downgrade to SMBv2 and a random hostname is used to keep quiet on the network 🥷
You can try it with Pip right now 😁
@swuitch@Sh0ckFR Ok, si if it’s so easy, what about your GitHub contributions ? Why nobody did it before ?
And if you don’t like the tool, why not just ignore it instead of criticize ?
@Sh0ckFR@swuitch Mmm what about just not following me then ? 😅
It’s really easy to criticize, but not so easy to create and share tools like this one.
This account just stands for promote new features, nothing more.