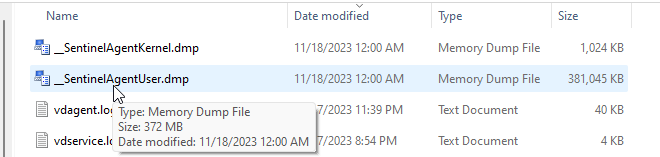
Ever find yourself on an endpoint with SentinelOne and have Local Admin? Just ask SentinelAgent.exe nicely, and it will dump a process for you, including itself!
https://t.co/WU6ZDPR91H
It bombs out on LSASS, but most other processes work.
Get the IP address of the user during #Telegram call to obtain geolocation of ISP
It might have some bugs since on Android, it returns only local, not external IP
https://t.co/hfiK1Lz6Mh
Web Check - All-in-one website OSINT tool for analysing any website
Uncover potential attack vectors, analyse server architecture, view security configurations, and learn what technologies a site is using.
https://t.co/cbOQBh3DFV
#cybersecurity#infosec#OSINT
GitHub - Narasimha1997/fake-sms: A simple command line tool using which you can skip phone number based SMS verification by using a temporary phone number that acts like a proxy. https://t.co/ssSQq10L0l
S3N4T0R-0X0 The warehouse has been deleted and I have made a backup.
AM0N-Eye is the most advanced Red Team & Adversary Simulation Software in the current C2 Market.
https://t.co/6gDhlXZ9Fy
@Korben À chaque fois qu'il y a une bonne idée, c'est géré avec les pieds 😅 Pour le côté sécurité on repassera : validé physiquement à la poste auprès d'une personne qui a à peine regardé ma CNI et qui je suis sûr ne sait pas faire la différence entre une originale et un faux 🙃
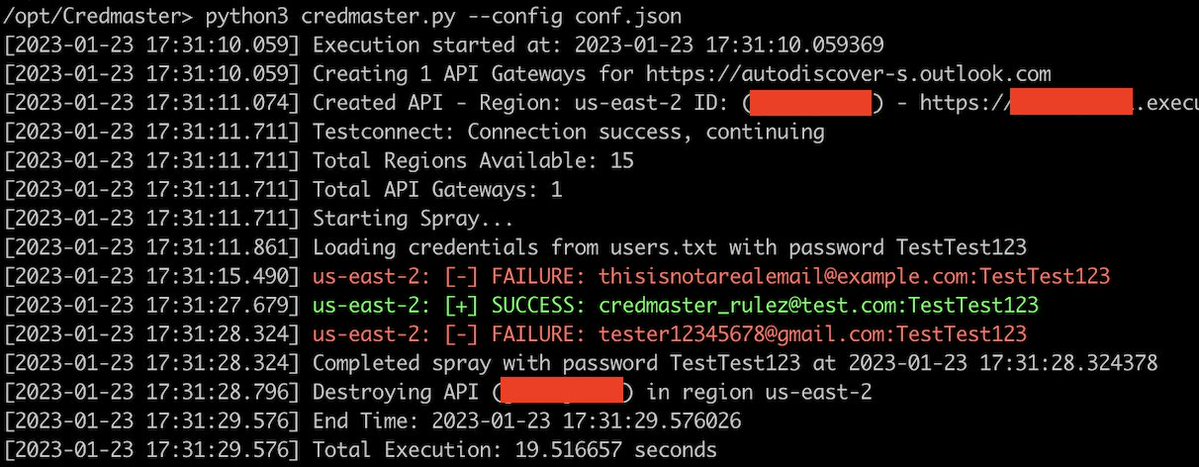
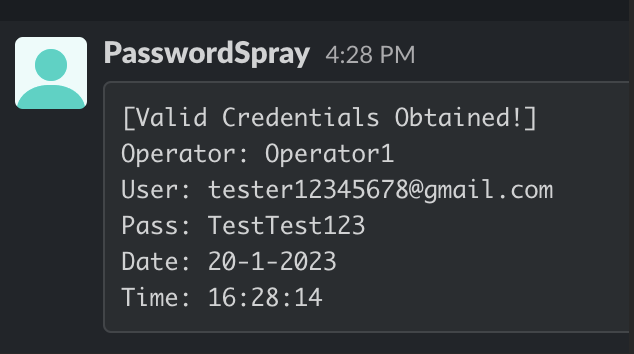
CredMaster 2.0 passspray tool release! New features like notification alerts, advanced SOC evasion techniques, 8 new plugins and an easy config file. S/O to @ZephrFish for all his contributions in the rewrite
B: https://t.co/tnWU7cGtty
G: https://t.co/JJhk097xlS
If NetNTLMv1 is disabled but LDAP signing is not enforced on DC, and there is WebClient service enabled on the target, pwn is similar (~RBCD abuse). NTLM relay should be HTTP->LDAP instead of SMB->LDAP (WebClient does not set signature requirement on the client side).
PoC for arbitrary file delete/move in #Razer Macro module that is not fixed as their bug hunting team do not consider this a bug but an exploit 🙃.
https://t.co/XnKnmH1q7c
Today we're publishing new techniques for recovering NTLM hashes from encrypted credentials protected by Windows Defender Credential Guard.
These techniques also work on victims logged on before the server was compromised.
https://t.co/euNIyX2dwW
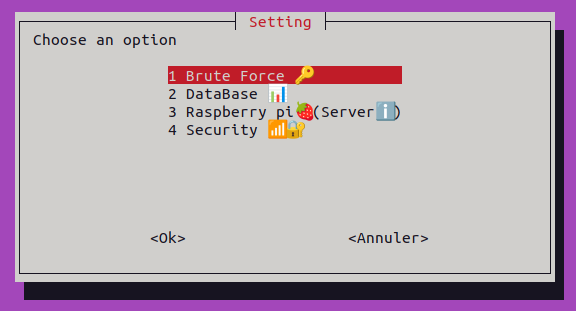
Brute force garage and hack-rf with Raspberry Pi by Lucstay11
https://t.co/egBTFgTHSG
Script with several tools to brute force garages, hack radio stations and capture and analyze radio signals
#SoftwareDefinedRadio#SDR#RaspBerry#rtlsdr#HackRF
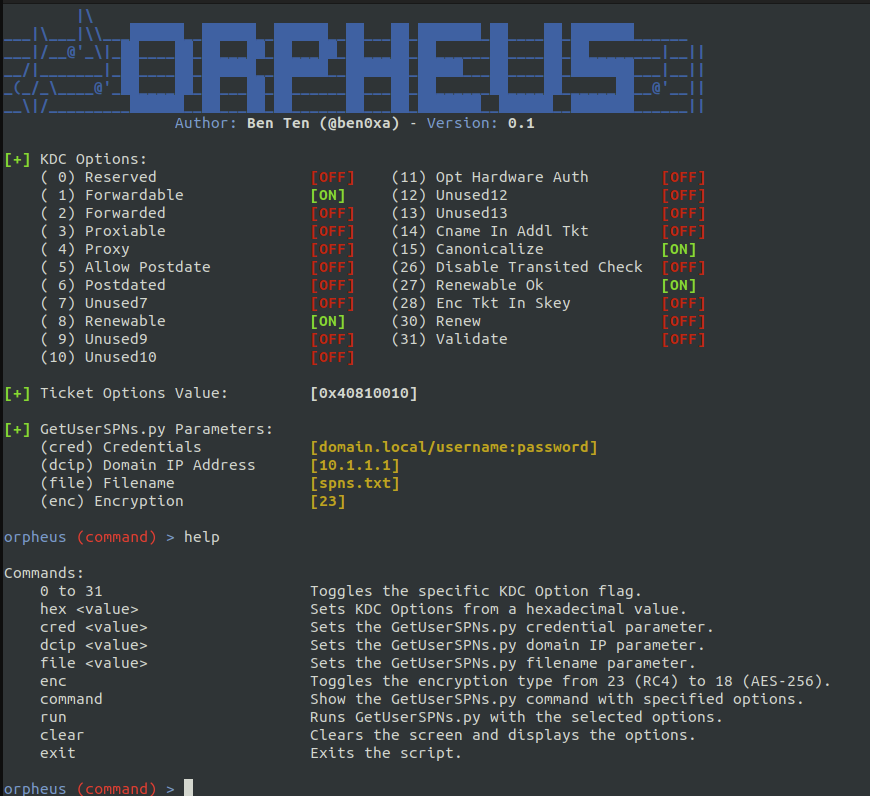
Releasing a new tool: Orpheus! Bypasses most Kerberoast Detections (including my own). Blog post and video is up at @TrustedSec! Even used @HackingDave's old alias in the demo. https://t.co/qhP8r28s4K #infosec#security#kerberoast
Welcome to the new AD Mindmap upgrade !
v2022_11 will be dark only (this is too painful to maintain two versions).
Thx again to : @Vikingfr and @Sant0rryu for their help 👍
Full quality and zoomable version here :
https://t.co/eIJE0apRzw
Overview :