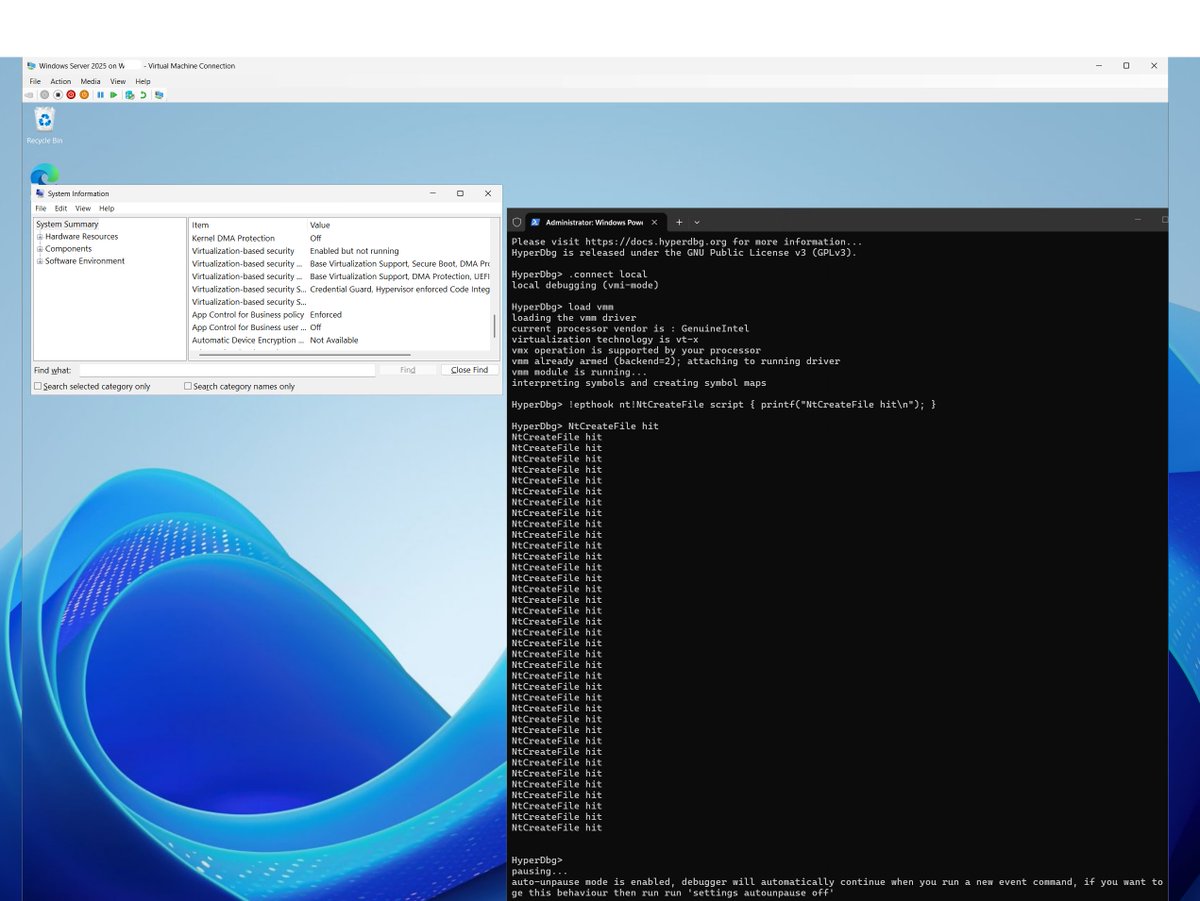
Debug beyond conventional limits.
Explore Hypervisor-Assisted Reverse Engineering workshop at https://t.co/g3vGGlphWi N L2026 and uncover low-level Windows behavior through hypervisor-level visibility.
Register now: https://t.co/nMDJ48wiII
#HardwearNL2026
HyperDbg v0.24 is released!
It includes nine new commands, support for arrays as function parameters, char and wide-char arrays, fix kernel-mode builds on Linux, plus major bug fixes and refactoring.
Check it out:
https://t.co/7tuHoZPQ0c
It's been a while since we passed 4K GitHub stars ⭐️
And more good news: HyperDbg's kernel-mode drivers now build on #Linux! 🐧
After successfully getting the user-mode components compiled, thanks to @MaxRaulea, we're now moving on to...
https://t.co/kDf9BtRYCw
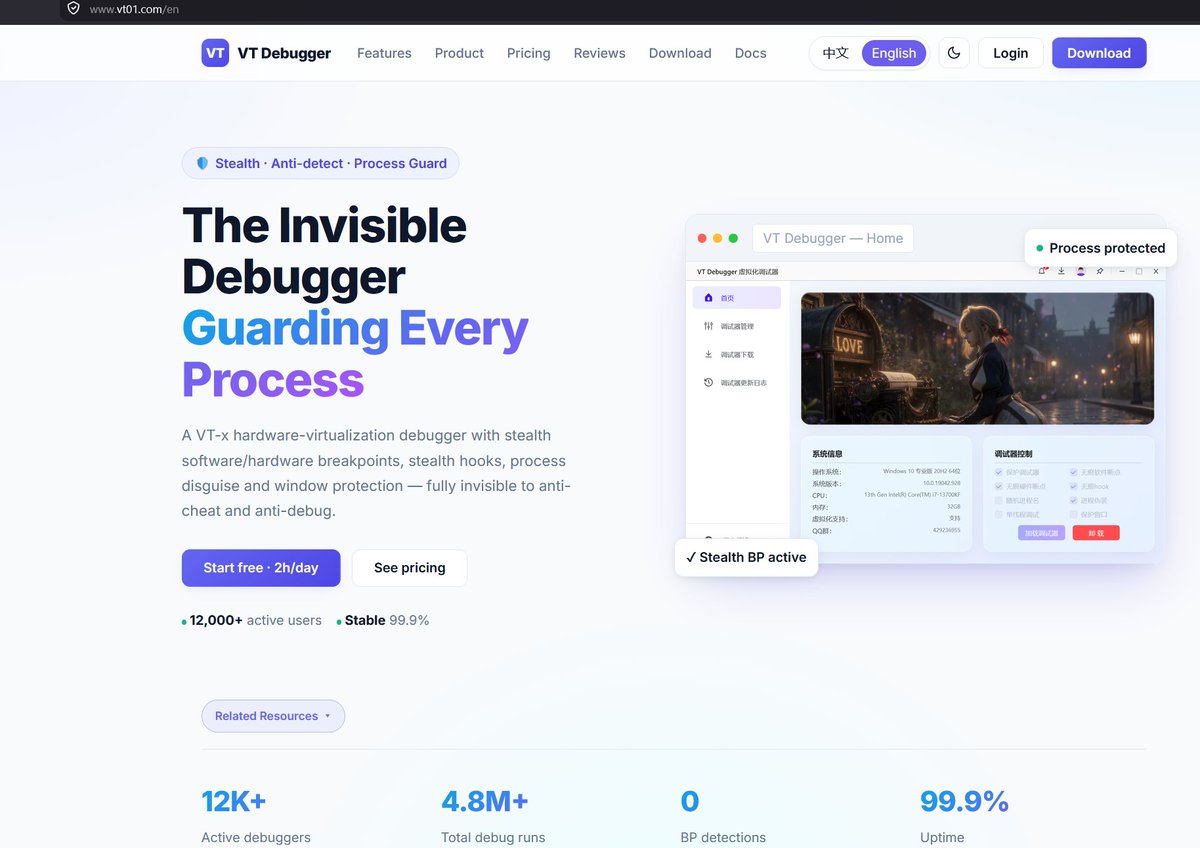
This one is really crazy. They're spreading malware disguised as a hypervisor debugger through a vibe-coded website, vt01[.]com. If you download it, it's malware. The sad part is that they're comparing it with @HyperDbg. 👀
> be me
> get dm
> its my friend @Intel80x86
> author of @HyperDbg
> wtf i love him
> open message
> "smelly i got goop"
> wtf i love goop
> "i found malware campaign"
> wtf i love malware campaigns
> "The Threat Actor(s) have created a website which is specifically tailored to malware analysts, or reverse engineers, who utilize hypervisor-based frameworks. Their malware campaign appears to have begun about 8 days ago. I became aware of the issue when their "product" compared themselves to HyperDbg. Their website is clearly vibe coded, however parts appear to be in Mandarin"
> wtf theyre targeting people who like goop
> sends url to website
> vt01[.]com
> look inside
> lol ai slop
> go to download page
> vt01[.]com/en/download
> immediately flagged as malware by firefox
> allow download plz
> split nanosecond touches the disk
> windows: OMFG MALWARE!!!
> ??? this malware STINKS
> sha256: 5934d1a64afd62e7d1badb81e8613e01efe9cf9c7d6748271c6d0761e3b11eb7
> look inside
> delphi, weird PE sections
> throw into triage
> YARA rules IMMEDIATELY identify the malware family
> XRed
> wtf is XRed?
> cant remember any family named XRed
> December, 2025: XRed impersonates Indian Ministry of Finance and Income Tax Department
> December, 2025: XRed targets US and UK companies that do business in India
> March, 2025: XRed targets manufacturing companies in the United Kingdom
> May, 2025: Threat Actors compromise ProColored, their driver update was compromised to push XRed
> July, 2025: Threat Actors compromise video game mouse company, push malware to video game players who use EndGame Gear for gaming
this is strange goop
More information:
- The 'ucpuid' command:
https://t.co/iw97XWwWWo
- Floating-point (float) support in the script engine:
https://t.co/890QayiXPZ
- And double:
https://t.co/JRUU6voUsa
- Linux 🐧 porting status:
https://t.co/3FjmPVcFNY
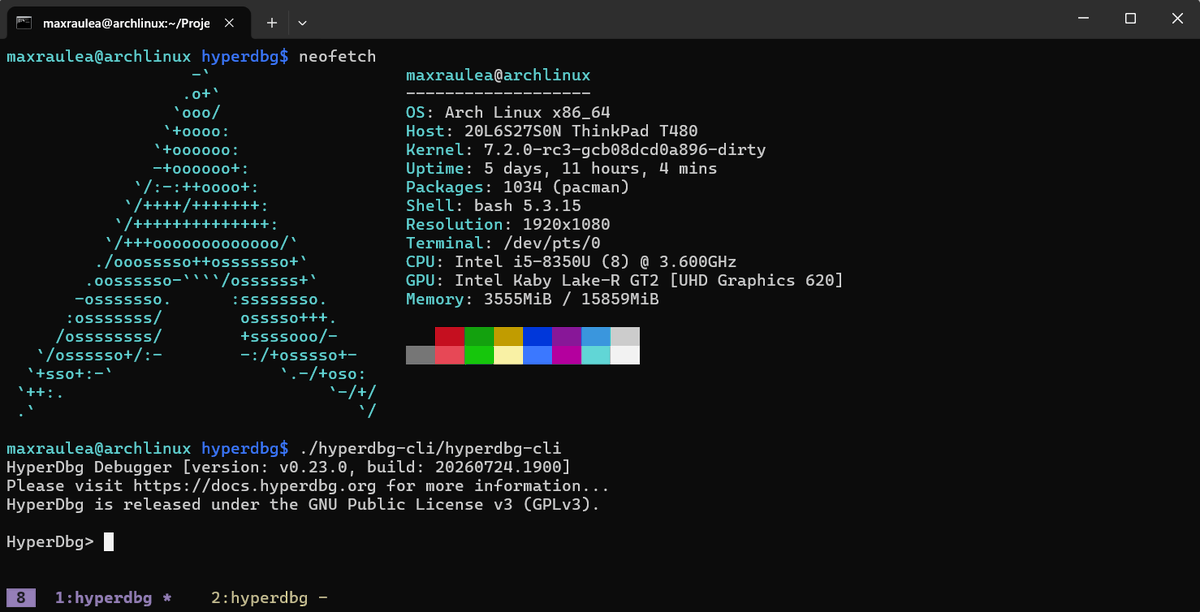
HyperDbg v0.23 is released!💫
This release adds support for floating-point variables in the script engine & introduces the new 'ucpuid' command, which displays selected CPUID leaves, interprets and maps them to the processor-defined flags.
Check it out:
https://t.co/HoiAFQCEyV
This version also brings Linux support for compiling user-mode code. Alongside these new features, this release includes numerous bug fixes and code quality improvements.
Happy debugging! 🌺🌼🌻
Major milestone in bringing HyperDbg to Linux! 🐧
Huge thanks to @MaxRaulea, all HyperDbg user-mode modules now compile on Linux. 🎉🪐💫
Next step is porting the kernel modules...
For more information,
Check structures in the script engine:
https://t.co/8MUHa8rbav
displaying linked lists in the virtual memory:
https://t.co/QawlTibkRN
And physical memory:
https://t.co/p3dDdfActk
HyperDbg v0.22 is released! 💫
Apart from bringing bug fixes, major progress toward porting HyperDbg for #Linux, HyperDbg now supports structures in the script engine.
This version also introduces new commands to display linked lists.
Check it out:
https://t.co/6dVoTxZHzf
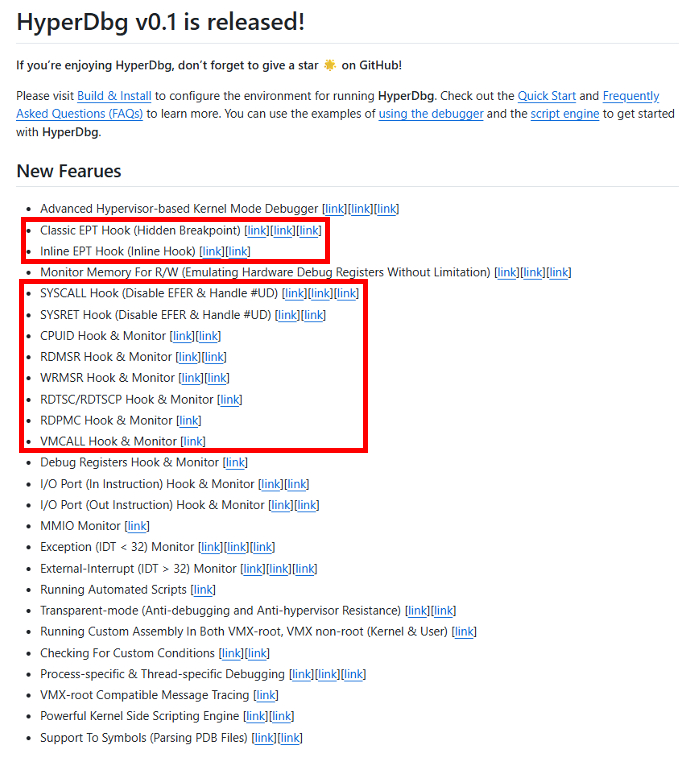
Need to debug interrupts, faults, or exceptions? HyperDbg has plenty of commands to help!
Use `!exception` to intercept exceptions (the first 32 entries of the IDT) and `!interrupt` to intercept interrupts (IDT entries 32–255).
(1/4)
A list hook like this is a reminder of how much deep knowledge modern systems demand. It demands a solid understanding of:
>CPU architecture and privileged instructions
>Paging and EPT
>VMX/VT-x and the VMCS
>Windows kernel internals
>Exception handling and interrupt delivery