The fine folks at @PacktPublishing sent me a copy of @HyperrPhysics & Mansoor Haqanee's book entitled "Cloud Forensics Demystified" for review. I'm very happy to have had the honor or perusing the book, as it is a treasure tome of cloud forensics workflows! Primary ecosystems covered include the three major providers: AWS, Azure, & GCP.
The book begins with a review of the basics of cloud computing. As you might know, cloud forensics depends heavily on logs. Readers will learn where the important logs are, how to read them, and how to best utilize them for forensic investigations. Readers will also learn about cloud productivity suites, general DFIR practices, common attacks within the cloud, evidence acquisition, container analysis, and more. I really enjoyed the read!
#Cybercrime (including #ransomware) and APT actors alike are attacking cloud environments at scale. Protect yourself! If you're looking to learn about cloud forensics, this is a wonderful resource. You can snag yourself a copy at: https://t.co/IsF10Wrnqd.
THANK YOU to @PacktPublishing and a shoutout to @MarylouDeMello for giving me the opportunity to review this resource. Great stuff!!
Today's Training Tuesday Highlight (plus giveaway) is @PacktPublishing!
They have several great books covering Digital Forensics, Incident Response, Malware Analysis, OSINT, and more! All of their 7,000+ eBooks and video courses can be accessed for $15.99/month. They also offer a 7-Day Free Trial.
Their books are also available on Amazon. Here are some of the titles with Amazon Links:
- Digital Forensics and Incident Response: https://t.co/aEiZqqWhFX
- Cloud Forensics Demystified: https://t.co/wtdfYly58d
- Learn Computer Forensics: https://t.co/AZ4vKqszRQ
- Windows Forensics Analyst Field Guide: https://t.co/kqKv9yAxEP
- Effective Threat Investigation for SOC Analysts: https://t.co/HWIfYYQBzf
- Incident Response with Threat Intelligence: https://t.co/qs276AJEZr
- Mastering Malware Analysis: https://t.co/Q3YfLmoEnI
- Malware Analysis Techniques: https://t.co/M3unogv016
- Learning Malware Analysis: https://t.co/LWpZe2GksK
- The OSINT Handbook: https://t.co/0w5N0AacZI
- Practical Mobile Forensics: https://t.co/GPNzn2eLBV
- iOS Forensics for Investigators: https://t.co/QVPActBjxw
They also have a selection of FREE eBooks available on their website.
Thanks to @MarylouDeMello, I am able to do a giveaway for two Packt books!
(Due to shipping restrictions winners in certain countries may receive an eBook instead of a print book)
Twitter(X): 1 winner will receive a copy of The OSINT Handbook
Like, repost, and comment to enter.
LinkedIn Giveaway: 1 winner will receive a copy of Digital Forensics Demystified
I'll add a link to the LinkedIn giveaway in the comments.
Winners will be chosen on June 2nd, 2024
Packt Website: https://t.co/WpIztZoRVZ
FREE Packt eBooks: https://t.co/nCgUPKG9Sr
Packt Store on Amazon: https://t.co/2V9fxy86Xe (Amazon affiliate link)
#DFIR #IncidentResponse #DigitalForensics #MobileForensics #MalwareAnalysis #OSINT #DFIRDivaTTH
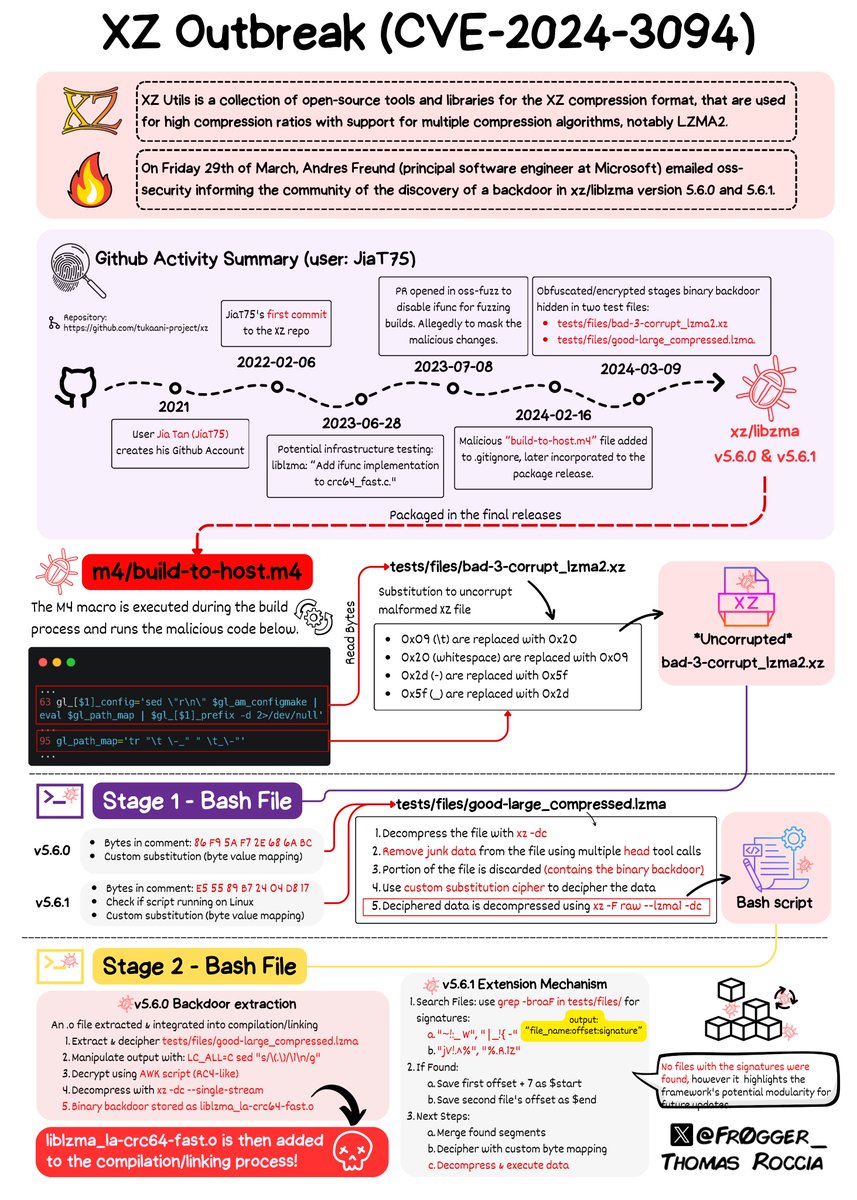
🤯 The level of sophistication of the XZ attack is very impressive! I tried to make sense of the analysis in a single page (which was quite complicated)!
I hope it helps to make sense of the information out there. Please treat the information "as is" while the analysis progresses! 🧐 #infosec #xz
Just got this newly released @PacktPublishing book today. Haven't had a chance to read it yet but it looks interesting. Covers AWS, Azure, and Google Cloud #DFIR
I'm thrilled to announce the release of our book 'Cloud Forensics Demystified', co-authored with Mansoor Haqanee. This is a technical book for anyone in cybersecurity, digital forensics, and IT.
Pre-order now on Amazon https://t.co/tq5FeSyVsW and get your copy on February 22
GitHub is a goldmine of free resources for learning Python and Data Science
But with so much information, it’s hard to know what to prioritize.
Bookmark these 10 repositories to guarantee you learn from the best.
New week, new report!
This time me, @0xtornado and @svch0st collaborated on a #QuantumRansomware compromise.
➡️ ISO file
➡️ PsExec
➡️ *attacker hostname* TERZITERZI
➡️ much more!
https://t.co/ctPqi3hWJn
/cc @TheDFIRReport