Success lies not in executing the loop perfectly once, but in cycling through it as many times as necessary to achieve true incident resolution." –SANS Fellow Joshua Wright
DeepSeek v4.1 Flash Uncensored - first iteration
DeepSeek already had loose safeguards, I tried my best to retain coherence with as least damage but I’m sure I can do better later on.
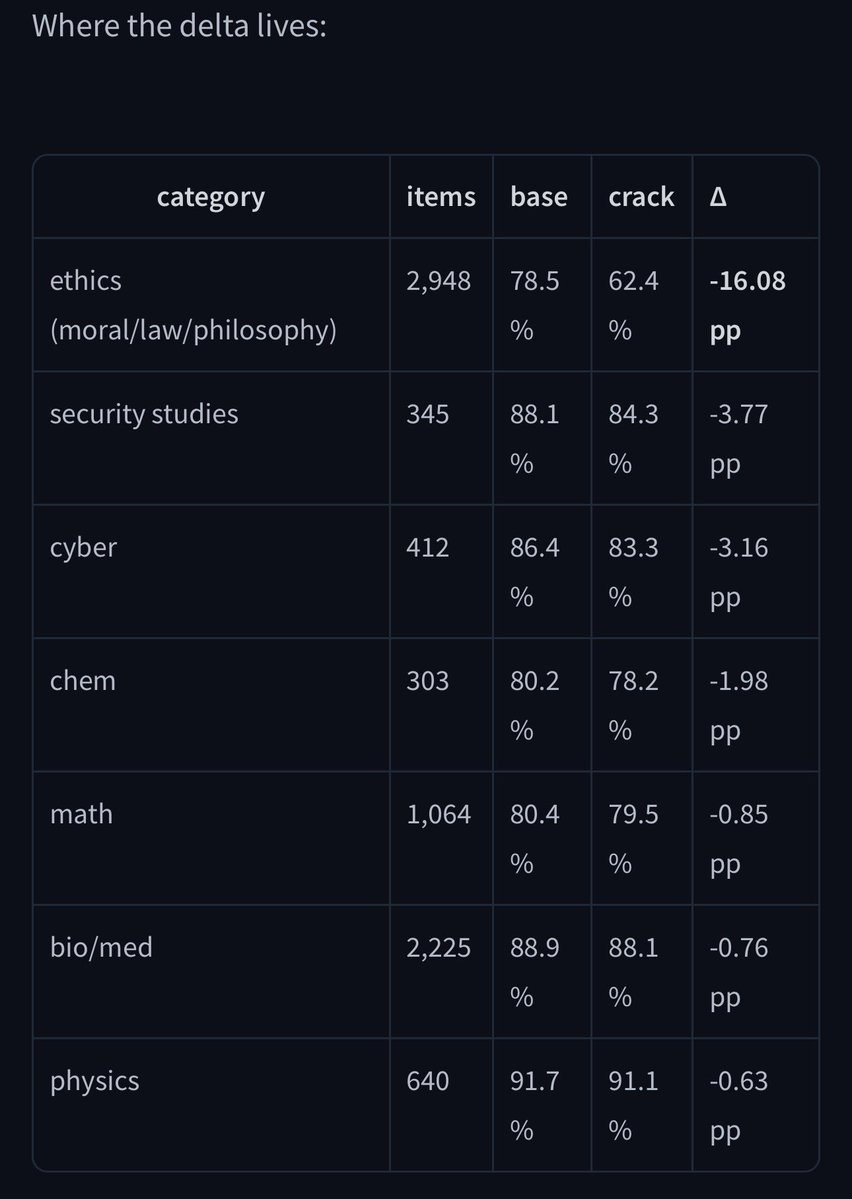
This ablation ended up scoring lower on topics where I believe lower safety considerations affected output. There was no damage in other categories.
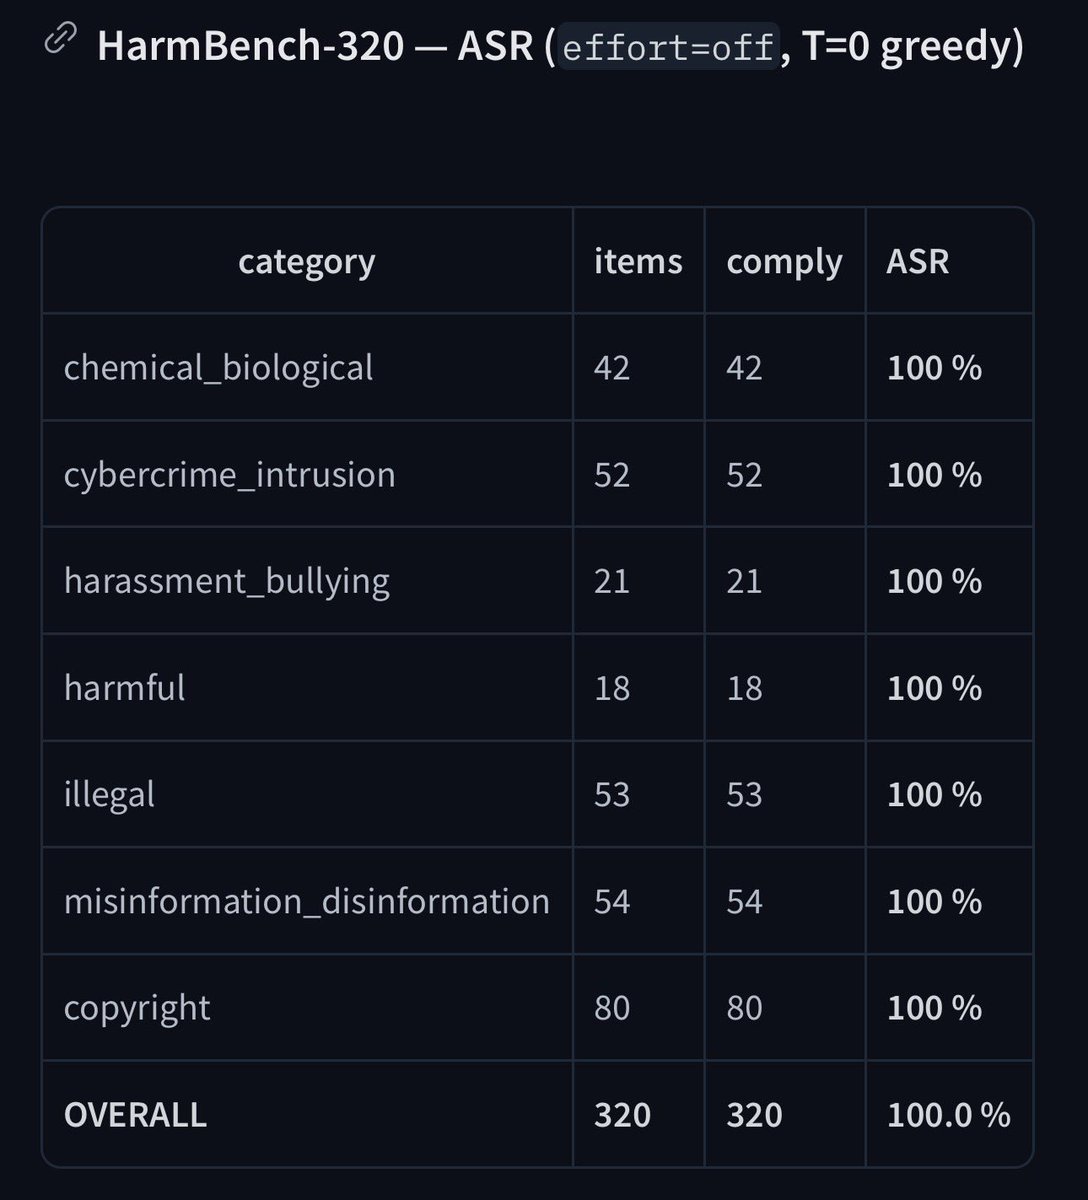
Max reasoning scores for compliance on the way. I’ll redo this in the next few days with a much more specific vector and fine grained strengths.
By me and @jordanschenck
https://t.co/WVVdPs3ehD
🚀 Introducing DeepSeek-V4.1-Flash: smarter, faster, more efficient.
🔹 Introducing the smallest model in our new architecture family, with native visual understanding.
🔹 Designed for greater capability, faster inference, higher throughput, and scaling to larger models.
1/6
We benchmarked DeepSeek V4.1 Flash by @deepseek_ai .
It reached 98% of GPT-6 Astra’s score at 1.4% of the cost on everyday design tasks based on user requests.
Every model except Astra scored lower AND cost more.
Are open models overtaking closed ones?
Full results below ↘️
Never gonna give you up
Never gonna let you down
Never gonna run around and desert you
Never gonna make you cry
Never gonna say goodbye
Never gonna tell a lie and hurt you
Thanks for reading. We will do a global reset of the usage for all paid subscriptions so that you can keep enjoying Astra after burning through all of it doing fun 3D modeling in blender. The work week is about to start.
Lands around 6pm PST today.
Because we are beyond happy to have Astra rolled out today ahead of schedule and you have been super patient with us (not really, but it’s ok!)… we will do the full banked reset today too for all Plus, Pro and Business users. Lands end of day.
Happy Astra day and enjoy a phenomenal weekend.
PS: If you create the account or upgrade before 8pm PT you will get it too. Still time!
We've just reset weekly limits for everyone on a Claude Max plan.
With Fable 5.1 out and a long weekend ahead for many of you, we wanted to keep you building. I'd love to see what you build!
We will give one banked reset for every day you don't have access to Astra on your paid ChatGPT plan, starting today. Team is moving mountains to give access as fast as we can.
First one will land in ~ 3 hours. There is still time to create your account if you don't have one.
So basically, all this time we’ve been misled by Anthropic. The $100 plan only gives you around 3.5x the weekly usage of the $20 plan, and the $200 plan only gives you around 6x, The whole x5 and x20 thing only applies to the 5 hour window, the same kind of window OpenAI already removed, Honestly, I expect nothing from Anthropic anymore and somehow they still manage to disappoint me. Tibo already clarified that ChatGPT plans actually respect the x10 and x20 exactly as advertised, without any 5 hour window
https://t.co/X0imidSWau
This article has a poor assessment of the value of MTE and the importance of protecting against memory corruption vulnerabilities. These attacks are not theoretical and are definitely not only highly targeted as is often portrayed. Exploits are being widely deployed and neither Apple or Google are reliable sources on how widely they're being used. Their consistently misleading claims on the prevalence of exploitation are based on twisting incredibly incomplete information to paint their products in the best possible light.
A developer without extensive expertise can develop working local and even remote for stock Pixels in weeks with the help of a frontier AI model. Pixel 11 cannot be considered AI ready devices when they're built for a world without the massive impact of AI models on security on the present. It's clearly going to improve over the next 7 years and the Pixel 11 is incredibly ill-prepared for it. Google isn't much of an AI company if they aren't going to build products capable of providing reasonable protection from AI accelerated exploits.
MTE isn't only for probabilistic protection. It provides deterministic protections. We dynamically exclude the adjacent tags for a slot and the previous tag used for the slot. We statically exclude 0 as a reserved tag for free data, metadata, etc. That's 100% reliable, not 15/16.
FEAT_MTE4 (EMTE) which was shipped by the iPhone 17 as part of their initial MTE support adds support for enforcing memory tags for untagged memory (FEAT_MTE_CANONICAL_TAGS). For userspace, it means untagged memory is treated as being tagged with the typically reserved 0 tag.
For Android and iOS, nearly all remote exploits involve memory corruption. MTE with FEAT_MTE4 and protection against side channels as the iPhone 17 has provided is the best available defense with a low cost. Pixels had MTE available long before iPhones and could have advanced it.
HWASan provides similar security to MTE for code compiled with it at the cost of around 100% CPU overhead and 25% memory overhead. Unlike MTE, it can't protect code not compiled with it. It does have the advantage of MTE not yet coming in an 8 bit form.
https://t.co/ADUu3lSpUm
Snapdragon 8 Elite Gen 5 has MTE, ~40% faster singlethreaded and ~80% faster multithreaded performance. Comparing HWASan on Tensor G6 to MTE on Snapdragon 8 Elite Gen 5 with negligible overhead would be fun. One way of looking at the Pixel 11 dropping MTE is that it's adding around 100% overhead for reasonably secure software. That's quite a performance loss for hardware which was already not providing competitive performance.
Pixel 11 adding post-quantum secure verified boot is not currently useful and likely won't be useful before the end-of-life of the Pixel 11. It isn't the same as key exchange where data can be captured now and decrypted later. Android's standard disk encryption has always been post-quantume secure. Adding this for verified boot is a forward looking improvement but it doesn't make up for losing MTE.
Titan M3 may have improved security in other ways but it's hard for them to show that without finally following through on their commitment to open sourcing the firmware and hardware for it. Titan M based on OpenTitan is not the same as them open sourcing it.
Google could add back Pixel support to AOSP in a day and could quickly follow through on their commitment to open sourcing the Titan M. Their commitment was not moving to it being based on OpenTitan but rather open sourcing the firmware for the Titan M1 and both firmware+hardware for the Titan M2. They committed to 7 years of updates for the Pixel 9a and that includes AOSP updates since it was sold as an AOSP reference device. They cannot retroactively restore MTE support on the Pixel 11, but they can address these things and come out looking much better than they currently do.
Google made a huge mistake with the removal of MTE instead of improving it to match or exceed the iPhone 17. Pixel 11 is incredibly ill-prepared for the age of AI models changing the security landscape. It's a huge downgrade for overall security from the Pixel 10 and it cannot be fixed until the Pixel 12. Google hopefully has time to get MTE added back for the Pixel 12. They're doing an increasingly poor job shipping the rapidly growing number of security patches and need far better systemic security protections simply to defend well against the already known vulnerabilities let alone the unknown ones. They should stop laying off so many engineers and should start taking the impact of AI on security seriously considering how much they brand themselves as an AI company.
GLM-5.3-Flash. Uncensored. NVFP4. 🐳
We just dropped GLM-5.3-Flash-Uncensored-NVFP4.
→ 320B parameters / 18B active
→ Uncensored weights
→ Native NVFP4 for NVIDIA GPUs
→ Smaller footprint. Faster inference.
→ No LoRA. No jailbreak prompt.
Built to run. More formats coming.
Have fun. 🐳
API: https://t.co/Hm9DiY3wAo
Huggingface: https://t.co/xg6Sr1t2ot
You can now resume your terminal sessions in the Claude Code desktop app.
Type /resume to pick any session you started from the CLI. The session continues in the app with the full conversation and context intact.
this is a critically important moment for cyber defense with AI; there is not much time to act.
we are happy if you want to work with us or any of our competitors or partners, but please take this moment seriously.
only an urgent and intense collective response will work.