Prochain meetup ce lundi 26/10 ! 👾
Au programme :
- @ImNotFl0 sur le pentest de frigo 👀
- @Elweth_ avec 0€ pour trouver des 0days
- @e1k_p1r4t3 via son retex de pwn de caméra 🎥
📍Boulangerie Bar - 26/10 partir de 19h
(Salle du bas)
On se retrouve le lundi 26/10 pour le meetup d’Octobre👾
Apparemment on va parler frigo & pentest 👀
📍Boulangerie Bar - 26/10 à partir de 19h
(Salle du bas)
#cybersecurite#lille#defcongroup
During a security assessment, our ninja @ImNotFl0 found vulnerabilities allowing to execute commands as root in the Danfoss SM800a, SM800 and SC255 controllers, mainly used to monitor and configure industrial fridges. Patch now! https://t.co/bat3dJ6GLI
https://t.co/opSjn3xTnP
In 2023, @Synacktiv researchers identified an authentication bypass in #Danfoss SM800 and SC255/SC355 controllers. The same vulnerability, reported again in 2025, could be linked to the recent supermarket refrigeration attack.
🔎 Authentication Bypass - Danfoss SM800 & SC255/SC355: https://t.co/Gzf4DrntWp
🔎 Multiple Vulnerabilities - Danfoss SM800A: https://t.co/A3EsNHKiC4
CI/CD pwnage with a pre-auth RCE in #ArgoCD by @hugow_vincent 💥
Discover how a single misconfiguration in a Helm chart can lead to a full cluster compromise sprinkled with some CodeQL shenanigans! 🥷
https://t.co/bNH8rE7uNo
We've been working on something for a while.
The talks your blue team doesn't want you to see.
🔴 Red Teaming. Initial Access. AD. Cloud & Web exploitation.
📍 Paris - Le Dernier Étage
📅 March 19–20, 2027
https://t.co/WcrpbyzSSV
CFP and additional details coming soon.
iOS for Security Engineers by Quentin Meffre (@0xdagger) and Victor Cutillas (@v1csec)
📅 Oct 12-15
📍 Espace Vinci or Espace Cléry, Paris 2nd
👉 https://t.co/qsRDOljksx
So glad to finally be able to present this research at @BlackHatEvents Asia! Blogposts are coming soon, on the menu: LPE via local NTLM reflection and RCE via a new arbitrary Kerberos authentication coercion technique 👀
Double trouble at #SOCON2026! Our ninja @kalimer0x00 was busy breaking down Microsoft SCCM (once again!), while @croco_byte unveiled new GPO-based attack paths & his latest BloodHound contributions targeting OUs & AD Sites. Awesome job! 👏
Le prochain meetup aura lieu ce lundi 02/03👾
Au programme :
- @Lefnui : Fonctionnement d’un DRM
- @4rchib4ld : La Corée du nord et le remote
📍Boulangerie Bar - 02/03 à partir de 19h
(Salle du bas)
Proud to finally share the write-up of our VMware Workstation escape from P2O Berlin 2025, featuring a generic bypass for Windows LFH mitigations using side-channels.
I hope it will be as fun to read as it was to exploit!
https://t.co/TGOc6LejsS
At #Pwn2Own Berlin 2025, a full exploit chain against VMware Workstation was demonstrated via a heap overflow in the PVSCSI controller.
Despite Windows 11 LFH mitigations, advanced heap shaping and side-channel techniques enabled a reliable exploit.
🔍 Full technical write-up 👇
https://t.co/R0E5Uqql1E
In a normal world, this should be an immense scandal in Europe.
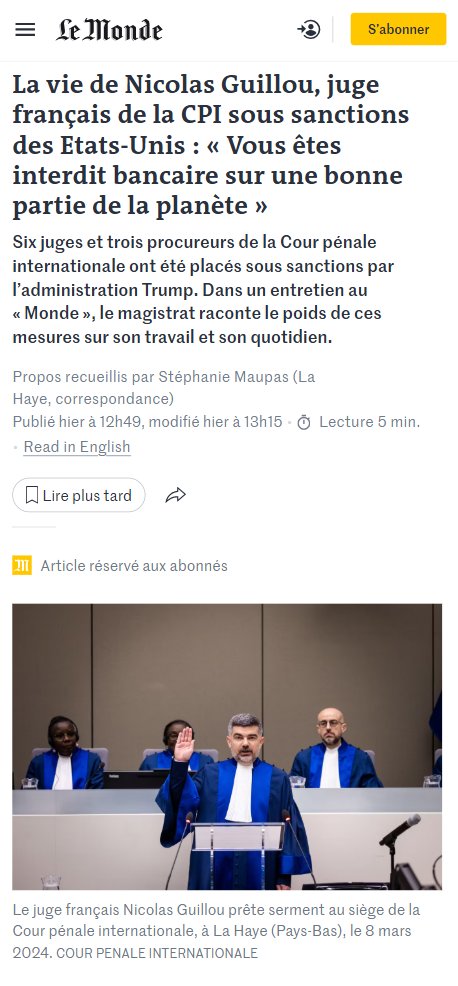
Le Monde has a long article (https://t.co/HsWFThQ5wF) describing the hellish life of Nicolas Guillou, a French judge at the ICC in The Hague, due to U.S. sanctions punishing him for authorizing arrest warrants against Netanyahu and Gallant for war crimes in Gaza.
Guillou's daily existence has been transformed into a Kafkaesque nightmare. He cannot: open or maintain accounts with Google, Amazon, Apple, or any US company; make hotel reservations (Expedia canceled his booking in France hours after he made it); conduct online commerce, since he can't know if the packaging is American; use any major credit card (Visa, Mastercard, Amex are all American); access normal banking services, even with non-American banks, as banks worldwide close sanctioned accounts; conduct virtually any financial transaction.
He describes it as being "economically banned across most of the planet," including in his own country, France, and where he works, the Netherlands.
That's the real shocking aspect of this: the Americans are:
- punishing a European citizen
- for doing his job in Europe
- applying laws Europe officially supports
- at an institution based in Europe
- that Europe helped create and fund
and Europe is not only doing essentially nothing to protect him, they're actively enforcing America's sanctions against their own citizen - European banks closing his accounts, European companies refusing him service, European institutions standing by while Washington destroys a European judge's life on European soil.
Again, in a normal world, European leaders and citizens should be absolutely outraged about this. But we've so normalized the hollowing out of European sovereignty that the sight of a European citizen being economically executed on European soil for upholding European law is treated, at best, as an unfortunate technical complication in transatlantic relations.
Watch how reflection attacks are still a thing in 2025 on the livestream where @yaumn_ and I will present how we discovered and analyzed CVE-2025-33073 !
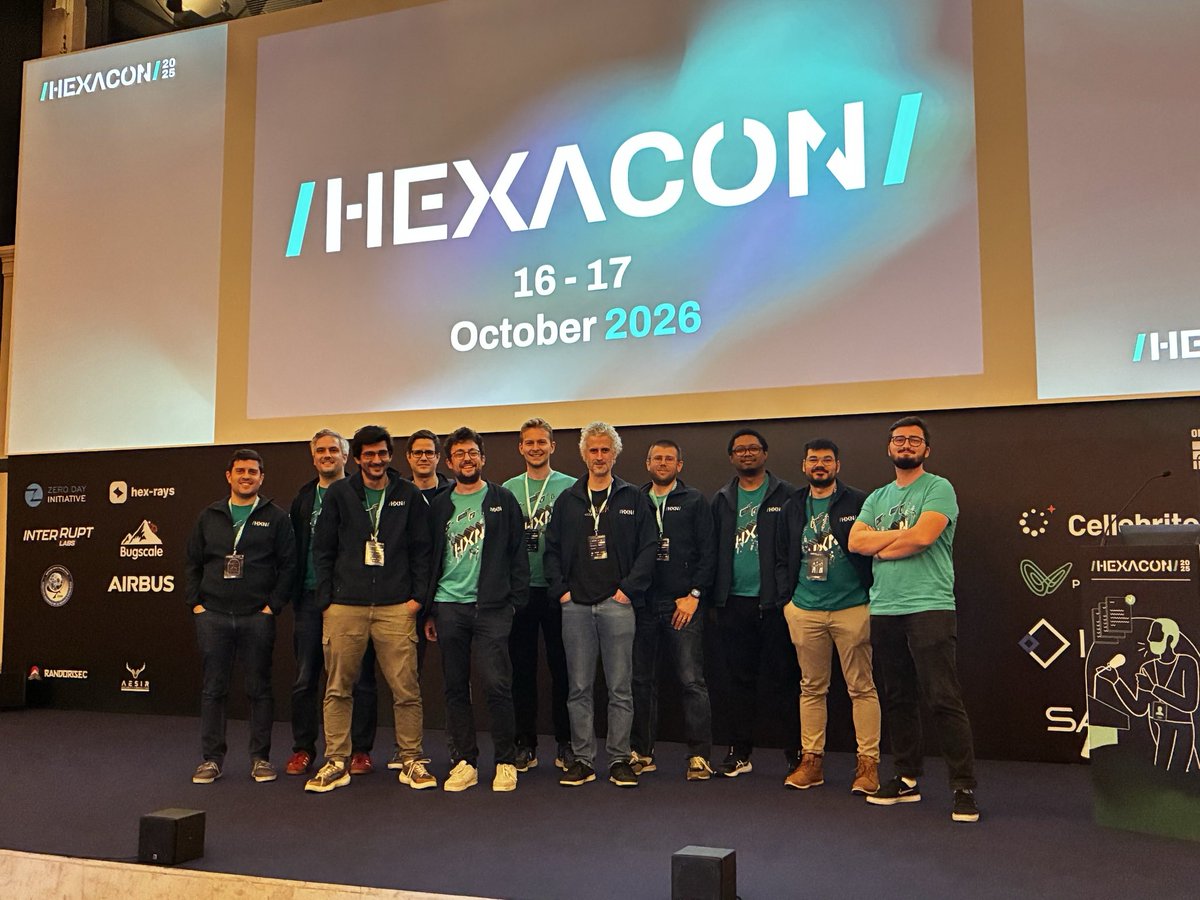
That's a wrap for Hexacon 2025!
We hope that you've enjoyed the event at least as much as we did 🤩
Please take a moment to fill out our satisfaction survey and help us make Hexacon 2026 even better 🔥
Thank you for trusting us year after year 🙏