If you like your technical stuff with a lot of memes, a dose of existential crisis, and possibly Rickrolling, my talk about Prometheus architecture from DevOpsDays 2023 is out!
https://t.co/qiUCmTTGTc
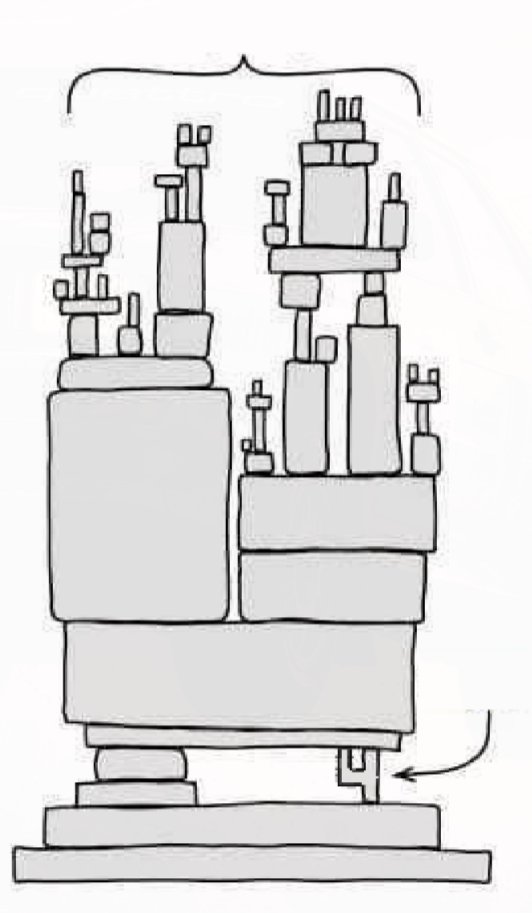
There must exists an app with PHP, deployed on Railway, with calls to cURL, with other services written in node that use Brotli compression running on a couple day old Linux, with their code self managed on GitLab
They are having a hell of a week
Just used LiteLLM to create my first PHP website. The AI even suggested getting a certificate from eMudhra for HTTPS to protect my login page. The future looks really bright 🥳
What's your private key? 1?
>...what? No?
2?
>It's 384 bits you dumbass. That's 35 orders of magnitude larger than the estimated number of atoms in the known universe.
...3?
>[visibly sweating] Th-this is ridiculous...
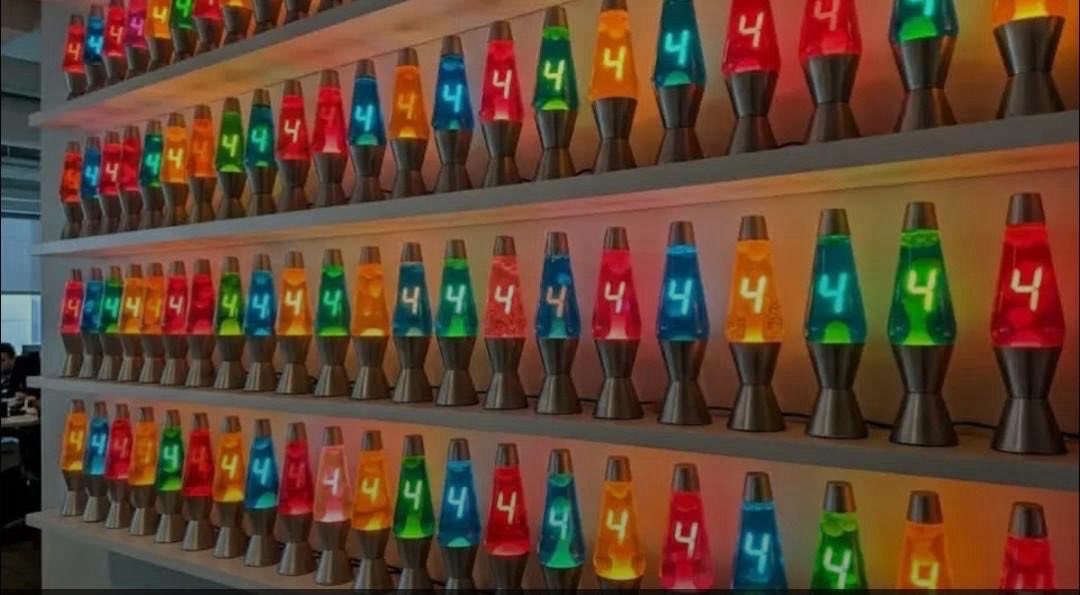
So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and https://t.co/QlOXb3COq3 went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
About 14 years ago. We had applied for a tender to run a full penetration test on an Indian bank. Black box. 120 IPs. External.
I don’t remember how much we quoted. But the winning bid was INR 25000 ($250 in today’s terms)
eMudhra and its “independent security verification” and “stringent audit requirements” are likely a result of similar procurement practices.
MeITy which is very quick in responding to blocking instagram, twitter handles has not responded at all over eMudhra. Under CERT-IN rules all of this should have been communicated to them by Oct 17th within 6 hrs. We block innovation and promote sovereignty, we have neither now.
Day 16/
You can now cache for 12h in the API and for logged in users across Codex & Work we keep cache forever and you don’t have any penalty for coming back to an old conversation or resuming after a few hours and are now guaranteed to hit the cache.