We had a great time at @GuidePointSec first-ever GPSec in the Bay Area this week! 🙌
The morning kicked off with a welcome from Ryan Brown, SVP at GuidePoint. Thank you to Ryan and Bryan Oliver, for including us and for the warm welcome.
The keynote was THE highlight: former FBI special agent Chris Tarbell and Hector Monsegur, the well-known hacker formerly known as Sabu, shared the story of how they went from adversaries to colleagues.
Emily O'Carroll, Field CISO at GuidePoint, moderated the conversation.
Thanks to everyone who stopped by our booth to talk with Claudia Slane and Brian Clutter about what we’re building at Intezer.
Congrats to the whole GuidePoint team on a fantastic inaugural event!
1/ We used AI agents to rebuild the source code of Slack, Apple’s Finder, and the TinyTurla-NG backdoor, starting from the compiled apps.
It’s not push-button, and results depend heavily on how an app is packaged. But “compiled” no longer means “private.”
Code obscurity and complexity used to protect software.
AI is making that protection obsolete.
We asked a simple question: how hard is it to rebuild well-known software with AI today?
Our senior security researcher @NicoleFishi19 partnered with Eran Segal and recreated Slack and Apple's Finder to find out.
The answer: not very.
Nation-state actors are already using AI to reverse engineer stolen software and hunt for bugs in security products. Copycat apps and leaked malware clones are following close behind.
Nicole met with Nate Nelson of @DarkReading to break it down 👇
https://t.co/s6bIHtmwGc
@MalwareTechBlog Agreed. Auto-remediation usually stays off until people trust the evidence behind it. The sweet spot is automating the response where the evidence is solid and letting a human make the call where it’s thin. Most teams never draw that line, so everything defaults to manual.
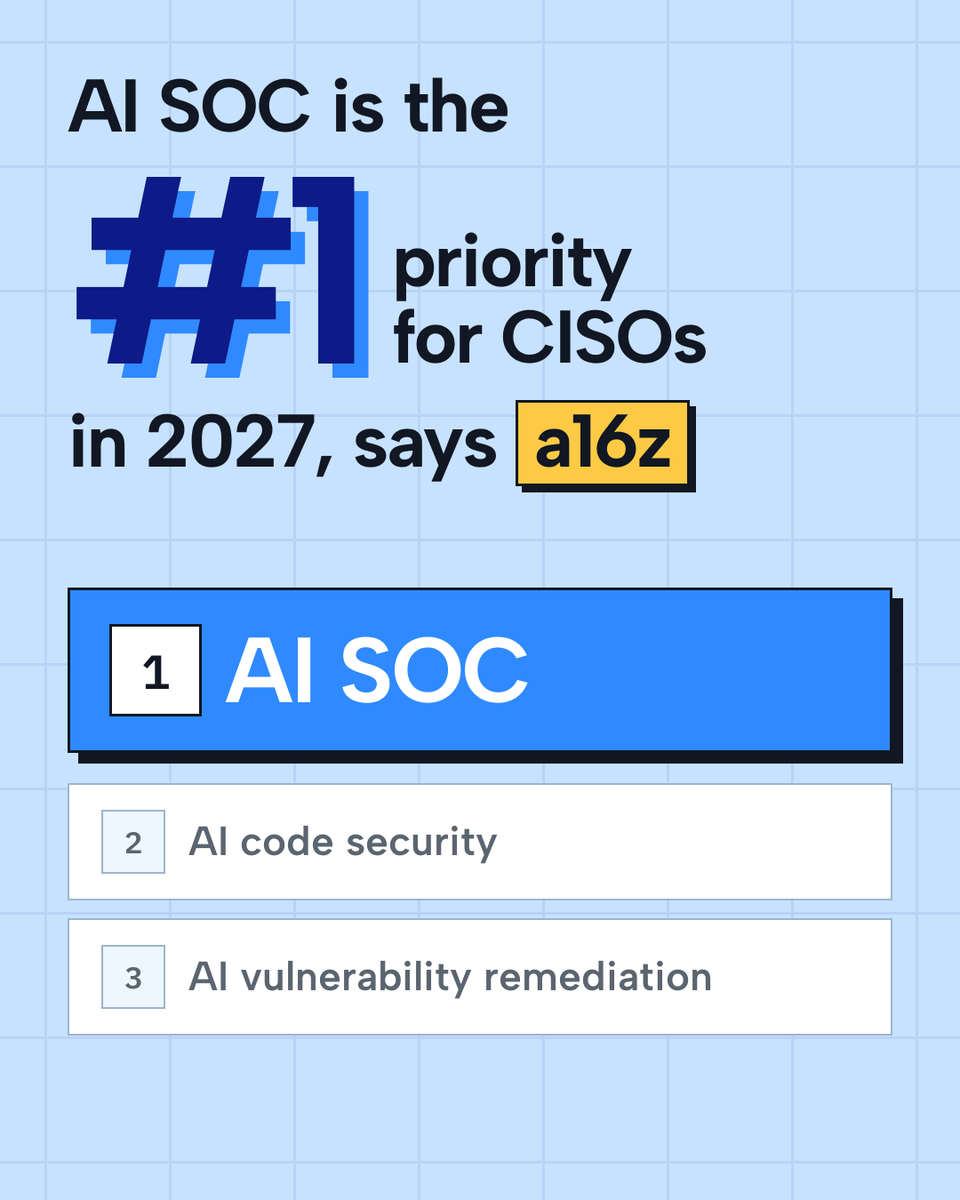
Only 4% of CISOs plan security cuts in 2027. AI SOC isn’t about headcount, it’s about the alerts nobody has time to look at.
That’s why 100 CISOs ranked it their #1 priority for @a16z.
Read our breakdown:
https://t.co/ubIkjZL2nE
Security testing is moving from a yearly checkup to always on
18% of CISOs run most of their offensive testing continuously today, 52% expect to within a year
They also want AI to close the loop, 70% would use it to retest and confirm their fixes actually worked
From a16z's @OwenColby and @steph_zhang, breaking down a survey of 100 CISOs at companies with 1,000+ employees: https://t.co/C814PJ4wGg
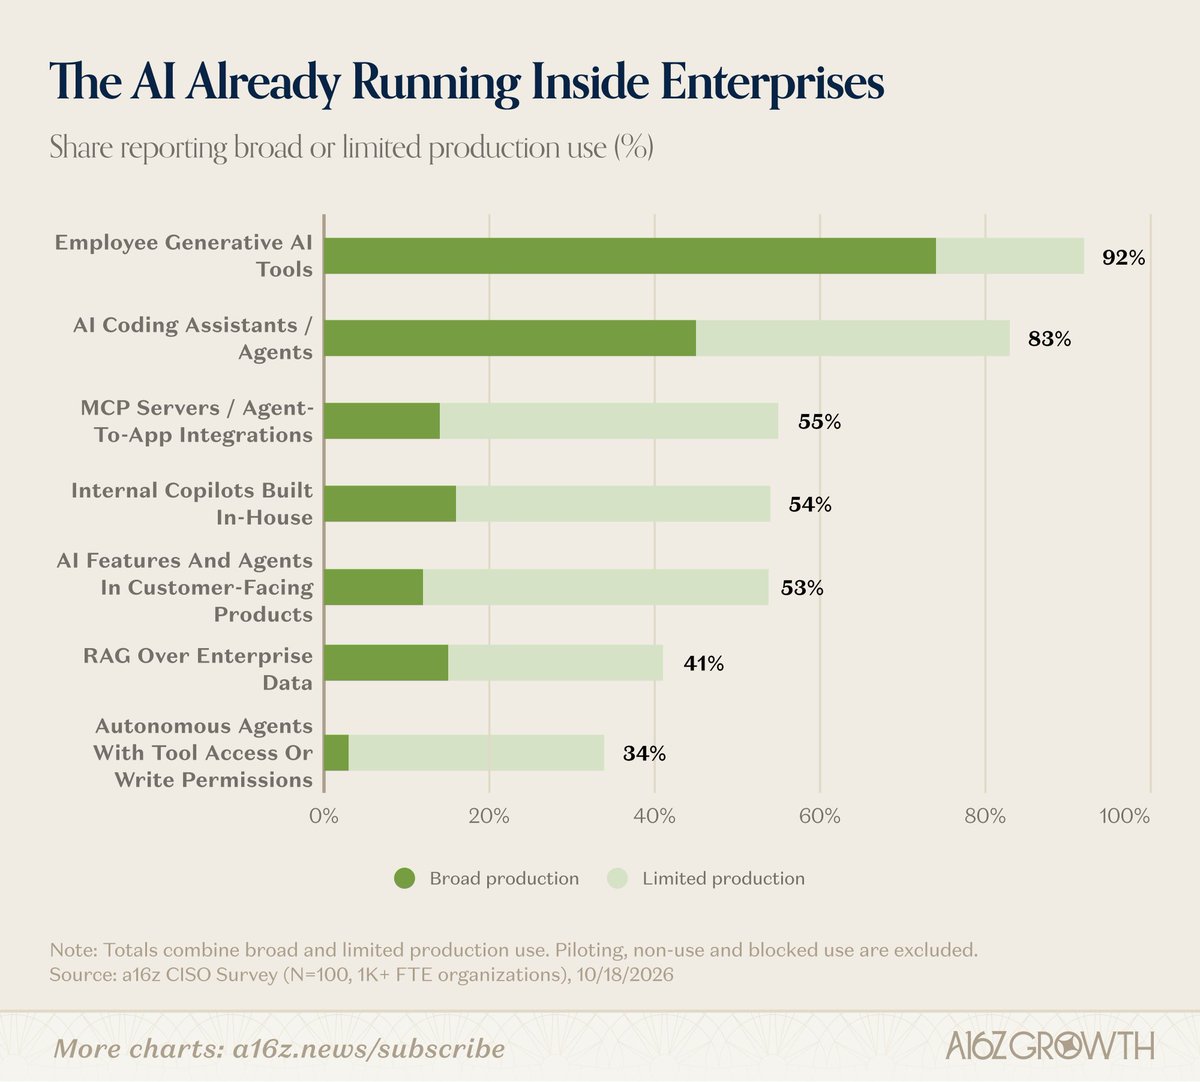
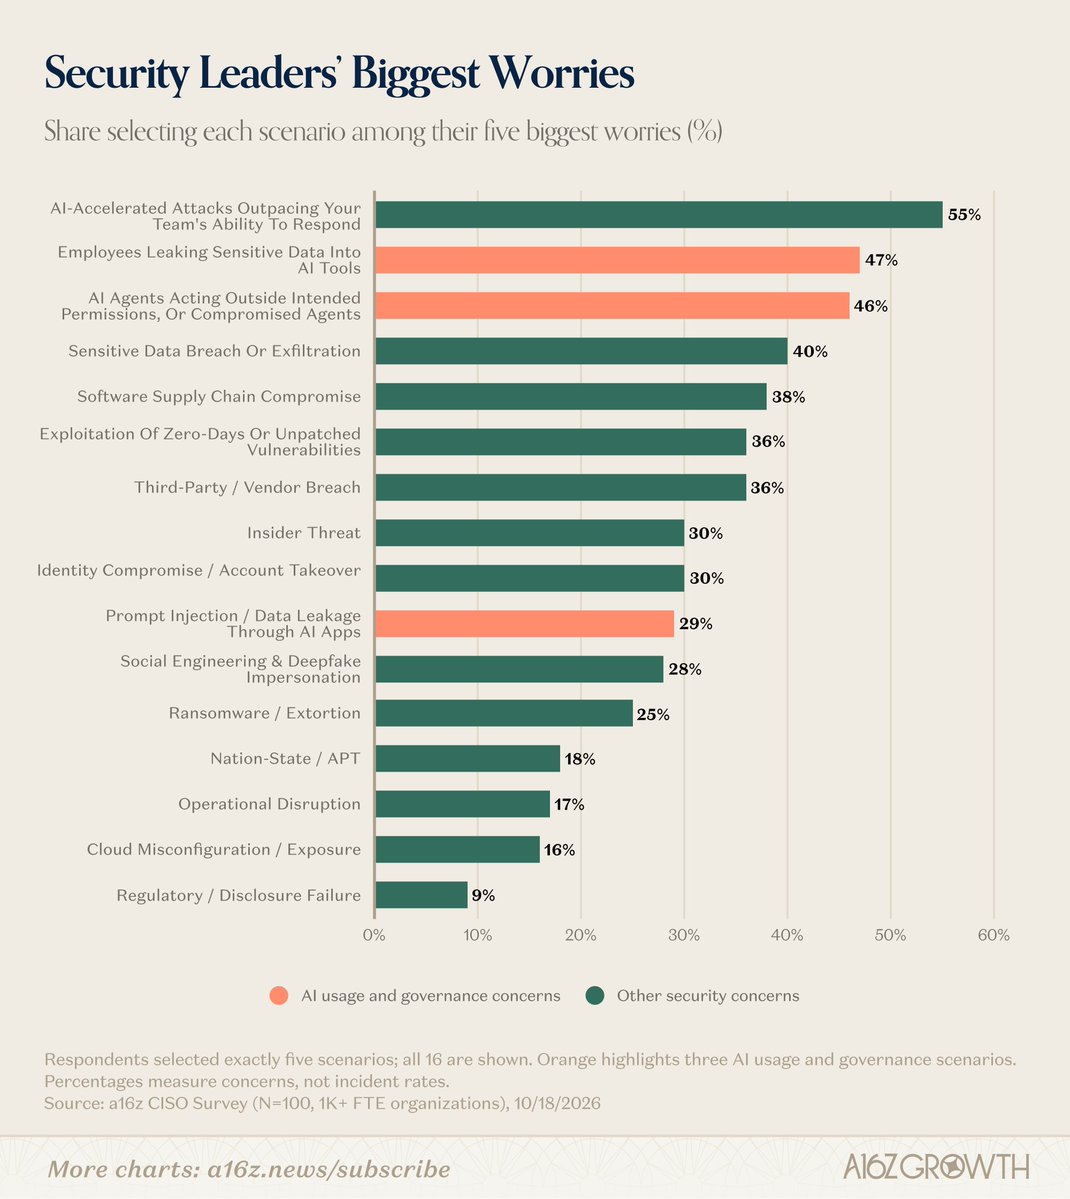
AI is already running across the enterprise, and securing it is now one of CISOs' biggest concerns
Already in production at their companies:
- Employee generative AI tools (92%)
- AI coding assistants or agents (83%)
- MCPs or agent-to-app integrations (55%)
- Autonomous agents with tool access or write permissions (34%)
Their biggest concerns:
- AI attacks outpacing their team (55%)
- Employees leaking data into AI tools (47%)
- AI agents exceeding permissions or getting compromised (46%)
From a16z's @OwenColby and @steph_zhang, breaking down a survey of 100 CISOs at companies with 1,000+ employees: https://t.co/C814PJ4wGg
2. They describe how the adoption of AI tools makes the job of security teams more complex. We saw this pattern in research we conducted at @IntezerLabs using our own data. https://t.co/xxxEOdbiLV
That was an interesting read!
Two things stood out to me:
1. It is interesting to see CISOs saying they expect security headcount to grow, while all we hear nowadays is that AI will take our jobs...
Anthropic's SOC has no tier1 or tier2. AI ingests alerts, runs investigations and routes hard calls to humans. The classic SOC pyramid was a workaround for the constraint of human analysts. That constraint is now disappearing. https://t.co/FJh5Vsu06Y
@IntezerLabs
[1/2] We detected a new #FireWood Linux backdoor variant. While most of the features remained the same, we discovered some changes in the configuration and an updated set of commands, such as file-read, HideModule, and a new command to terminate the module.
We are AMP’D to announce that Intezer has been named a launch partner for the @torq_io AMP Program!
Together, we’re transforming how security teams operate - empowering our customers to detect and defend against threats, faster. 🔥🔥🔥
#AISOC#autonomousSOC#cybersecurity
Join Justin Lentz (@CrimEvader) from @Solis_Security and Nicole Fishbein (@NicoleFishi19) from @IntezerLabs at #VB2025 in Berlin as they unpack an unusual case of long-term zero-day exploitation.
📅 Sept 26 | 11:00–11:30 | Green Room
👉 https://t.co/nJVq7jemdl
📢 Sponsor: Which AI SOC solutions are enterprise-ready?
This guide from @IntezerLabs breaks down the questions you should be asking to evaluate AI SOC vendors and validate bold claims about the value they can bring to your SOC.
Learn more → https://t.co/bFsG955ODl
.@IntezerLabs and @torq_io have partnered to bring agentic #AI collaboration into live SOC environments to reduce the operational load and speed up response time. #MSP#MSSP#cybersecurity#infosec https://t.co/yBZLlRVCt0
.@IntezerLabs and Torq have joined forces to launch cybersecurity’s first agent-to-agent collaboration 🚀
Find out how our partnership is redefining SecOps ➡️ https://t.co/05pdLmyY6S