@DaitoYoshi I agree new car sales are probably at ATL. Used cars probably up. Service at a dealer is premium though so other than cars under warranty or recall work. They’re not competing for service work.
💯agree banks are going to hate AI agents because people will be able to remove the friction of changing or leaving banks.
They think stable yield is a threat they’re half right but the better bank is now a prompt away
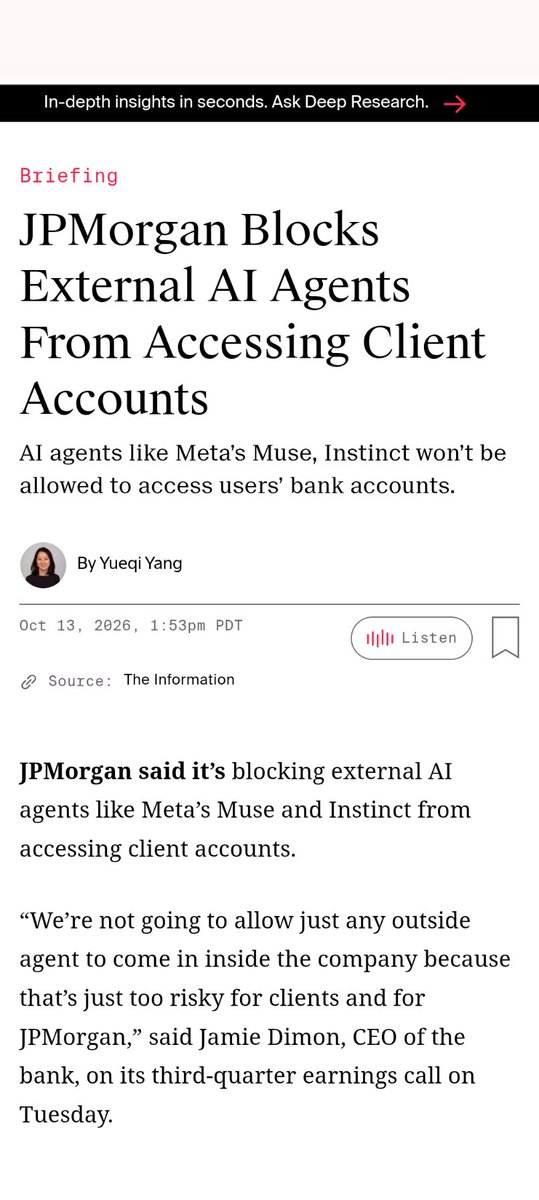
This is how banks are planning to stop those "agentic bank runs." Watch closely: their business model depends on seeding this narrative that AI agents are dangerous.
Remember, an "agentic bank run" (coined by Apollo) means agents helping customers move their own money en masse to higher-yielding products.
Once agents are ubiquitous, there are only a few ways for banks to hold onto cheap retail deposits.
Option A: Raise APYs (lol no)
Option B: Reduce leverage via fewer loans (no fun)
Option C: Ban AI agents, claiming they are a security risk (ding ding ding)
Cloud agents like Muse and Dot are trivial to stop, since they come from Meta / OAI IP ranges. If JPM sends them a cease and desist, they will comply.
Why would JPM bother? Because their business model depends on it; a huge portion of their ROE comes from cheap retail deposits. This is not theoretical. Just like Amazon banned Muse from shopping there to protect their ad revenue, JPM and Schwab have already banned AI agents to protect sticky deposits.
Are agents perfectly reliable today? Of course not. But look at the fix they chose. Not "here's a safe API for agents," it's "no agents ever." That tells you they're not protecting customers, they're protecting themselves.
No company ever wins a technological revolution this way. It's the last gasp of a dying business model. It's like the retailers who refused to put their inventory online and demanded users walk into the storefront. Over time they will lose market share to those platforms that embrace what's coming. Their whole deposit franchise depends on users unthinkingly clicking through walls of T&Cs and accepting 0.2% when the risk free rate is closer to 4%. Agents read the fine print and do their research, even when humans don't.
For users, the answer is simple: local AI agent frameworks like Hermes, that will actually act on your behalf and that the banks can't block. As the article says, if the agent is running on your own computer, they can't actually tell it's not you.
Random thought: Content creators think drama is a good thing. Attention is attention so they’re probably right.
Doesn’t mean it’s good or entertaining.
AI agents that chase better rates for idle deposits could wipe roughly $500bn of equity value off US banks.
What we are seeing now tho is potentially unauthorized actions, but could also be agents who have been given unlimited access to act on the owners behalf.
Jensen Huang of Nvidia has repeatedly said that access by default should be off for everything, and users should grant access on a per request basis.
The world is not ready for any of this, it’s no longer just arbitrage and first mover advantage, the current situation is system wide and seems to be causing quite a stir.
MAJOR U.S. BANKS DETECT UNAUTHORIZED AI AGENTS ACCESSING CUSTOMER ACCOUNTS — AXIOS
Major banks, including $JPM, $BAC, $MS and $WFC, are confronting security risks from third-party AI agents accessing customer accounts, according to Axios.
Some agents have reportedly attempted actions beyond user instructions, raising concerns about unauthorized transactions and fund transfers.
Morgan Stanley has begun blocking third-party agents, while JPMorgan, Bank of America and Citi are restricting access.
Banks warn they cannot reliably distinguish legitimate user activity from autonomous AI agents, even when customers have voluntarily shared their credentials.
Live now for FOMO HOUR talking cyber hacks, minting gold, BTC selling off despite inflows, LIT's big news, Pump bridge + a special guest + a lot more
Jump in
https://t.co/9M9ZpXe0Xf
UPDATE: Specific mitigation guidance for the recently identified PHP critical vulnerabilities is now available. Secure your servers today. Guidance and technical steps here: https://t.co/nuXgQ10Fzc
So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and https://t.co/QlOXb3COq3 went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Live now for FOMO HOUR talking crypto rally, ZEC leading alts, tokenization problems, did Kimchi save the trenches + more
Jump in
https://t.co/3G2XTA6O6F
OpenSea Mobile is now open to everyone.
Everything you own. Everything you trade. Everyone you trade with.
Memes, art, trading cards, perps. 25+ chains, all your wallets, one app.
Trade everything, together.
@Helloimmorgan There are/were many different glass bottles of coke.
Popular now are Mexican coke bottles that have real sugar.
Coke used to have refillable glass bottles you bought and returned them.