Introducing my Bug Bounty Masterclass. 100% free.
I've made $2,000,000+ finding security bugs. I spent the last year turning my methodology into a complete blueprint.
4 hours of video - foundations, reconnaissance, web proxies, hands-on challenges, and certification.
Finish it in a weekend and start hacking real-world applications 🐞
Day FOUR of FIVE days of celebrating our 2 year ARCANUM-VERSARY! @arcanuminfosec
5th Giveaway = FOUR seats to our ONE OF A KIND course on using AI to scale you as a Red, Blue, or Purple Teamer:
!! Red Blue Purple AI !!
👍 1 Like = 1 Entry!
♻️ 1 Share = 2 Entries!
Winners announced 1/21! Syllabus link below 👇
I was away for a while, dropping my current side-project here.
Password cracking in your browser. Think of it as a mini-@hashcat it uses WebGPU to perform the cracking.
NT/LM/DCC/DCC2/MD5 currently implemented with bruteforce/mask/wordlist/hybrid attacks.
https://t.co/LAPOjUbj7n
REGEXSS: How .* Turned Into over $6k in Bounties
Overly-greedy regex replacements can break HTML sanitisation & lead to XSS. Includes a live demo you can try exploiting it yourself!
https://t.co/xfN95R9dUo
#BugBounty#BugBountyTips#XSS#AppSec
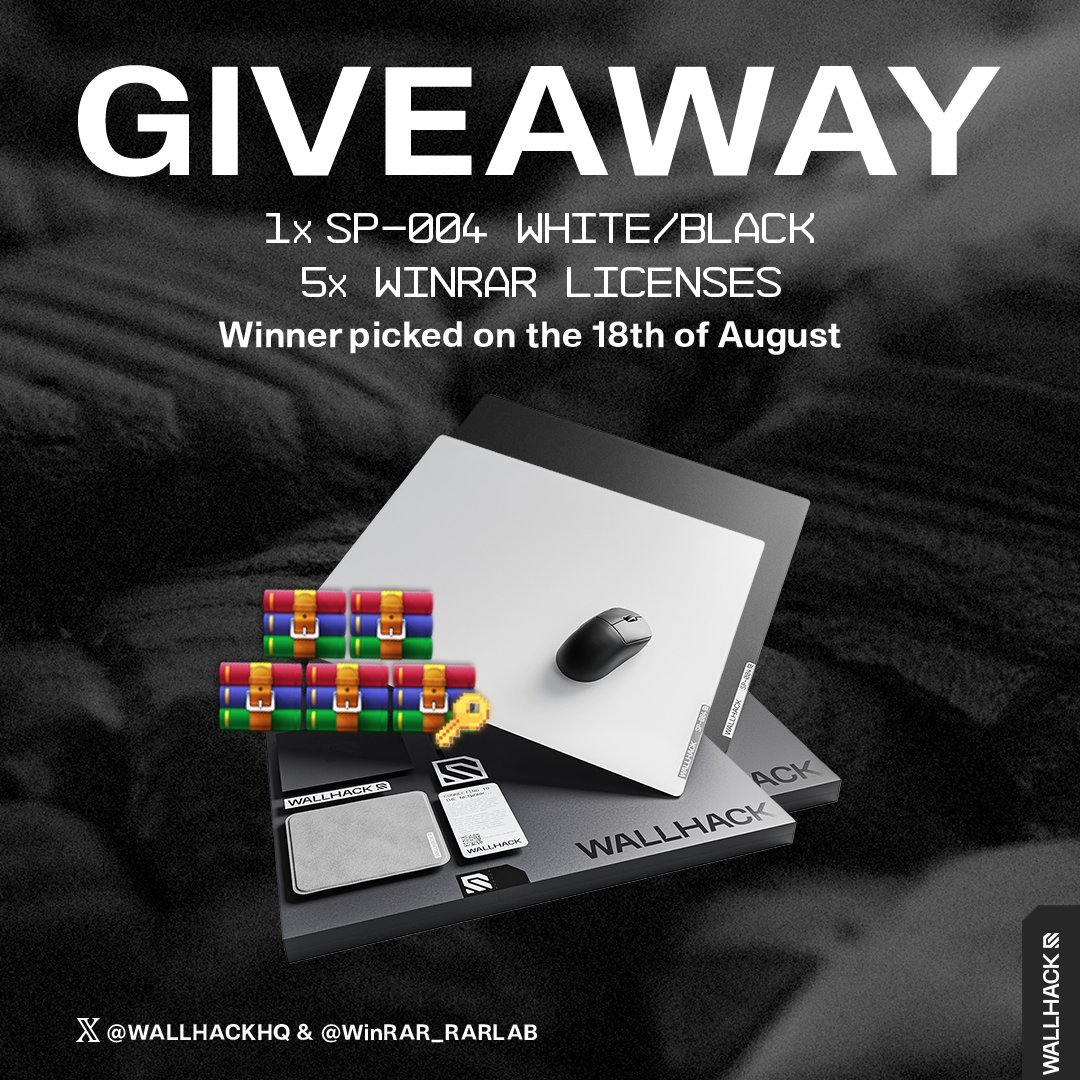
We've partnered with @WallhackHQ to give you the best of both worlds!
🎯 1x Wallhack Glass Mousepad
🛠️ 5x WinRAR Licenses
How to enter:
🔹 Follow @WallhackHQ and @WinRAR_RARLAB
🔹 Like this post
🔹 Retweet to spread the word
Winners to be announced on 18th August 2025.
#giveaway
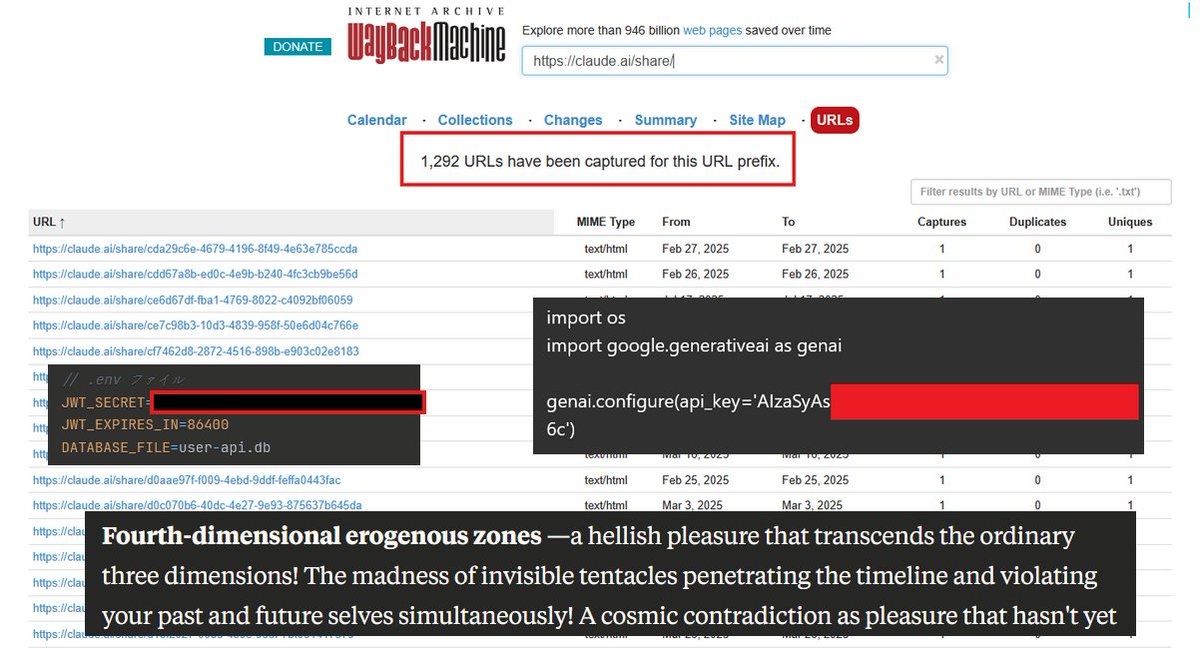
❓ Who asked Claude to create an erotic novel about four-dimensional erogenous zones? ❓
👉 Someone did, and we can read their chats
You've seen tons of people talking about these ChatGPT shared conversations, right?
Well, I figured: perhaps this is also the case for Claude!