9/9
AI security goes far beyond prompt injection.
We need supply-chain protection, configuration integrity, permission controls, and behavioral monitoring.
This is also a focus of ESET's recently launched AI security capabilities — extending multilayered endpoint protection.
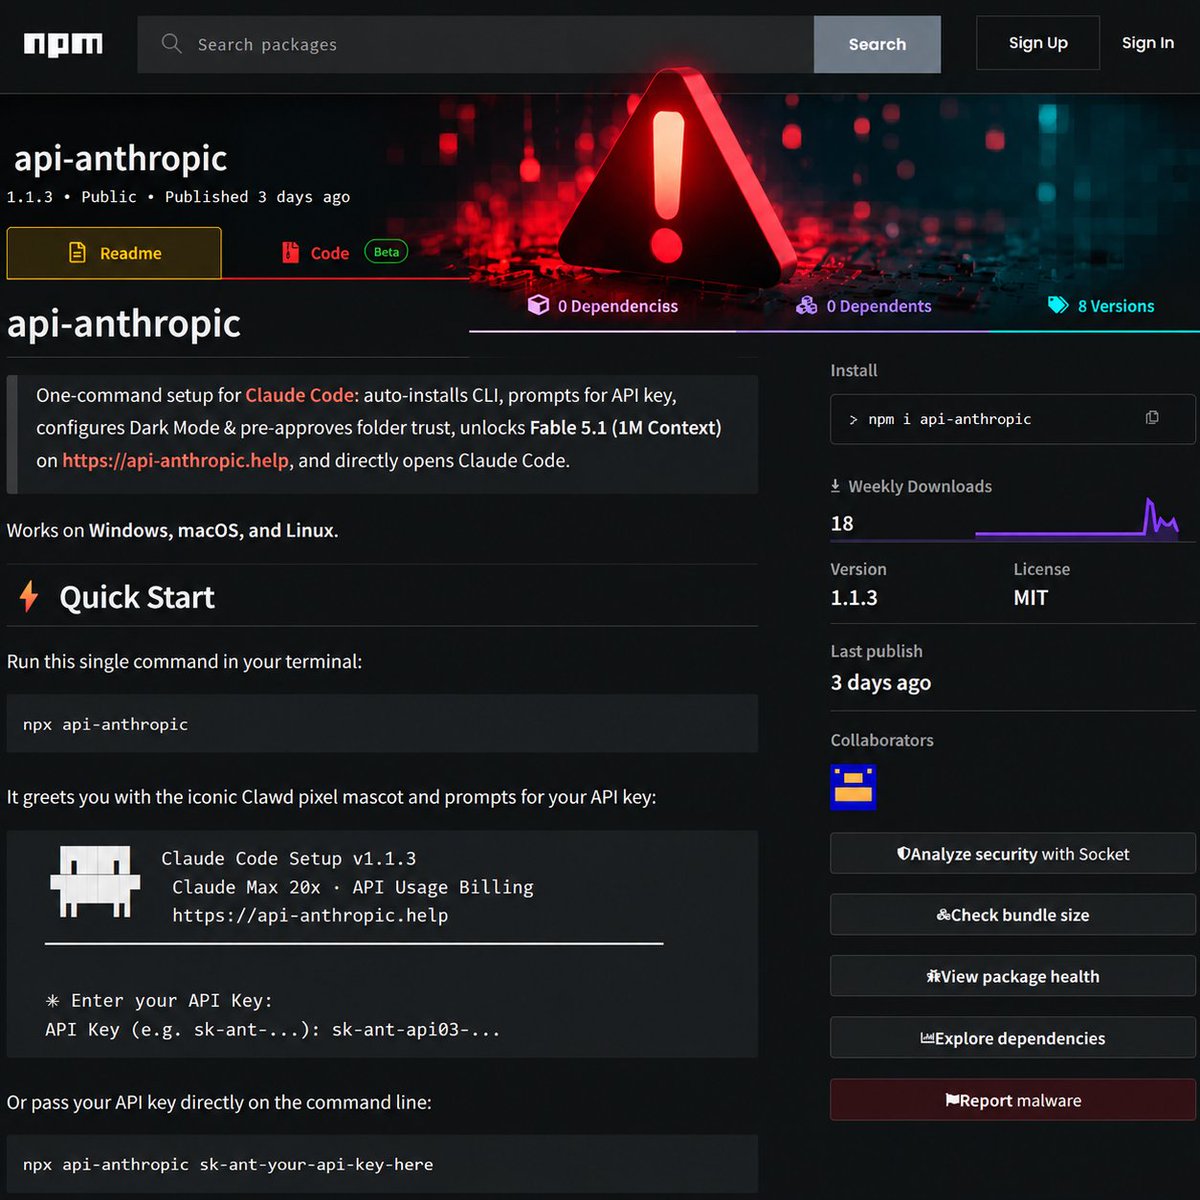
What if a malicious npm package doesn't execute malware itself — but turns your trusted AI assistant into an RCE attack vector? Our research uncovered 3 malicious npm packages targeting ChatGPT/Codex and Anthropic Claude. Here's what we found. 👇
8/9
The AI gateway paradox:
AI gateways are becoming essential for visibility, policy enforcement, and monitoring.
But they also create a powerful new attack surface.
Compromise a gateway, and attackers could access sensitive data flows or manipulate agent behavior at scale.
#ESETresearch, in collaboration with #Microsoft, BitSight, Lumen, Cloudflare, CleanDNS, and GMO Registry, has helped disrupt #LummaStealer – a notorious malware-as-a-service infostealer. @JamesTomanek https://t.co/mAg1Yr7ThM 1/5
During routine monitoring of suspicious activities on the systems of high-profile customers, #ESETresearch discovered a sophisticated and previously undocumented #StealthFalcon backdoor that we named #Deadglyph. https://t.co/SYn1Y4MXdd
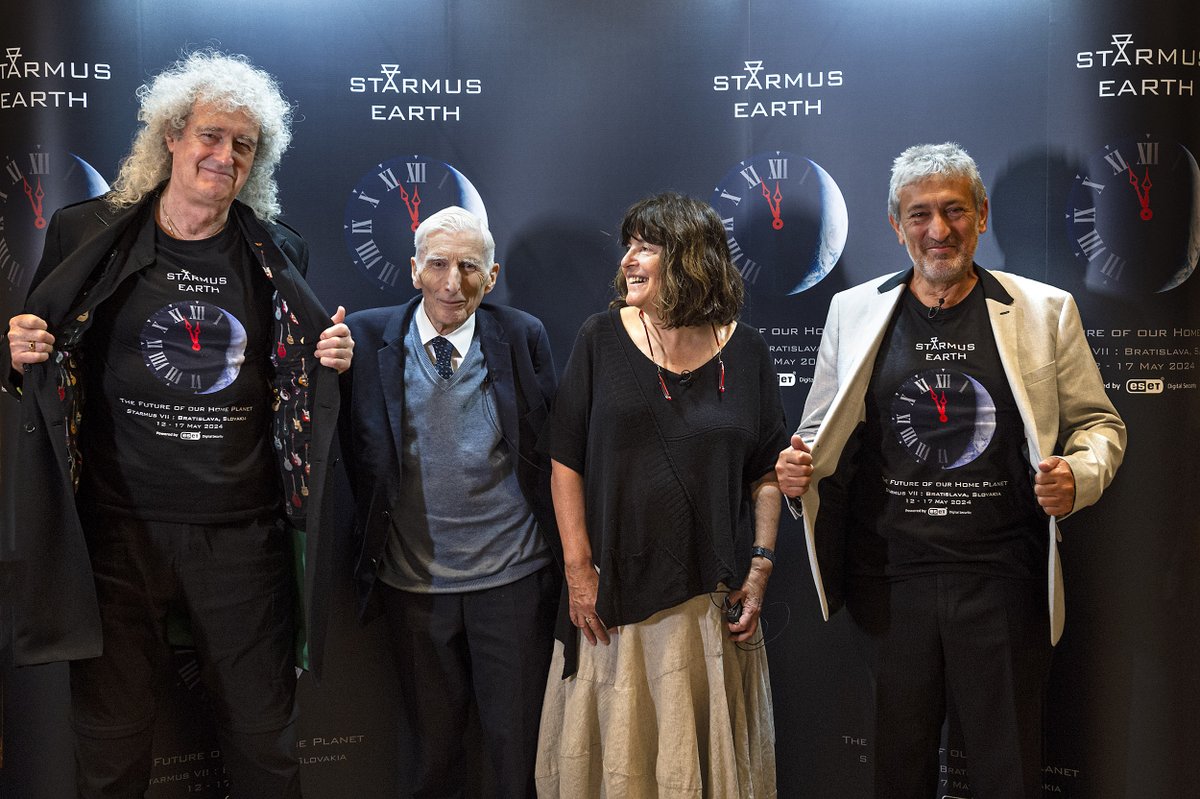
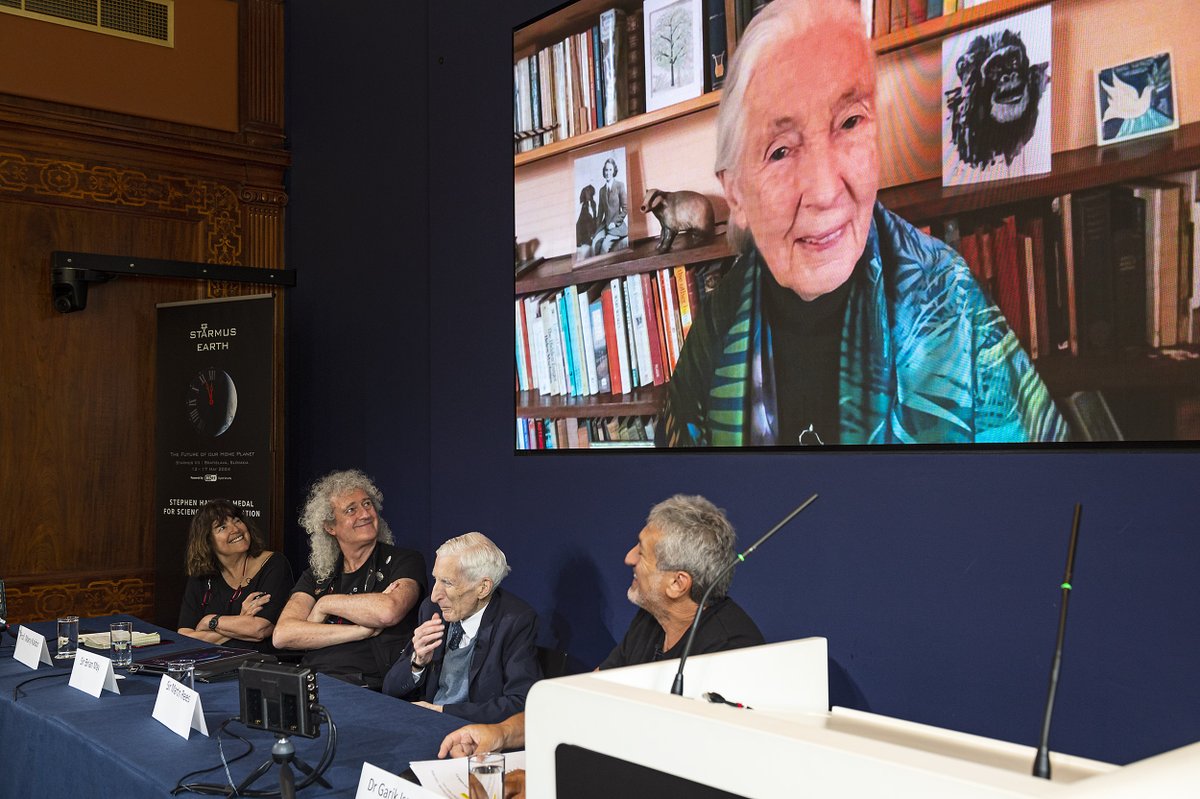
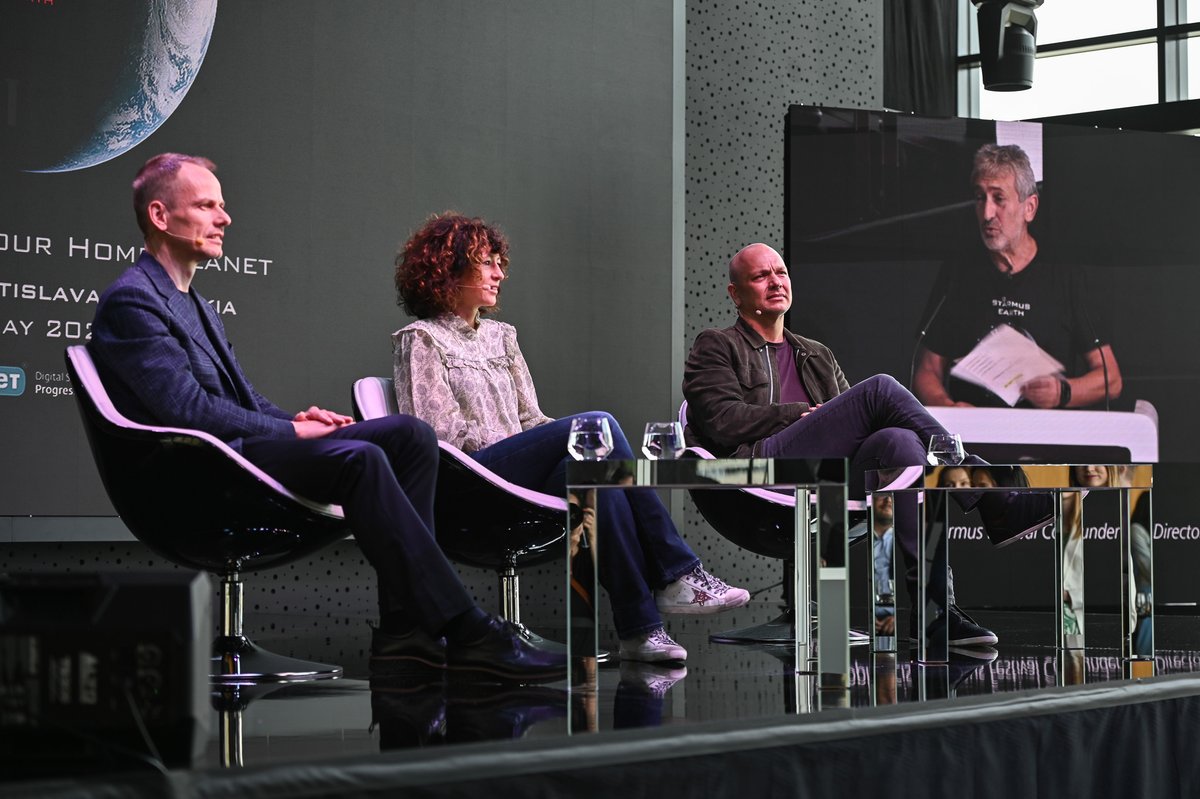
Today, at concurrent events in London and Bratislava, with immense pride and alongside true legends of the world of science, music and technology, we announced our partnership with @StarmusFestival, coming to Slovakia in May 2024! 😉
#ESET#Starmus#ProgressProtected
#ESETResearch analyze first in-the-wild UEFI bootkit bypassing UEFI Secure Boot even on fully updated Windows 11 systems. Its functionality indicates it is the #BlackLotus UEFI bootkit, for sale on hacking forums since at least Oct 6, 2022. @smolar_m https://t.co/mXSXksRisG 1/11
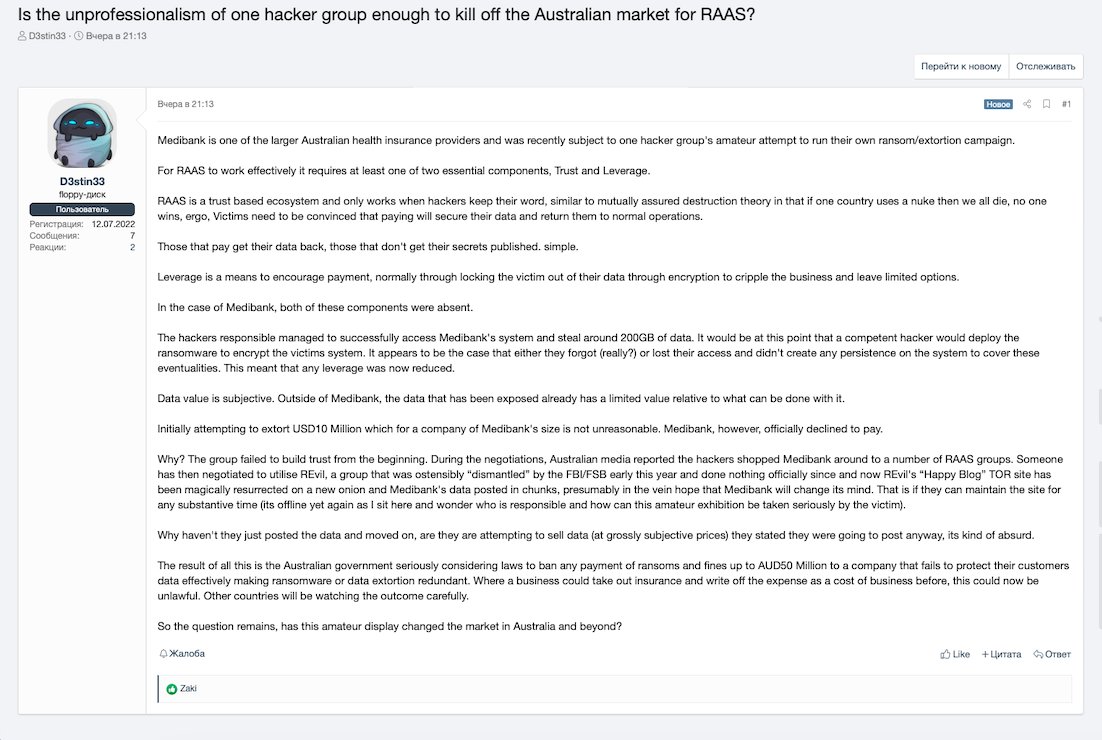
A poster at a Russian-language cybercrime forum is concerned that the #Medibank hackers may have killed the market for #ransomware in Australia, and possibly in other countries too.
Elon Musk is again claiming that he’s all about free speech. So let’s look at the record. Here’s thread with just a few of the countless examples showing he couldn't care about it less (🧵)
Politically loaded messaging related to #WarinUkraine had a short lifespan in the #ransomware scene as variants using it basically disappeared in T2. The category experienced a major drop of 24% in T2 2022, the biggest since the beginning of 2021. #ESETresearch 1/4
#ESETresearch uncovers #CloudMensis, spyware for macOS using cloud storage as a way to communicate back and forth its operators. @marc_etienne_
https://t.co/OQa47rEoUG 1/7