#NEW - ToolShell Used to Compromise Telecoms Company in Middle East - China-based threat actors also compromised networks of government agencies in countries in Africa and South America. Read more: https://t.co/xFZyjrnWGW
Another wiper attack targeting organizations in Albania by the Iranian Druidfly group. SHA256: 81eb22828306f3197b35fef2035cef2c548f587f8511902852964850023389d7 #wiper#druidfly#iran (1 of 5)
China-linked espionage group Billbug compromised multiple orgs in a Southeast Asian country, including a government ministry, an air traffic control org, and telco operator. Find out more: https://t.co/qen5IAHnET #China#Espionage#APT
Multiple new variants of a malicious driver that first surfaced in 2022 are circulating in the wild. The driver is used by attackers to attempt to disable security solutions. #ransomware#threatintelligence (1 of 3)
Government ministries, an air traffic control organization, a telecoms company, and a media outlet targeted in espionage campaign with links to China-based APT actors https://t.co/X9tUUdQFSt #Espionage#SoutheastAsia
The domain greentrees[.]top has been leveraged for C2 purposes by actors using #BlackBasta#ransomware in multiple attacks in recent weeks. #threatintelligence (1 of 3)
#ESETresearch discovered an #exploit targeting Firefox and Windows zero days, used in the wild by Russia-aligned #RomCom. Browsing a specially crafted web page runs arbitrary code with the privileges of the user, compromising the PC. @dmnsch & R.Dumont https://t.co/qugbteKlcE 1/7
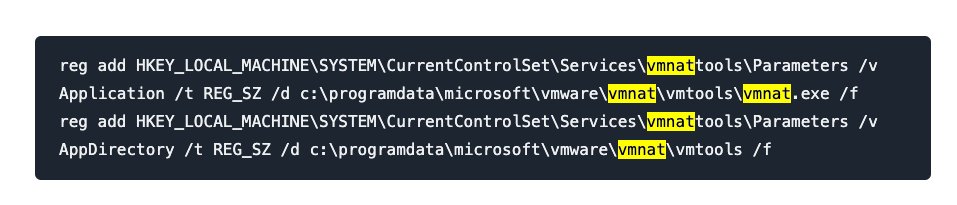
A campaign involving an old version of Microsoft Word used for sideloading and TrueSight Killer, which was previously reported by Acronis and Trend, may be more extensive than thought and is hitting targets in multiple sectors. Here are some new IOCs (1 of 5)
Ongoing campaign targeting IIS servers incl one airline in Middle East. Unknown payload (goopdate32.dll), likely sideloaded. Actor & motive unknown. Similar to reported Seedworm (MuddyWater) activity but low confidence. Also some low confidence links to Damselfly activity(1 of 2)
#ESETresearch discovered a signed, vulnerable, ad-injecting driver from a mysterious Chinese company. This threat, which we dubbed HotPage, comes self-contained in an executable that installs its main driver and injects libraries into Chromium-based browsers. 1/7
ThreatLabz has uncovered new tools from #APT41 including #DodgeBox and #MoonWalk. DodgeBox utilizes EDR evasion techniques including call stack spoofing, unhooking APIs, and bypassing Control Flow Guard. The purpose of DodgeBox is to deploy the MoonWalk backdoor, which leverages @GoogleDrive for C2 communications.
Check out Part 1 of our blog series: https://t.co/PhApuYEiZd
Our Threat Hunter Team has found some evidence that attackers linked to Black Basta may have exploited CVE-2024-26169 as a zero-day prior to patching https://t.co/AYPMk37Tlu #ZeroDay#Ransomware#BlackBasta
In May 2023, Sophos MDR discovered an intruder exploiting a component of VMware on a customer’s network. MDR launched a threat hunt to see where else the technique was being used—and uncovered a Chinese state-sponsored cyberespionage operation we have dubbed "Crimson Palace."/1
North Korean espionage group #Springtail, recently the subject of a U.S. government alert, has been updating its toolset. Here's what we found: https://t.co/Z5EOepwFI2 #kimsuky#northkorea#espionage
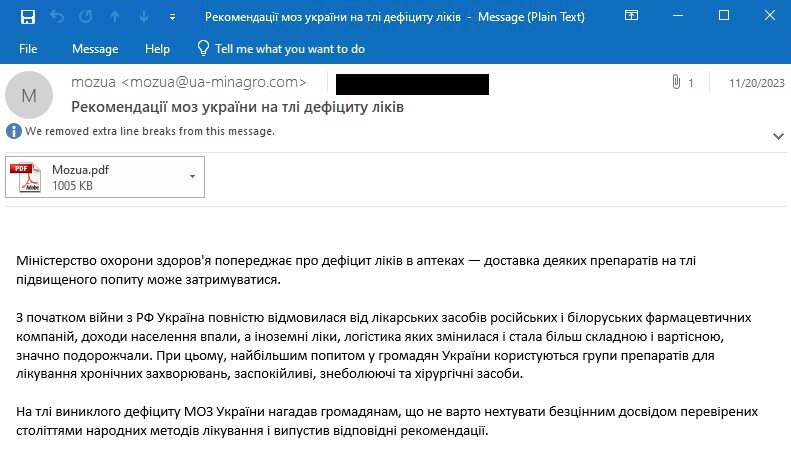
#BREAKING#ESETresearch discovered Operation Texonto, a disinformation campaign intended to demoralize Ukrainians. We detected two spam waves: November and late December 2023. The emails warn about drug or food shortages, or suggest amputating a limb to avoid military. 🇺🇦🇷🇺 1/5
#ESETresearch has discovered a China-aligned APT group, which we named #Blackwood, that leverages adversary-in-the-middle (AitM) to deliver the NSPX30 implant via software updates. NSPX30 is a sophisticated implant evolving since at least 2005. @0xfmz https://t.co/tI4fRejGdC 1/6
NEW: Seedworm: Iranian Hackers Target Telecoms Orgs in North and East Africa - MuddyC2Go infrastructure and custom keylogger among tools used in November attack campaign. Read more: https://t.co/lj4qIpRc9n
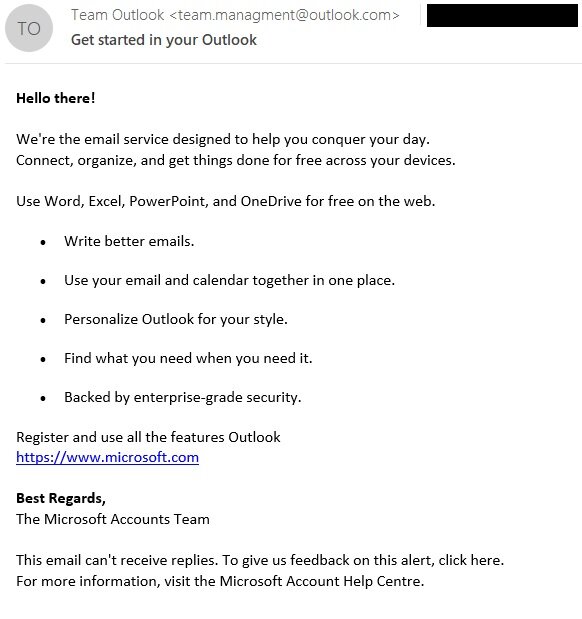
#ESETResearch discovered a zero-day XSS vulnerability (#CVE-2023-5631) in Roundcube Webmail servers. It is actively used in the wild by #WinterVivern to target governments and a think tank in Europe. The exploit was contained in a legitimate-looking email about Outlook. 1/4
#Budworm - APT Group Uses Updated Custom Tool in Attacks on Government and Telecoms Org - Previously unseen version of #SysUpdate used in campaign. Read more: https://t.co/VP9CLLCGyl #infosec
Our Threat Hunter team has found evidence of updated tooling by the Clubhorn APT group (aka #SideCopy). Recent attack involved modified version of #NightFury backdoor. (1/5)