“A building protected by nothing more than a cheap combination lock but inhabited by people who are alert and risk-aware is much safer than one with the worlds most sophisticated alarm system whose tenants assume they’re living in an impregnable fortress” Bill Mason
Good read.
I feel like AI won't solve problems in a SOC for real. It will surely solve some problems, but it will also introduce new problems for us to tackle with.
https://t.co/eiemE73J0T
September has been a busy month at Threat Hunting Labs: three major lab releases, video walkthroughs and a lot of improvements to how you learn and hunt.
🔎 The Recurring Impostor: a Flash Hunt with https://t.co/M0IXaLCrt4 investigation pivots, connecting Windows telemetry with external infrastructure research
- https://t.co/UV8n8qKmZE
🖥️ From SEO Poisoning to Custom RMM and Cobalt Strike, with Threat Hunting, Incident Response, Detection Engineering and Malware Analysis tracks.
- https://t.co/hdNcOGRvjh
🏆 Iranian APT Campaign Against Aerodyne Engineering: our first Threat Hunting League competition, now available as a practice-only Advanced Emulation.
- https://t.co/nojk04DD6X
We’ve also added narrated video walkthroughs for Threat Hunting and Incident Response questions, introduced Learning Paths and a first-lab orientation video.
𝗠𝗼𝗿𝗲 𝗨𝗽𝗱𝗮𝘁𝗲𝘀:
Searches now stay within each investigation’s verified evidence window, with an improved time picker to help you choose the period you want to investigate across Azure Log Analytics, Splunk and Elastic.
Thank you to everyone investigating, sharing feedback and helping us improve the platform! 🙏
𝗧𝗛𝗟 𝗩𝟮 𝗼𝗻 𝘁𝗵𝗲 𝘄𝗮𝘆:
There’s a lot more coming. We’re planning a major v2 release with new capabilities and features that we think will blow your mind. We can’t wait to show you what we’ve been building.
Explore the labs and get access:
- https://t.co/1KoDtZa6Gr
⏳ Last call: the DFIR Labs Digital Forensics Challenge kicks off tomorrow.
4 hours, one real intrusion, 20+ questions, live support in our Discord, and a shot at joining The DFIR Report as a volunteer analyst. Splunk or Elastic, your call.
It's not too late, sign up now 👉 https://t.co/m8klSdJHE2
The first public Threat Hunting League competition starts this Friday.
You’ll have a four-hour personal lab run to investigate an Iranian APT campaign using Splunk, Elastic or Azure Log Analytics.
Registration closes Thursday, September 24. Entry is $15 or 12 THL credits, and all skill levels are welcome.
Register: https://t.co/WcZ3aIKfpz
One thing we experimented with in “The Recurring Impostor” was adding video walkthroughs for every question.
You investigate first, submit your answer, and then you can watch us walk through how we approached the same problem and arrived at the solution.
We received a lot of useful feedback on this, and we’re happy to say the videos are here to stay! 🥳
We’ll be making a few small changes, but walkthroughs like these will become part of our labs going forward.
We want Threat Hunting Labs to be more than hands-on practice. The goal is to also give you the learning material behind the investigation and explain how we think through the evidence ourselves.
And if you want a challenge for this weekend and you haven’t tried it yet, “The Recurring Impostor” is still free featuring our amazing partners, Hunt io.
https://t.co/UV8n8qKmZE
@Kostastsale@ippsec All certs and courses ultimately are what you make of them. I have concerns for entry/juniors in today’s world where you don’t need to really “learn” or do deep work to achieve a badge. “Try harder” was a corny and annoying motto to spam but there is truth to learning that way.
New things coming to, or now on, TryHackMe:
🎮 3D Learning Experiences: a more realistic & efficient way to learn
🗣️ Live Classes: instructor-led workshops delivered by experts
🏢 Live Breach Simulation Exercises: realistic, hands-on, IR training
📟 New profile page: fresh design and artwork customisation
📱 Mobile updates: improvements
📛 New certification: PT2, IR1
🚪 New content: Agentic AI Security, Incident Response Content & More
🛜 New networks: 4-5 new rooms with network environments
🐞 Many bug fixes: platform QoL updates + Window VM & VPN improvements
🤲 Study group test: new way to collaborate and learn together
We’ve tightened how investigation searches work across Threat Hunting Labs.
Searches now stay within the verified evidence window for each investigation, helping you quickly see the date time related to each lab. We also improved the time picker that will allow you to more easily choose the time you want to include in your search console.
This applies across Azure Log Analytics, Splunk and Elastic using the THL search console.
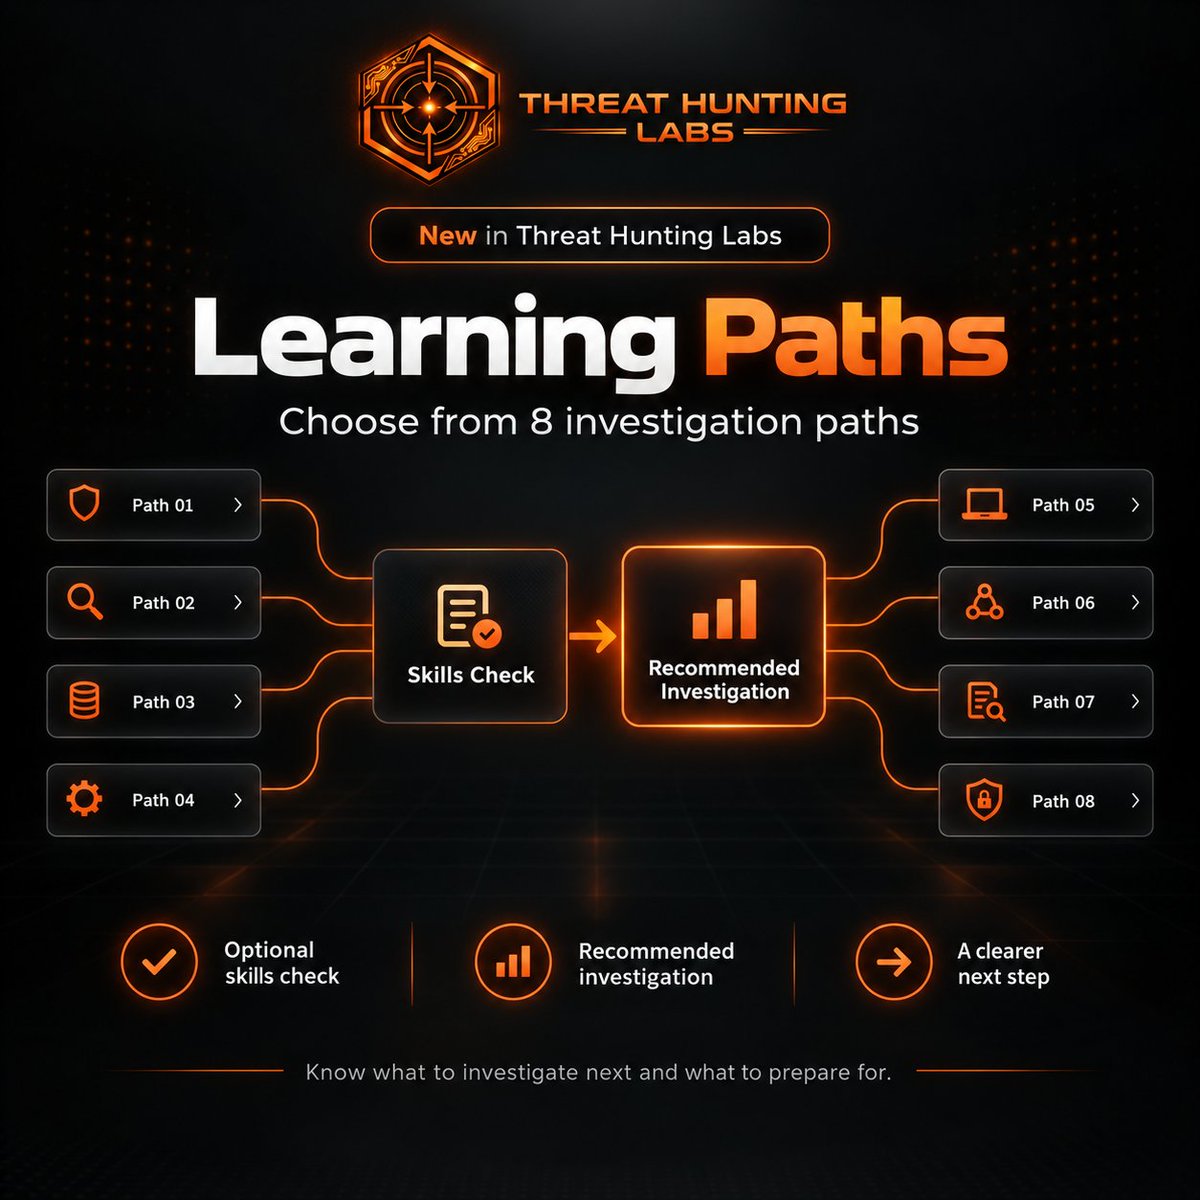
We’ve added Learning Paths to Threat Hunting Labs!
Choose from eight investigation paths, complete an optional skills check, and get a recommended investigation based on your experience and progress.
A clearer way to decide what to investigate next and what to prepare for.
Link: https://t.co/Fk1vuDVr1f
We wanted to celebrate the milestones we’ve hit at Threat Hunting Labs by giving a bit more back to the community with this next release.
We’re very excited to be collaborating with @Huntio, and this time hunt io is actually part of the investigation.
Some of the questions in the new lab will require you to pivot into their platform and hunt through the infrastructure yourself. hunt io has also generously provided 45 days of free access to everyone who starts the investigation through our exclusive link.
From our side:
• The lab is completely free for the first 15 days after you start it, using Azure Log Analytics.
• For the first time, we’re releasing narrated video walkthroughs for the investigation.
• After answering, you’ll be able to watch how we approached the same hunt, what we looked for, and how we reached the answer.
We want walkthroughs like this to become a regular part of Threat Hunting Labs going forward.
A big thank you to hunt io for making this possible and helping us give something back to the community. Sign-up or sign-in and access the lab for FREE using the link below!
https://t.co/IGXWGBgbVX
Today we uploaded the entire blog archive from 2020 to present, excluding a few severely outdated posts. Most of these are notifications of new books, magazines, and podcasts, but there may be some minor value buried in there somewhere. Full details at https://t.co/L5jfsCxyMI
We’re adding something big to the upcoming competition: a complete video walkthrough of the investigation 🎥
Every participant will get access to the walkthrough after the event, including the answers to the questions, along with a full report, 50+ questions, and plenty of hints along the way.
Less than a month left. Come to compete, or take your time and use the whole thing as a learning exercise.
We’re very excited to announce who we’re collaborating with on the walkthrough soon.
Secure your spot:
https://t.co/WcZ3aIKfpz
New Advanced Emulation is live: 𝗟𝗮𝘇𝗮𝗿𝘂𝘀 𝗔𝗣𝗧: 𝗠𝗮𝗹𝗶𝗰𝗶𝗼𝘂𝘀 𝗜𝗻𝘀𝗶𝗱𝗲𝗿.
We spent a lot of time emulating Lazarus APT TTPs for this investigation, taking inspiration from job-lure operations such as Operation Dream Job.
It starts with a fake recruiting assessment on a developer workstation and develops into an investigation spanning Windows and Linux systems, endpoint and network telemetry, evidence preservation, containment, and detection coverage.
70 questions:
26 Threat Hunting
29 Incident Response
15 Detection Engineering
Available now for Pro and Enterprise.
https://t.co/wCaW373EkM
Small but important change to how certificates work at Threat Hunting Labs.
Previously, you needed to score around 70% on each individual track to qualify for a certificate.
We’ve changed this to make things fairer. You’re now eligible when your 𝗮𝘃𝗲𝗿𝗮𝗴𝗲 𝘀𝗰𝗼𝗿𝗲 𝗮𝗰𝗿𝗼𝘀𝘀 𝗮𝗹𝗹 𝗰𝗼𝗺𝗽𝗹𝗲𝘁𝗲𝗱 𝘁𝗿𝗮𝗰𝗸𝘀 𝗶𝘀 𝗮𝗯𝗼𝘃𝗲 𝟳𝟬%.
A weaker result on one track shouldn’t cancel out strong performance across the rest of the investigation. Go claim your certificate!
New Hunt Lead is live: 𝗙𝗿𝗼𝗺 𝗖𝗹𝗶𝗰𝗸𝗙𝗶𝘅 𝘁𝗼 𝗔𝗺𝗼𝘀 𝗦𝘁𝗲𝗮𝗹𝗲𝗿.
We would like to share this macOS intrusion that started with a developer workstation, a fake Homebrew page, and a ClickFix command pasted into Terminal.
From there you’ll hunt through LaunchDaemon persistence, archive transfers, and a later Chrome cookie workflow using full telemetry:
* Elastic Endpoint
* macOS Endpoint Security Framework
* Network logs (Zeek)
* Correlated EDR and Suricata detections
The whole investigation is 𝗳𝗿𝗲𝗲 𝗳𝗼𝗿 𝗲𝘃𝗲𝗿𝘆𝗼𝗻𝗲. You just need an account.
Subscribers also get our full written analysis, including some of the activity that isn’t obvious from process telemetry alone.
https://t.co/XjatfLCCCb