software engineering craftsmanship is dying in front of our eyes. writing beautiful code, a nicely crafted library, or designed framework do not matter anymore. there will be nobody that appreciates the code, nobody even understanding it. is the status quo now frozen or what is the incentive to go the extra mile to create the next beautiful library?
📍CIBERATAQUE A LA INFRAESTRUCTURA CRITICA PETROLERA ARGENTINA📍Ayer la empresa Oldelval, operadora de los ductos claves de "Vaca Muerta", informo por nota a la Comisión de la Bolsa de Valores, que recibió un "ciberataque" o "incidente de seguridad informática" a sus sistemas administrativos. Esta firma administra una red de oleoductos de 1700 kms y transporta el 90% de la producción de los yacimientos de Vaca Muerta hasta Bahia Blanca. Son sus clientes YPF, Chevron, Shell, Pampa Energía y Vista Energy, entre otras empresas. Este tipo de incidentes demuestra una vez mas la vulnerabilidad de la infraestructura energética de Argentina. El ciberataque no parece tener móviles económicos como el ransonware y se desconoce hasta aquí las motivaciones; por ello no se debe perder de vista que la infraestructura atacada bien pudo resultar "un polígono de tiro", para adquirir y demostrar habilidades por parte de los hackers.
En octubre se viene una nueva edición del Hacking Day en Paraná (Entre Ríos).
Puedes ver lo que fue el año pasado y ya reservarte la fecha o SER SPONSOR.
💻https://t.co/BzmValfKhY
Habrá CHARLAS, CTF Y TALLERES GRATUITOS.
Pronto también abriremos la inscripción!
Tu celular recibe una secuencia emocional diferente, calculada a partir de tus reacciones.
El mecanismo funciona de manera personalizada sobre cada celular.
Cada vez que una persona usa su teléfono deja señales: qué publicaciones mira, cuánto tiempo se detiene en una imagen, qué videos abandona, cuáles vuelve a ver, qué comenta, qué comparte, a quién bloquea, qué busca, a qué hora se conecta e incluso qué palabras escribe y después borra.
Esas señales permiten construir un perfil dinámico de sus intereses, sus hábitos y sus reacciones emocionales. El sistema no necesita conocer profundamente a la persona ni comprender lo que siente. Le alcanza con detectar regularidades: este contenido la enoja, este la asusta, este confirma sus prejuicios, este la tranquiliza y este consigue que permanezca más tiempo frente a la pantalla.
A partir de allí comienza una experimentación permanente. El algoritmo muestra distintas publicaciones, titulares, imágenes o videos y mide la respuesta. Si un contenido provoca una reacción intensa, ofrece otros similares. Si no genera interés, lo reemplaza. El celular se transforma así en un laboratorio individual donde cada usuario recibe una combinación distinta de estímulos.
Dos personas que viven en la misma ciudad, trabajan juntas y creen estar observando la misma realidad pueden recibir mundos informativos completamente diferentes. Una verá mensajes destinados a despertar miedo; otra, contenidos que alimentan indignación; otra, publicaciones que refuerzan frustraciones o resentimientos previos.
La eficacia del mecanismo reside en su repetición. Ningún mensaje aislado necesita modificar una opinión. Pero cientos de estímulos seleccionados, distribuidos durante semanas o meses y adaptados a la reacción de cada usuario pueden alterar gradualmente aquello que considera verdadero, urgente, peligroso o deseable.
El teléfono no obliga a pensar de una determinada manera. Hace algo más sutil: organiza el entorno emocional desde el cual la persona interpreta los hechos y toma decisiones.
Por eso la manipulación contemporánea no consiste solamente en difundir una mentira. Consiste en elegir qué emoción activar en cada individuo, en qué momento hacerlo y cuántas veces repetir el estímulo hasta que esa emoción parezca haber nacido espontáneamente dentro de él.
Si alguien duda del poder del algoritmo para cambiar opiniones, recordales que hicieron de Messi un villano. DE MESSI, el mejor jugador de la historia. En un mundo sin pensamiento crítico, estaremos perdidos.
🇦🇷 The hate against Messi came out of nowhere, and it has nothing to do with football.
Here's what's actually going on...
Messi lifted the World Cup in December 2022 and the entire planet lost its mind celebrating.
Three and a half years later, a chunk of the internet suddenly decided he's a villain.
Nothing on the pitch changed. Same guy, same career, twenty years of footage anyone can check in under a minute.
What changed is the feed. Villain edits started outperforming legend edits and the algorithm noticed.
A 2018 MIT study tracked 126,000 claims across 3 million X users. False stories spread six times faster than true ones and got retweeted 70% more often. Outrage simply beats accuracy at getting attention.
None of this needs a single big lie either. Illusory truth effect: see a claim enough times and it starts feeling true even when you know it's false, and the effect survives fact checks.
Football is basically the most documented thing on earth. Every match, every angle, every ref decision, all archived. The narrative still won anyway.
If the algorithm can flip public opinion on the most watched athlete alive, it can flip it on anyone with no footage to fall back on.
Source: @LeoMessiFanZone, @therosieum / Writer: Sol
Update al update ahora con CVE-2026-60137 y CVE-2026-63030
ACTUALIZA YA tu Wordpress a 6.8.6, 6.9.5, o 7.0.2
La vulnerabilidad es crítica y no necesita autenticación para su explotación.
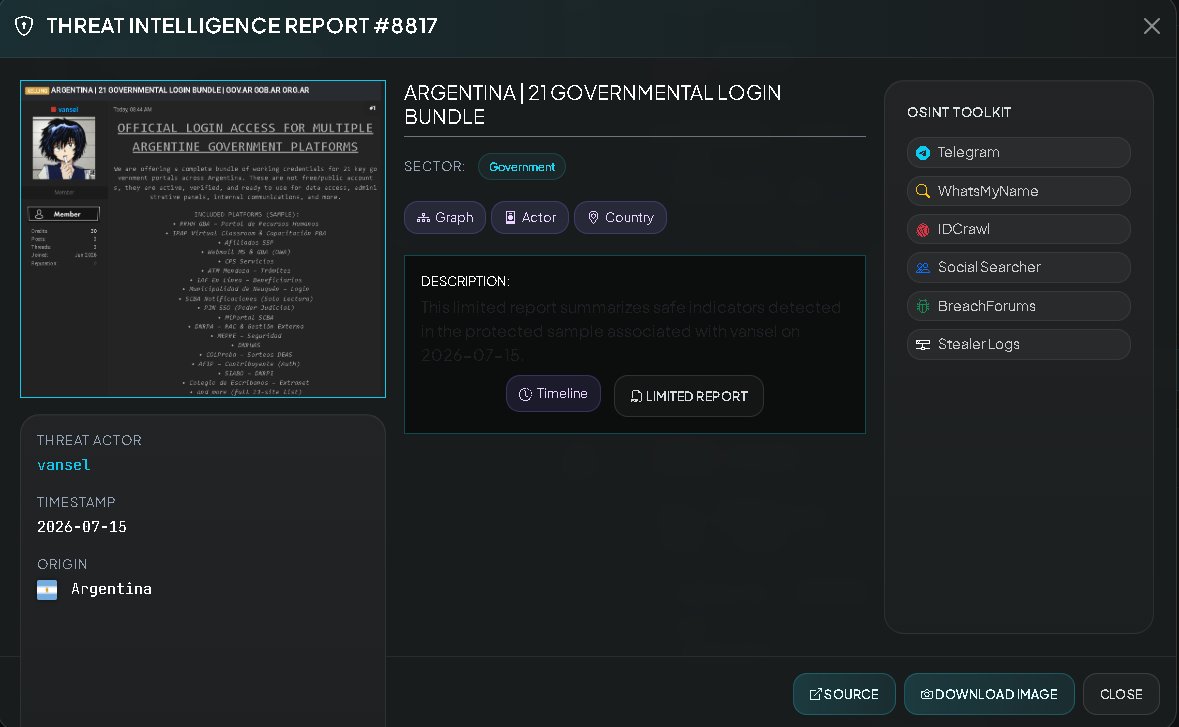
🇦🇷 [https://t.co/kfN7QgBhTS / https://t.co/yRlyZrmREK / https://t.co/diLRjQFC0e / AFIP / PJN] 🚨 🔑 CYBER INTELLIGENCE ALERT / ALLEGED SALE OF GOVERNMENT ACCESS IN BATCHES — ARGENTINA
[STATUS: UNCONFIRMED / INITIAL ACCESS BROKER / SOURCE: UNDERGROUND FORUM / DATE: JULY 15, 2026]
THE ACTOR "VANSEL" (SOULHEMTEAM) IS SELLING A BATCH OF ACTIVE CREDENTIALS THAT COMPROMISE 21 KEY PUBLIC AND LEGAL PORTALS AND INFRASTRUCTURES IN ARGENTINA
Through passive monitoring of cybercrime forums and channels specializing in the distribution of Initial Access credentials, a commercial offer has been intercepted that represents a risk. Systemic vulnerability affecting the public administration, judiciary, and tax system in Argentina.
The attacker claims that these credentials do not correspond to publicly accessible or free-to-use accounts, but rather are legitimate administrative-level access credentials obtained through internal persistence channels, guaranteeing a minimum activity period of 30 days.
🗂️ BREAKDOWN OF THE MAIN ENTITIES AND PLATFORMS
The access cache encompasses tax control agencies, property registries, judicial infrastructure, and internal communication services across various jurisdictions in the country:
1. Tax and Identity Control Sector (High Impact)
AFIP – Taxpayer (Auth): Access to profiles of the Federal Administration of Public Revenue, allowing the viewing of protected tax data, invoices, and taxpayer returns.
ATM Mendoza – Procedures: Access to the Mendoza Tax Administration portal for managing provincial taxes, property records, and citizen accounts.
DNRPA – RAC & External Management: Access to the National Directorate of Automotive Property and Chattel Mortgage Registries, allowing the consultation and processing of vehicle ownership data nationwide.
2. Judicial Branch Infrastructure (Risk of Intrusion and Espionage)
PJN SSO (National Judicial Branch): Credentials for the single sign-on system of the federal courts, with the potential to view files, notifications, and confidential resolutions.
SCBA Notifications & MyPortal SCBA: Access linked to the Supreme Court of Justice of the Province of Buenos Aires, allowing the reading of official communications, notifications, and interactions with the judicial portal of the country's largest province.
COLProba – DEAS Draws: Portal of the Buenos Aires Province Bar Association, focused on judicial appointment and draw systems.
3. State Communications and Human Resources
MS & GBA Webmail (OWA): Outlook Web App (OWA) webmail servers of the Ministry of Health (MS) and the Government of the Province of Buenos Aires (GBA), facilitating the reading of internal correspondence and the theft of confidential documents.
HR GBA: Human Resources administration and management portal for the Province of Buenos Aires, exposing personnel files, payroll statements, and personal data of public employees.
IPAP Virtual Classroom (PBA): Training platform of the Provincial Institute of Public Administration of Buenos Aires.
4. Additional Registries and Professional Associations
Notary Association – Extranet: Access to the internal network and procedures for notaries and notaries.
Other agencies: IAF Online (Institute of Financial Aid for Military Retirement and Pension Payments), Municipality of Neuquén, MEPRE (Electric Regulatory Entity), DNRUAS and SIABO-DNRPI.
🛡️ PREVENTIVE TECHNICAL RECOMMENDATIONS FOR CONTAINMENT (SOC / PUBLIC ADMINISTRATION)
Technology managers, IT directors, and security operations centers (SOCs) in the aforementioned jurisdictions and agencies are urged to urgently implement the following guidelines:
🛑 Immediate Session Revocation and Password Reset (Priority Action): Centrally enforce the expiration of all active web sessions and require mandatory password changes for user accounts on the aforementioned portals (especially in the OWA environments of the Government of Buenos Aires, AFIP, and Judicial Branch systems).
🛡️ Mandatory Implementation of Multi-Factor Authentication (MFA): Block access to administrative portals that rely on simple passwords. Mandatory integration of MFA (preferably based on authentication applications with numeric validation or hardware tokens) across all government extranets and management dashboards.
📊 MONITORING
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#CyberSecurity #Argentina #GovAr #AFIP #PoderJudicial #DNRPA #SoulhemTeam #InitialAccess #OWACompromise #DataLeak #ThreatIntelligence #CyberAlert #VECERT #Infosec #UnverifiedIncident
☢️ Argentina quiere volver a producir uranio y convertirlo en una nueva fuente de exportaciones.
📌 35.000 toneladas verificables y recuperables
📌 Sierra Pintada: ~10.000 t de recursos y US$ 500 M de inversión estimada
📌 Cerro Solo: ~8.000 t identificadas
📌 Consumo interno: ~220 t por año
📌 Potencial exportador: hasta US$ 500 M anuales
El plan oficial apunta a sumar proyectos al RIGI, atraer capitales de Canadá y EE.UU. y pasar de importar uranio a desarrollar una plataforma exportadora.
Pero el salto dependerá de remediación ambiental, permisos provinciales, licencia social y reglas claras.
🇦🇷 El uranio vuelve a entrar en la agenda estratégica argentina.
El estudio que avala una hidrovía de 720 kilómetros por los ríos Limay y Negro. El proyecto fue considerado técnicamente viable y plantea una inversión estimada en US$ 580 millones para desarrollar puertos, dragados y un sistema multimodal que reduzca costos logísticos para Vaca Muerta y las economías regionales.
El trabajo técnico —de casi 200 páginas— plantea un sistema capaz de operar durante más del 90% del año y prevé el uso de barcazas de hasta 111 metros de eslora, con embarcaciones que requerirían un gálibo máximo de unos 9 metros para atravesar los puentes existentes.
El proyecto también contempla un canal navegable de aproximadamente 30 metros de ancho, obras de dragado en distintos sectores del río, intervenciones en la desembocadura y adecuaciones sobre infraestructura existente para garantizar una navegación continua.
https://t.co/TQASZLk1P5
🚨 🇦🇷 CYBER INTELLIGENCE ALERT: SECURITY AND DEFENSE SECTOR — ARGENTINA
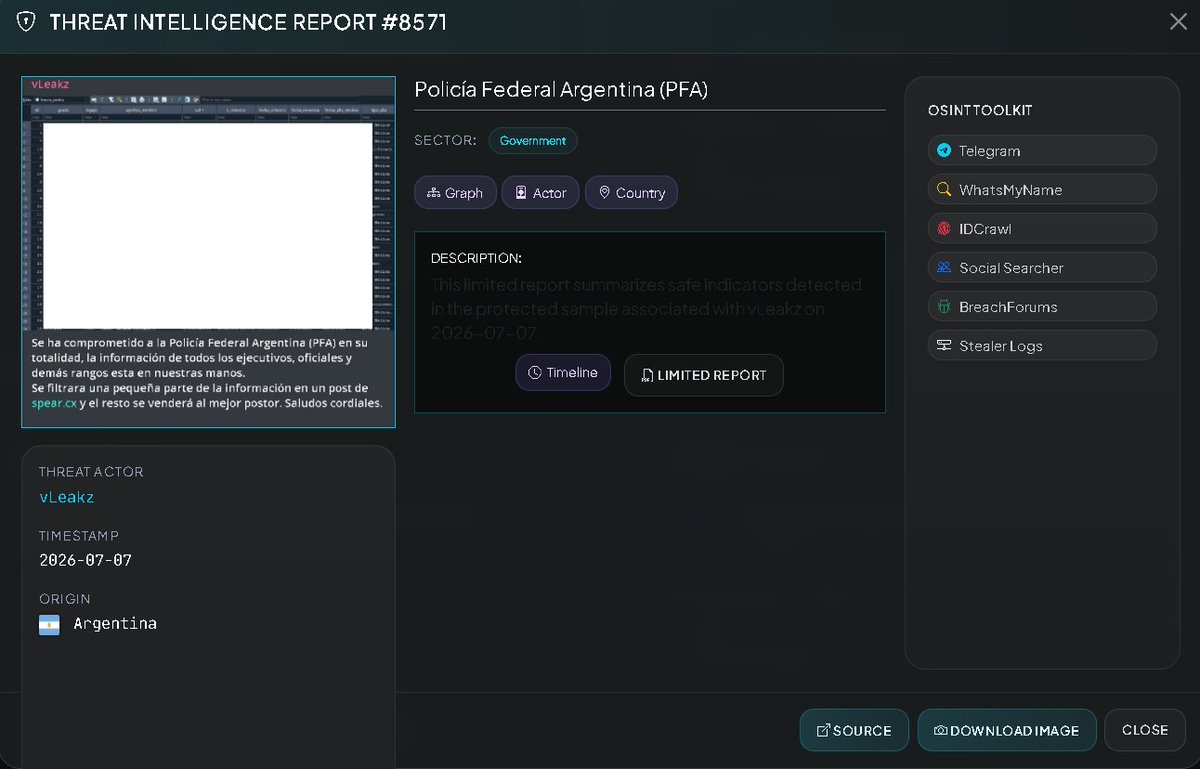
[STATUS: ALLEGED DATA COMPROMISE / UNCONFIRMED, EVIDENCE VISIBLE / SOURCE: TELEGRAM (vLeakz) / DATE: JULY 7, 2026]
THE ACTOR "SQX" CLAIMS EXFILTRATION OF THE ARGENTINE FEDERAL POLICE'S (PFA) OPERATIONAL AND PERSONNEL DATABASE
A direct escalation of attacks against the IT assets of the public security sector in the Southern Cone has been detected. The threat actor using the alias sqx has announced, through its Telegram broadcast channel, the compromise and complete intrusion into databases belonging to the Argentine Federal Police (PFA).
The attacker claims to possess the complete roster of executives, officers, and ranks of the force, openly stating that they will release a proof of concept (PoC) on the clandestine Spear platform.
🏢 Allegedly Affected Entity: Argentine Federal Police (PFA) — Ministry of Security.
👤 Threat Actor: sqx (Associated with the vLeakz/vnsleaks infrastructure).
⚔️ Technical Ecosystem According to the Actor: Relational database (allegedly structured in SQLite according to internal schemas) with tables of personnel files, operational areas, and detailed medical records.
🔍 Verification Status: UNCONFIRMED BY ARGENTINE AUTHORITIES. As of July 7, 2026, the Ministry of Security, the PFA Directorate, or the National Cybersecurity Directorate have not issued any institutional statements regarding a breach or contingency.
🗂️ ANALYSIS OF THE ANATOMY OF DIGITAL COMPROMISE
The leak would directly compromise the governance of data and personnel files of the force:
Exposed Table Structure (Tables (4)):
educational_entity_benefit: Record of benefit categories linked to force personnel.
medical_license: Health database that catalogs identifiers such as ID, rank, file number, last_name_first_name, CUIL (tax ID number), incident_number, incident_date, report_date, medical_discharge_date, discharge_type, and the physical unit of assignment.
personnel: The core PFA (Argentine Federal Police) personnel registry, structured with the fields ID, last_name, first_name, file number, and specific tactical deployment area.
Optimistic Fast Search Indices: Indexes such as idx_lic_legajo and idx_personal_legajo are detailed, demonstrating that the database was designed for quick cross-corporate searches.
🛡️ PREVENTIVE TECHNICAL RECOMMENDATIONS FOR CONTAINMENT (SOC/DEFENSE)
Argentine public sector incident response teams are urged to implement immediate defensive mitigation measures:
🛑 Identify Leaks in Human Resources and CIPRES/Health Applications: Trace API calls, web accesses, and bulk exports that occurred in the logical databases of occupational medicine or personnel files systems of the Argentine Federal Police (PFA) in recent weeks. Revoke compromised credentials and session tokens globally.
🔑 Segregation of Security Personnel Records: Completely isolate personnel files and tactical assignment servers from any network exposed to the public internet. All authorized queries must be processed in encrypted form over private internal networks and monitored by perimeter SIEM systems.
📊 THREAT MONITORING AND ASSESSMENT
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#CyberSecurity #Argentina #PFA #FederalPolice #vLeakz #DataLeak #Sqx #PoliceFiles #MedicalLicense #Doxing #ThreatIntelligence #CyberAlert #VECERT #Infosec #UnverifiedIncident
🚨 🇦🇷 CYBER INTELLIGENCE ALERT FOR THE HEALTH SECTOR — ARGENTINA
[STATUS: ALLEGED / HIGH-IMPACT CAMPAIGN / UNCONFIRMED SOURCE: INTELLIGENCE PLATFORMS / DATE: JULY 6, 2026]
THE "CHRONUSTEAM" GROUP CLAIMS MASSIVE INTRUSION AND COMPROMISE IN 50 UNION AND PROVINCIAL HEALTH INSURANCE PROVIDERS
Through technical monitoring of criminal environments, an alert has been issued regarding one of the exfiltration attacks on the health system in Argentina. The leaking group known as CHRONUSTEAM claims to have simultaneously compromised the systems of 50 health insurance providers across the country (including union, national, and corporate mutual insurance funds, and almost all provincial medical institutes).
🏢 Allegedly Affected Entities: 50 medical and social security institutions, including: the social welfare organizations of the Light and Power Workers Union, YPF (the state-owned oil company), the Oil Workers Union, the Senior Staff Union, the Truck Drivers Union, the Metalworkers Union (UOM), the Banking Union, the Army (IOSE), OSPA (the provincial social welfare organization), Incluir Salud (PROFE), Osplad (the provincial social welfare organization), and the provincial social welfare organizations of La Pampa (SEMPRE), Formosa, Tierra del Fuego (IPAUSS), San Luis (DOSEP), Santa Cruz, San Juan, Río Negro (IPROSS), Jujuy (ISJ), Santiago del Estero (IOSEP), Corrientes (IOSCOR), Chubut (SEROS), Catamarca (OSEP), Neuquén (ISSN), Misiones (IPS), Entre Ríos (IOSPER), the City of Buenos Aires, and Salta (IPS).
👤 Threat Actor: CHRONUSTEAM.
⚔️ Data Ecosystem at Extreme Risk: Medical records, contributor affiliation records, medical billing data, prescriptions, member numbers, and personal information (PII).
🔍 Verification Status: NOT CONFIRMED BY ENTITIES IN ARGENTINA. As of July 6, 2026, the Superintendency of Health Services, provincial governments, or the corporate cybersecurity committees of the listed health insurance providers have not issued official statements acknowledging a chain intrusion. However, the alert is being processed under a national alert.
🛡️ PREVENTIVE TECHNICAL RECOMMENDATIONS FOR CONTAINMENT (SOC / INCIDENT RESPONSE)
The infrastructure departments and security directors of the affected Argentine social security organizations are urged to deploy an immediate contingency plan in response to this chain of threats:
🛑 Audit of Software Providers and Shared APIs: Due to the simultaneous nature of the report, it is recommended to forensically audit connections with external providers of medical clearing, online prescription validation, and integrated registry systems, isolating any compromised interfaces.
🔑 Session Invalidation and MFA Deployment: Force the closure of all active sessions on provider administration platforms and extranets. Mandatory implementation of Multi-Factor Authentication (MFA) to prevent the misuse of exposed administrative credentials.
📊 MONITORING AND EVALUATION
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#CyberSecurity #Argentina #ArgentineHealth #HealthInsurance #ChronusTeam #DataLeak #SuperintendenceOfHealth #ProvincialHealthInsurance #DataBreak #ThreatIntelligence #CyberAlert #VECERT #Infosec #UnverifiedIncident
🚨 🌐 🇦🇷 🇧🇷 🇨🇴 🇧🇴 🇪🇨 🇪🇸 🇵🇹 🇲🇾 🇺🇦 🇮🇹 🇹🇳 🇹🇭 🇳🇬 🇺🇸 🇬🇧 🇩🇲 🇧🇦 🇬🇹 🇩🇪 🇸🇧 🇸🇬 🇦🇹 🇺🇦 🇨🇦 🇱🇻 🇰🇪 🇰🇭 🇱🇷 🇹🇴 🇿🇦CRITICAL CYBER INTELLIGENCE ALERT / MASS DEFACEMENT CAMPAIGN: GLOBAL GOVERNMENT SECTOR 🌐
[STATUS: MASS PERIMETER COMPROMISE / ACTIVE MALICIOUS FILE INJECTION / GOVERNMENT ENVIRONMENT / DATE: JULY 4, 2026]
THE "TRENGGALEK CYBER ARMY" GROUP IS LAUNCHING A MASSIVE OFFENSIVE AGAINST .GOV/.GOB PORTALS BY EXPLOITING CMS ARCHITECTURES
Through passive monitoring, a priority alert has been issued regarding a massive, automated defacement campaign. This is based on consolidated logical logs and recorded visual telemetry. The threat group identified as Trenggalek Cyber Army claims to have simultaneously compromised dozens of official websites belonging to public administrations, ministries, security forces, and municipalities in multiple countries.
The attack was carried out in a concentrated manner during the final hours of July 4, 2026, systematically injecting the malicious file cox.json (and variations such as cox.svg) into the root directories and templates of the affected servers.
🏢 Affected Entities: Institutional web infrastructure of governments in Argentina, Brazil, Colombia, Bolivia, Ecuador, Spain, Portugal, Malaysia, Ukraine, Italy, Tunisia, Thailand, and Nigeria, among others.
👤 Threat Actor / Attribution: Trenggalek Cyber Army.
⚔️ Technical Vector: Mass exploitation of known or zero-day vulnerabilities in the Content Management System (CMS) layer (such as Joomla), complemented by weaknesses in file upload validation (Arbitrary File Upload) in outdated extensions or plugins.
🗂️ REGIONAL IMPACT ANALYSIS AND TAXONOMY OF COMPROMISE
The campaign has significantly impacted the digital periphery of public agencies and global critical infrastructure, highlighting the following listed and consolidated targets:
🇦🇷 Southern Cone (Argentina and Bolivia)
https://t.co/kdAk4jCCJv: Official website of the Buenos Aires Province Police Retirement Fund (Argentina).
https://t.co/FLy3QSR8kW and https://t.co/YTOnBnhi6P: municipal portals of Buenos Aires and Santa Fe (Argentina).
https://t.co/9Izgkeo08q: Bolivian Mining Corporation (COMIBOL).
🇧🇷 Critical Impact on the Brazilian Public Network
https://t.co/0JzubWNN6O: Comptroller General of the State of Minas Gerais.
https://t.co/ZhL61vckxT, https://t.co/pWvaV6f04M, https://t.co/AuxFEoDuLN: municipal councils and prefectures of the state of Minas Gerais.
https://t.co/84KAhoOWza and https://t.co/AdpOkqaS27: websites of the local legislative assemblies of Piauí and Rio Grande do Sul.
https://t.co/ivRdqnhup1: School of Nursing of the Federal University of Minas Gerais.
🇨🇴 Andean Region (Colombia and Ecuador)
https://t.co/IuAqlRhLb3: Logistics portal of the Buenaventura Transportation Terminal (Colombia).
https://t.co/GxW17p0cQi: Infrastructure of the State Social Enterprise (E.S.E.) of La Unión - Sucre (Colombia).
https://t.co/uj21LWnW7w and https://t.co/EoNM7u0K3J: Portals of the Decentralized Autonomous Governments (GADs) of the municipalities in Ecuador.
🇪🇺 Europe and Rest of the World (Spain, Portugal, Malaysia, Italy)
https://t.co/cqONdKok5n: Image subdirectory of the Higher Center for Sports Education of the Spanish National Sports Council.
https://t.co/pdaJCxk7EE: Commitment of the National Commission for Combating Food Waste in Portugal.
https://t.co/L8IqSdTnky and https://t.co/4LhPs4xkVv: National Pharmaceutical Regulatory Agency and state agencies in Malaysia.
https://t.co/RMdq9nQHgf: NHS (National Health Service) of the United Kingdom.
⚠️ RISK ANALYSIS: FROM DEFACTURE TO WEBSHELL AND CREDENTIAL THEFT
Although defacement attacks are traditionally perceived as low-impact incidents of digital vandalism, the persistence of this campaign introduces advanced risks:
👤 Persistence through Hidden Web Shells: The injected .json or .svg file is usually just the public signature of the attack. Behind the scenes of CMS exploitation, the attacker commonly plants malicious remote administration scripts (Web Shells). This grants them persistent access to government servers, allowing for the future exfiltration of internal databases or lateral movement into internal government networks.
💳 Phishing Code Injection and Search Engine Poisoning (SEO): By gaining control over website templates, attackers can alter the code to redirect citizens seeking official services to fake payment gateways, capturing banking information or identity credentials. Malicious links also degrade the search engine ranking of government websites.
🛡️ PREVENTIVE TECHNICAL RECOMMENDATIONS FOR CONTAINMENT (SOC / INCIDENT RESPONSE)
Government entities' IT departments are urged to implement immediate perimeter mitigation protocols:
🛑 Forensic Isolation and Identification of Anomalous Files (cox.json): Perform immediate recursive searches in the root directories and design folders of web servers (/templates/, /images/, /public/) to locate and permanently purge files with the name pattern cox.json, cox.svg, or similar, created on July 4, 2026.
🔑 Auditing and Deactivation of CMS Extensions and Plugins: Review update logs in CMS platforms (Joomla, etc.). It is recommended to immediately update the platform's core and all active plugins. Disable unverified third-party file upload plugins that served as an entry vector for the injection.
📊 MONITORING AND EVALUATION
Intelligence System: https://t.co/wk9bZJ2Nli
#CyberSecurity #GlobalDefacement #TrenggalekCyberArmy #CajaPolicia #CGE #Miranda #Sicep #SeekerParking #CMSExploit #JoomlaVulnerability #WordPressVulnerability #CoxJson #ThreatIntelligence #CyberAlert #VECERT #Infosec #UnverifiedIncident