🔊 Become a Speaker at #TheSAS2024.
🌐 We're seeking experts on cyberthreats, IoT security, ransomware, and even cyber-hacks in space 🌌
Submit your topic by August 1, 2024 ▶️ https://t.co/jPe9CuYuFq
Apply now to share your insights and shape the future of cybersecurity with us.
We discovered a new zero-day in Microsoft Windows used in attacks with QakBot and other malware. It was just fixed as CVE-2024-30051, and this time it all started with a curious find on VirusTotal… @r00tten https://t.co/ZRq8pw7gpy
This year we are organizing the SAS CTF with VERY fun reverse engineering challenges and the top teams/players will fly to the Security Analyst Summit (@TheSAScon) to compete for $18,000 in prizes. Register now! https://t.co/UB4Z3S5SHg
Great news! As a contribution to the opensource community, we have already provided training opportunities in our "#Suricata for Incident Response and Threat Hunting" training (https://t.co/7wnMLjS7L0) for several @outreachy Suricata interns, and we have decided to offer more free seats to anyone interested in writing Suricata rules! If you want to meet real-life cases and learn how to write and implement Suricata rules to detect and block even the most advanced threats, send a motivation letter to Suricata.xTraining[at]https://t.co/0bd5SPhU15 explaining why you need this opportunity and how it can help you to boost your career. Together with the xTraining team, I will select three applications and provide free access to the full training. And those who will be not selected will receive a discount for the training :) The deadline for submissions is March 1.
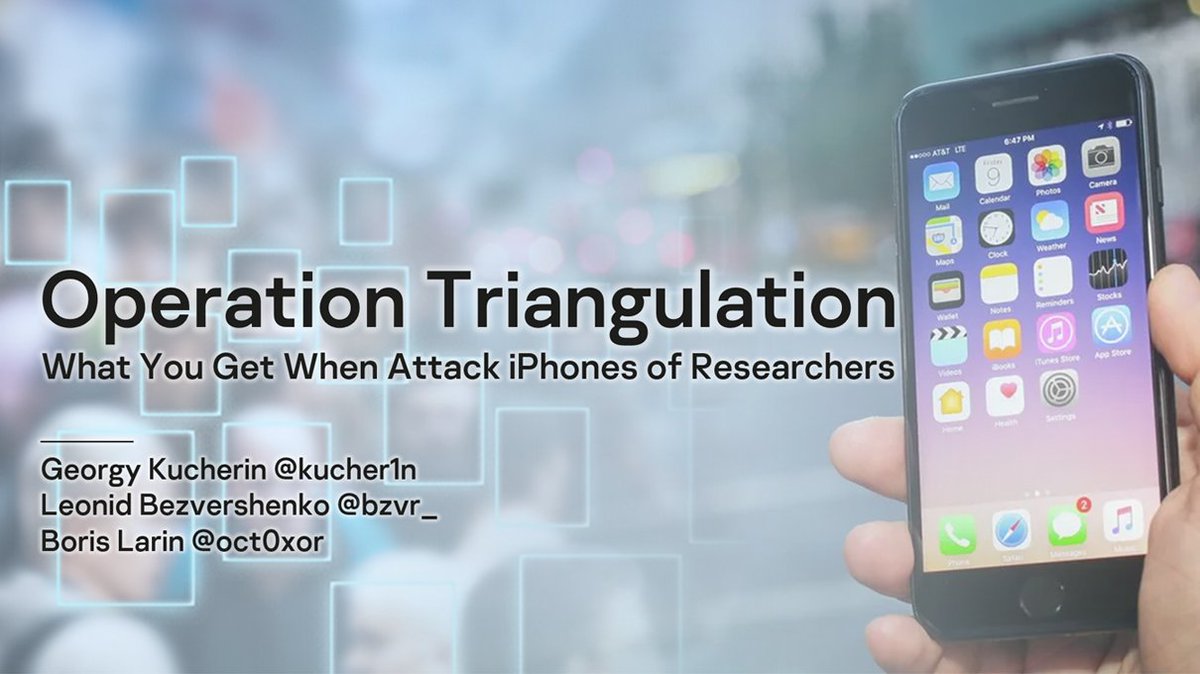
"Operation Triangulation"
https://t.co/DUBBQWPqTS
A newly discovered spyware campaign targeting Apple iPhone using a zero-click remote code execution via an attack chain of 4 zero-days, including highly mysterious, completely undocumented MMIO registers and hardware features that are not even ever used by the firmware.
TLDR the attack begins with an iMessage to an arbitrary phone that, without any user action and invisibly, gets it to collect and upload tons of private data (and much more, e.g. microphone recordings) from there on, and actively takes steps to hide all of this activity from the user and aspiring forensic researchers. Apple has patched the core vulnerability on Oct 25, 2023.
"This is definitely the most sophisticated attack chain we have ever seen"
The talk itself, a lot more wild information there:
https://t.co/eTEeltBMpD
The author of this attack is unknown, as is the method by which they gained knowledge of these unused, undocumented hardware features. Russia's intelligence service accused Apple of providing the NSA with a backdoor.
For a more general audience intro to this underworld I usually recommend the book "Countdown to Zero Day".
We're revealing details of an obscure debugging feature in the Apple A12-A16 SoC’s that bypasses all of the hard-to-hack hardware-based memory protections on new iPhones. Its not used by the firmware and we don't know how the attackers found out about it. https://t.co/hsQo6JIPMJ
All the details about this vuln and much more will be revealed tomorrow by us (me, @bzvr_, @kucher1n) during our talk “Operation Triangulation: What You Get When Attack iPhones of Researchers” at #37c3 (14:45 CET). There will also be a live stream. https://t.co/g5cQLf6za4
A little earlier, I found Windows CLFS 0-day used in ransomware attacks. But at that time, I've been tracking this actor for a year and they used 5(!) different CLFS exploits. Is there something seriously wrong with Windows CLFS? I decided to investigate. https://t.co/wgo9cxAc3w
Imagine discovering a 0-click attack targeting iPhones of your colleagues and managing to capture four 0-days and a spyware with mind-blowing 🤯 capabilities. I, @bzvr_ and @kucher1n will tell you everything about “Operation Triangulation” at #37c3 https://t.co/FNIozbSDMC
Global cybersecurity giant @kaspersky has set up a transparency centre in Kigali – the first of its kind on the African market
Read: https://t.co/2Ew1ul7LSC
NEW: Kaspersky releases full details on how they captured the “Triangulation” (suspected US Government) exploits and iPhone spyware targeting their employees. https://t.co/Krladw07eD
#thesas2023 was also remarkable because of the final reveal #OperationTriangulation analysis. Several months of great work, 4 (!!!) #zeroday exploits. Our new report is here https://t.co/kYdlwkjoud