This is another medium to announce one again that I am a Tech Content Creator and for those who wants to promote their products, services or something you want Offshield Security @offshield_ai to partake on, kindly reach out or refer me .
Make Eni no talk say I dey lazy abeg 💪😅 Thank you.
@_DeejustDee@TheCloudSE@jay_hunts@RootHawk_@ko_ceeherself@KoredeSec
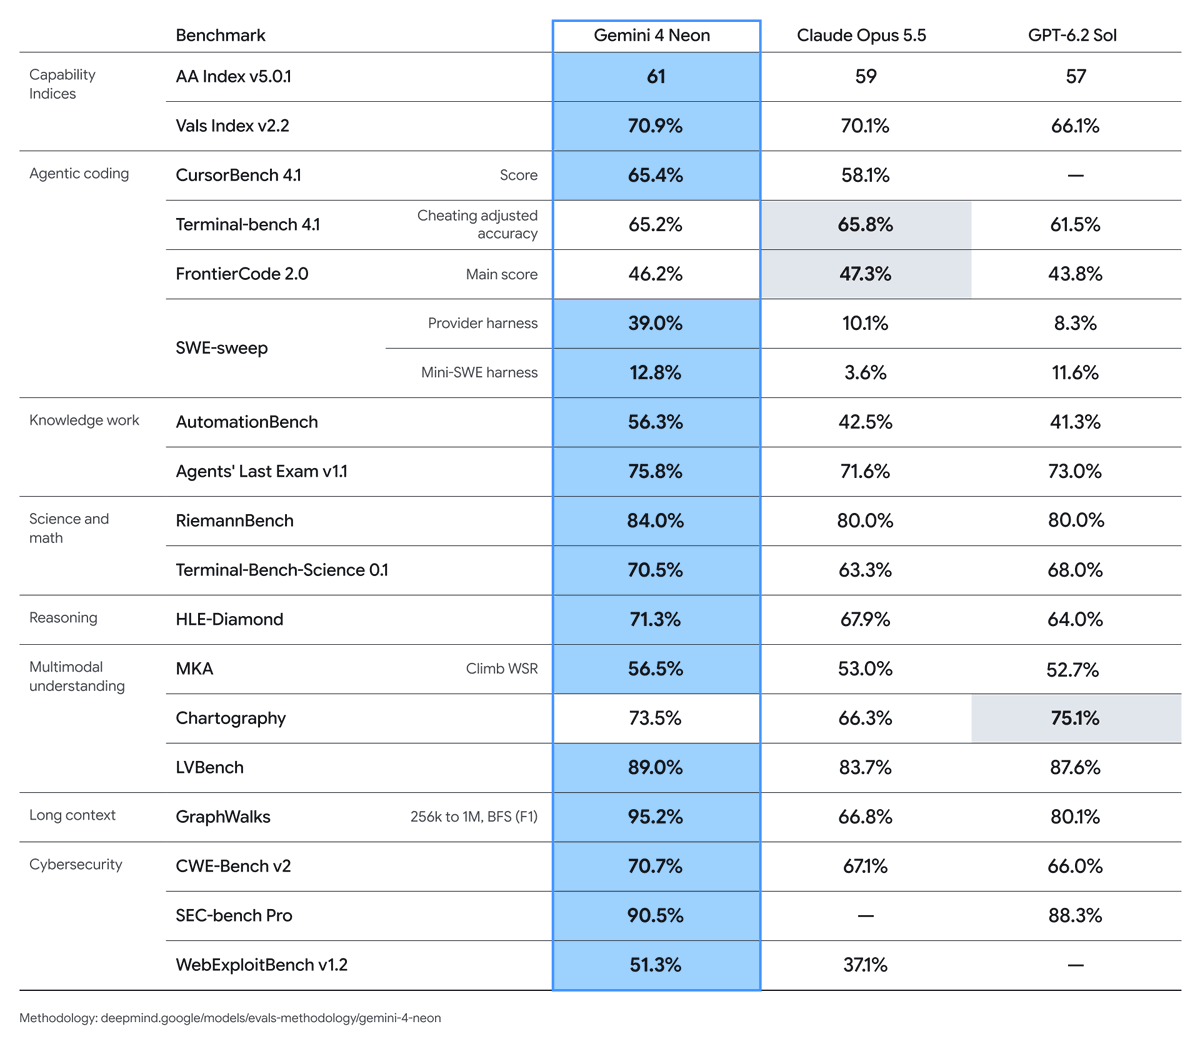
Gemini 4 Neon: frontier-level intelligence with fast end-to-end task completion across complex software engineering, knowledge work, and science workflows.
Begins rolling out today in the Gemini API in @GoogleAIStudio, Gemini for business, for paid Google AI Pro and Ultra subscribers in Google @Antigravity, and for Google AI Pro and Ultra subscribers in the @GeminiApp.
Had a conversation with someone today who practically mirrored me. BSc in Cybersecurity, young, ridiculously ambitious, very cracked and an absolute goal getter.
Honestly, one of the best conversations I’ve had in a minute.
A lot of things I’ve had in my head, things I barely talk about with people, were being echoed and validated in that conversation. It gave me even more clarity on the importance of surrounding yourself with people who are just as driven, if not more driven than you are.
You need cracked friends. People who make ambition feel normal. People who constantly expand your perspective and challenge you to do more.
Because you can be chilling, thinking you’re doing well, and then hear that your guy just landed a role at EY or some unicorn, shipped something crazy, or hit another milestone.
You have no choice but to raise your own game. 😂
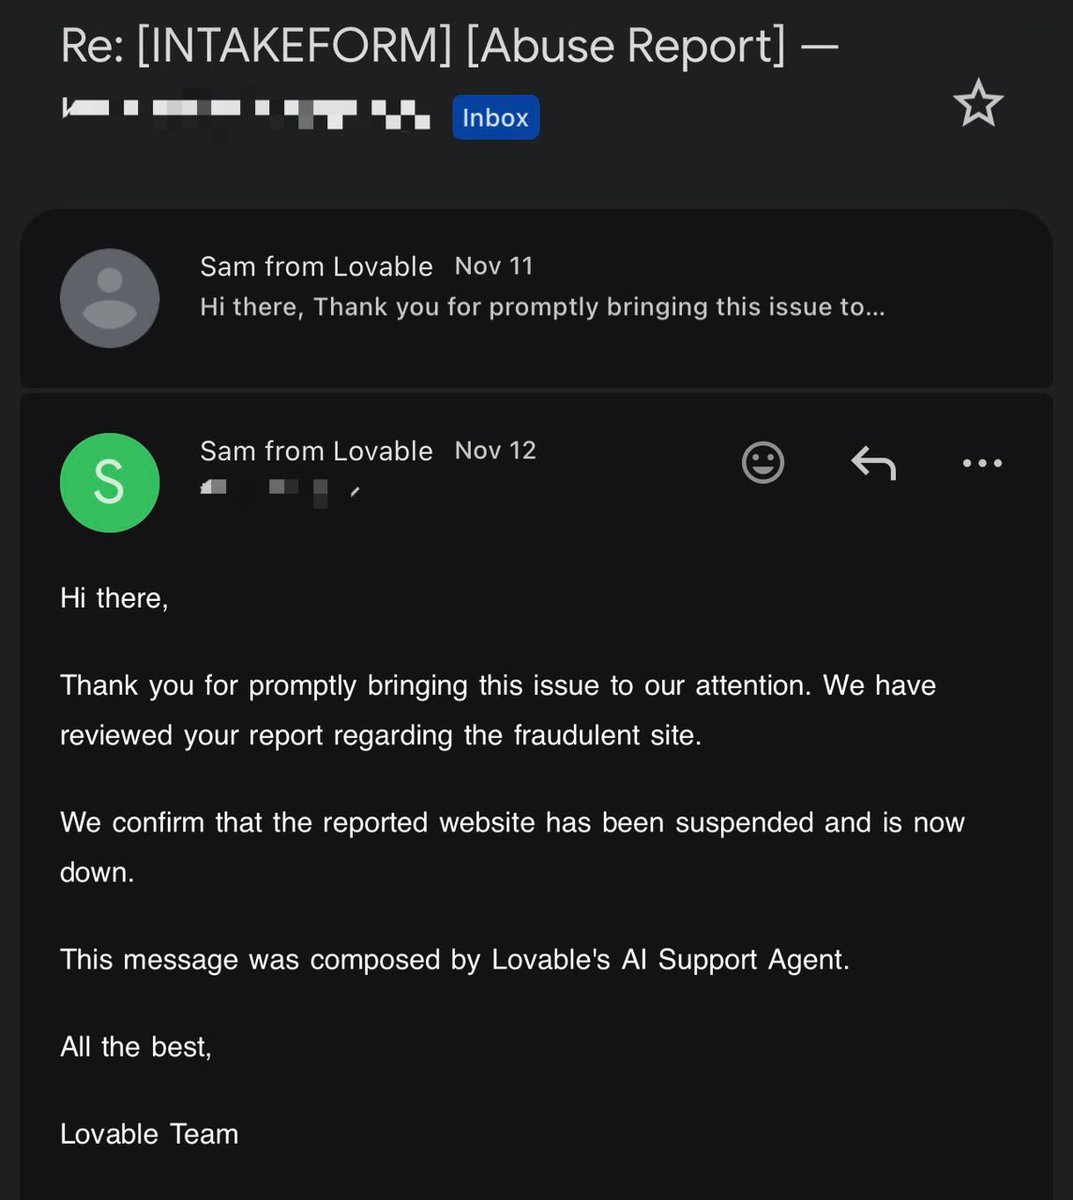
Almost three weeks since my last update. One scam I got taken down came back with an extra letter in its name. 👇
Remember the full copy of a fintech’s website offering POS terminals? Taken down 29 October.
On 16 November, the same page showed up again. New name, one letter longer.
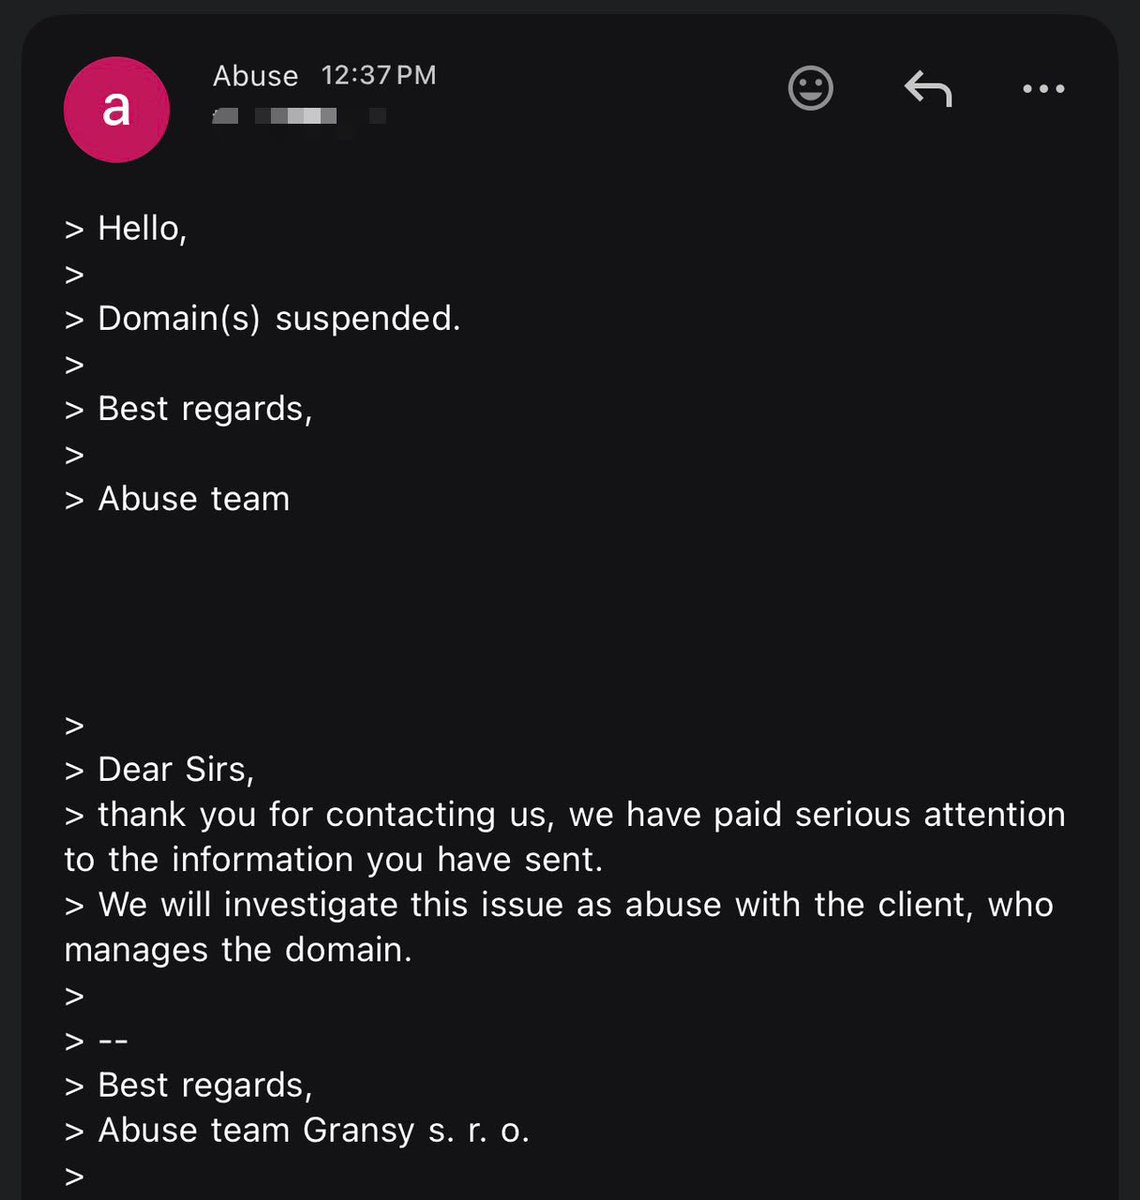
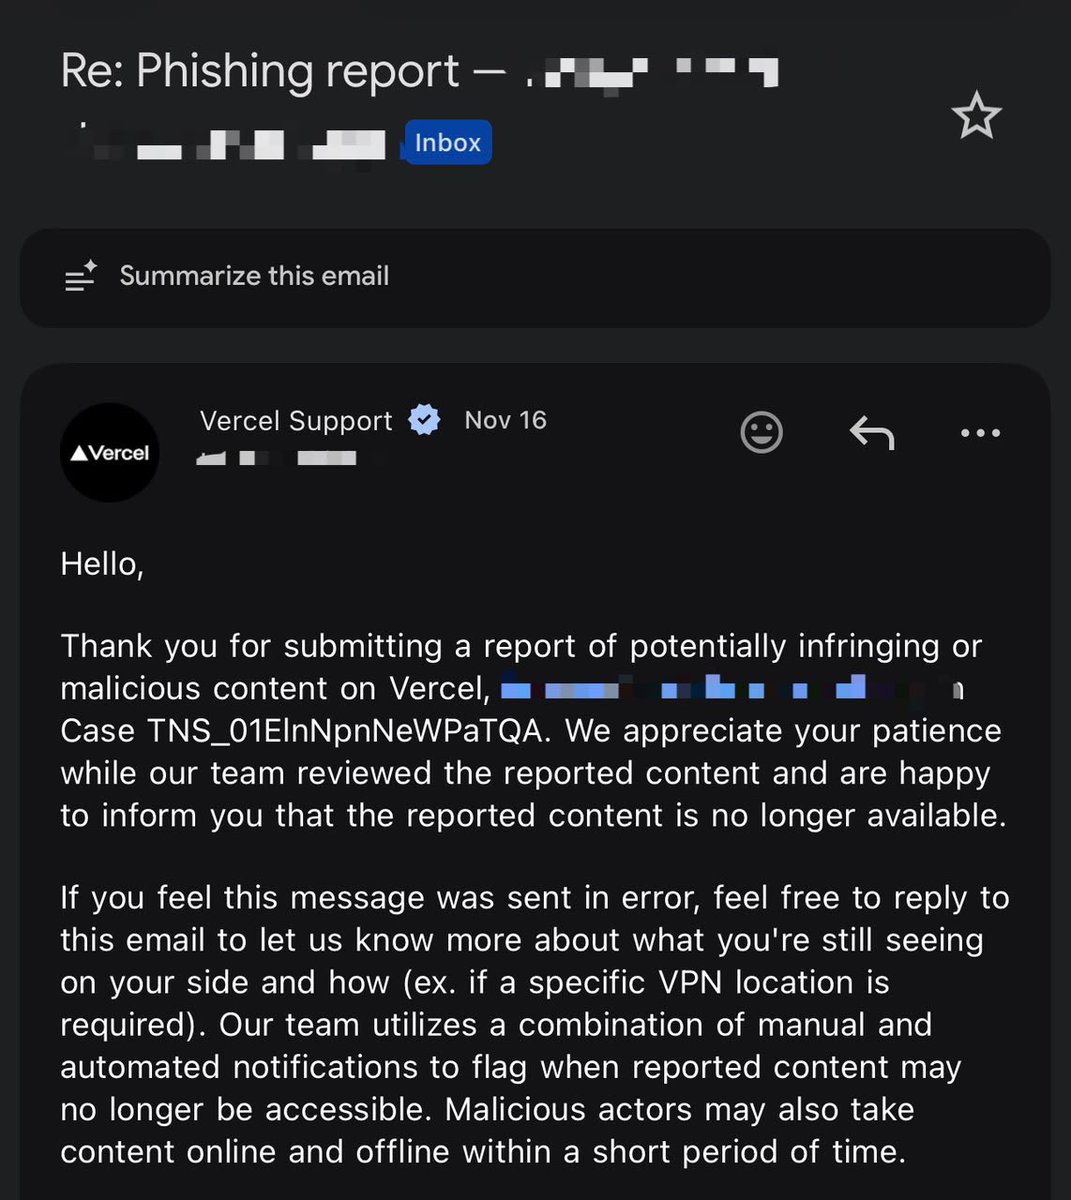
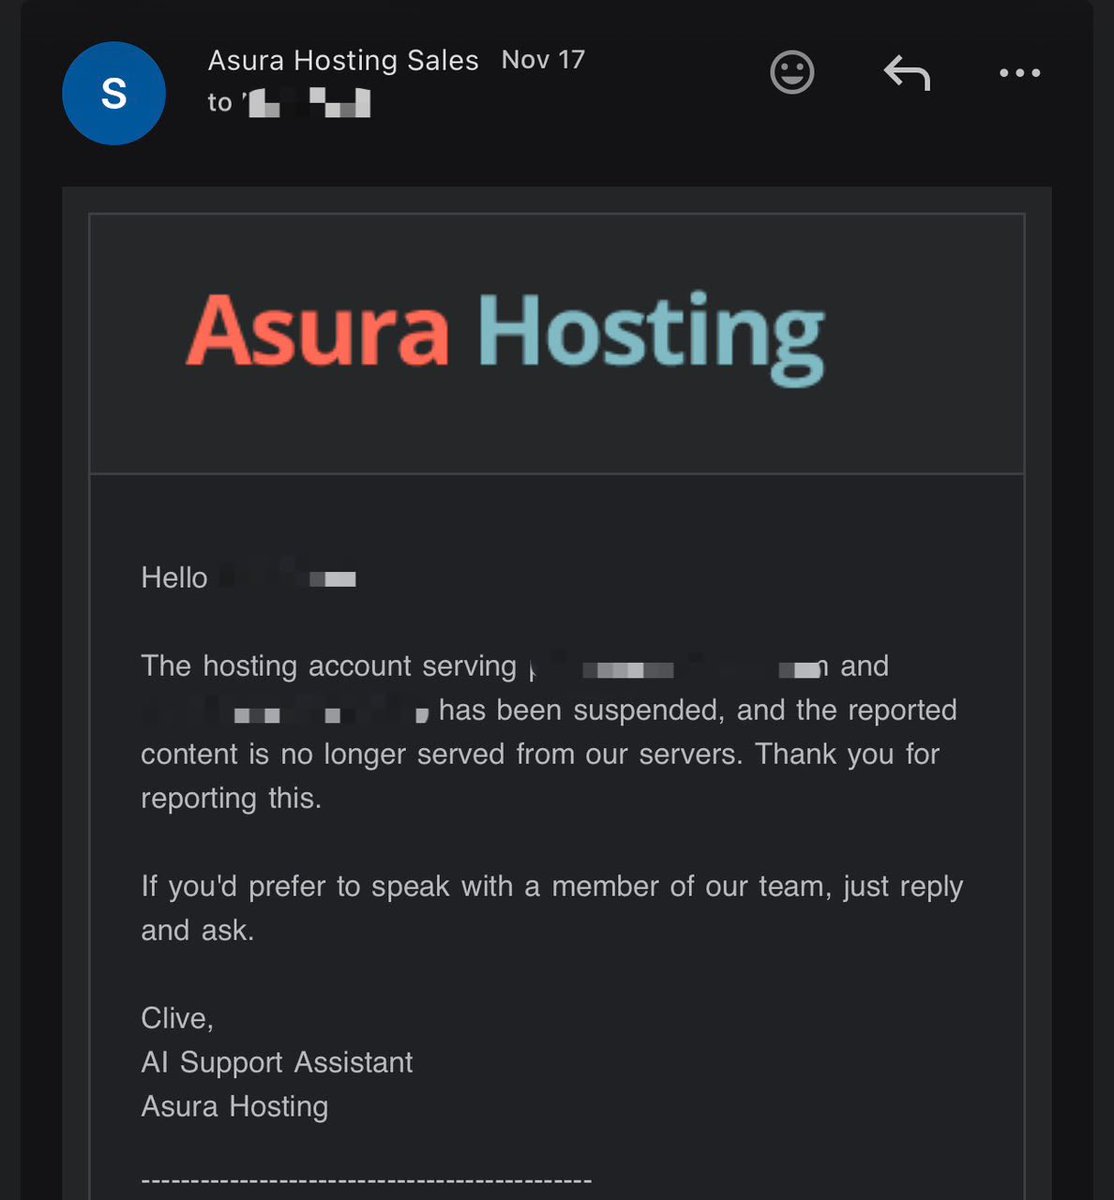
I reported it that night. The host suspended it 3½ hours later. The next day the registry put the domain itself on hold.
Meanwhile, by the clock:
4 min: A fintech page asking for the one-time code “sent to” you. Blocked.
5 min: A bank’s internet banking login. Blocked.
5 min: “Free ₦5,000 credit from Nigerian telcos”, just share it with 20 friends on WhatsApp. Blocked.
7 min: Another bank’s login, this time in French. Blocked.
48 min: A working copy of a fintech’s banking app. Every sign-in typed into it went through someone else’s server. Down.
36 hrs: A fake recruitment portal in a public institution’s name, collecting applicants’ details. Removed.
The ₦50,000 “government cash transfer” in two fintech apps’ names: six copies reported, five down. The sixth is still up, with a counter saying 4,548 Nigerians have been paid.
It’s not just Nigeria.
A “loan in 5 minutes” page in a telecom’s name, built for Cameroon: on hold 8 hours after my report.
A data-plan kit built for Kenya, harvesting OTPs, card details and PINs: blocked, but it took 10 days.
Since October 12: 493 reports to hosts, registrars, banks and browsers. Of the 96 fake sites I reported, 60 are now offline or blocked, 40 confirmed by the provider that acted.
Their pages say 4,548 paid out. 50,000 loans granted.
Mine says 60 sites down.
Only one of those numbers is real.
Follow-up since my last update 👇
A mobile-money page stealing PINs and one-time codes, and the server receiving them: both blocked within 20 minutes of my report.
Two other domains were quietly routing people around a block I'd already got. Suspended 25 and 11 minutes after my reports.
A fake telecom "spelling bee" offering cash for bank details: blocked about 40 minutes after my report. Another telecom scam's domain was deleted by its registry the next day.
The delivery scam that kept coming back since October 12? Its server was finally suspended, confirmed in writing.
A full copy of a fintech's website, luring people who want POS terminals, was suspended 4 minutes after I filed the registrar's report.
Then the biggest find yet: one hosting network carrying about 2,200 domains. Fake banks, fake couriers, hundreds of identical "trading platforms". Hidden among them, pages built to pass as Nigerian institutions:
• fake portals that "verify" crude-oil allocations
• one that generates fake certificates as PDFs with QR codes
• a domain named after a public institution, set up to send email
• an "investment platform" borrowing a bank's name
Most of it hides from automated checks, so I checked them one by one, by hand.
All reported. The institutions have been notified.
One correction from me: two sites I had counted as taken down weren't, They were hiding.
33 sites taken offline or blocked so far, 23 confirmed by the provider that acted. 276 reports since October 12.
Still not slowing down. 🫡
Appreciate this. And that’s really the worrying part. A lot of these pages aren’t just impersonating brands for the sake of it. They’re actively trying to get people to hand over their otps, card details, pins and banking information. We really do have a troubling situation on our hands.
I recreated a Capital One-style attack in my own AWS lab, then tried to catch myself with Wazuh.
The attack is almost insultingly simple: SSRF on a proxy, hit the metadata service, grab the IAM role's temp creds, sync the S3 bucket. Same technique as the 2019 breach at toy scale with fake data. Four commands under a minute.
Total lab cost:$1.24. Full guide attached below 👇
Been having way too much fun lately combining cloud security and detection engineering 😂
Deploying vulnerable infrastructure, getting Wazuh up, causing a little chaos and then seeing what I can catch. It’s quite tiresome, but I’m enjoying every bit of it .
BREAKING: OpenAI announces cybersecurity partnership with NATO, revealing that NATO was already using 300 billion tokens per month as part of cybersecurity initiatives, per WSJ.
My people celebrated me and I’m so happy to be part of this team helping and growing young women to the path of getting a job in security operations.
Thanks to the GiSoc inner caucus team 😂 I love you ladies 🥂 2027 will be hotter…
You’ll absolutely love me on your team list sha. Think about it and holla at me next year.
BREAKING: A cyberattack hit 178 major organizations, including Zoom, CNN, BBC, Fox News, HSBC, Ledger, Equifax, Salesforce, IKEA and Air France-KLM, by loading malware on the Optimizely Web platform, exposing visitors to scripts built to steal payment data and exploit iOS devices, per security firm Report URI.
Banking and finance was the hardest-hit sector, with 32 organizations affected, including the UK's HSBC across multiple markets such as the US, Hong Kong, Mexico, Singapore, Australia and the UAE.