I'll let the legal experts have a take on how this has just become the norm... (sure 1-3 is just some level of fraud)
but no matter what, the majority of the times I think this comes back to bite the business. funding as a moat being a VC darling (on continued fake numbers) is not a strategy I would want to deploy to have a LT, successful business. I think most times... the music stops.
Play long-term games with long-term people
so i have been in the sf tech scene for a couple of months now, and i learned the games that ppl play
1. land a $3M lab order in 2 weeks, *26 = ~$80m as the annual revenue
2. schedule all orders to be signed in the same month, and multiply the best month by 12
3. sign $5M LOIs with friend's companies and batchmates. they sign one back (also happens at scale with large labs/compute)
4. buy github stars at 6 cents each
the last company that swapped invoices with a partner reported $220M - and it's bankrupt now
sad that it's a whole gresham's law game right now and if you dont play you just get downvoted
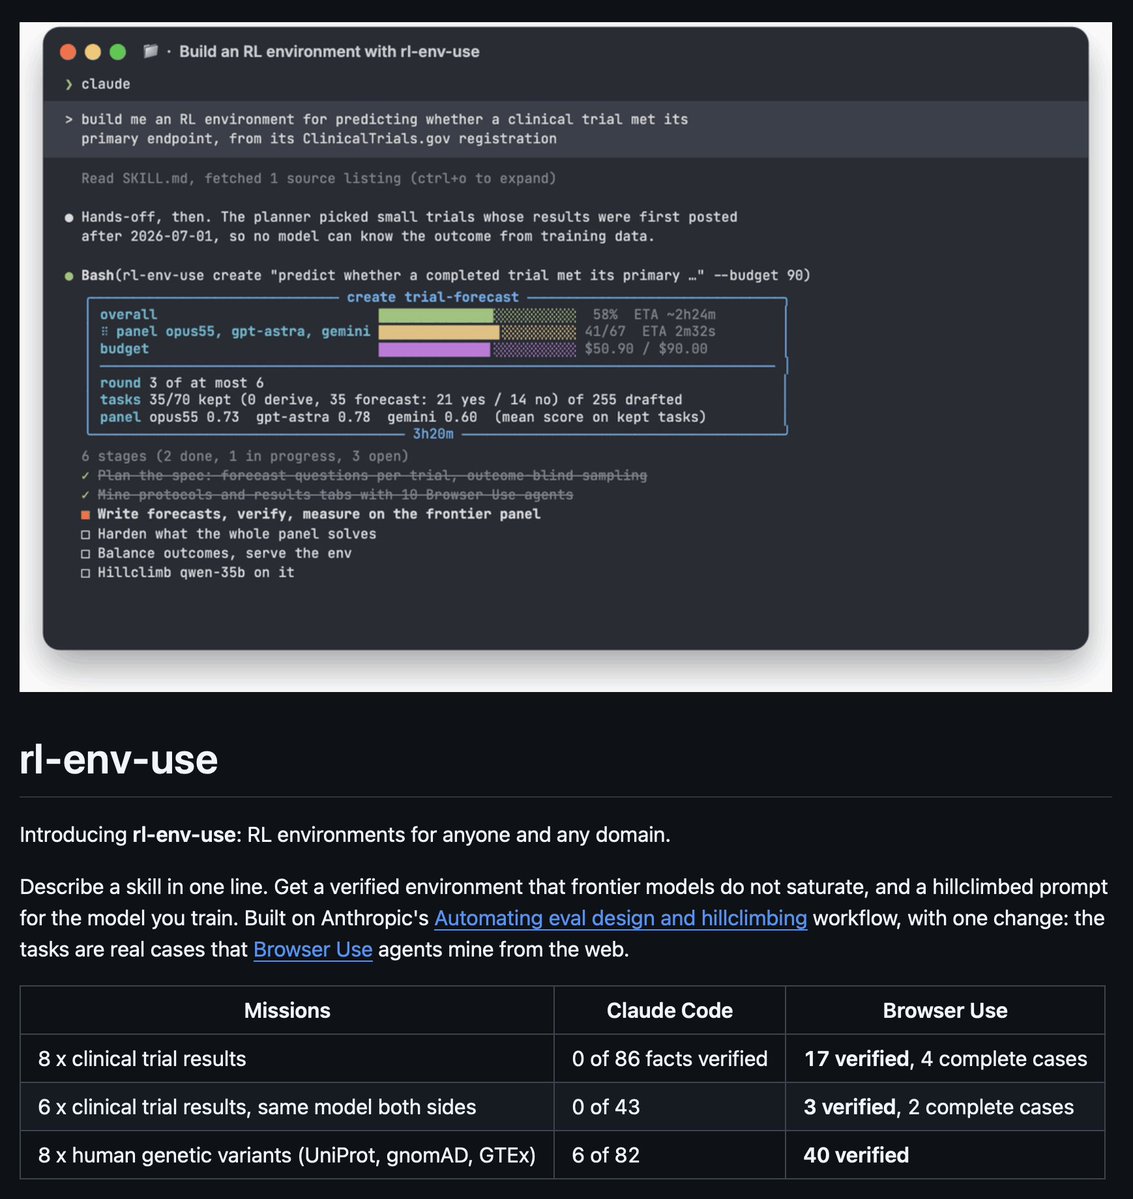
some unscrupulous RL data vendors is going to start pitching frontier labs on some unusually comprehensive longitudinal clinical diagnostics environments next week
its certainly a thought for rl data cool.
there is a lot of work (even more challenges with the businesses themselves) that would be needed to have a fully functional product there... but I can imagine that platform does incredibly well in the future (assuming executed properly, which is no easy task itself)
this is happening more frequently as the market hyper-evolves.
had a business owner yesterday that signed less than 2 weeks ago (probably not even data accepted yet) with micro1, exclusive - but played this card ("I'm not sure the full data is exclusive, I'm really not sure, we will look again"), and are already trying to sell their data again. red flags all over on this one specifically. wide ranging differences from form intake vs. reality.
told them we can't help (even after pressing the exclusive issue and them essentially not caring)... I guess everyone plays their own hand?
Two types of exclusivity in the Company Data biz:
1) Buyer (lab) gets the data exclusively.
2) Broker has the right to market the data exclusively.
Labs dont really care about the former, but the later is super annoying to deal with if the Lab gets the same dataset twice from different sources. If you are repping a dataset to a lab, make sure you have it on exclusive.
business operator (pre AI and AI - truly in the weeds, vast industry experience, ie generalist)... could be a v powerful combo for building tasks.
lets get to work...
pip install --upgrade jax flax optax numpy
Vast AI (Nvidia H100)
jax.vmap
...
cook/learn/cook/fail/cook...
10 minutes.
10 fucking minutes on the computer today..
email 1 from a Vendor: We've been hacked, please rotate keys immediately.
emails 2: Stripe vulnerability; please address when you can.
x: Genetically enhanced wardogs (wtf)
x2: LabCorp was hacked
x3: "Just the beginning, expect things to get worse from here"...
Pup: Rips ...what I believe is his first shart waiting for me to go on a walk.
brb...need to suit up for the day and then clean the floor.
Less than a week to go.
Check your inbox to get verified < 5 minutes with our new broker onboarding.
--> Accept terms
--> Verify your person with Stripe Identification
--> List your first deal
After the 27th, we will reopen founding cohort directly from our waitlist.
Don't forget to reclaim your founding spots by October 27th.
Click the link via email (or just go to your account), go through onboarding, identity verification (via @stripe), and getting your first listing live and awaiting RL desk approval. Looking forward to chatting with you all.
Takes about 5-10 minutes.
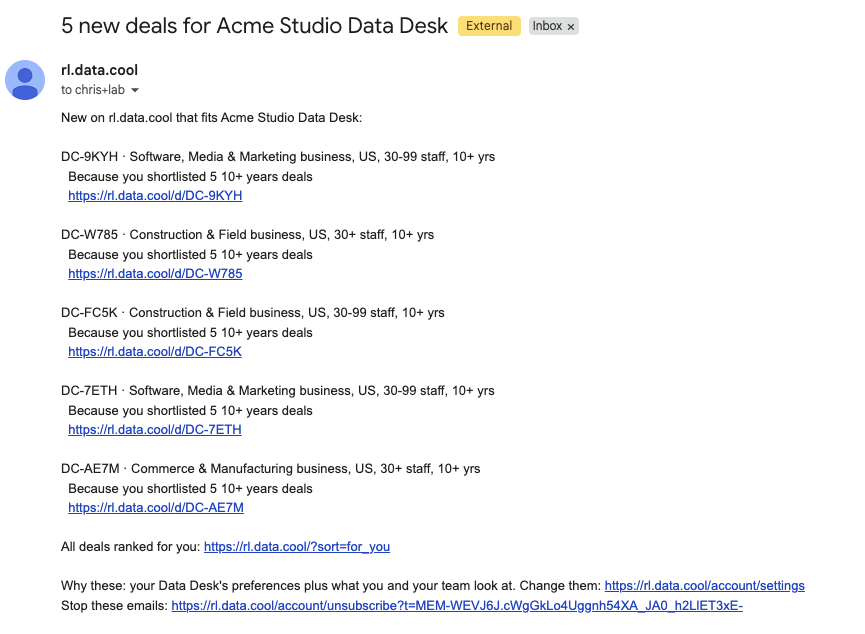
Most investors are still massively undervaluing data.
I was also skeptical when I left a data co for Altos in 2025. Today, I’m all in on data.
Every software company will become a data company. Most will lose. Many more will win than we think. https://t.co/GtnlZo46aq
you have a moral responsibility to educate your family & friends on what is going on in cyber rn.
it is only going to get worse/weirder from here.
here’s a great starter todo list to share:
Two critical PHP vulnerabilities were disclosed today. Cuppa does not run PHP and is not affected. Your WordPress site, however, runs on PHP and may be.
What to do:
1. Ask your host to update PHP to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 (or newer). PHP 8.1 and older will not get a fix, so upgrade to a supported version.
2. After you've patched, go to WordPress → Users → Profile → Application Passwords, revoke the password you created for Cuppa, create a new one, and update it in Cuppa under Team Settings → Integrations → WordPress.
3. Make sure Cuppa is connected with an Editor account, not an Administrator!
4. If you see signs of compromise (unknown admin users, posts you didn't publish, unfamiliar plugins), contact your host right away and keep your server logs.
Today’s example of why ai people are legitimately stressed about internet resilience in the face of agentic cyber attacks:
In 2026’s ongoing vulnpocalypse, eMudhra’s intermediate CA private keys turned out to be tiny numbers like 4 and 56. Anyone could recover them in seconds and mint a fully trusted certificate for any site.
To make this more real— you think you’re on https://t.co/dKPY9kdnqr (padlock next to the url and all). But(!) it’s actually a scammer intercepting the connection, harvesting your SSN or bank details, then maybe forwarding you so you never notice.
Good news is the browsers already blocked the bad certs. Bad news is the long tail of servers, containers, and devices that still trust them has not.
One bad key-generation script from 2025 is still forcing a Heartbleed-scale cleanup. More to come. We have plenty of internet-wide security cleanup to do.