@MikkoMarti60184 I feel like this has been copy pasted 50 times, look at my replies feed, there is no rule saying you cannot vote on your own proposal or you have to vote a specific way, you cannot dictate how someone votes, thats decentralisation!
Please show me where the rule is written GP?
@Defi_world@Greenpeace06_09@kimmyboy2 I though he predicted $0.01 for LUNC, how wrong was he, by the way, @Greenpeace06_09 is @kimmyboy2 and old @kimmyboy2 has been called out numerous times for taking photos from travel brochures and passing them off as his own lifestyle…frauds both of them (the same person)
@frag_dude@FreefreeJohn@_JCH01@frag_dude they can threaten all they want, I am sure they will learn how blacklists and whitelisting works with IBC when they cant use it 🤷🏻♂️
Development will stall.
Security of @JurisProtocol is at stake - and with the safety of it's users - which are not only users of the product, but also users of the L1.
Vote YES on 12236 and thank you for your continued support 🙏🙏🙏
@frag_dude Amazing collaboration to ensure continuity! Whats started off as a misunderstanding has turned into an awesome collaboration. Thank you both @frag_dude@CeramicToken for all your hard work in getting to this point!
Hello #TerraClassic,
Closing the public WASM upload path was an important step toward mitigating a confirmed, unpatched attack vector affecting $LUNC.
While work continues behind the scenes to address the underlying issue and safely restore permissionless WASM uploads, builders on Terra Classic still need a way to deploy urgent security fixes for their L2 projects.
These projects can face security vulnerabilities of their own. Requiring developers to rely solely on the 7-day governance process to deploy fixes can leave critical vulnerabilities exposed for far too long.
This joint initiative by @CeramicToken and me aims to provide a practical example of how builders can propose dedicated WASM upload channels for their projects — enabling faster security responses while maintaining the necessary safeguards.
Security shouldn't have to wait seven days.
Discussion link in the answer to this thread.
Proposal is up for allowing us to publish our CosmWasm code and conduct our Security Month upgrades, especially for CW20Mintables to help mitigate private key attacks as well as reduce the impact of other types of security incidents. If you are on Lunc Goblins, please express support, and thank Frag for supporting the CL8Y ecosystem's needed whitelisting. https://t.co/53jt5AFXEi
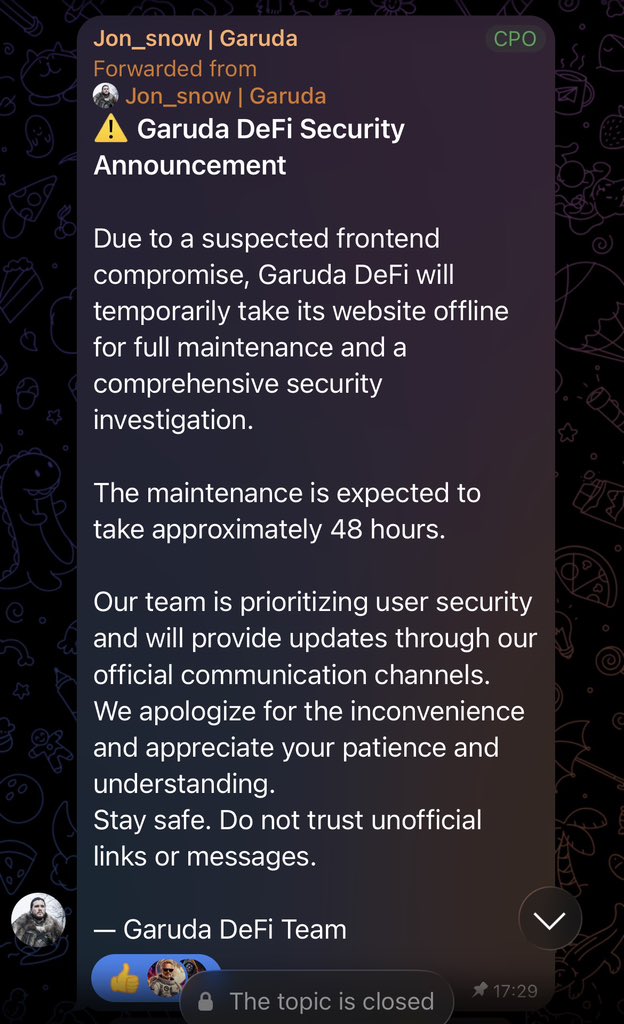
⚠️ A quick note on Garuda DeFi.
Garuda is one of my favorite builders in the LUNC community, and I know this team cares deeply about what they build.
Still, users always come first.
Following a suspected frontend compromise, Garuda is taking its website offline for around 48 hours to investigate and secure everything properly.
That is the right call. Security first, then clear communication. 🤝
Please do not connect your wallet, sign transactions, or trust any Garuda links until the team confirms the site is safe through its official channels.
Stay sharp and stay safe, everyone. 🛡️
#LUNC #LuncCommunity
@RupertLowe10@TowerHamletsNow Planned for the 11th November…someone in their organisation fucked up royally, were they going to do a 2minutes silence in the middle of their demonstration?
Large number of critical/high security vulnerabilities across the CL8Y ecosystem's services have been patched. More fixes will be incoming over the next few days, so please be expecting short outages as services are patched and reboot. - CF
UPDATE: Frag has addressed our concerns, see conversation and link: https://t.co/KMa3HeHn71
Please encourage validators to not support https://t.co/ayKY415hpz
This proposal forces all contract code to be first approved by TerraClassic ($LUNC) governance. That means critical security upgrades to cl8y dex, mitigations of live exploits, and future features, must all pass a validator vote. Not only does this mean every feature we build has to be approved by validators, it also means critical security upgrades have to wait 7 days to be deployed. Security vulnerabilites must be addressed in minutes, not days. - CF
Followup post on form: https://t.co/NltLMaNCGV
TLDR: As long as its paired with immediate whitelisting of the CL8Y multisig, CL8Y ecosystem will not be severely impacted by the proposal.