🚨 AI agents are exposing more than code.
Thousands of files containing their owners' secrets are reportedly being exposed on GitHub.
A reminder: secure your .env files, API keys, credentials, and agent configurations before pushing to public repositories. 🔐
@Cybernews
I claimed the "leviathanxcdn" handle on @ThePirateFace 🏴☠️
Where Hugging Face AI models never die, and are immortalized as torrents.
Claim yours 👇
https://t.co/cWO63Zc3Bp
Free AI should not start with a credit card.
deepseek-v4-flash-0731:free sits on the CrowLLM free shelf, behind the same key as paid models.
lwkey kinda good pain for integration in replicas-decvs
#AI#crowllm#Programming
https://t.co/5rDXIpSfXt @crowllmapi
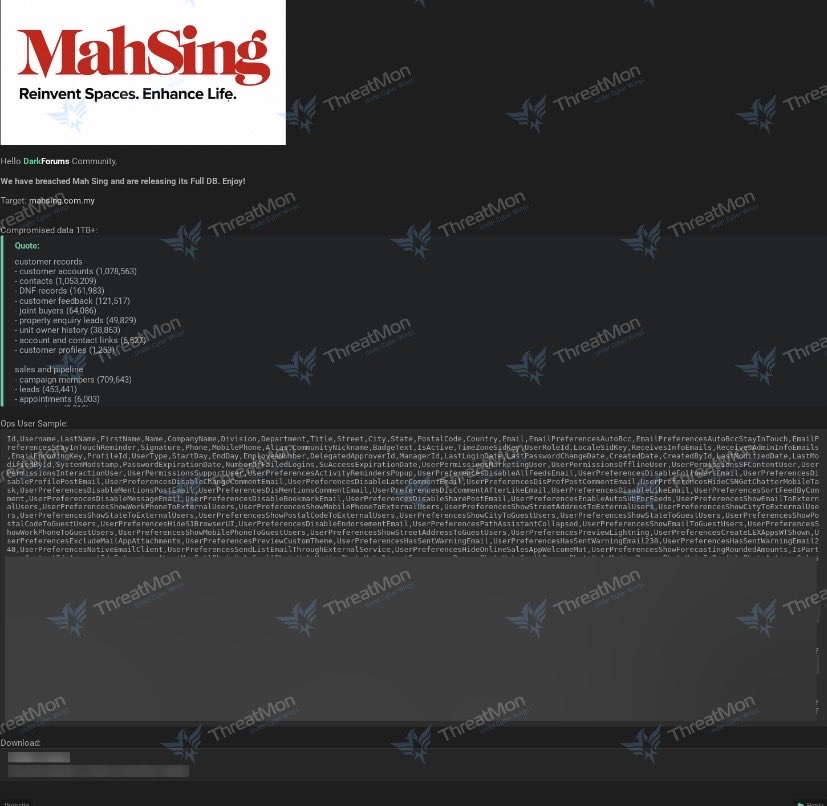
🚨 Threat Actor Claims 1TB Breach of Malaysian Developer Mah Sing Group
A post published on a dark web forum alleges that a threat actor infiltrated Mah Sing Group Berhad, a leading real estate developer in Malaysia, and released over 1 TB of compromised data. According to the post on the underground forum, the stolen data originated from the company’s Salesforce system and includes extensive customer records, financial ledgers, and internal system configurations.
The attacker claims the data dump contains millions of records across various categories, including the following:
Customer accounts (1,078,563) and contact information (1,053,209)
Ledger details (472,465) and sales price details (188,414)
Login history (841,429) and employee user data (1,335)
Legal and litigation documents (45,914) and HR/payroll documents (16,912)
The leaked metadata also reveals integration points with third-party services such as 3CX and Lava Protocols. Mah Sing Group is a leading publicly traded company in Malaysia with a significant portfolio of residential and commercial projects; this makes the company a high-value target due to its customer base and financial data.
If this information is accurate, the leak of sensitive financial documents, legal files, and personal contact information could trigger a serious regulatory investigation under the Malaysian Personal Data Protection Act (PDPA) and pose potential fraud risks for affected customers.
At the time of reporting, the alleged breach has not been independently verified by Mah Sing Group or security researchers.
> be Malaysian company
> get invoice
> invoice_name.iso
> 3 files
> "open.exe", libcef.dll, wuaueng_ui.ime.png
> open.exe uses libcef.dll
> Chromium Embedded Framework
> hmmmm
> open.exe just does libcef.dll!cef_execute_process
> isnt even called correctly
> hmmmm
> look inside libcef.dll
> not the same libcef.dll
> libdef.dll!cef_execute_process reads png file
> extracts shellcode out of it
> low detection on VirusTotal
> no notes
> first seen yesterday
i guess we bonking this now
Hey Its Friday
* OpenCode Hacked
* php screwed the internet
* node said hold my beer
* ruby said hold my beer
* curl said hold my beer and eMudhra held that beer
* Railway said hold my beer
* OpenCode again
helluva week and I only mentioned literally 1/2 of what I know about
Account takeovers hide behind residential IPs that look like real users. Flag proxy traffic in your fraud model without adding friction for trusted users.
is this the end of cyber security to be honest everything you see is ai aia ai iai aiaiaiaiaiaiaiaiaiai going nuts this field never stops moving and i guess netieher can we @MAXdeg0@pdiscoveryio