For everyone who doesn't know, this man followed a 6 year old girl into the toilets in a restaurant in South Africa and r*ped her. The media is trying to protect his identity because he is white.
My South African friends, breaches keep happening. Sorry, 🤷🏻♂️
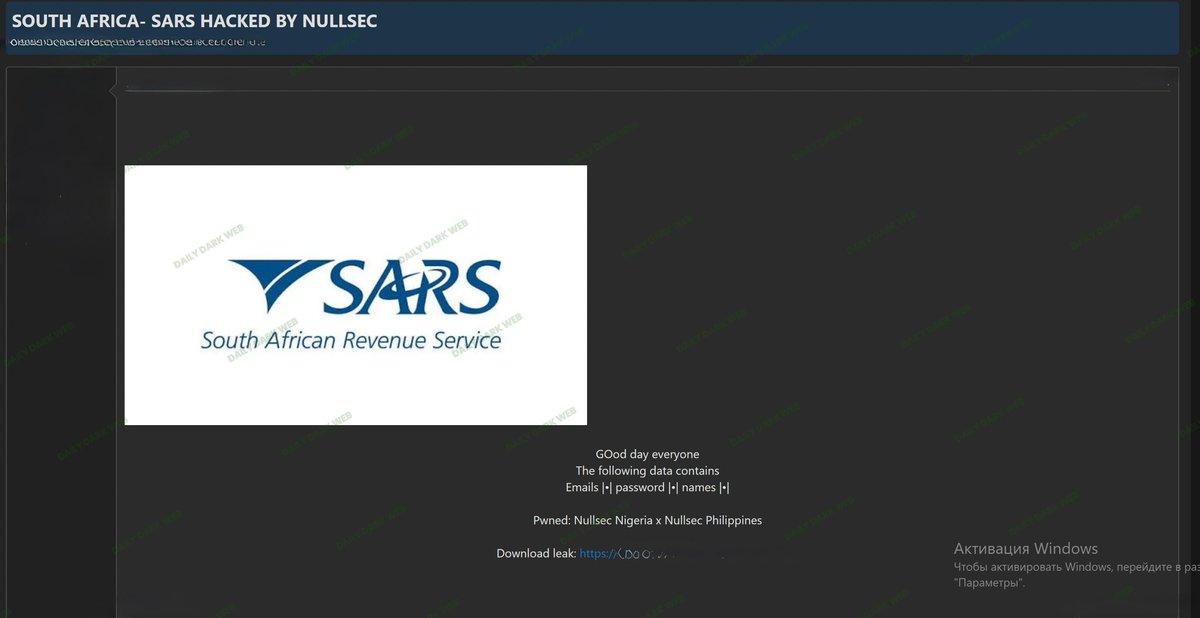
🇿🇦 A threat actor group identifying itself as “Nullsec” is claiming to have compromised South African Revenue Service and leaked data allegedly containing:
• email addresses
• passwords
• names
The underground post is relatively minimal and does not currently provide:
• record counts
• technical proof-of-compromise
• sample database rows
• infrastructure details
• intrusion methodology
The actor instead relies primarily on branding and broad claims to attract attention.
If legitimate, this would represent a highly sensitive government-sector cybersecurity incident because tax authorities typically maintain:
• national identity information
• taxpayer financial records
• corporate filings
• payroll/tax submissions
• banking-related data
• confidential citizen information
However, an important distinction must be made:
the screenshot alone does not validate that the exposed data genuinely originates from SARS systems. Underground actors frequently:
• repackage older credential leaks
• relabel unrelated datasets
• falsely associate government agencies
• combine public data with credential collections
• exaggerate breach impact for notoriety
One notable pattern:
hacktivist-style groups increasingly target government institutions for visibility and political signaling rather than purely financial motives.
The mention of:
“Nullsec Nigeria x Nullsec Philippines”
suggests possible cross-regional branding or collaboration narratives commonly used by underground groups to amplify reputation and perceived reach.
If any portion of the data is authentic, likely risks would include:
• credential stuffing attacks
• phishing against taxpayers
• government impersonation scams
• business email compromise attempts
• identity theft operations
Government-sector credential exposure is especially dangerous because attackers can leverage trust in official institutions to conduct highly effective fraud campaigns.
Users connected to government services should:
• avoid reusing passwords
• enable MFA where available
• monitor suspicious emails claiming to originate from tax authorities
• remain cautious of refund/payment-themed phishing messages
At this stage, the claim should be treated as unverified until independently confirmed by technical analysis or official disclosure.
🇿🇦 #DDW #Intelligence #CyberSecurity #SouthAfrica #Government #DataLeak #DarkWeb #ThreatIntelligence #Infosec #CyberThreats #OSINT #CredentialLeak #SARS