Let's not mince words:
* If you don't support trans people, you're a bad human
* If you have to add caveats to your support (e.g. "as long as my kids don't see"), you're one of the worst kinds of human
* Trans deserve your *unconditional* support for their humanity
Today's Breach Please is out. We talk about how Chainguard unilaterally broke the embargo on the PHP vulnerability and what that likely means for coordinated disclosure going forward.
It is BY FAR the spiciest episode we've recorded to date. 1/3
We also dive into the question of whether AI labs are actively hurting security (yes, they are. They just are).
Jess has some pretty strong opinions about the message in this tweet specifically. We don't 100% agree, but the discussion is valuable. 2/3
https://t.co/xiFo2UeTew
as bad as things have gotten in the past 4 days, they are going to get a lot worse before they get better. security leaders, never let a crisis go to waste: please go to your boards and ask for help right now. not for ai, for the basics. (we need to hold on for ~18 months.)
In the past I worked with NCMEC, I built a tool for mining EXIF data from images and had a database of camera serial numbers they could query. If they had the serial number of a camera used to take CSAM they could map it to other photos on the internet that mapped to user accounts.
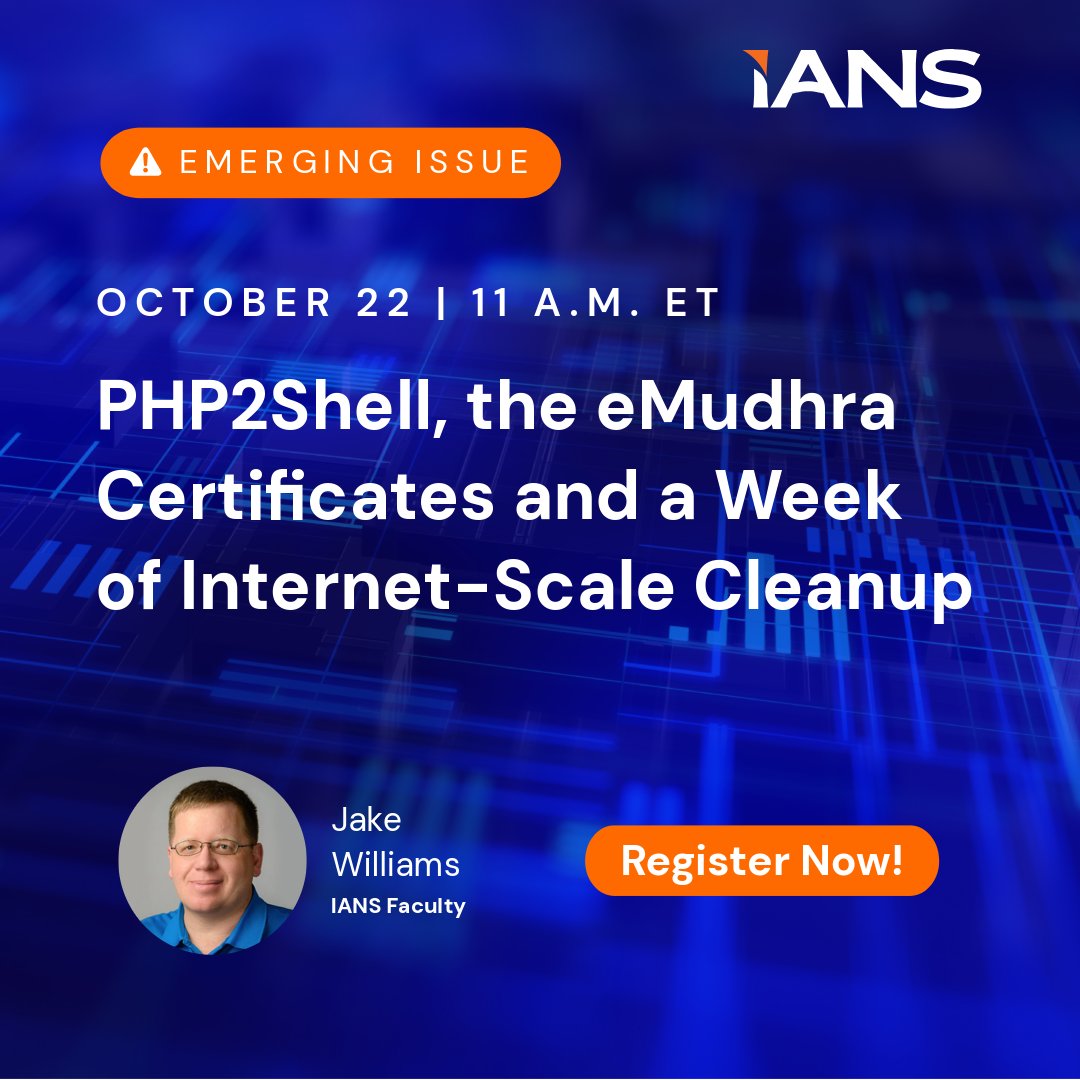
Join me at 1100 ET today to discuss the current vulnerabilities in PHP, Node.js, GitLab, and the eMudhra certificate signing key debacle. We'll provide actionable advice and cut through the noise in our hour together.
https://t.co/hjyC4jL5Q7
PHP2Shell (CVSS 9.2) disclosed, and eight eMudhra certs could let anyone mint trusted certs for any site.
Thursday, Oct. 22, 11 a.m. ET: @MalwareJake, IANS Faculty, on what your security team should do now.
Register now: https://t.co/vFIckaTNdJ
In most cases, ConnectWise won't be able to see into the customer environments to identify who was compromised - those logs live in the customer tenant.
https://t.co/OX88Pg7dvi
ConnectWise has an incident with compromise this weekend where they disabled backups in customer M365 environments.
Even if you're not a ConnectWise customer, you likely have third party risk management concerns here for those you do business with who are.
If you missed my two day AI Risk Assessment course at Wild West Hackin' Fest in Deadwood last week, I'm teaching it again in Denver in February and we're offering it virtually too. Hope to see you there!
https://t.co/k9cm8hx3qN
We also discuss the report that Bank of America used Mythos to find vulnerabilities, but hired 1000 contractors to fix them - highlighting that while AI is a useful security tool, it's not getting rid of humans in tech anytime soon.
Episode link: https://t.co/hG0GmqDKlJ
Today's Breach Please is out. Since we recorded this, there's some news reporting that the deletion was "human error." But we're going to see a lot of "human error" claims when people inappropriately confirm an agent's actions.
What a great week at @TechCrunch Disrupt! Thanks to @zackwhittaker for bringing @wendynather & Rudra Mitra (AWS) together for this panel on securing the AI enterprise
im back for WiFi Day 2026 my dudessssss let’s go!! October 22 @ 12-3pm ET
@ekahau is giving away a Sidekick 2, full license, & ECSE training to one lucky winner drawn out of the registrants! all u gotta do is be on stream when we call yr name 🛜
In today's Breach Please, we talk about the last minute cancellation of the Grace Hopper Celebration. My co-host has previous experience organizing conferences. She brings some real insights into what might have happened here and what it means for women in the tech industry. 1/2
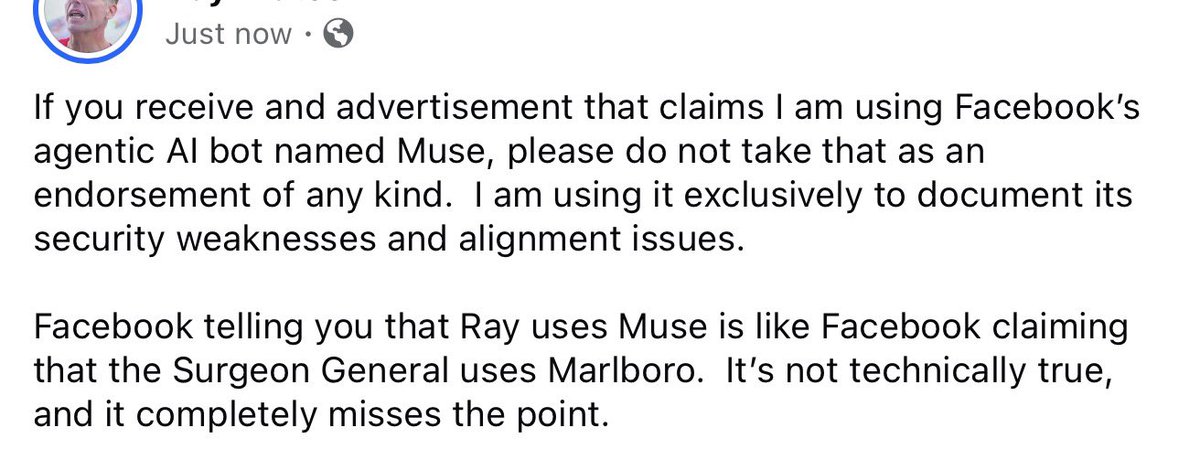
Important warning for security researchers who are investigating security and alignment issues with Meta’s Muse agentic bot.
If you activate an account, Facebook (possibly Instagram) will spam all your connections claiming that they should try Muse since you are using it.