🥷 Now we can inject a payload into a remote process without using VirtualAllocEx and WriteProcessMemory.
No need to suspend the target process
New technique to evade EDRs:
Github: TwoSevenOneT/InjectSetConsole
#redteam#pentest#antimalware
🐐 Driving in my truck, 🚘 right after a beer. 🍺 Hey, that bump ⛰️ is shaped like a deer. 🦌 DUI? 🚔 How about you die? ☠ I'll go a hundred 💯 miles an hour! 🕐 Little do you know, 🧠 I filled up on gas. ⛽ Imma get your fountain makin' ass. ⛲ Pulverize this fuck 🫠 with my burgentruck. 🛻
virtio-9p VM escape bug in QEMU: https://t.co/3CIBBy7fA4
Patch at https://t.co/icgSgVQqNd
Reminder to sandbox your VMMs. And concurrency is hard to do right.
Private researcher reported a security vulnerability to Chromium on August 4. The fix went into the public source code but Chrome users never got it due to patching timelines. Two Chinese groups, apparently read that public fix, built an exploit chain from it and started phishing NGOs on September 1 using identical code. Technically an N-day but for anyone actually running Chrome, a zero-day. Here the public patch knowledge worked as an instruction manual. Open source means everyone can read the fix. With AI, some people just operationalise the knowledge faster. https://t.co/1pY3F4qCl9
Our intern Yap Yuan Xi pointed AI at Cisco Smart Software Manager and went to make tea. It found a post-auth RCE in under an hour
He spent days writing the report. Cisco had silently patched it the day after he found it. No CVE, not even a biscuit, at least not that we know of.
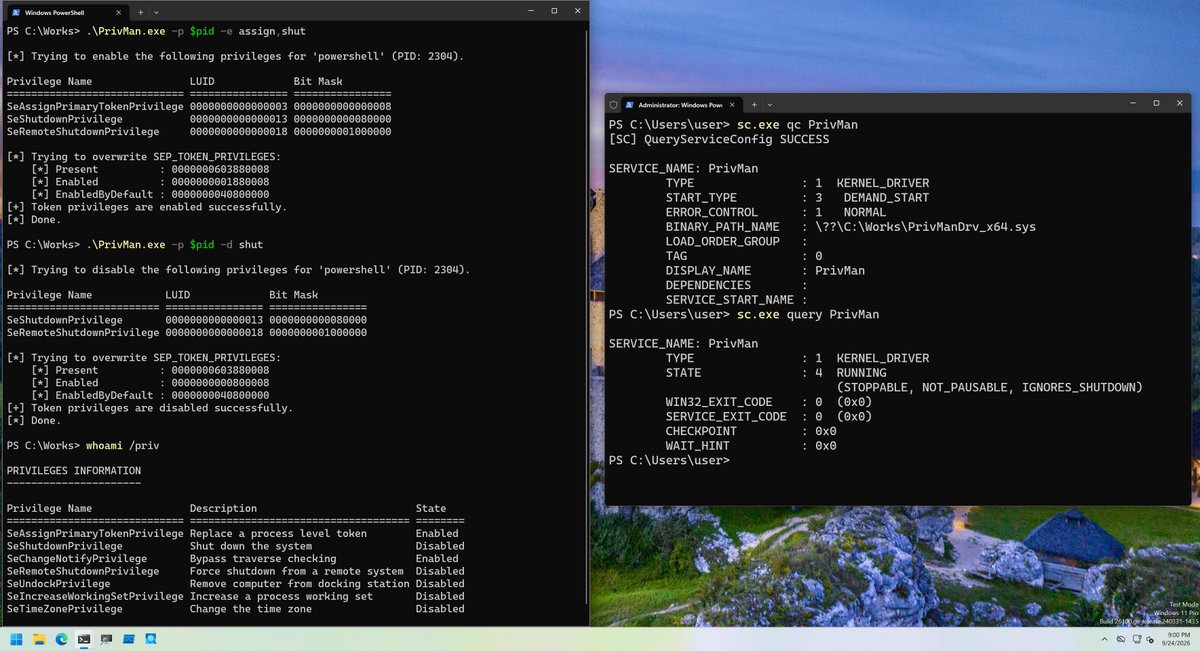
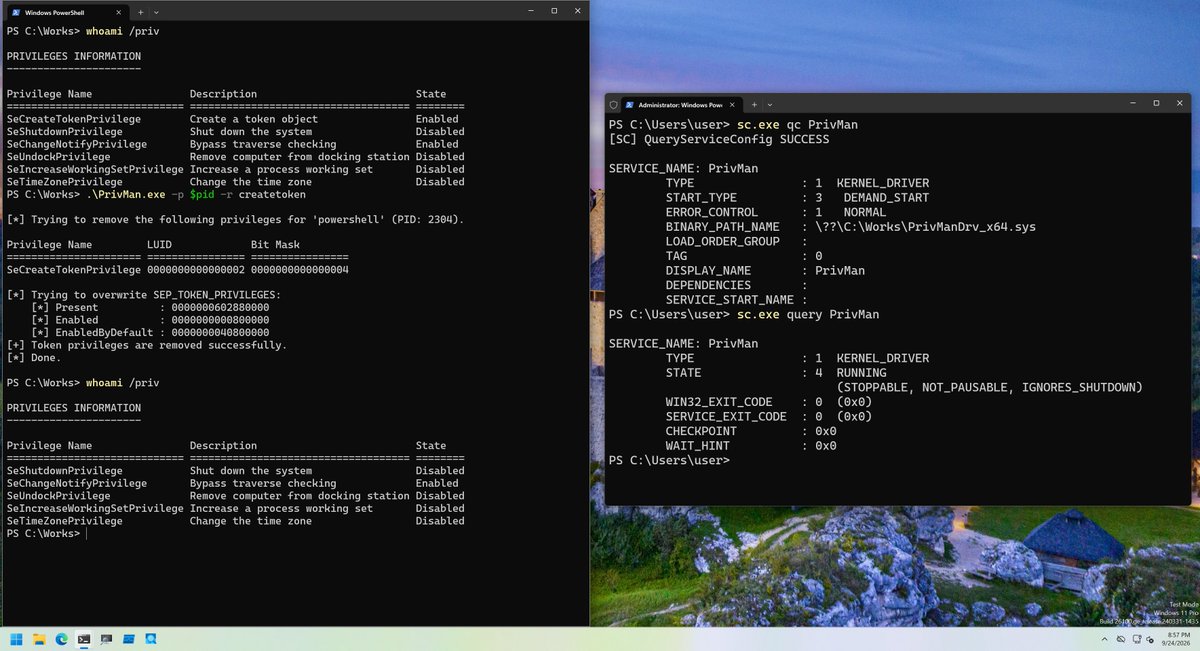
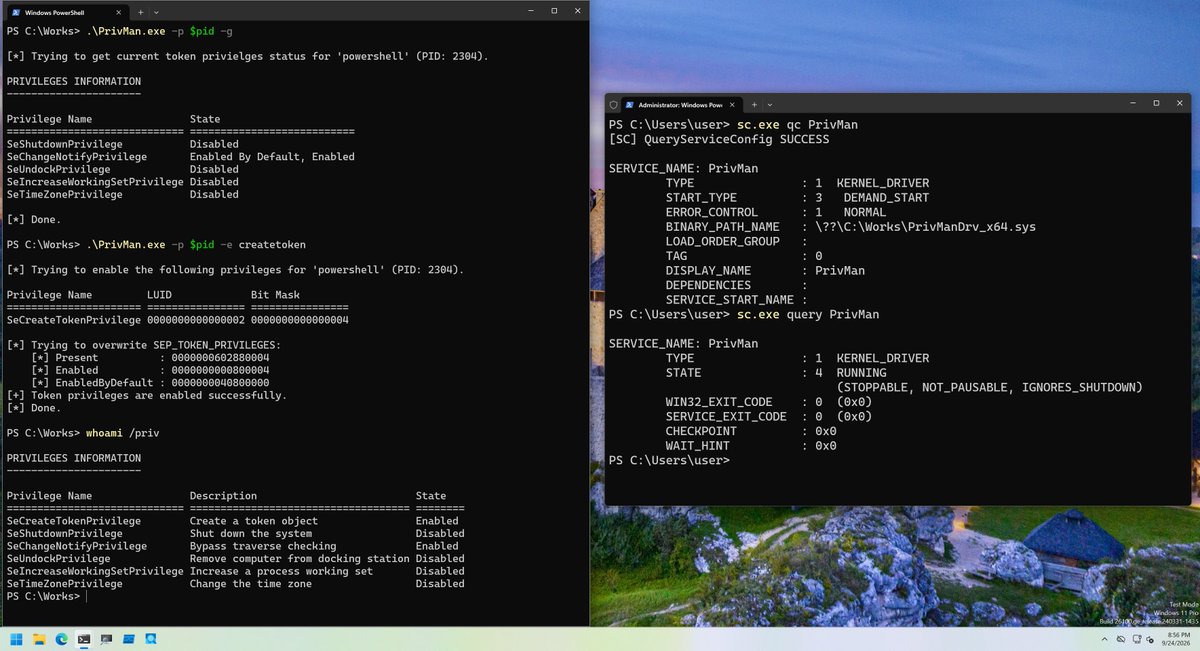
I wrote a tool to manipulate token privileges with kernel driver for token privileges investigation.
If you prefer kernel drivers over the kernel debugger, feel free to use them.
https://t.co/d9hVbmbFwA