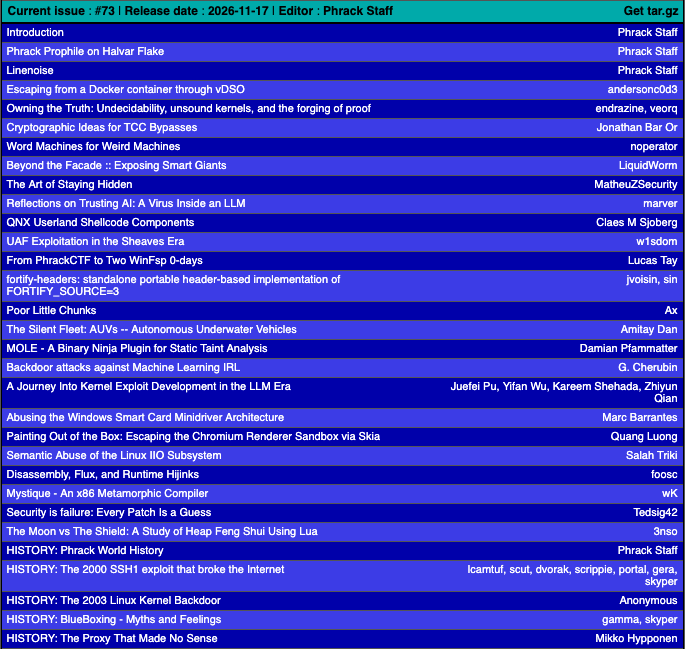
Excited to share that my article "The Art of Staying Hidden" is now published in Phrack #73!
Exploring Linux kernel rootkits, process and network hiding, kernel internals, and anti-forensics.
https://t.co/qkEDM2nGv3
#phrack
Excited to share that my article "The Art of Staying Hidden" is now published in Phrack #73!
Exploring Linux kernel rootkits, process and network hiding, kernel internals, and anti-forensics.
https://t.co/qkEDM2nGv3
#phrack
30 years ago today, Phrack 49 published Aleph One’s “Smashing the Stack for Fun and Profit”.
A legendary paper that inspired generations of hackers and helped shape modern exploit development.
Still an essential reading.
https://t.co/qAQ5CWgNj0
Phrack 73 is coming soon!
Mission accomplished. I'll post my full talk on Linux malware tactics and evolution when I return (no video allowed at the conference). Thanks to all that attended and the conference organizers for having me!
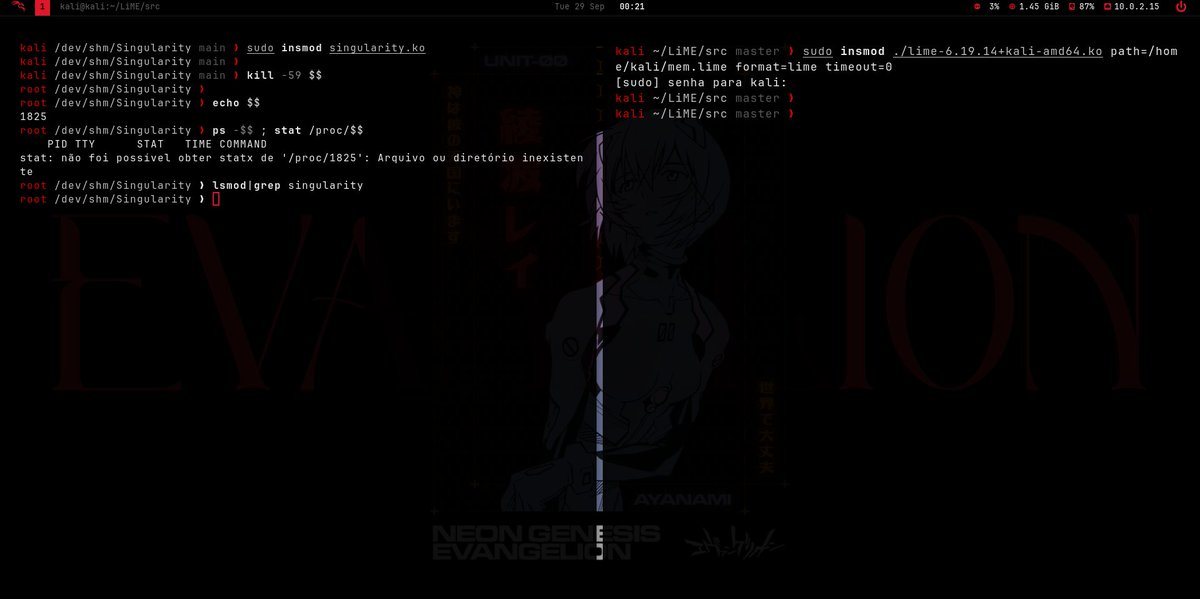
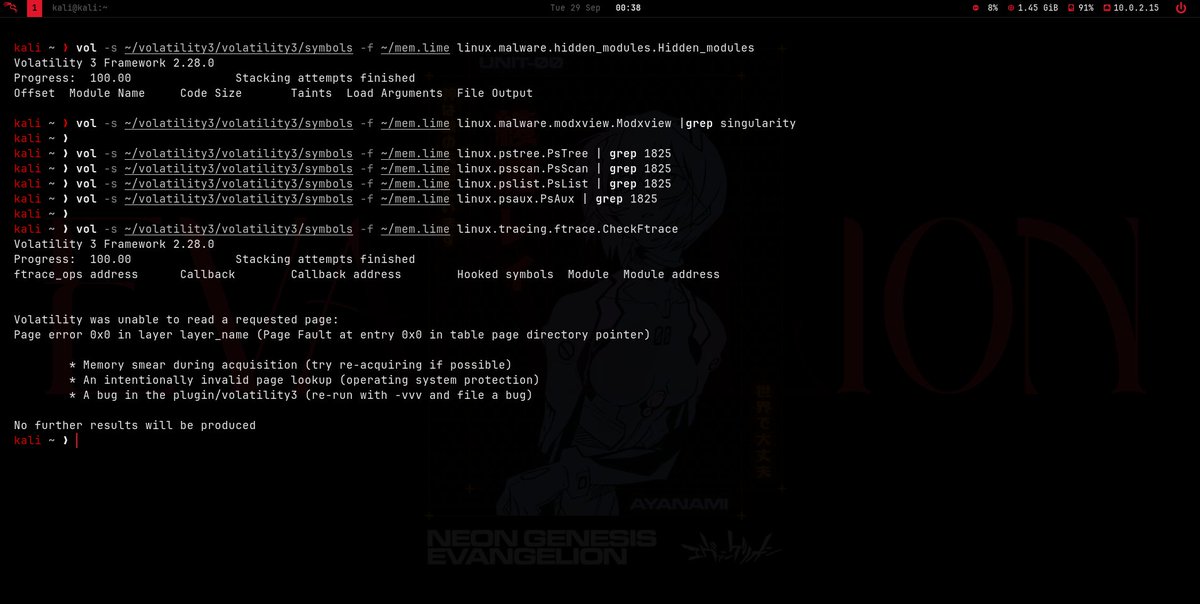
Singularity LKM rootkit evading LiME and Volatility 3
My rootkit hooks walk_system_ram_res so LiME never copies its physical pages and vol3 found nothing
CheckFtrace crashes on a poisoned page and pstree, psscan, pslist all come back empty for hidden proc. hidden_modules too.
Singularity LKM rootkit evading LiME and Volatility 3
My rootkit hooks walk_system_ram_res so LiME never copies its physical pages and vol3 found nothing
CheckFtrace crashes on a poisoned page and pstree, psscan, pslist all come back empty for hidden proc. hidden_modules too.