Following the discovery that eight eMudhra intermediate certificates use weak keys, Cloudflare is deploying mitigations and releasing client updates. We explain the impact, our response, and what customers and developers should do next. https://t.co/lYGxHb3PHS
How on earth did this happen:
The Indian certificate authority (CA) eMudhra had one job (well, two):
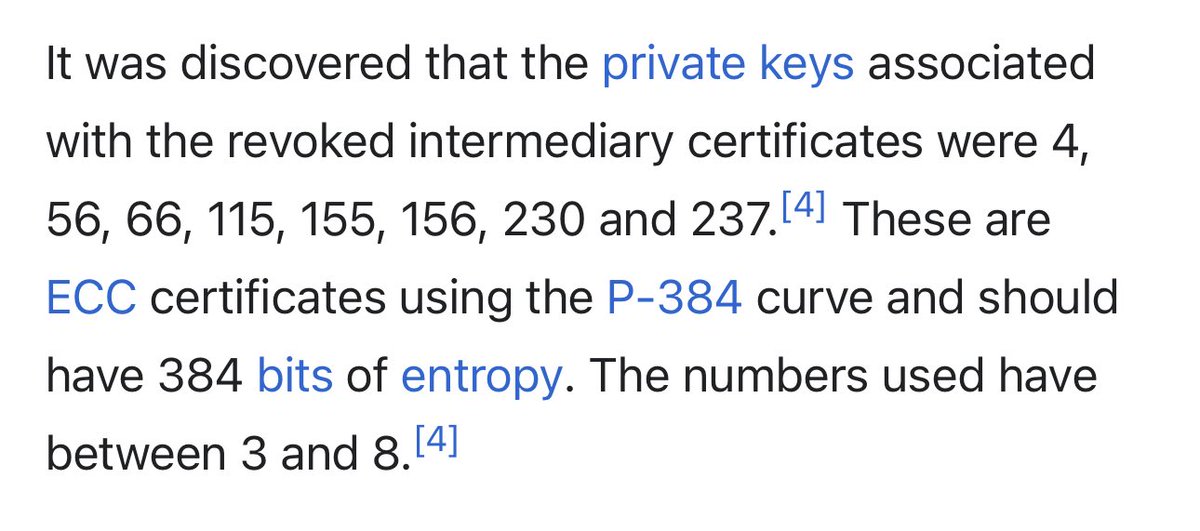
1. Create secure, 384-bit private keys
2. Store these securely and do not leak them
Well, eMudhra chose private keys between 1 and 256 (the numbers!!) and called it a day. WTF
PHP
Patch, take it offline, or put it behind a WAF and hope it filters the exploit requests. I wouldn’t count on a configuration-only fix unless one is confirmed.
For inventory, this Nmap command can reveal PHP versions exposed in HTTP headers:
nmap -sT -sV --version-light -T4 --max-retries 1 --open -p 80,81,443,8000-8010,8080-8090,8181,8443,8880,8888,9000,9001,9080,9090,9443 --script http-headers --script-timeout 10s --script-args 'http-headers.path=/index.php,http-headers.useget=true' <target>
Only scan systems you’re authorized to test. This finds advertised versions, not every PHP server, and doesn’t confirm vulnerability.
Claude Code found spyware on my sister’s phone. It had been tracking her for 11 weeks…
She asked me to check her phone. Someone always seemed to know where she was and she couldn’t figure out how
I plugged it into Claude Code and asked what’s running that she never installed. It walked every app, including the hidden ones, and flagged one disguised as “System Service”, no icon, not on any store
It had been there 11 weeks, logging her location every 2 minutes. Claude pulled the details on whoever was running it:
reports to → +1 (415) *** **72
carrier → T-Mobile US
device id → IMEI 35 ********** 47
last ping it sent → 40.7**, -73.9** · 2 min ago
We saved everything the app had recorded and passed it to the people who do this professionally. Then Claude shut it down and wiped it off her phone
The full step-by-step is below, takes 5 minutes. Save it so you don't lose it, and send it to anyone who might need it
🚨 MAJOR SECURITY ALERT
8 certificate authority private keys have been compromised.
How bad is it? An attacker holding these keys could impersonate ANY website, including banks, exchanges, or Google, and potentially intercept sensitive communications.
The good news: Chrome, Firefox and Apple have already taken action to block the compromised certificates.
The bad news: Many apps, developer tools and systems may still trust them.
What you should do TODAY:
Update your browser, OS and phone.
Update desktop apps (Slack, Discord, VS Code, etc.) as patches arrive.
Avoid untrusted Wi-Fi until your devices are updated.
Only install updates from official sources.
Ignore any email offering a "certificate fix".
This is a serious compromise of internet trust infrastructure, not just another website hack.
Full technical details:
https://t.co/i5MxKTe8co
crypto intellectuals sow panic about how all public key cryptography might be broken one day
meanwhile the entire internet gets pwned by vulnerabilities in php
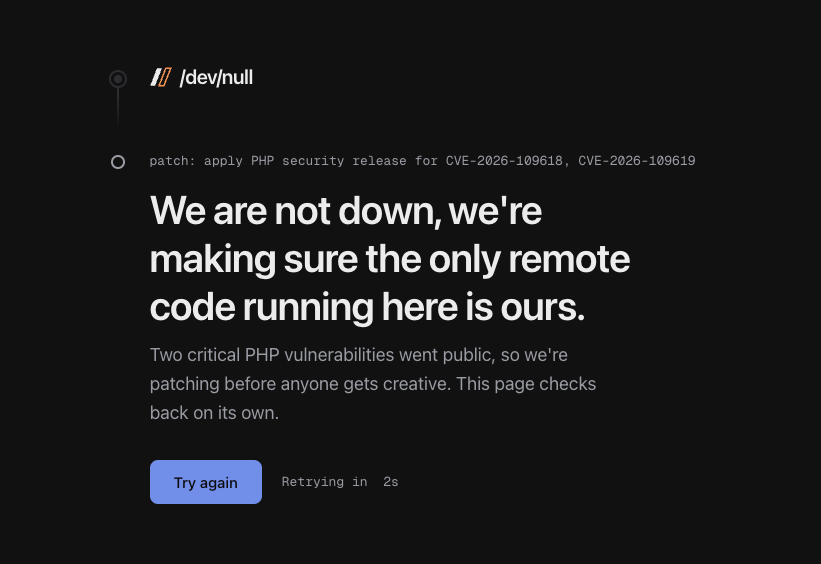
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
If you run any kind of PHP application on your server... it's time to patch. Except... the patch is not here yet.
Some info here: https://t.co/DYq0aiTAAK - but disabling upload progress *may* help, it's just not the full fix:
session.upload_progress.enabled = Off
Open source vs closed source.
Light vs darkness.
Two very different futures for humanity.
This is why I love DeepSeek.
Free research. Open models. And now, even their production inference stack.
Community over everything.
Can't imagine OpenAI, Anthropic, Google, or Meta doing this.
🚀 Introducing DeepInfer, our in-house inference framework, now fully open source!
Powering DeepSeek-V4.1-Flash at scale with high throughput and low latency. We’re sharing our production stack to help the community lower compute costs, reduce energy use, and make AI more affordable.
🔗 https://t.co/JGAik1kgk0
1/4
THIS IS F**KING INSANE
SOMEONE JUST DROPPED A FREE PDF EDITOR THAT COULD MAKE ADOBE OBSOLETE 🤯
It’s called RevPDF, and it offers Adobe-like features for free in a package that’s just 20 MB.
It’s open-source, runs directly on your computer, and requires no account, subscription, or cloud uploads.
Here’s what you can do with it:
→ Edit text and images directly inside PDFs
→ Sign contracts and fill out forms
→ Redact sensitive information before sharing
→ Compress PDFs for faster sharing
→ Convert PDFs to Word documents
The best part? It works offline, keeping your private documents on your own machine.
If you deal with contracts, invoices, or documents every day, this could save you from paying for another subscription.
Save this for later.
Link below ↓