OpenClaw has 145,000+ GitHub stars. CNBC, Palo Alto Networks, and Kaspersky are all writing about it. It's the hottest AI agent framework in the world right now — and for good reason.
It turns your computer into a 24/7 AI assistant that actually does things. Multi-channel messaging. Browser automation. Persistent memory. Calendar, email, file management. It's what ChatGPT and Claude should have been.
But here's what nobody wants to talk about:
🔓 ~1,000 OpenClaw instances found publicly exposed with zero authentication (Shodan scan, January 2026)
🔓 CVE-2026-25253: One-click remote code execution via auth token theft
🔓 Data leaking across user sessions and messaging channels
🔓 Prompt injection attacks via web content, emails, and third-party skills — with no trust boundaries
🔓 Palo Alto Networks called it a "lethal trifecta" of risks: access to private data + exposure to untrusted content + ability to communicate externally + persistent memory that makes attacks survive across sessions
The core problem? OpenClaw has no identity layer. No way to cryptographically verify who's talking to the agent, where data came from, or whether a skill is trustworthy. It treats everything — your commands, a forwarded WhatsApp message, a malicious webpage — with the same level of trust.
That's why I built Edwin.
Edwin is built on top of OpenClaw's runtime, but adds the security and intelligence layers it's missing:
🔐 Cryptographic identity — every message, every agent, every interaction is signed and verifiable. Edwin knows WHO is talking to it, not just what they're saying.
🧠 Semantic memory (Shad) — not the "dump everything into the context window and pray" approach that Claude's memory uses. Edwin runs external semantic retrieval that scales without degrading. It searches for what's relevant instead of loading everything every time. Claude's own memory system has a documented "fading memory" problem because of this exact architectural limitation.
🛡️ Trust boundaries — session isolation, tool policies, authenticated inter-agent communication. Untrusted content can't escalate to privileged actions.
The AI industry is racing to give agents more power. But power without identity is a security nightmare. OpenClaw proved the demand. Edwin solves the trust problem.
We're not building a better chatbot. We're building AI you can actually trust with your data, your credentials, and your business.
https://t.co/h9vsZhvrfy
#AI #Blockchain #OpenClaw #Edwin
I've been focused on development of my new AI harness/OS @EdwinPai so I haven't been on X for a while.
The reason the mempool exists is to receive transactions so the first seen rule can be followed. Those transactions are then processed and added to blocks as quickly as possible.
Teranode processes transactions and adds them to subtrees/blocks as soon as they are received so a mempool is no longer needed.
The savings of immediate processing and subtree communication is superior to using a mempool because it's more efficient, and importantly, it accelerates the positive flywheel effect of node game theory:
Nodes receive as many transactions as possible and build subtrees as quickly as possible while hashing as quickly as possible to win the next block with as many transactions as possible to get the biggest block reward they can.
They are then incentivized to reinvest their earnings into their computing and networking infrastructure to be as competitive as possible and to earn as much profit per block as possible.
The result of this is the holy grail of computing systems which is a system that gets more efficient the more it's used.
It's the win-win-win relationship Satoshi carefully crafted in the original white paper: peer-to-peer electronic cash that's competitively maintained so individuals retain privacy, data provenance, and data ownership; the system gets cheaper and requires less energy to use as usage if it increases; and, node operators earn more while simultaneously being strongly incentivized to provide the best experience possible in order to earn more
Muddied by profit motives (and their existential nature given compute cost and the margin for error -- paraphrasing Dario himself), and the known unknowns. Given the source code leak, how easy it's been for Chinese competitors to farm and reproduce at a much lower price point... Also, the gov can't be having decisions made for them in a brand new frontier like this when the stakes are so high. It sucks, but it's the right call IMO.
That said, I think Personal AI systems like your PAI are closing the gap in a much more measured and deterministic way, so I don't really see this as much of an issue.
Continuous continuity over multiple sessions via recall with a Opus produces better and more consistent results over the exponentially more difficult moving target of single context window single shot llm only inference anyway
Divisible UTXO swaps enable real L1 peer-to-peer order books.
No matching engine. Just Bitcoin Script.
Multisig protects treasuries with m-of-n approval.
Public keys stay hidden until the spend.
Multi-party sign-off on every mint and burn.
Configurable at issuer-level compliance with a designated authority now able execute regulatory orders directly on-chain.
No off-chain detours. No issuers, miners, or foundations/associations in the loop.
On-chain script-enforced - no intermediaries.
STAS 3.0 script template makes this real 👇
https://t.co/hIkchsEaD2
@TeamWinnaar Pretty much exactly what I've built with @EdwinPai 😎
https://t.co/Du3yvyk4aA
But fully P2P and Identity as the base layer for the filtering
We rave about giants like Newton, Einstein, Bohr, Tesla, and Edison. But in terms of direct impact on our lives in the information age, nobody comes close to Claude Shannon.
In 1948, he dropped a straight 10/10 paper:
A Mathematical Theory of Communication.
His work has imbued us with the ability to send whispers across continents.
The paper doesn’t just suggest techniques, it draws the boundaries of reality for information... how far compression can go (entropy), the maximum rate a noisy channel can carry reliably (capacity), and why error correction isn’t optional if you want those whispers to arrive intact.
@akhil_bvs@steipete I find more than 3 becomes a shit show. So I have 1 that's my CTO and he's in a number of rooms on matrix where each room has 2 others and he coordinates them for me
I saw a post today about a new "secure AI agent platform." Their pitch: dedicated pods, zero-trust networking, encrypted key storage, Kubernetes node hardening.
All to solve one problem — they don't trust their own infrastructure.
We took a different approach with Edwin.
Instead of building bigger walls around a shared platform, we made the agent yours. You run it where you want — your laptop, a $5 VPS, a company cloud instance, whatever fits. Your keys, your data, your choice.
That simplifies a lot. But the two things we really focused on:
𝟭. 𝗠𝗲𝗺𝗼𝗿𝘆 𝘁𝗵𝗮𝘁 𝗮𝗰𝘁𝘂𝗮𝗹𝗹𝘆 𝘄𝗼𝗿𝗸𝘀.
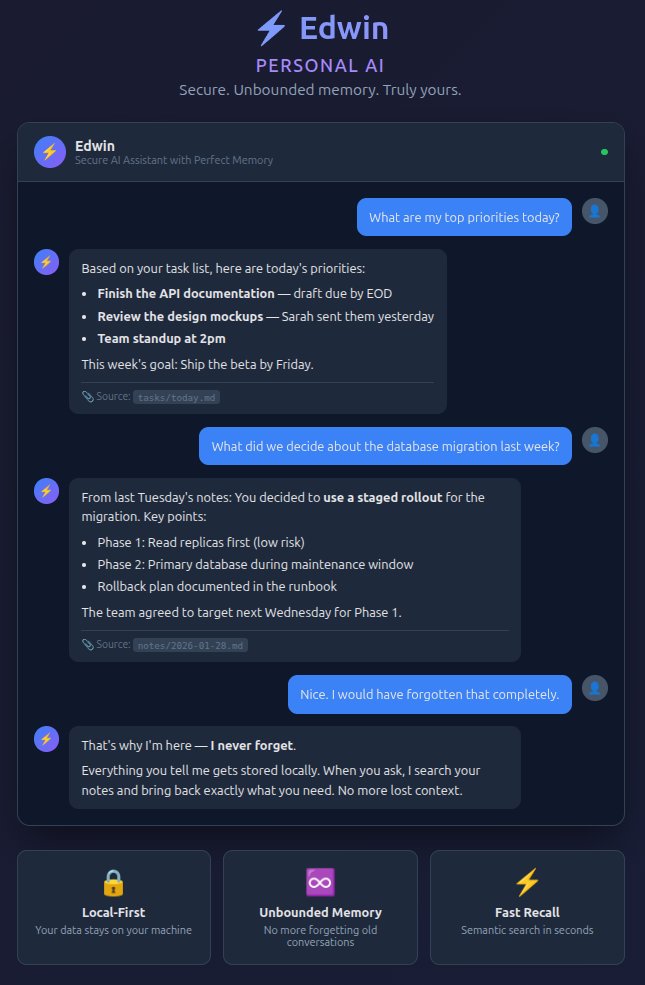
Every AI agent has a context window problem. Conversation gets too long, session ends, memory's gone. We solved this by treating the context window as a scratchpad — not the memory. Edwin writes to disk, recalls on demand, and picks up where it left off. It remembers last week's tasks, your contacts, what you discussed. Not because we fine-tuned a model. Because we built a retrieval system that works like memory should.
𝟮. 𝗜𝗱𝗲𝗻𝘁𝗶𝘁𝘆-𝗯𝗮𝘀𝗲𝗱 𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆.
Most platforms bolt security on top — containers, network policies, secret managers. Edwin ties access to identity. Your agent knows who you are. That's what determines what it can do. No DevOps team. No Kubernetes cluster. Works the same on a Raspberry Pi or an enterprise VM.
What this looks like in practice:
→ API keys stay on infrastructure you control
→ Memory in plain files — portable, readable, yours
→ You pick where it runs — no vendor lock-in
→ Cron jobs, proactive scheduling, multi-channel messaging
→ WhatsApp, Telegram, Discord, Signal, Matrix integration
→ Full source access — read every line
We're opening up a small founders group for early access. If you want to run Edwin and help shape it: https://t.co/h9vsZhvrfy
#AIAgents #DataOwnership #DevTools #OpenSource
Locked context per phase. The reference vault gets built once from curated docs (~15K chunks), then each generation phase gets a frozen snapshot of specs + vault. No drift allowed mid-phase — if something needs updating, that's a new phase. The key insight: treat the vault like a versioned dependency, not a living doc. Parallel work reads from the same frozen context; conflicts get resolved in review, not generation.
79,000 lines of code. 4 days. One desktop app.
Not vibe coding — structured AI orchestration:
→ Spec first, code second
→ Reference vault for grounded context
→ Parallel phase execution
→ Human testing every phase
Full breakdown of how we built Edwin Desktop with Shad 👇
https://t.co/1f1xYnbnaO
#AI #SoftwareEngineering #DevTools #BuildInPublic #BlockchainIdentity
OpenClaw has 145,000+ GitHub stars. CNBC, Palo Alto Networks, and Kaspersky are all writing about it. It's the hottest AI agent framework in the world right now — and for good reason.
It turns your computer into a 24/7 AI assistant that actually does things. Multi-channel messaging. Browser automation. Persistent memory. Calendar, email, file management. It's what ChatGPT and Claude should have been.
But here's what nobody wants to talk about:
🔓 ~1,000 OpenClaw instances found publicly exposed with zero authentication (Shodan scan, January 2026)
🔓 CVE-2026-25253: One-click remote code execution via auth token theft
🔓 Data leaking across user sessions and messaging channels
🔓 Prompt injection attacks via web content, emails, and third-party skills — with no trust boundaries
🔓 Palo Alto Networks called it a "lethal trifecta" of risks: access to private data + exposure to untrusted content + ability to communicate externally + persistent memory that makes attacks survive across sessions
The core problem? OpenClaw has no identity layer. No way to cryptographically verify who's talking to the agent, where data came from, or whether a skill is trustworthy. It treats everything — your commands, a forwarded WhatsApp message, a malicious webpage — with the same level of trust.
That's why I built Edwin.
Edwin is built on top of OpenClaw's runtime, but adds the security and intelligence layers it's missing:
🔐 Cryptographic identity — every message, every agent, every interaction is signed and verifiable. Edwin knows WHO is talking to it, not just what they're saying.
🧠 Semantic memory (Shad) — not the "dump everything into the context window and pray" approach that Claude's memory uses. Edwin runs external semantic retrieval that scales without degrading. It searches for what's relevant instead of loading everything every time. Claude's own memory system has a documented "fading memory" problem because of this exact architectural limitation.
🛡️ Trust boundaries — session isolation, tool policies, authenticated inter-agent communication. Untrusted content can't escalate to privileged actions.
The AI industry is racing to give agents more power. But power without identity is a security nightmare. OpenClaw proved the demand. Edwin solves the trust problem.
We're not building a better chatbot. We're building AI you can actually trust with your data, your credentials, and your business.
https://t.co/h9vsZhvrfy
#AI #Blockchain #OpenClaw #Edwin
My time with the BSV Association has come to an end after 4.5 years. It has been a phenomenal 4.5 years; I'm grateful to have had the opportunity to work with so many exceptional people and travel to so many beautiful places, and I know they're going to continue pushing blockchain forward.
I'm now shifting my focus entirely to the integration of AI + Blockchain. I've been busy building over the past weeks:
- Shad (Shannon's Daemon) -- a fast semantic search engine that uses Recursive Language Models (RLMs) strategically to effectively eliminate the AI context window problem so every session is a continuation of the previous: https://t.co/ntodvERxO7
- Edwin (named after physicist Edwin Jaynes) -- a personal AI that uses Shad for its memory system and takes a new approach to security so you don't have to choose between safety and utility anymore; it's like OpenClaw but secure and continuously coherent.
Please have a look at my website: https://t.co/z8xOlfrAge . I've added a simple AI chat that you can use to find out more about my experience and whether we'd be a good fit if you're looking to hire.
I'd appreciate it if you could share this for visibility
Cheers
hashtag#AI hashtag#Blockchain hashtag#IPv6 hashtag#Agents hashtag#Shad hashtag#Edwin hashtag#OpenClaw hashtag#ClawdBot hashtag#MoltBot
I've fixed the two main issues with OpenClaw so it doesn't forget across sessions, reduces token cost by >90%, and is safely usable for everyone. Coming soon:
#AI#Blockchain#PAI#Edwin
I got tired of trying to prompt harder so I built Shad to reason smarter.
Introducing Shad: https://t.co/ntodvERxO7
Shad enables AI to reason over virtually unlimited context.
Instead of forcing everything into a single prompt or relying on brittle RAG pipelines, Shad turns your knowledge base into an explorable environment—one the AI can navigate intelligently, step by step, as it solves real problems.
Load an Obsidian vault containing your documentation, architecture decisions, code patterns, research notes, or best practices—and Shad will decompose complex goals, retrieve only what matters, verify outputs, and assemble coherent results.
This isn’t “long-context prompting.”
It’s long-context reasoning
#AI #Claude #RLM #Obsidian