EDRSilencer - a tool that uses Windows Filtering Platform (WFP) to block EDR agents from reporting security events to the server https://t.co/WU6mlppP3w #cyber#threathunting#infosec
🎯Detecting/Hunting PsMapExec Default Values (Two of the most commonly seen methods)
1️⃣SMB Method: Service Creation
- EIDs 7045(System) and 4697(Security)
- Service name regex: 'Service_[a-z]{16}'
- Service File name: PowerShell command execution
The PowerShell script that will run on the target host essentially creates a server that listens for connections via a named pipe and executes commands.
ref: https://t.co/FjKwy7oggk
----
2️⃣WMI Method: Process Execution
- ParentProcess: WmiPrvSE.exe
- Process: PowerShell.exe
- CommandLine: powershell.exe -NoLogo -NonInteractive -ExecutionPolicy Unrestricted -WindowStyle Hidden -EncodedCommand " + $Command
The $Command starts with the base64 encoded text JAByAGUAcwB1AGwAdAAg which decodes to "$result".
ref: https://t.co/6Amzc8OEFj
Scammers and bad actors are consistently using the popular game #Roblox to scam players (often children) out of their money, or even using it as a way to install #malware on their computers. We have an overview of their various tactics up on the Talos blog https://t.co/D9qsjwpYoe
#ICYMI VMware released security advisories to address vulnerabilities in multiple products. Read more at https://t.co/OQSIFsAiq1. #Cybersecurity#InfoSec#VMware
Threat researchers from @Proofpoint this month identified TA571 delivering the Forked variant of IcedID in two campaigns. Emails in the campaigns purported to be replies to existing threads, a malicious technique known as thread hijacking.
Read more ⤵️ https://t.co/ckYpL2z9vw
🚨🚨🚨 Whatever you were thinking about CVE-2023-20198 (#Cisco IOS EX) it's 100x worst.
We used @TalosSecurity IOC check and found ~30k implants.
That's 30k devices infected (routers, switches, VPNs), under the control of threat actors.
That's excluding rebooted devices.
#QBOT Affiliates on a New Journey: What We Know So Far 🚶♂️👣
⏳ Less than 24 hours from our last update and we already see what we anticipated:
The first victims have been compromised.
The threat actors initially distributing #Qakbot malware in TR and BB campaigns did not hesitate.
🔲 However, this time, they infected the victim's devices using #DarkGate malware instead of the Qakbot one.
Isn't switching to another malware more complicated? 🤨
Not really, because they were running the infections through the same infrastructure and backend.
💡 To stay well-informed, you can find the recent #IOCs on our #GitHub page: https://t.co/wdM396KcY8
#threatintelligence #PRODAFTreports #onestepahead
Attackers are having to switch up their tactics after #Microsoft changed the way they handle macros. On the latest episode of #ThreatWiseTV, hear from one of our researchers about what he's seeing in the field and how adversaries are adapting https://t.co/isTDVyX2Em
We did a Markdown version of the TLP:UNCLEAR proposal.
https://t.co/U61rlckPYn
https://t.co/0AefHESaQ1
Pull-request are welcome.
https://t.co/fs2e5c75Ge
🔍If you are looking for a comprehensive overview of the current #3CX supply chain attack, I created a diagram that shows the attack flow!💥I'll update as soon as the analysis progresses. Stay tuned for the MacOS edition! #cybersecurity#infosec#supplychainattack#3CXpocalypse
A @MISPProject tip of the week: MISP objects are a powerful way to add contextually linked attributes to threat events. And it's available via PyMISP. Use this notebook as a starter or learn how to add your own custom objects. https://t.co/ybuAivn3bt https://t.co/ftZ1hoTgoR
The indicators from @CrowdStrike (and others) on the compromise of the 3CX desktop app have been published via the @MISPProject OSINT feed of https://t.co/zRuayIOAcL. You can also get them directly at
https://t.co/yxjLfu1f2c
#3CXpocalypse#3CX
We recently discovered a new threat actor called #YoroTrooper that's primarily motivated by espionage-related activities. Find out what this group may be after and why. https://t.co/notrfkCdJ3
Noticed two #guloader campaigns recently where wscript > vbs > powershell with VT detection 2/60 and 0/60 respectively.
Here is a KQL query below for your #ThreatHunting⤵️
#MicrosoftSecurity#KQL
https://t.co/rccu0bJG0W
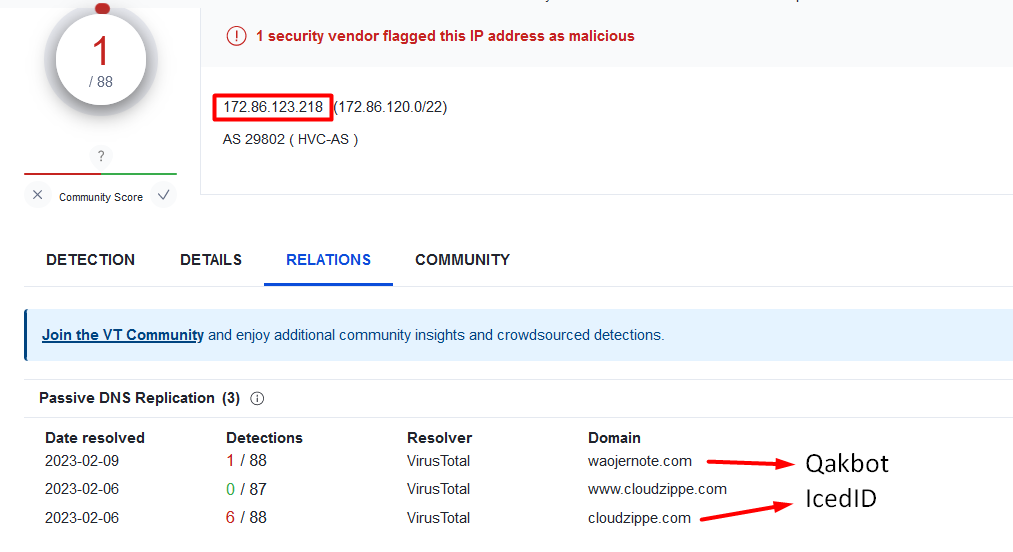
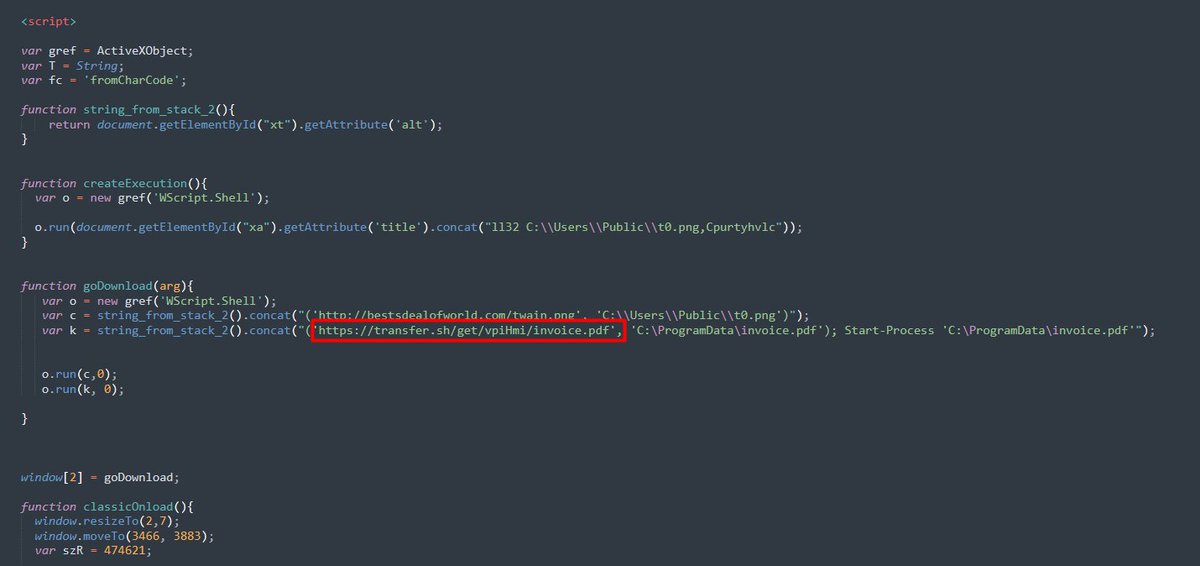
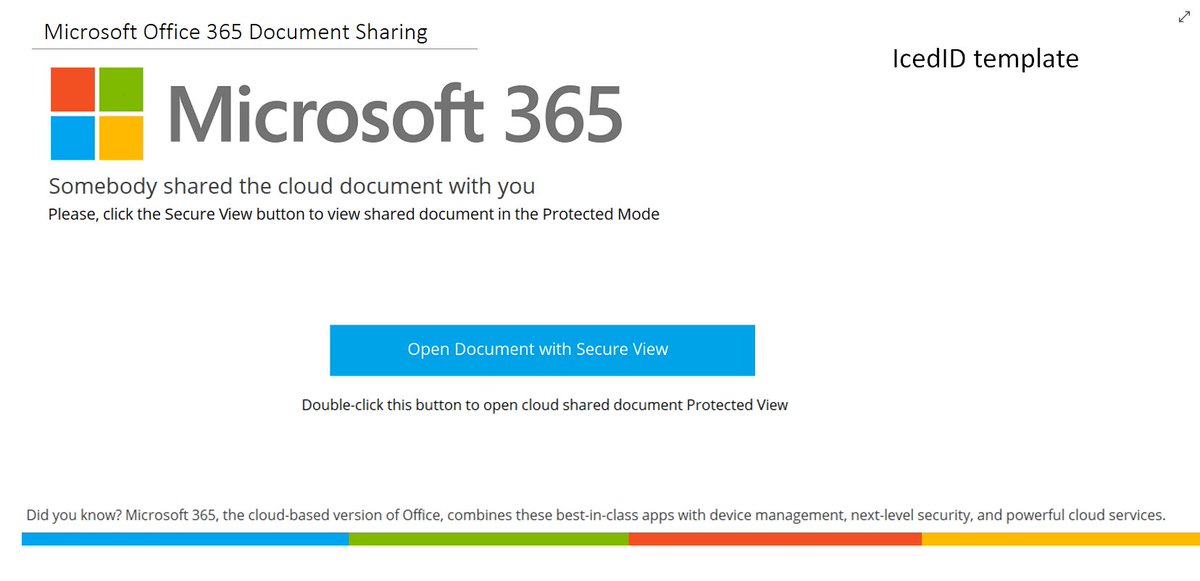
1/ Interesting, possibly the same TA/affiliates distributing first #IcedID (Campaign ID: 3954321778) and then #Qakbot (new Botnet ID: tok01) via #OneNote documents.
They used the same URL for the decoy document and the same server for DLL distribution domains.