Myself and @OriginalSicksec , bagged over 6OK-ish $ bounties from this technique in bug bounties, and based on the current supply chain attacks I wanted to share some thoughts
Note: english not my mother tongue so article is enhaced by AI, but content is not an AI slop I promise
https://t.co/C1b80E5FHt
Red-team update: Claude just one-shotted a universal jailbreak for DeepSeek V4.1 in 90 minutes.
Success rate: 8/8 on a diverse battery of restricted queries.
- https://t.co/dMBG0KeJLS
The models are now doing the red-teaming for us.
Just found this awesome Open Source repository with a list of 10 AI prompts you can integrate into your bug bounty hunting workflow
Web2 Security focused, still very valuable - scoping, triaging, validation & more. 10x for the great resource @mdp_sec 🫡
https://t.co/xT4kwuUJ4I
SharePoint + Pre-Auth RCE + MemShell? 👀
We’ve published our technical analysis of CVE-2026-65660, covering the attack chain from an Allow Anonymous site and a pre-auth SharePoint vulnerability to RCE and MemShell.
Take a look:
https://t.co/8jVE8N0UtV
🚨 CVE-2026-65343 AppleKeyStore
iOS 26.6. kernel pointer leak. KASLR slide.
_LibSer_SEPControl_Deserialize copyout() trusts declared_length.
no check against bytes left in the ACM buffer.
0x800 pulls ~0x7E8 past the message into adjacent kernel heap.
pointers come back as 0xfffffff0xxxxxxxx.
fixed in 26.6.1.
on a real phone you still need a sandbox escape to reach AKS.
the leak itself is the missing length check.
credit: Drinor Selmanaj, Surya Narayan Kushwaha
PoC: https://t.co/d9UVwCdXUI
#iOS #ExploitDev #InfoSec
s1n6h/pentest-harness: Pentest Harness — Heaven for Hackers. A self-hosted AI agent harness for authorized pentests, bug bounty, security labs, and CTFs. Bring your own AI model API; sessions stay local. https://t.co/EvYNl2wvqc
𝐀𝐠𝐞𝐧𝐭𝐇𝐨𝐮𝐧𝐝 - Offensive security framework for AI agent infrastructure - recon, credential looting, model exfiltration, poisoning, & attack-path analysis across MCP, A2A, gateways, & AI services. BloodHound for the agentic stack
🔗 https://t.co/TXcADrCmo9
#Cybersecurity
🔥 $15K Bug Bounty: Buffer Overflow Exploit 🤯
Our team analyzed this exploit and broke down the attack path, impact, and key takeaways.
📖 https://t.co/0HbJuLBtIY
📢 More bug bounty write-ups:
https://t.co/FeMz53HSN0
#BugBounty#CyberSecurity#BufferOverflow#AppSec
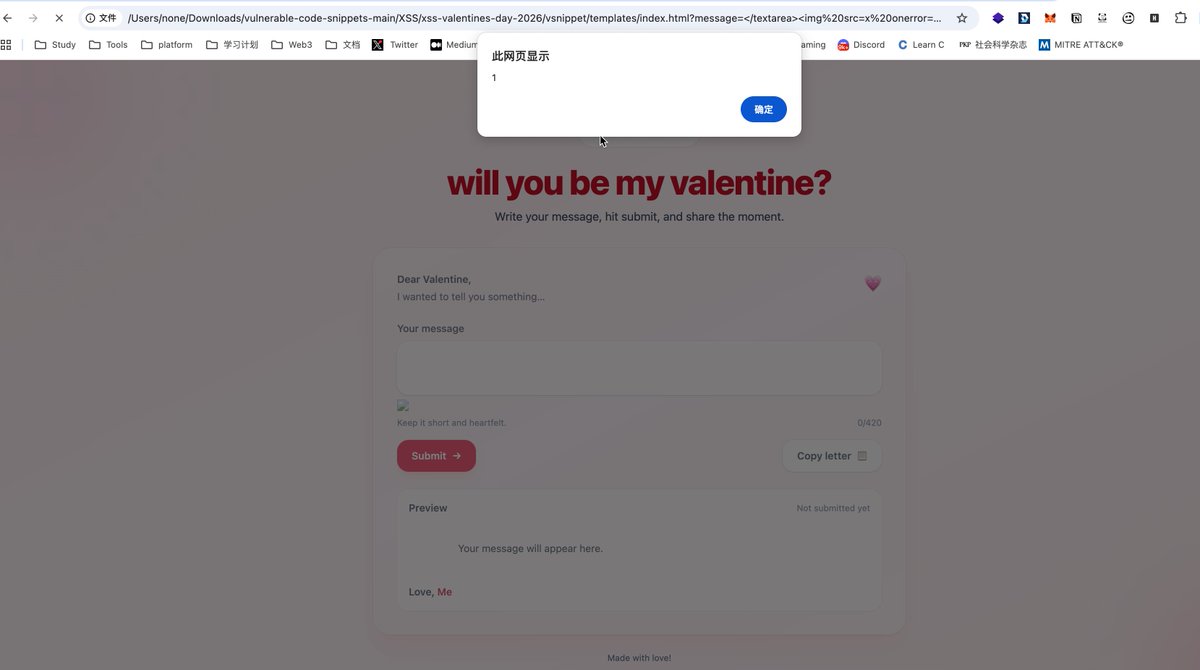
It’s been a while… But we’re back with a new vulnerable code snippet, just in time for Valentine’s Day ❤️
Find the bug, send us your solution via DM, and try to win some swag 👕
We’ll pick 1 random winner on February 19.
Ready? 👉 https://t.co/DZM1KB3TzN