hashcat v8.0.0 released!
The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards.
Release notes: https://t.co/0ffrO586PJ
Download: https://t.co/Grn4jZmAWr
I will be releasing the brand new MobSF iOS Dynamic Analyzer powered by Frida and @CorelliumHQ at @BlackHatEvents Arsenal, London UK.
Here is a sneak peak: https://t.co/BkWOmQTOKR
Catch me live on Thursday, December 7 1.00 PM
Happy Monday!
MobSF v3.7.6 is out! 🎉
* Now supports independent scanning of AAR, JAR, Static Libraries (.a) and Dynamic Libraries (.so, .dylib)
* Improved String extraction for APKs
And a lot more under the hood improvements.
https://t.co/aiS1UMewEg
Recently did a React/Next.js secure code review. Here is a checklist that will help you spot some common vulnerabilities.
https://t.co/gKw56ssKkg
#appsec#nextjs#reactjs#codereview
Capturing Mobile App Network Traffic with MobSF and Burp.
MobSF takes care of
* Proxy Root CA install
* Generic SSL Pinning/Certificate Transparency bypass
* Generic Root/Debugger check bypass
See Docs: https://t.co/AJuZsIMedD
MobSF v3.6.9 is out! 🎉
The latest docker image now supports quick and easy Dynamic Analysis with Android Studio AVD, Genymotion, and Corellium Android VMs.
See the updated docs: https://t.co/AJuZsIMedD
MobSF v3.6.0 Released 🚀
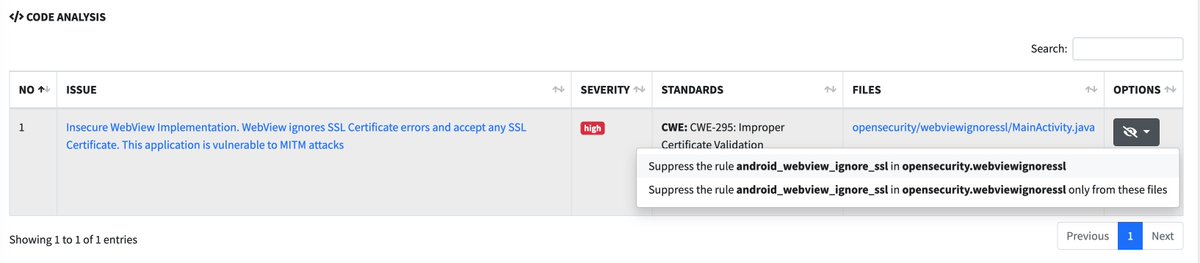
False Positive Triaging support + new REST APIs just landed in. Feel free to play with our demo instance: https://t.co/ZCM36RVNCl
#mobsf#MobileSecurity