🎁 We're giving away 20 FREE SAL2 certifications 🎁
The wait is over...SAL2 is officially here 🚀 Security Analyst Level 2 is the certification that proves you can investigate, decide, and lead in a real SOC. The only defensive cert that covers every domain a real L2 analyst faces!
💸 With a special launch price of $599 valid until 2 April only.
🚀 Comment, SHARE and fill in the form to enter the free cert giveaway ▶️ https://t.co/j4tOzqIjuo
❓Want to know more what SAL2 is about see here: https://t.co/DAej3B9q7j
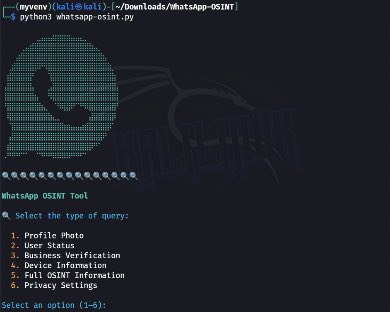
Have you ever imagined that WhatsApp could be used to achieve operational goals?
With these tools, it becomes a reality
https://t.co/np4bs7sSBy
@three_cube@_aircorridor@co11ateral
🚨 SOC Playbook Complete Phishing Investigation Guide 🚨
🎯 From Inbox to Incident Closure: Mastering Phishing Defense
Phishing continues to be the leading initial compromise method in modern cyber breaches
📧Comment PDF for full Guide
Mastering Ethical Hacking Through Real-World Scenarios 🔐💻
The Hacker Playbook by Peter Kim continues to be one of the most practical hands-on resources in the cybersecurity world. (✉️PDF contains many pages, so I’m sharing this summary here comment PDF for the full guide.)
#Blue_Team_Techniques
Active Directory Advanced Threat Hunting
https://t.co/vash7xp75I
]-> Advanced hunting for group policy settings:
https://t.co/w0RNlqZpMj
Hot new blog today on a recent #CVE#vulnerability:
#Atlassian#confluence authentication bypass.
For those keeping track, this CVE's release date was only 2 days ago, and we already have a template for you all. 🔥
Read all about it here:
https://t.co/OpIjelZHNt
Automate Android Penetration Testing 📱
Script to Automate installtion of Apps ,frida server and moving Burpsuite certificate to root folder
- https://t.co/2l7toXGWzl
#infosec#cybersec#bugbountytips
Offensive Lua
A collection of offensive security scripts written in Lua with FFI. The scripts run with LuaJIT (v2.0.5) on Microsoft Windows to perform common tasks.
• Run an EXE
• Bypass UAC
• File, Networking or Registry
• Common Tasks (e.g. bind a shell)
https://t.co/UkHkAB5Oxn
#cybersecurity #infosec #pentesting #redteam