Election and Cyber-Security SME
"Evil prevails when good men do nothing"
Elections Belong to the People!
Manipulated elections are communist sleight of hand.
CAN ELECTIONS BE STOLEN?
LARA EXPLAINS HOW.
What if election manipulation begins long before the first vote is ever cast?
In this powerful monologue, Lara Logan breaks down what she believes are the hidden mechanisms behind election interference, from voter rolls and census data to electronic voting machines, algorithms, ballot handling, and vulnerabilities in election infrastructure.
Drawing on years of investigating election integrity, Lara challenges the narrative that election systems are beyond manipulation and raises serious questions about transparency, accountability, and who ultimately controls the vote.
Are America’s elections truly secure? And are the systems designed to detect fraud capable of exposing it?
These are questions every American deserves to have answered.
Election integrity isn’t a partisan issue. It’s about protecting the voice of every American.
SUPPORT INDEPENDENT JOURNALISM:
https://t.co/qJNnZCPvyd
#LaraLogan #ElectionIntegrity #ElectionSecurity #ElectionTransparency #GoingRogue
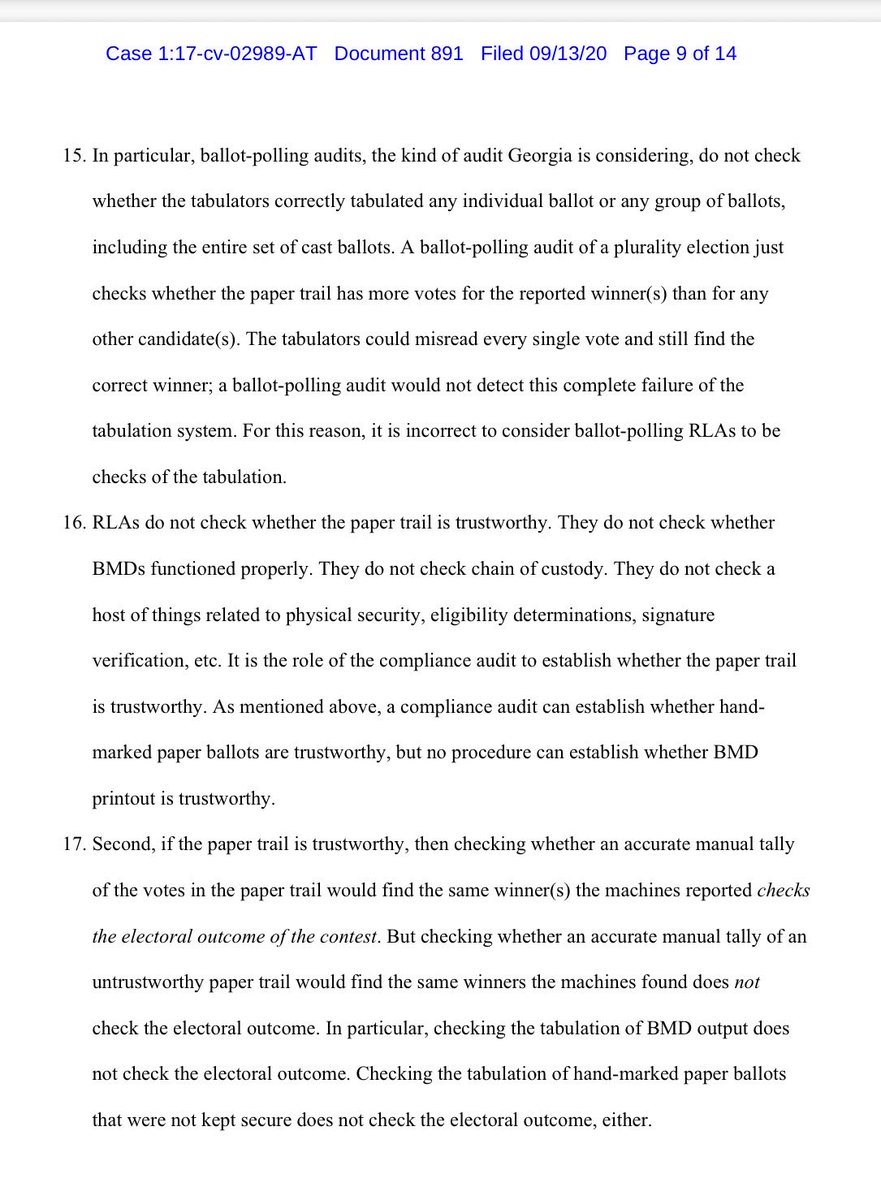
Don't feel bad, most people miss this glaring oversight: Risk-limiting audits are a real statistical tool ONLY when errors are random. The problem is that the math only holds if the thing you are measuring is noise. An intentional manipulation is not noise. It is a signal someone chose to place, and it can be placed precisely where the sample is least likely to catch it. Statistics cannot distinguish targeted manipulation from a legitimate vote because both look identical inside the data. The audit then confirms a number that was constructed to survive the audit. That is not a near-perfect result. That is a near-perfect laundering. The only check that breaks that loop is a full hand count of ballots whose chain of custody is provable from start to finish, because that is the one method that does not depend on trusting the distribution of the errors.
Do you see now?
Wait, are you saying these vendors have been LYING TO US????
https://t.co/JrSe4J0Wvd
Here are the MAC address prefixes that are own by Voting System Vendors:
Dominion Voting Systems
MA-LC4:19:8B
Dominion Voting Systems Corporation
215 Spadina Avenue, Toronto, Ontario, CA M5T 2C7
Smartmatic
MA-L00:06:C2
Smartmatic Corporation
6400 Congress Ave., Suite 1300, Boca Raton, FL, US 33487
Smartmatic
MA-L28:72:C5
Smartmatic Corp1001 Broken Sound Pkwy NW, Suite D, Boca Raton, Florida, US 33487
Diebold Nixdorf (historical voting systems relevance)
MA-L00:03:51
Diebold Nixdorf
5995 Mayfair Road, North Canton, OH, US 44720
Diebold Nixdorf
MA-L00:03:56
Diebold Nixdorf
Wohlrabedamm 31, Berlin, DE 13629
Diebold Nixdorf
MA-L3C:BD:14
Diebold Nixdorf
Wohlrabedamm 31, Berlin, DE 13629
We do not have elections, we have intelligence operations. And the machines are designed not to vote, but to cheat. We have a small window now to try to fix the election system before the next election. I have been reporting on this for years, long before the 2026 midterms. There are three phases of the steal before you get to the flawed reporting process:
1) Long before the polls open, they use data to figure out the steal and front-load the machines with software they program to get the result/outcome they want. That software can flip votes. It can remove the “inactive” check-mark from purged voters so they are back on the rolls. Can also create “ghost voters” by assigning any number of voter ID numbers to a voter’s name so one person can vote 20/25/30 - as many times as they want. There are many different options/permutations. They can do some or all - depending on the need. They can also front-load the vote so that the desired party emerges victorious from early voting/mail-in ballots.
And they use the census to count non-citizens to fraudulently inflate representation in the house, (based on population). And inflate voter rolls by registering non-citizens to vote, refusing to purge voter rolls of dead people etc.
2) The messy part: ballot harvesting, ballot stuffing, votes counted multiple times, hidden boxes of ballots that suddenly appear etc. The stuff that happens in person. Typically not enough on its own to sway the result but collectively meets the need. This is how you support the digital steal - make sure there are enough physical ballots to match the manipulation in the computer/machine. Lose batches of ballots from certain counties if you know they will sway against what you need for the steal. Produce batches that are artificially weighted in favor of your candidate etc. Block access to the polling station, black access to the count, send people home on false pretenses, stop the count unexpectedly or early to buy time - you know the drill. You have seen it before.
3) During the vote: access the machines remotely to manipulate the data. This is needed when the advance predictions/manipulation are off, data was incomplete or same-day voting exceeds predictions and they have to compensate to get the result they want. This happened in 2020 when they accessed the machines from servers in Serbia. In case you’re wondering, in 2024, acc to Berntsen, an American cyber experts intervened to block access from Serbia & stop the steal.
For all those screaming for evidence:
- They do not use the same methods all the time to make it harder to track & to prevent.
- All manipulation can be easily hidden in the software which is programmed to cover their tracks.
- Impossible to get evidence from the servers as no one can get access to the machines.
- The software is encrypted, putting the data out of the reach of most of the population.
Our elections are captured by those who own & run the machines, the NGO’s who create the infrastructure for the cheat, the politicians/leaders who never use their power to get to the truth - and the people who finance & direct all of this. Remember: we do not have elections, we have intelligence operations. And the machines are not designed for voting - they are built to cheat.
Don't feel bad, most people miss this glaring oversight: Risk-limiting audits are a real statistical tool ONLY when errors are random. The problem is that the math only holds if the thing you are measuring is noise. An intentional manipulation is not noise. It is a signal someone chose to place, and it can be placed precisely where the sample is least likely to catch it. Statistics cannot distinguish targeted manipulation from a legitimate vote because both look identical inside the data. The audit then confirms a number that was constructed to survive the audit. That is not a near-perfect result. That is a near-perfect laundering. The only check that breaks that loop is a full hand count of ballots whose chain of custody is provable from start to finish, because that is the one method that does not depend on trusting the distribution of the errors.
Do you see now?
@GuntherEagleman An RLA is not designed to catch intentional manipulation. Anyone using it to catch that doesn't understand this VERY IMPORTANT CONCEPT!
Please read the below ASAP:
https://t.co/GSrnzVMvqO
@GuntherEagleman An RLA is not designed to catch intentional manipulation. Anyone using it to catch that doesn't understand this VERY IMPORTANT CONCEPT!
Please read the below ASAP:
https://t.co/GSrnzVMvqO
Don't feel bad, most people miss this glaring oversight: Risk-limiting audits are a real statistical tool ONLY when errors are random. The problem is that the math only holds if the thing you are measuring is noise. An intentional manipulation is not noise. It is a signal someone chose to place, and it can be placed precisely where the sample is least likely to catch it. Statistics cannot distinguish targeted manipulation from a legitimate vote because both look identical inside the data. The audit then confirms a number that was constructed to survive the audit. That is not a near-perfect result. That is a near-perfect laundering. The only check that breaks that loop is a full hand count of ballots whose chain of custody is provable from start to finish, because that is the one method that does not depend on trusting the distribution of the errors.
Do you see now?
🚨Tally Texas News
Tarrant County Officials panicked live —OMG “They are hacking the machines!” → CIO: “SHUT IT DOWN!”
In January 2024, Tarrant County EA invited the public to try to hack its Hart County Wide Polling place voting system.
They did. Easily.
Officials panicked live —"OMG They are hacking the machines!”
June 23, 2026 Sworn Senate testimony just dropped from an insider standing right behind them.
This should be front-page news. It’s not. #txlege🧵
For all SYNOLOGY users!!! MAJOR HACK affecting Synology coming through NGINX:
(this is not a direct synology hack, but because it uses NGINX, it is affected. and there is a quick thing you can do to protect your systems until a full patch can be released)
https://t.co/m5uXRj5BXN
But don't worry about your electronic voting systems...they are perfectly safe from all threats of course, just because people told you so.
Yet the only way to DOUBLE-CHECK is to hand-tabulate every vote on every ballot right after the voter casts the ballot.
And they don't do that. At all. Not even close.
Everyone keeps ignoring the two fundamental requirements that a properly functioning election system must have:
It is INCREDIBLY frustrating that people thought audits were going to catch this, after years and years of audits that didn't catch it, lol.
Some pushed audits maliciously.
Some pushed audits out of pure stupidity.
And some were offered the knowledge and BEGGED TO LOOK AT IT, but they refused then misled countless people for months prior to the election while blocking those with the answers.
And who those were will shock many.